
 #1
Tools for discovering open ports, services, and potential entry points on network devices.
Kitploit recommended

 postmodern/ruby-nmap
A Ruby interface to nmap, the exploration tool and security / port scanner. Allows automating nmap and parsing nmap XML files.
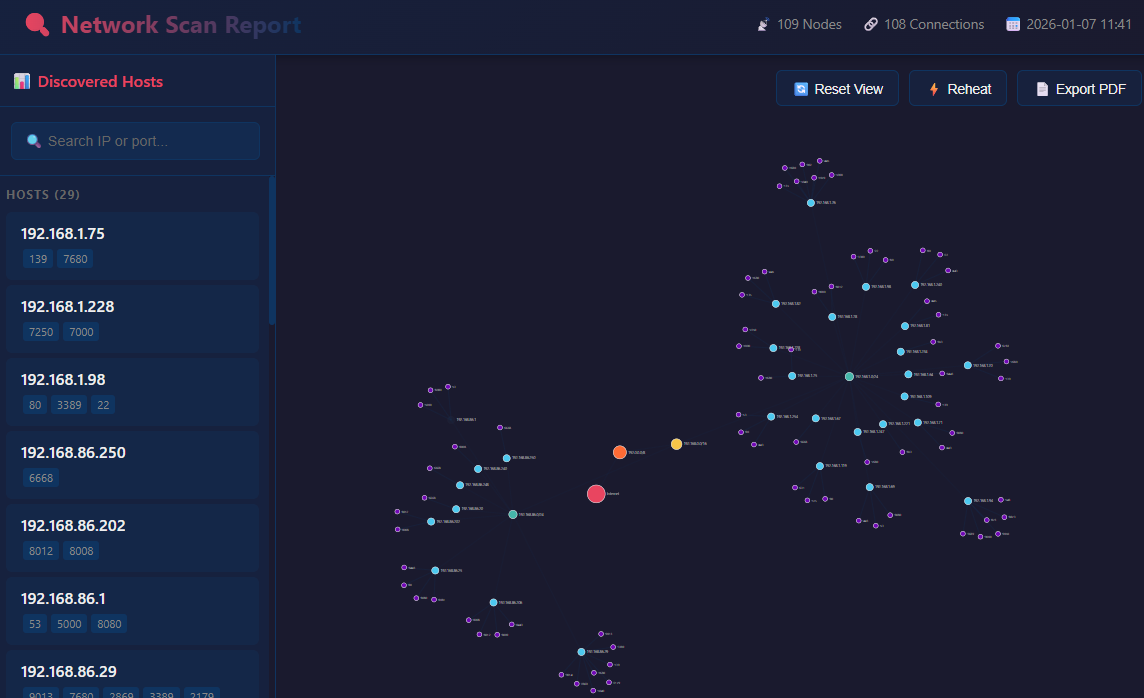 artofscripting/masscan-report
A Python tool that generates interactive React-based HTML visualizations from masscan JSON output, featuring a D3.js force-directed network graph.
 deade1e/radar
The hackable network scanner
 rxerium/bug-bounty-tools
A BASH Script to automate the installation of the most popular bug bounty tools
 alientec1908/alientec-recon-tool
AlienTec-Recon-Tool
 alechilczenko/kimi
Attack Surface Discovery tool built on a microservice approach, utilizing multi-threading for fast, internet-scale asset indexing
 cyberintel-labs/insightsnexus
OSINT Graph Investigation Application
 microsoft/ethr
Cross-platform CLI for network performance testing over TCP, UDP, HTTP, HTTPS, and ICMP: bandwidth, connections/s, packets/s, latency, loss, jitter,…
 divinelabio/argus
The Ultimate Information Gathering Toolkit
 bahaabdelwahed/killshot
A Penetration Testing Framework, Information gathering tool & Website Vulnerability Scanner
 mafiosohack/offensive-lab-2
Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…
 geeknik/scada-scanner
A high-performance, asynchronous SCADA/ICS scanner
 chvancooten/bugbountyscanner
A Bash script and Docker image for Bug Bounty reconnaissance. Intended for headless use.
 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 helich0pper/karkinos
Penetration Testing and Hacking CTF's Swiss Army Knife with: Reverse Shell Handling - Encoding/Decoding - Encryption/Decryption - Cracking Hashes /…
 gmh5225/mcp-god-mode
Did you ever just want it to do everything? 148 POWERFUL Infosec/Admin tools on a single MCP server.
 bandit-haxunit/haxunit
Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…








