

A Penetration Testing Framework, Information gathering tool & Website Vulnerability Scanner
This project is no longer maintained !
A Penetration Testing Framework, Information gathering tool & Website Vulnerability Scanner
Why KillShot?
You can use this tool to spider your website, gather important information, and automate data collection using tools such as WhatWeb, Host, Traceroute, Dig, Fierce, and WafW00f. It also allows you to identify the CMS and find vulnerabilities in your website using a CMS Exploit Scanner and a Web Application Vulnerability Scanner.
Additionally, KillShot can automatically perform multiple types of scans using Nmap and Unicorn. With this tool, you can also generate simple PHP backdoors, upload them manually, and connect to the target using KillShot.
This tool also includes a simple Ruby fuzzer tested on VULSERV.exe, as well as a Linux log-cleaning script to modify login path content. The spider feature helps you find website parameters and scan for XSS and SQL injection vulnerabilities.

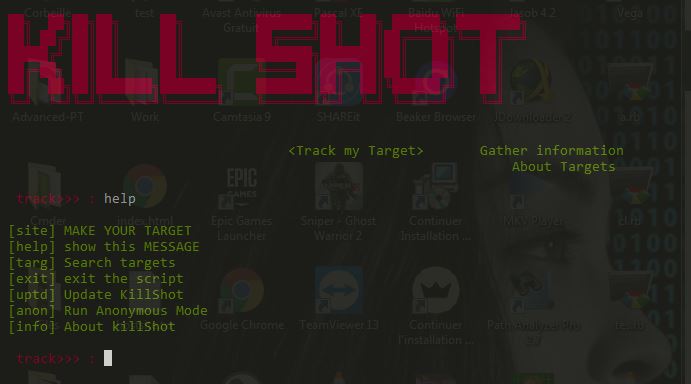
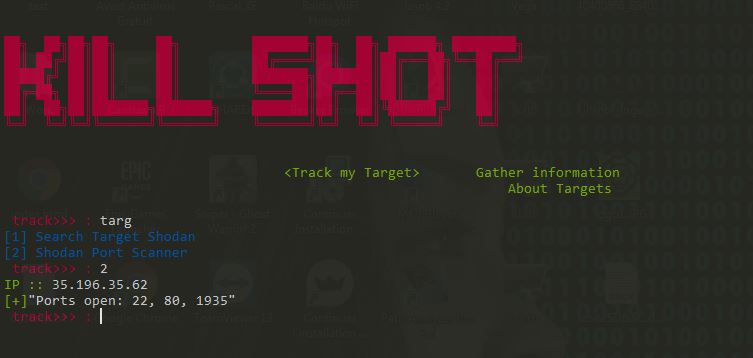
CreateAccount Here Register and get Your aip Shodan AIP And Add your shodan AIP to aip.txt < only your aip should be show in the aip.txt > Use targ To search about Vulnrable Targets in shodan databases

Use targ To scan Ip of servers fast with shodan
{0} Spider
{1} Web technologie
{2} WebApp Vul Scanner
{3} Port Scanner
{4} CMS Scanner
{5} Fuzzers
{6} Cms Exploit Scanner
{7} Backdoor Generation
{8} Linux Log Clear
{1} Xss scanner
{2} Sql Scanner
{3} Tomcat RCE
 [0] Nmap Scan
 [1] Unicorn Scan
Nmap Scan
 [2] Nmap Os Scan
 [3] Nmap TCP Scan
 [4] Nmap UDB Scan
 [5] Nmap All scan
 [6] Nmap Http Option Scan
 [7] Nmap Live target In Network
Unicorn Scan
[8] Services OS
[9] TCP SYN Scan on a whole network
[01] UDP scan on the whole network
 {1} Generate Shell
 {2} Connect Shell
1 ----- Help Command
[site]  MAKE YOUR TARGET
[help] show this MESSAGE
[exit] show this MESSAGE
2 ------ Site command
Put your target www.example.com
without the http
git clone https://github.com/bahaabdelwahed/killshot
cd killshot
ruby setup.rb (if setup show any error just try to install the gems/tool manual )
ruby killshot.rb
Download ruby for windows ==> https://rubyinstaller.org/downloads/
Download Cmder here       ==> http://cmder.net/
Download Curl For 64/32   ==> https://curl.haxx.se/windows/
Download nmap             ==> https://nmap.org/download.html
Enjoy !
 [+] Fix setup error
 [+] Fix sql injection detect error
 [+] Add Typo3 Scanner (+brute force)
 [+] Detect Of the MX and NS
Easy and fast use of killshot
https://www.youtube.com/watch?v=SEGRh86J6vk
Use KillShot To Detect and Scan cms vulnrability (Joomla && Wordpress) And Scan For Xss And Sql
https://www.youtube.com/watch?v=QPF-rppYSOY
Please Any one who find any error/bugs in any code contact me also if you want to add some codes
or to upgrade some codes in killshot just contact me
Vulnrability are taken from
       1) http://www.exploit-db.com
       2) https://sploitus.com
       3) http://cxsecurity.com







