
 #1
Tools for maintaining long-term access to compromised systems, even after reboots.
Kitploit recommended

 nccgroup/winpayloads
Undetectable Windows Payload Generation
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 calebstewart/pwncat
Post-exploitation platform automating enumeration, privilege escalation, persistence, and C2 operations via reverse/bind shells with cross-platform…
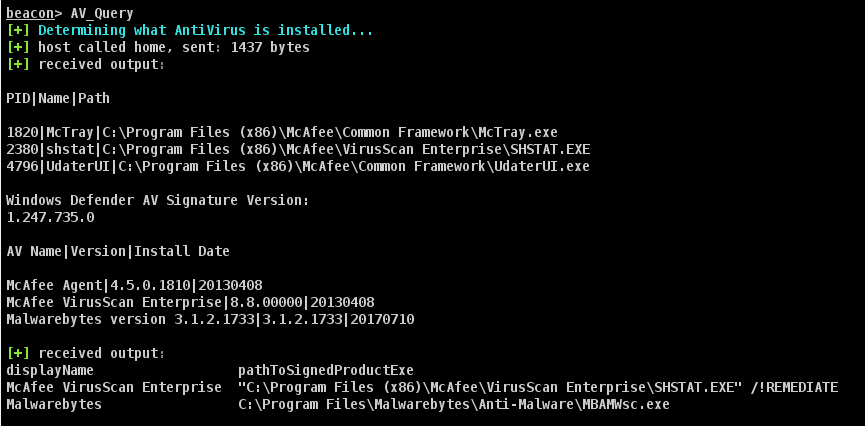 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
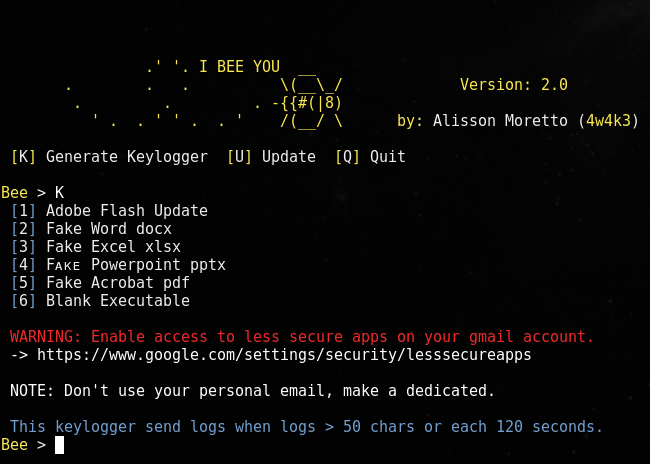 4w4k3/beelogger
Generate Gmail Emailing Keyloggers to Windows.
 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 jkornev/hidden
Windows driver with usermode interface which can hide processes, file-system and registry objects, protect processes and etc
 sweetsoftware/ares
Python botnet and backdoor
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 reverseclabs/sharpgpoabuse
SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.








