
 #1
Tools for maintaining long-term access to compromised systems, even after reboots.
Kitploit recommended

 hackerschoice/thc-tips-tricks-hacks-cheat-sheet
Various tips & tricks
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 m0nad/diamorphine
LKM rootkit for Linux Kernels 2.6.x/3.x/4.x/5.x/6.x (x86/x86_64 and ARM64)
 ghostpack/rubeus
Trying to tame the three-headed dog.
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 netspi/powerupsql
PowerUpSQL: A PowerShell Toolkit for Attacking SQL Server
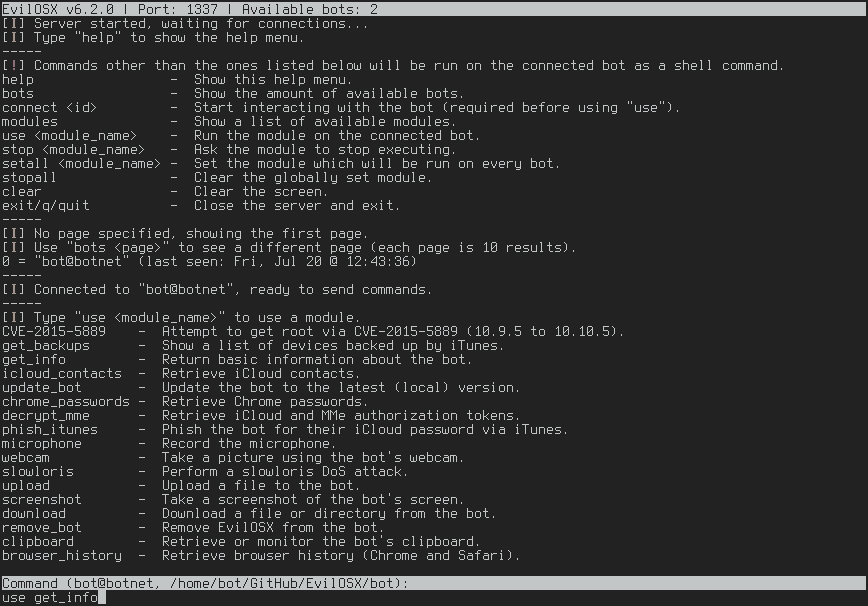 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
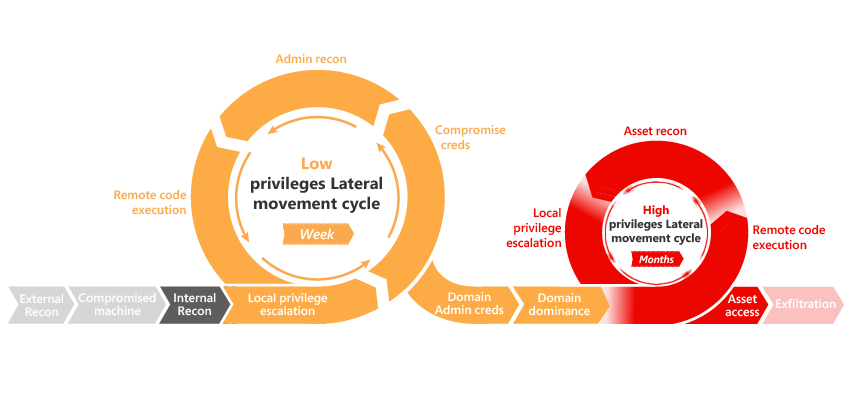 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 netbiosx/checklists
Red Teaming & Pentesting checklists for various engagements
 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
 nyan-x-cat/asyncrat-c-sharp
Open-Source Remote Administration Tool For Windows C# (RAT)
 ldpreload/blacklotus
BlackLotus UEFI Windows Bootkit
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…







