
 #1
Tools for maintaining long-term access to compromised systems, even after reboots.
Kitploit recommended

 gmh5225/kli-ex
Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…
 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
 mobilehackinglab/ghostlock-a17
Kernel exploit for CVE-2026-43499 on Samsung Galaxy A17 achieving root via KDP bypass, KASLR recovery, and forged workqueue execution with persistent…
 neofito/cve-2020-1337
CVE-2020-1048 bypass: binary planting PoC
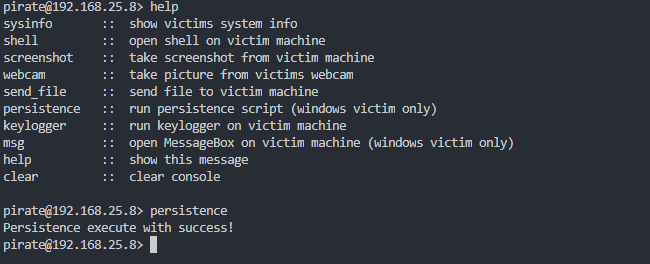 gbrn1/pirate
Python Remote Access Tool
 persistent-security/hermes-the-messenger
A PoC for achieving persistence via push notifications on Windows
 1ndevelopment/ghostlock-s26
GhostLock (CVE-2026-43499) app for the Galaxy S26 series
 kira2040k/redbloodc2
Node.js command-and-control server with FUD payload generation, encrypted communication, session management, and modules for data exfiltration and…
 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 agentshield-ai/sigma-ai
Sigma detection rules for AI agent security monitoring
 al1ex/pentest-command
Pentest-Command
 yijiacloud/ghostlock-oppo-pckm00
CVE-2026-43499 GhostLock futex UAF LPE PoC for OPPO PCKM00 (SM6150) / Linux 4.14.180
 rbowes-r7/refreshing-soap-exploit
A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
 jackdoan/tp-link-archerc5-rce
CVE-2018-19537
 t43wiu6/cve-2019-0887
exp for CVE-2019-0887
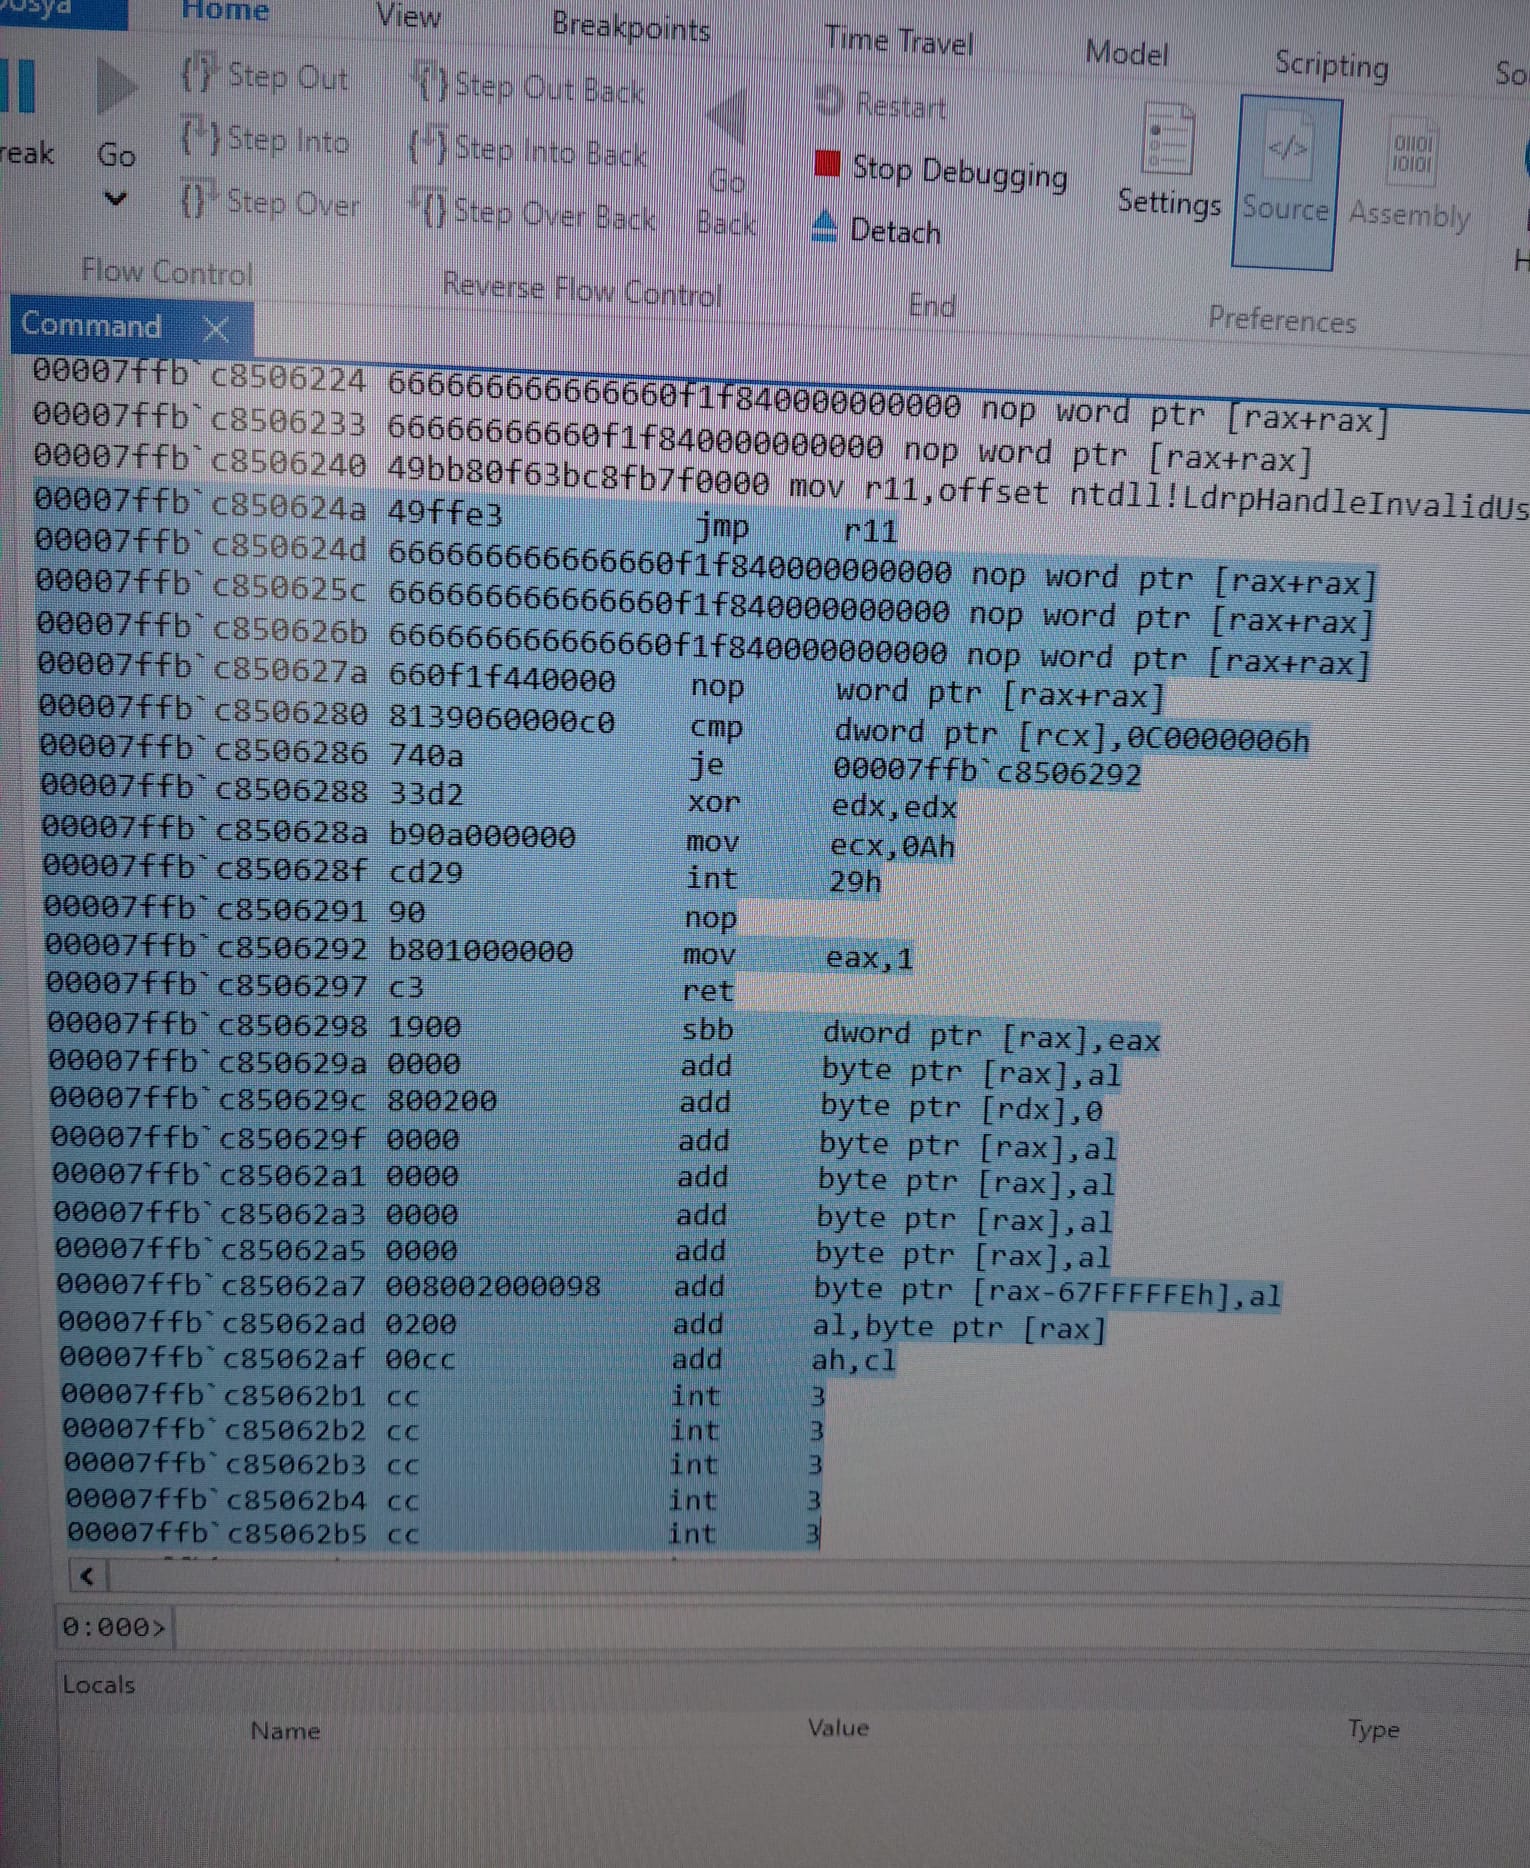 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 racoten/reflectivepluginloader
Reflective PE mapper and evasion-hardened module stomping engine for Windows x64
 synacktiv/extloader
A chromium extension exploitation toolkit








