
 #1
Tools for maintaining long-term access to compromised systems, even after reboots.
Kitploit recommended
 rhzv0/bat
Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…
 the-snek-initiative/snek_equinox
Repository hosting a hypothetical EDR Spoofer, as discovered originally by Nightmare-Eclipse
 johnswiftc/rustdllproxy
Generate Proxy DLLs in Rust
 slyd0g/dylibhijacktest
Discover DYLD_INSERT_LIBRARIES hijacks on macOS
 u53rw4r3/remotekeystrokes
A script to automate keystrokes through a graphical desktop program.
 mhdgning131/teletunnel
Bypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !
 yo-yo-yo-jbo/macos_sandbox
Blog post exploring macOS App Sandbox, entitlements via codesign, and sandbox escape techniques using launchd, LaunchAgents, and quarantine…
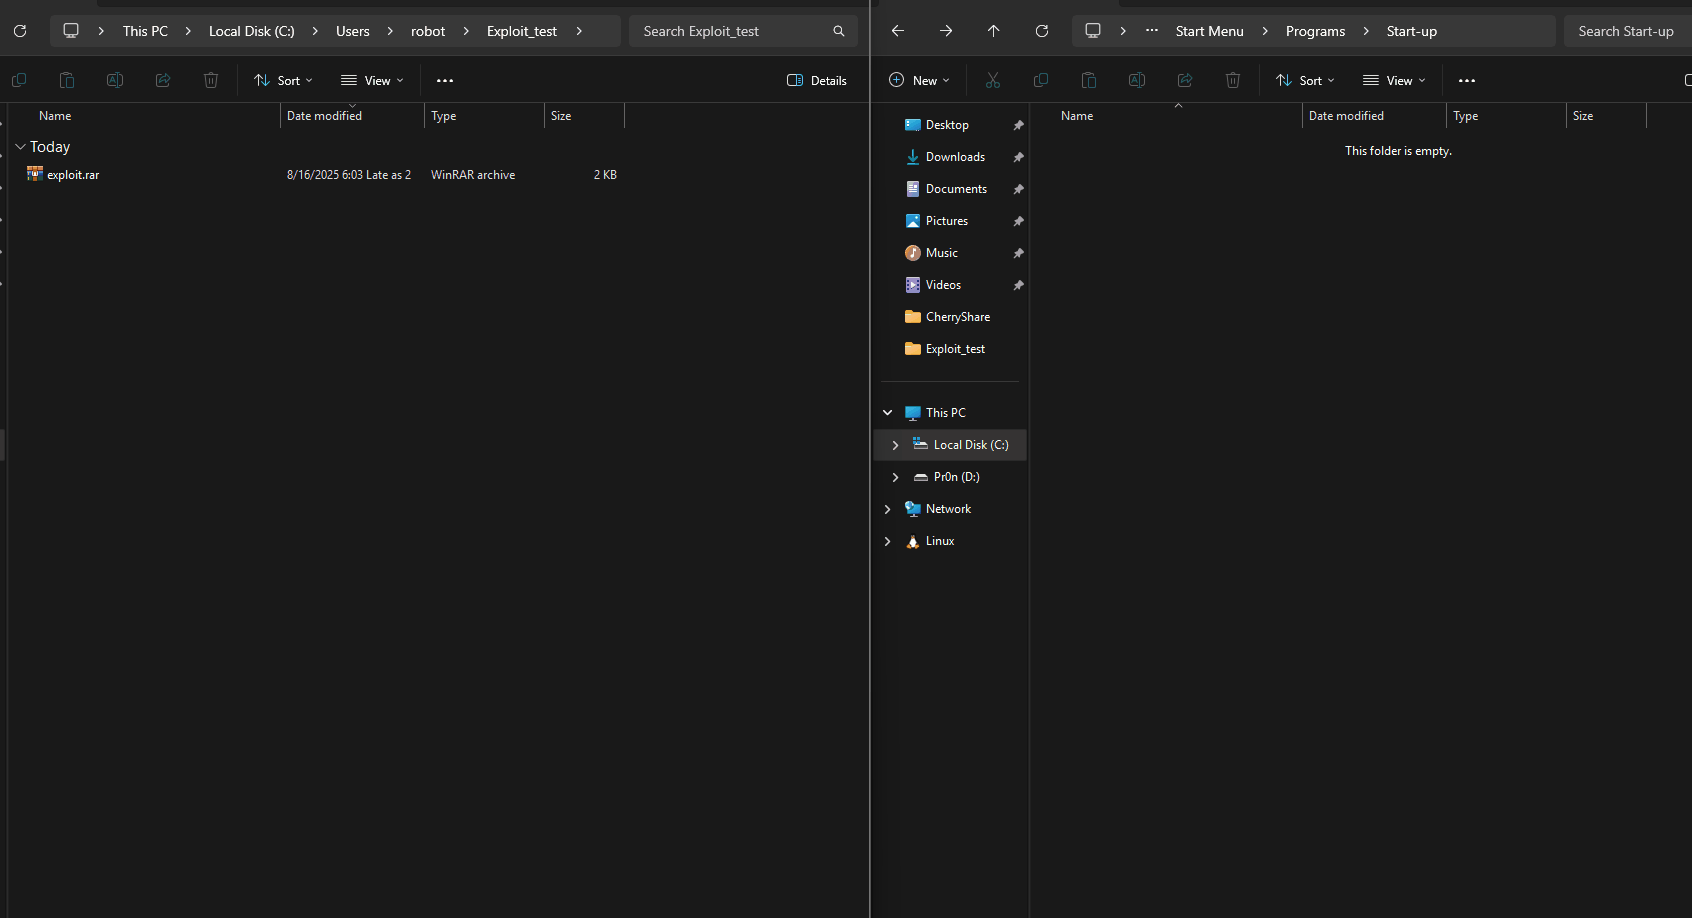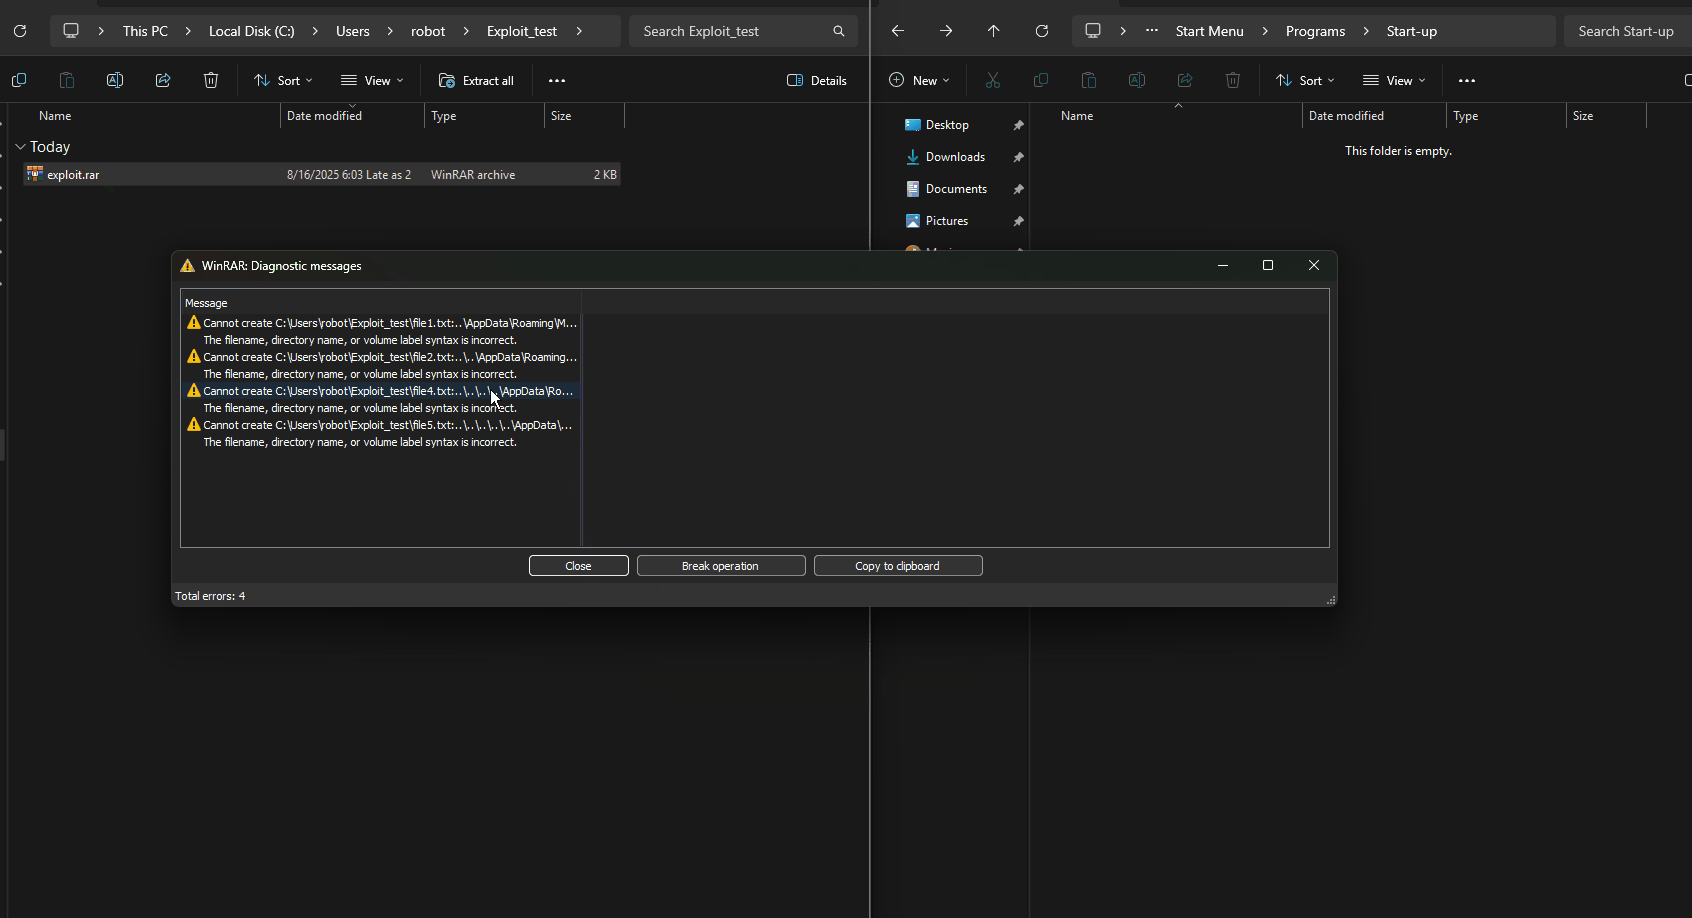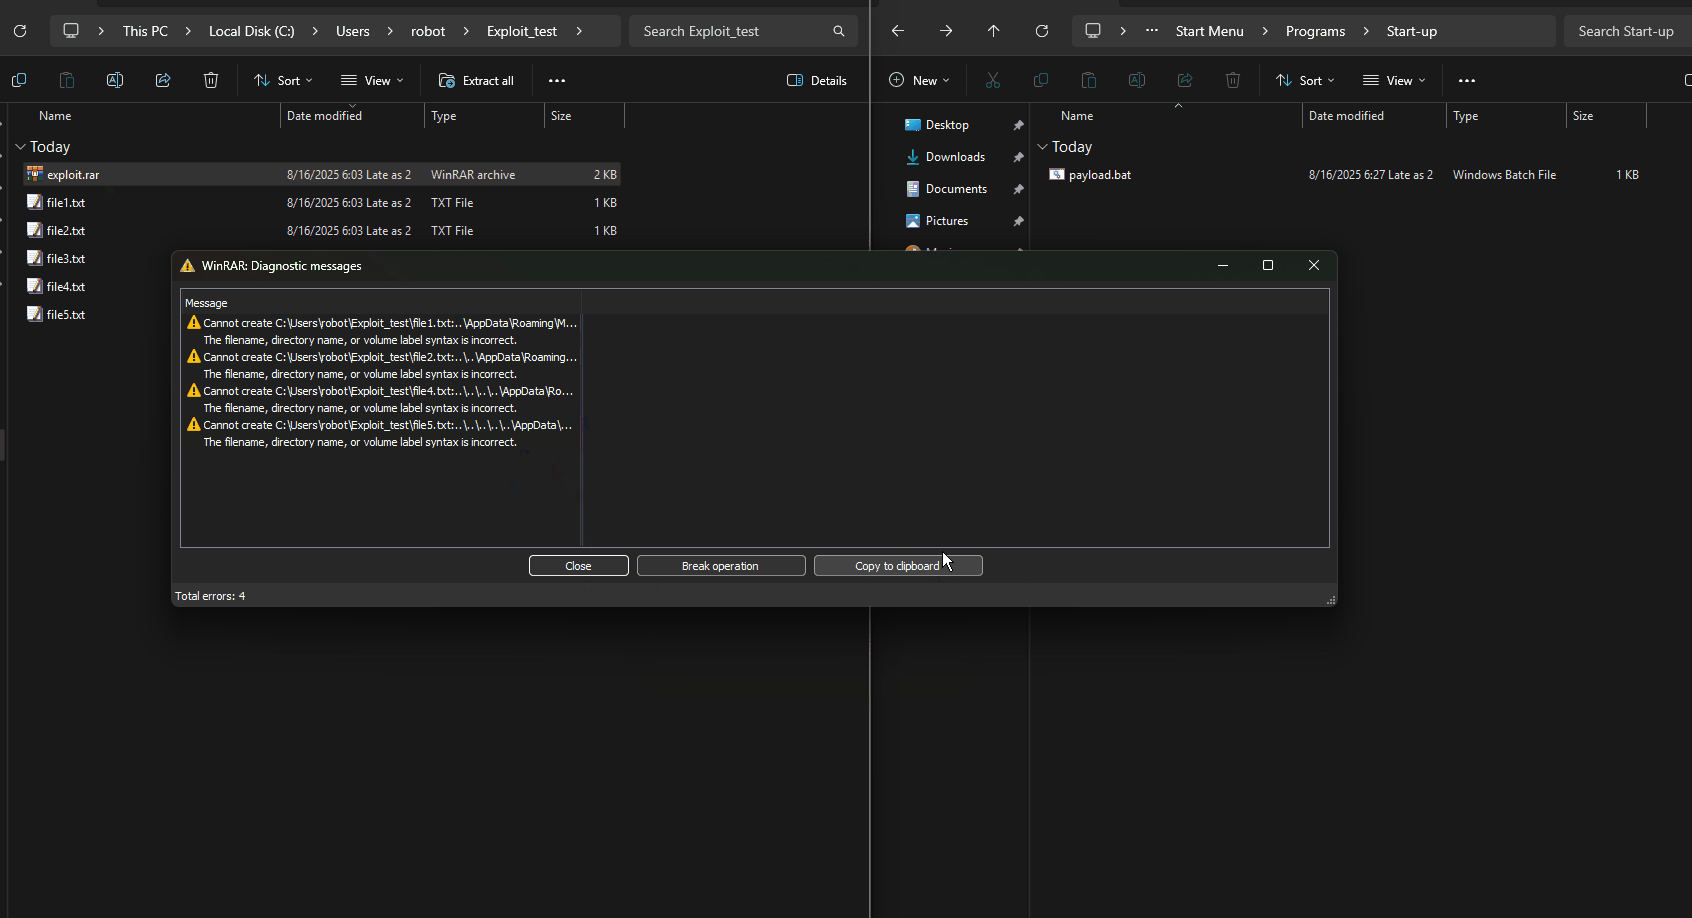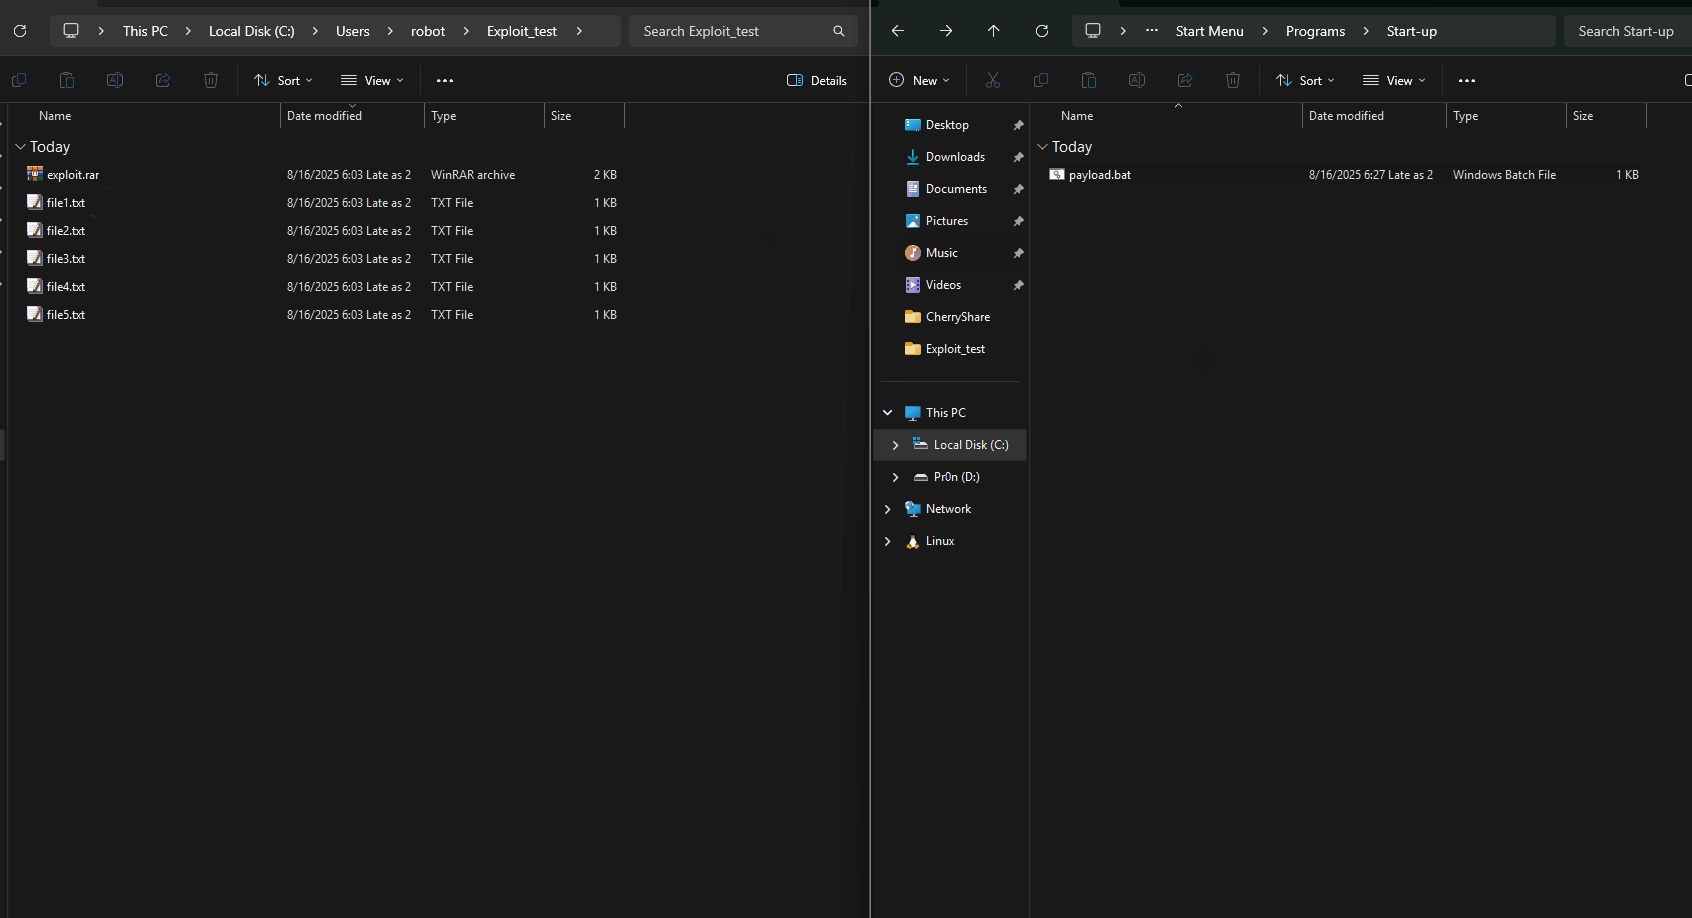 pentestfunctions/cve-2025-8088-multi-document
Exploit systems using older WinRAR without knowing their username (unlike other projects)
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
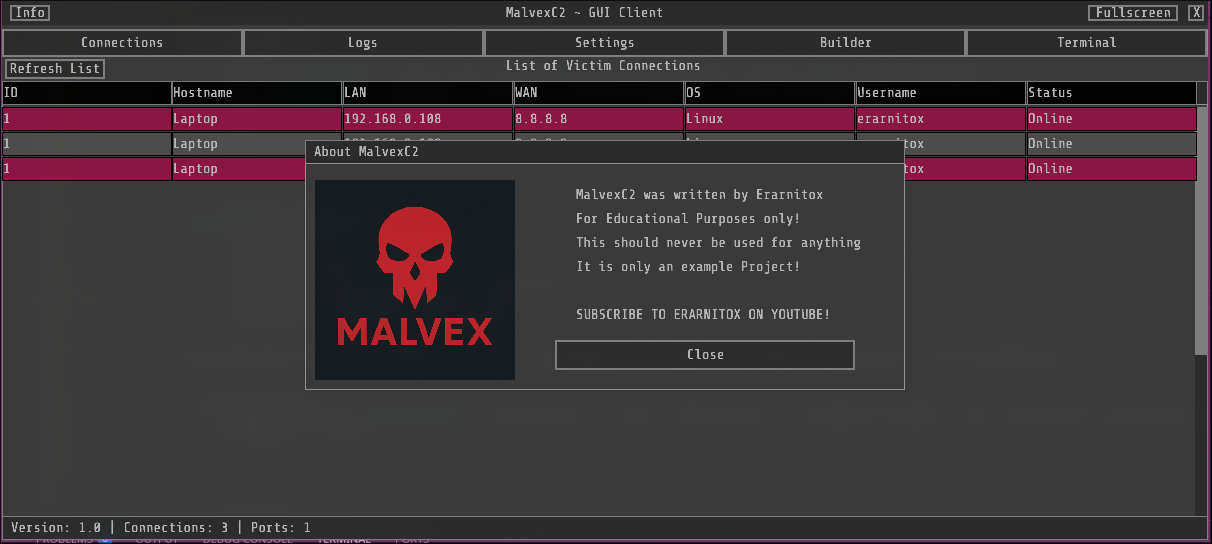 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
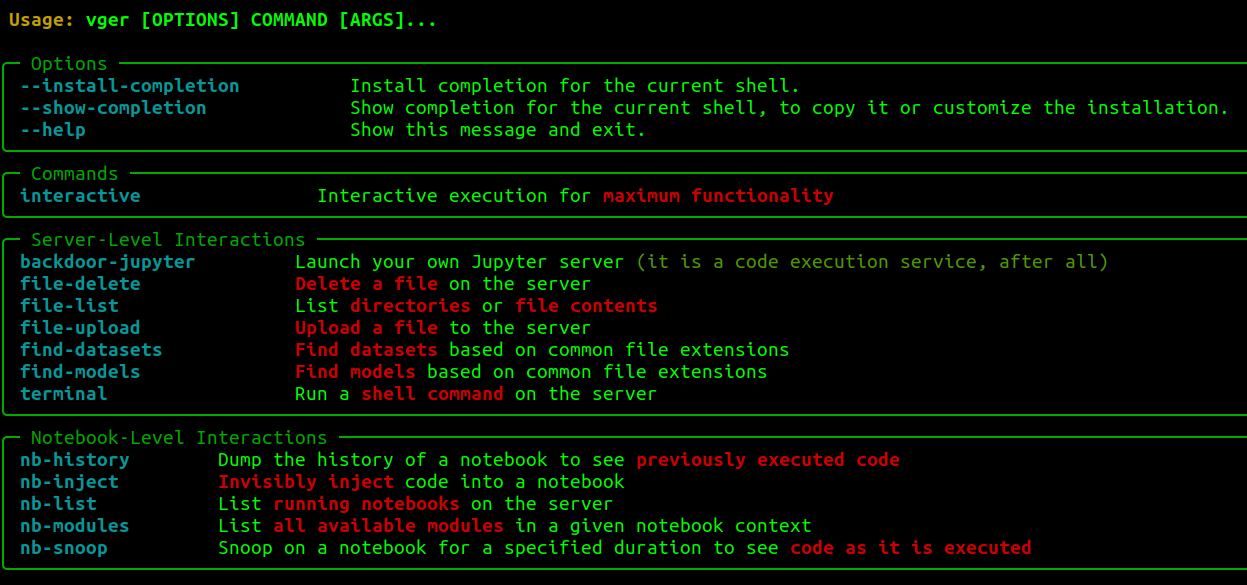 josephtlucas/vger
An interactive CLI application for interacting with authenticated Jupyter instances.
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 gmh5225/dse-patcher
Windows tool that disables Driver Signature Enforcement by patching kernel variables, allowing unsigned drivers to load for testing and research.
 d3adzo/shepard
In progress persistent download/upload/execution tool using Windows BITS.








