
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended
 joelgmsec/autordpwn
The Shadow Attack Framework
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 hakluke/weaponised-xss-payloads
XSS payloads designed to turn alert(1) into P1
 christophetd/log4shell-vulnerable-app
Spring Boot web application vulnerable to Log4Shell (CVE-2021-44228).
 sweetsoftware/ares
Python botnet and backdoor
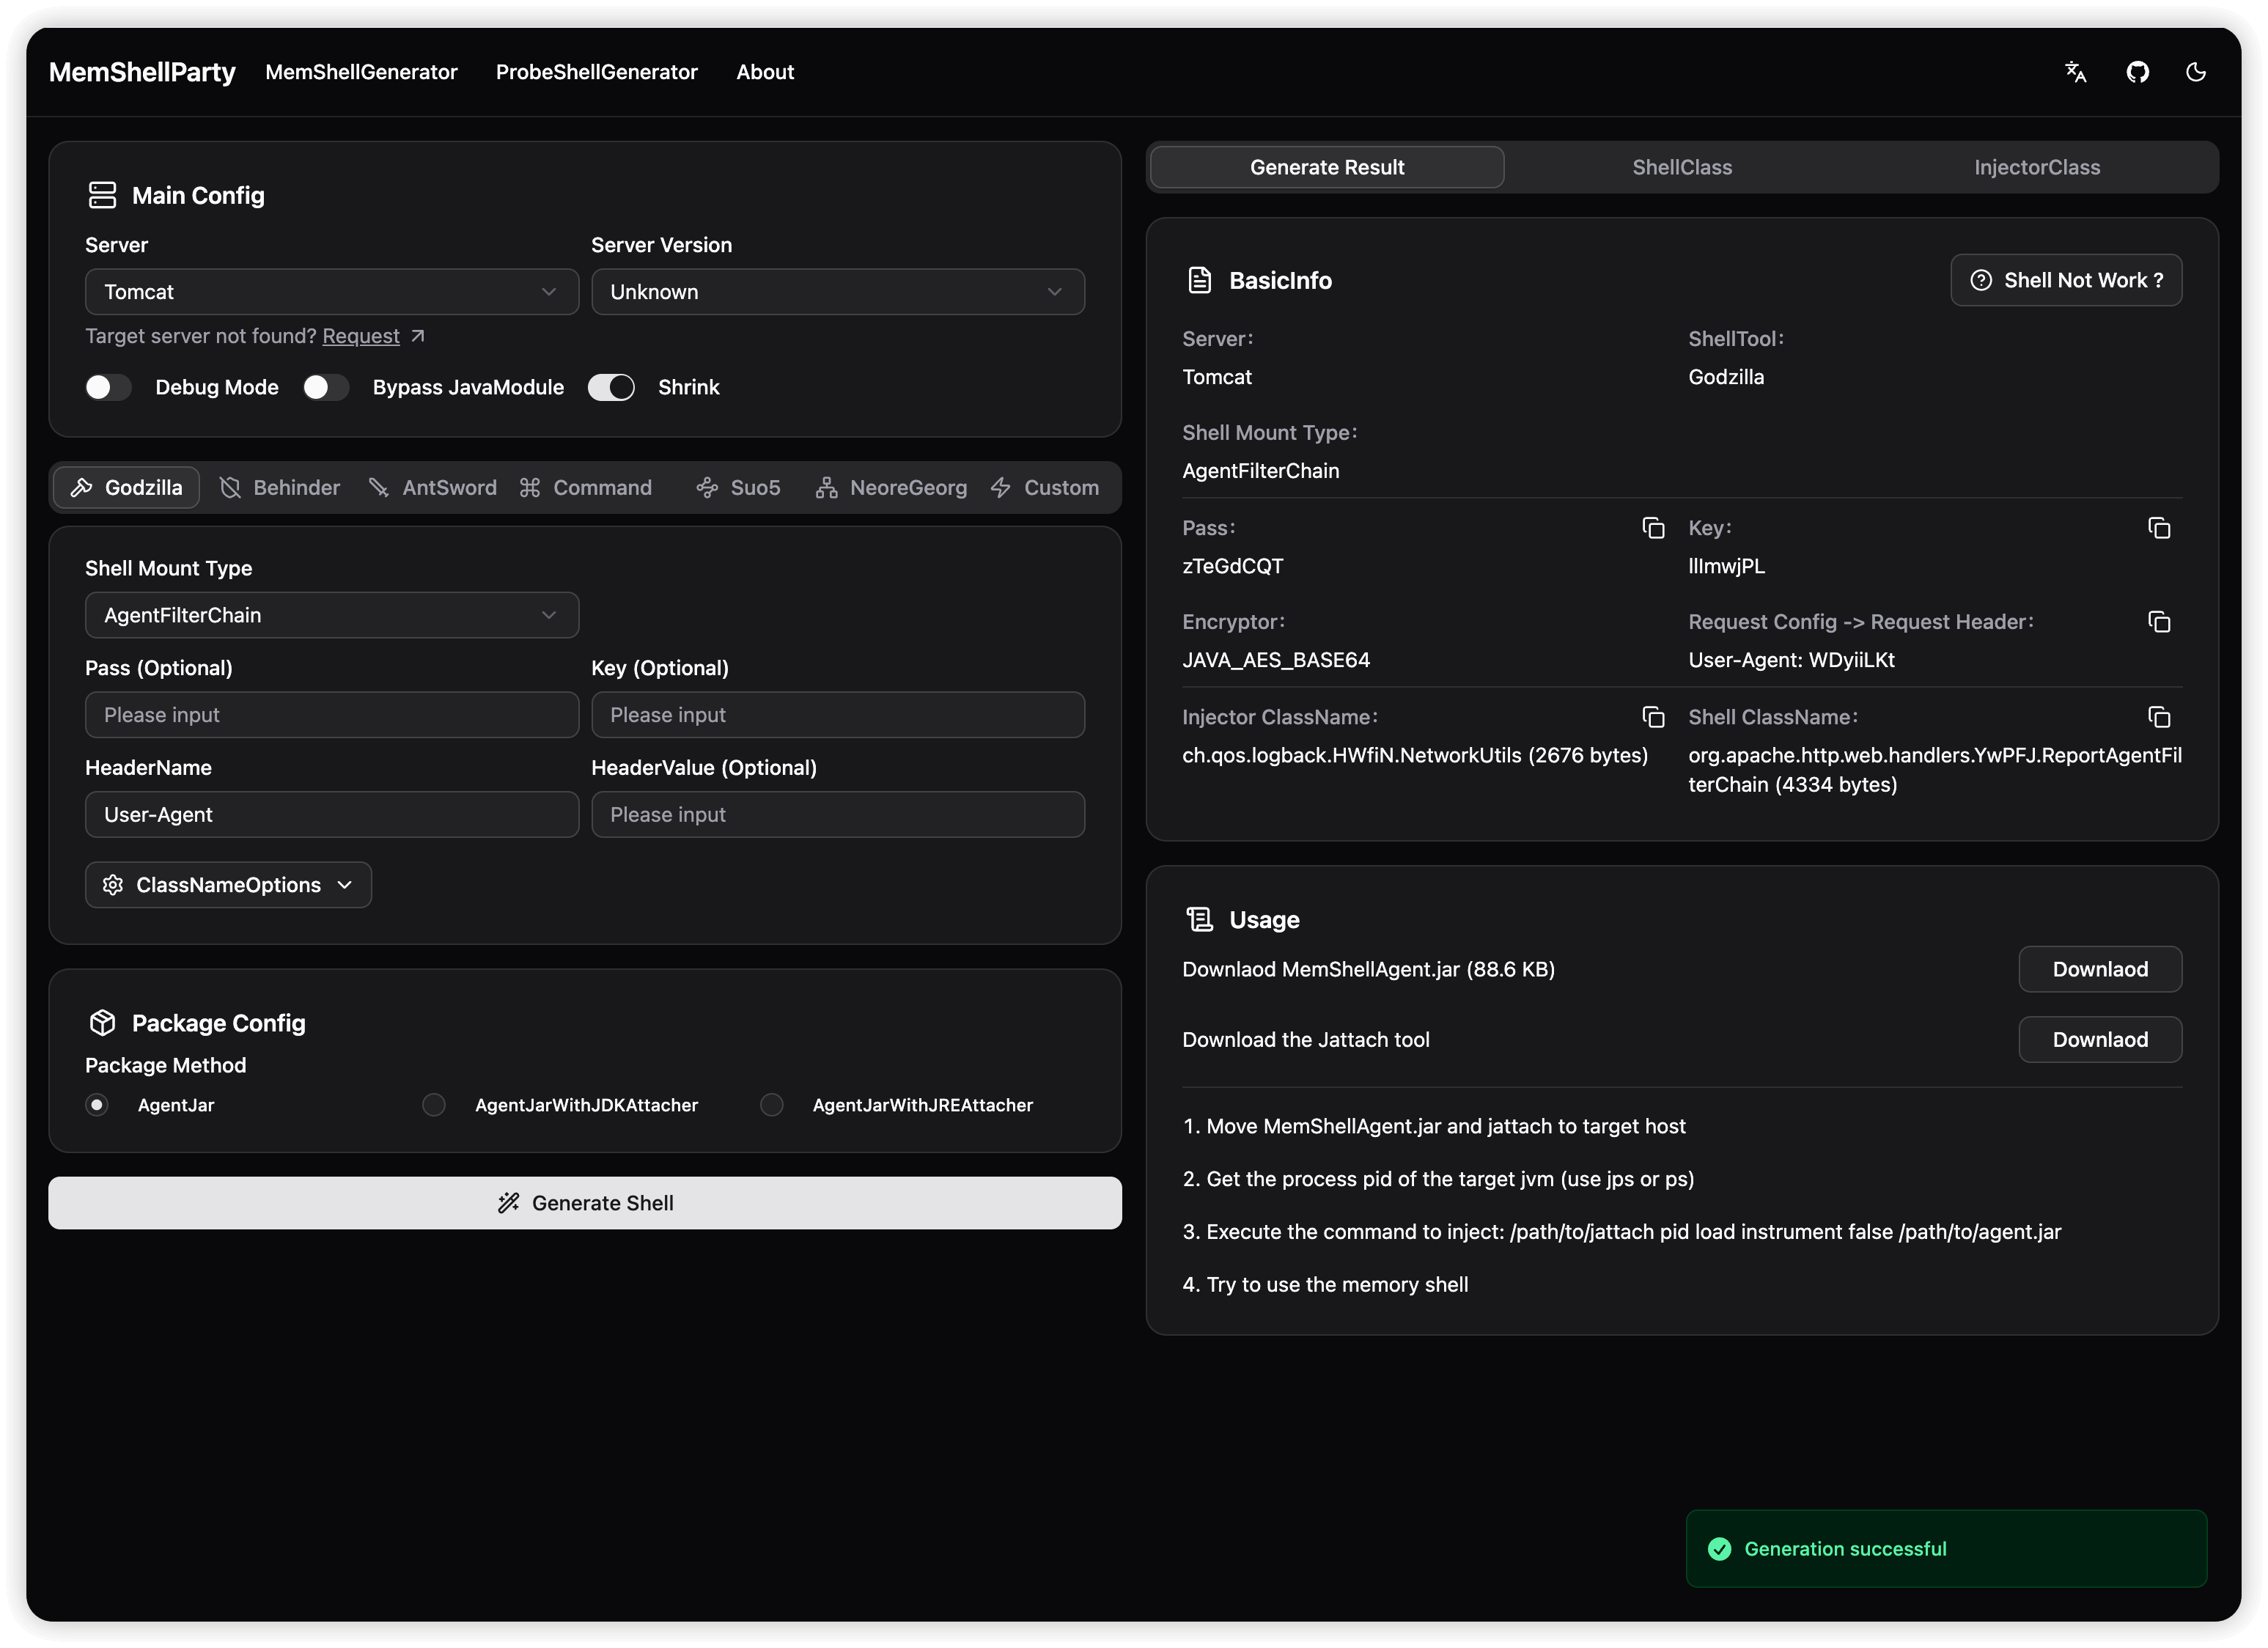 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
 bats3c/shad0w
A post exploitation framework designed to operate covertly on heavily monitored environments
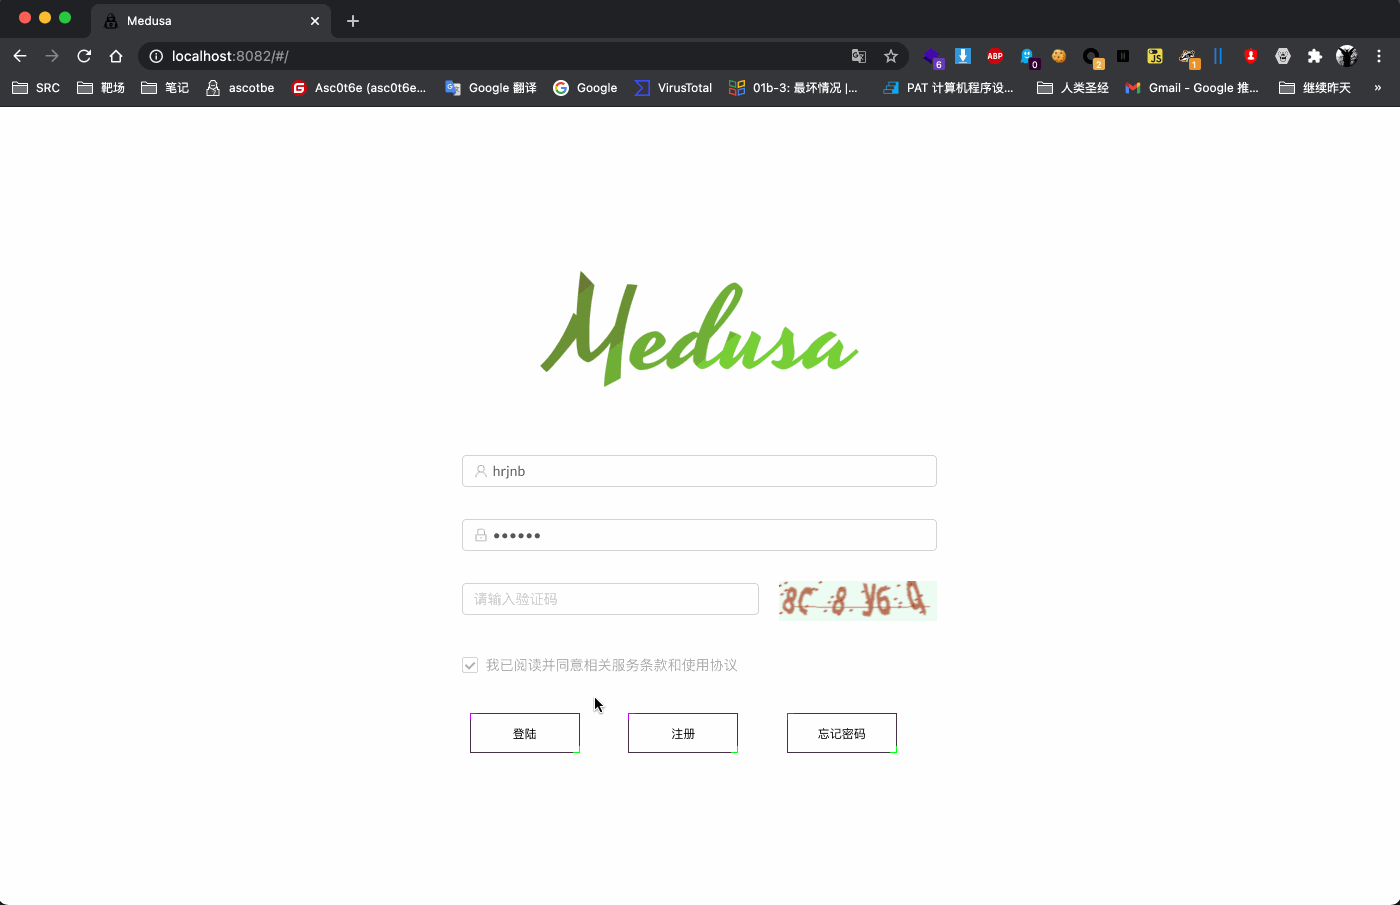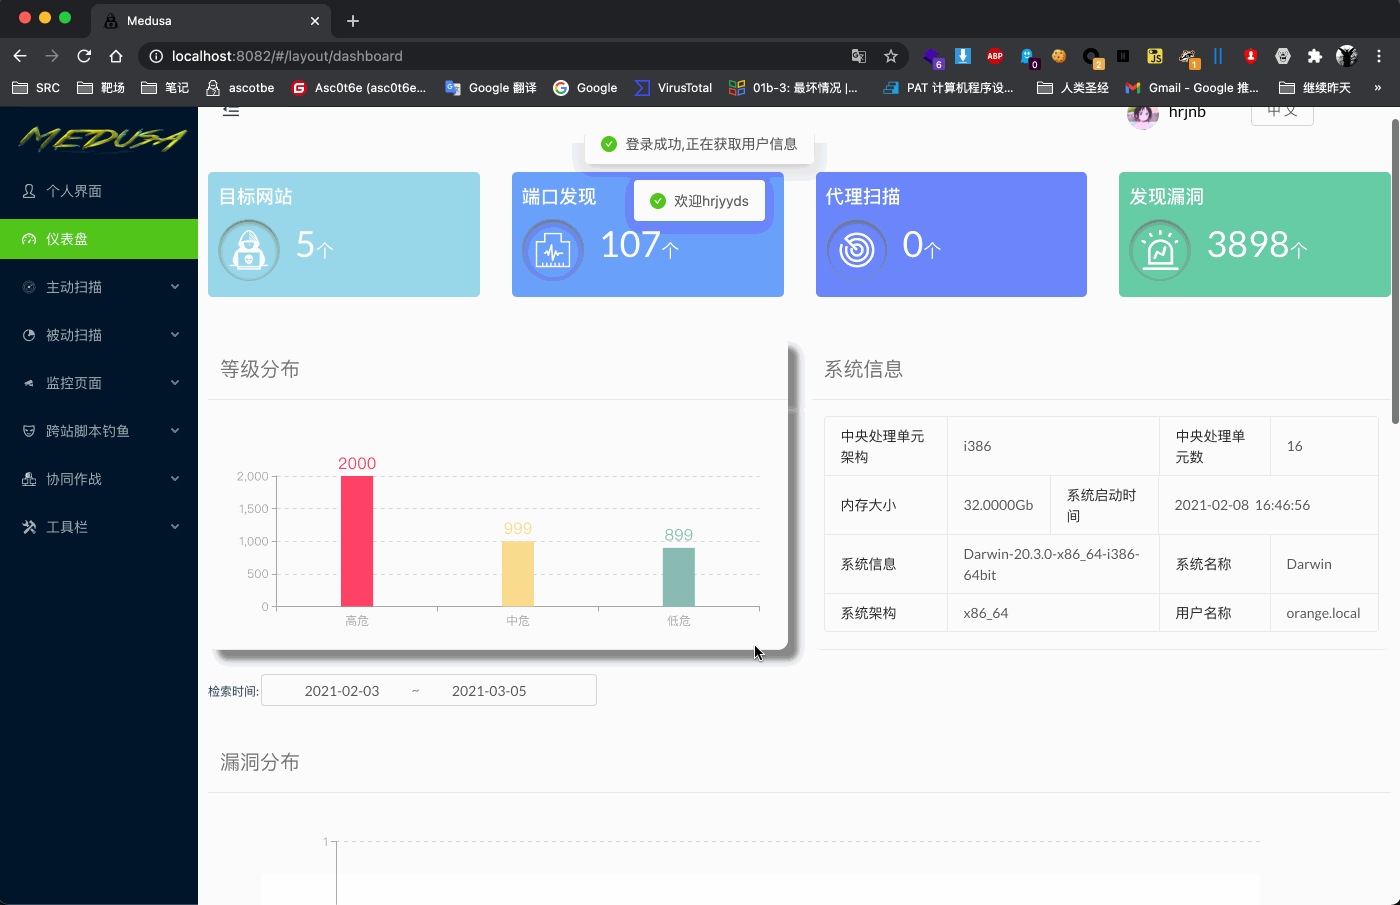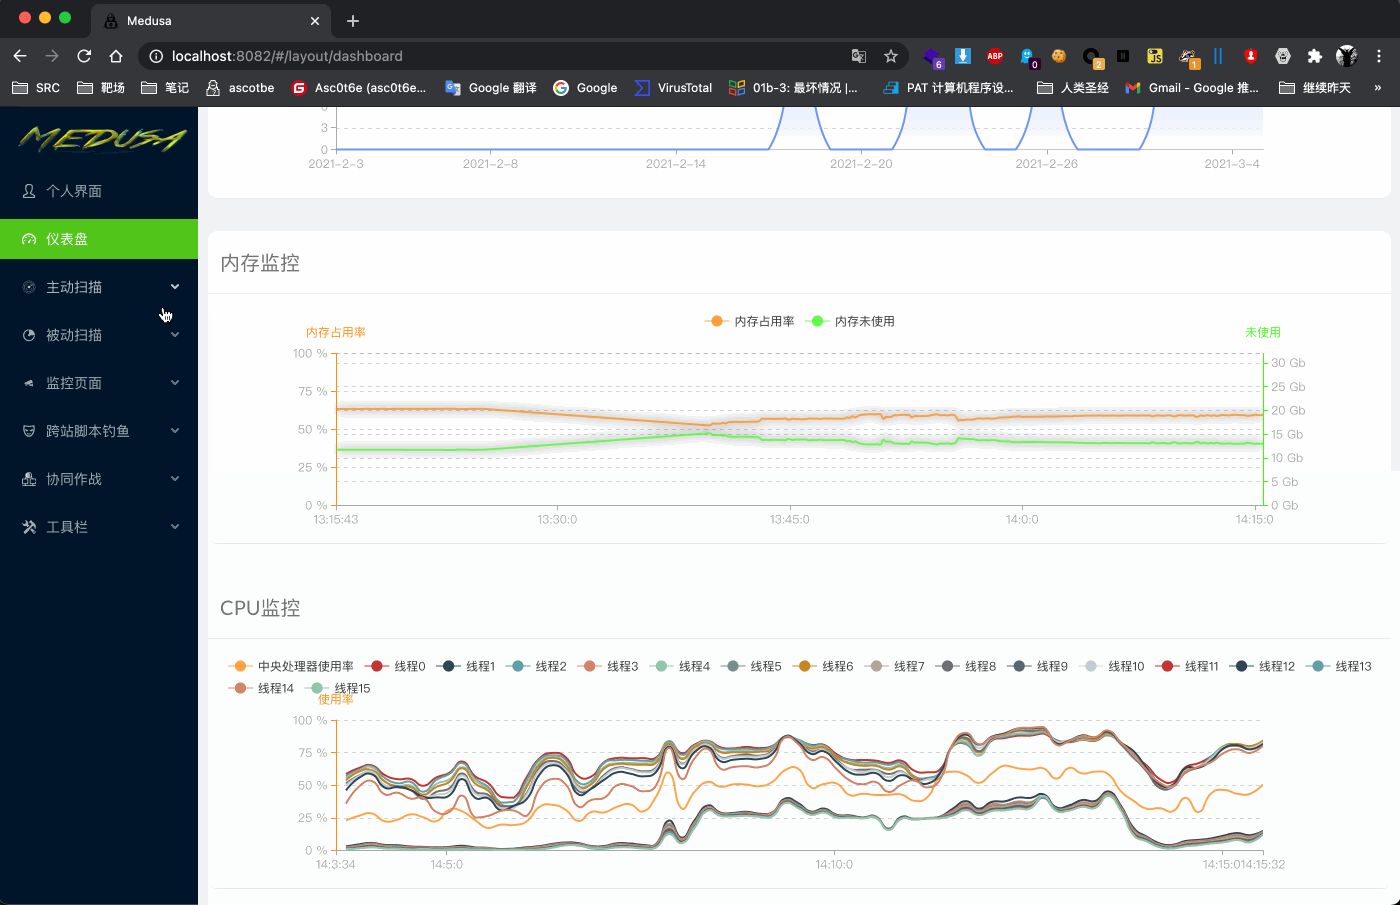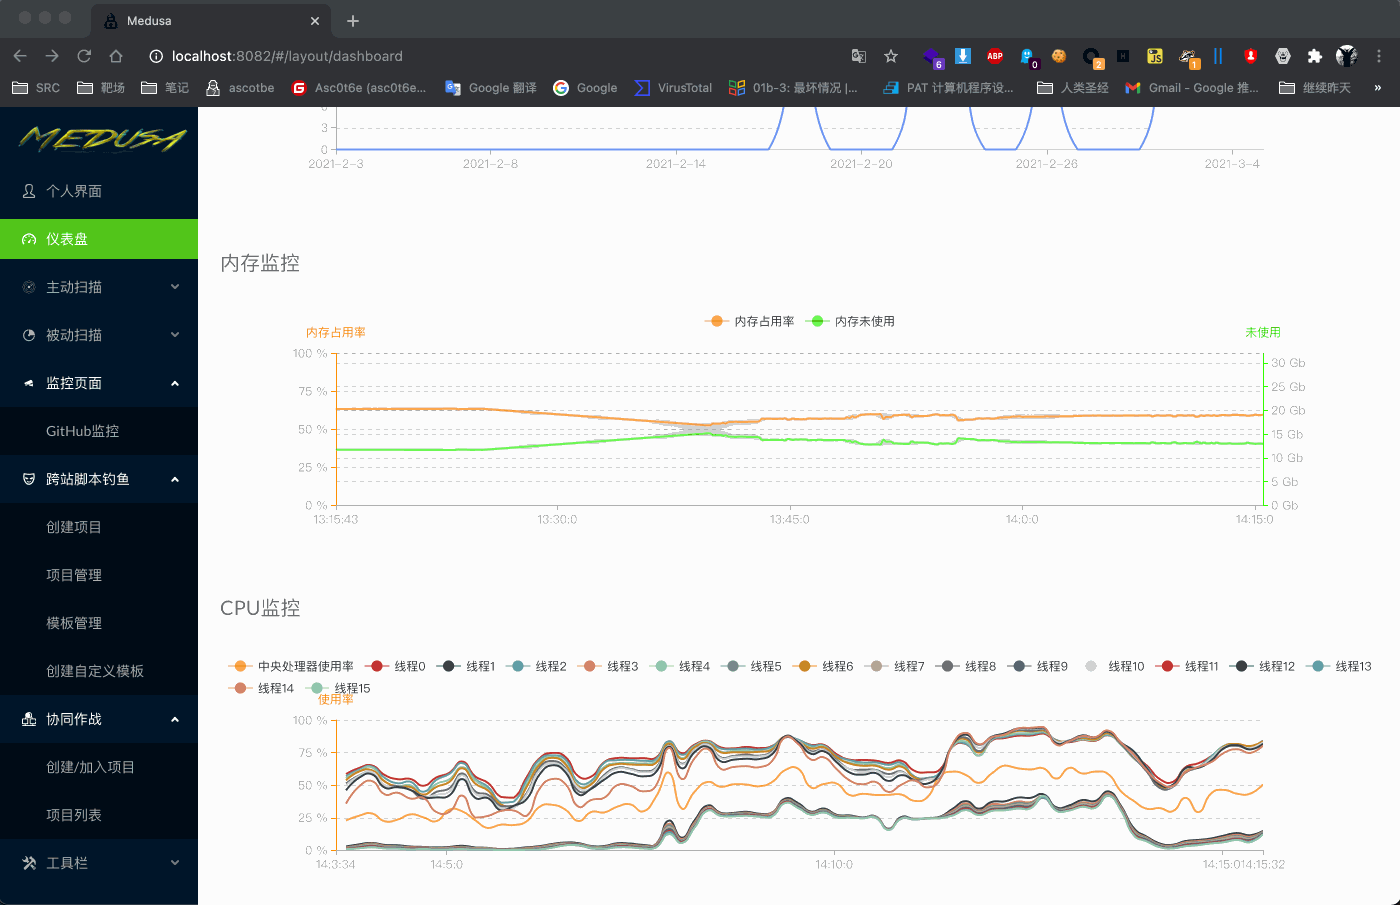 ascotbe/medusa
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
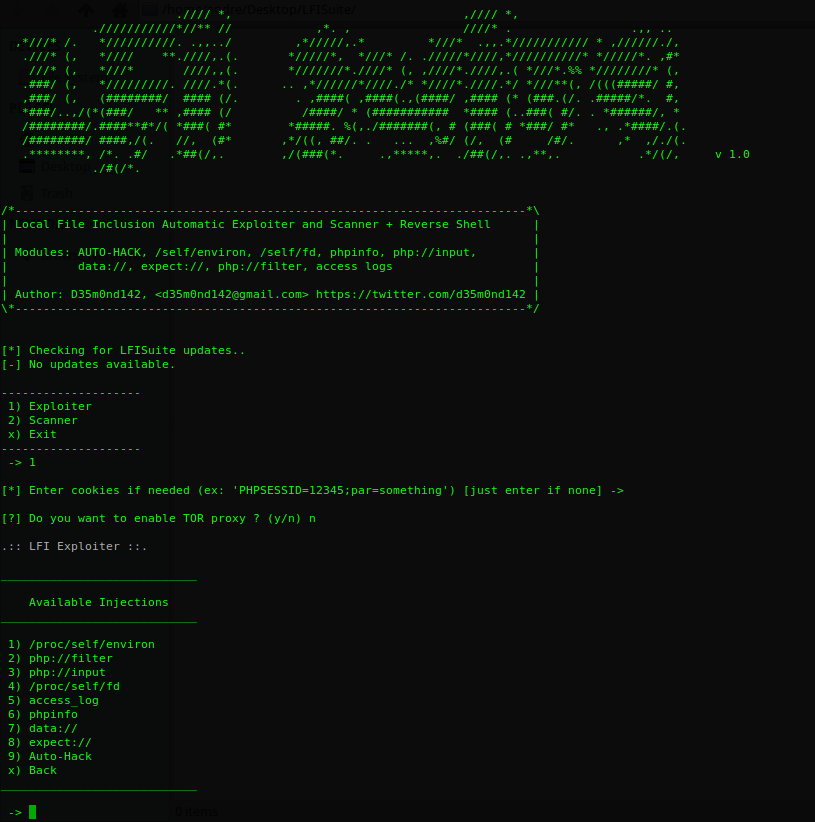 d35m0nd142/lfisuite
Totally Automatic LFI Exploiter (+ Reverse Shell) and Scanner
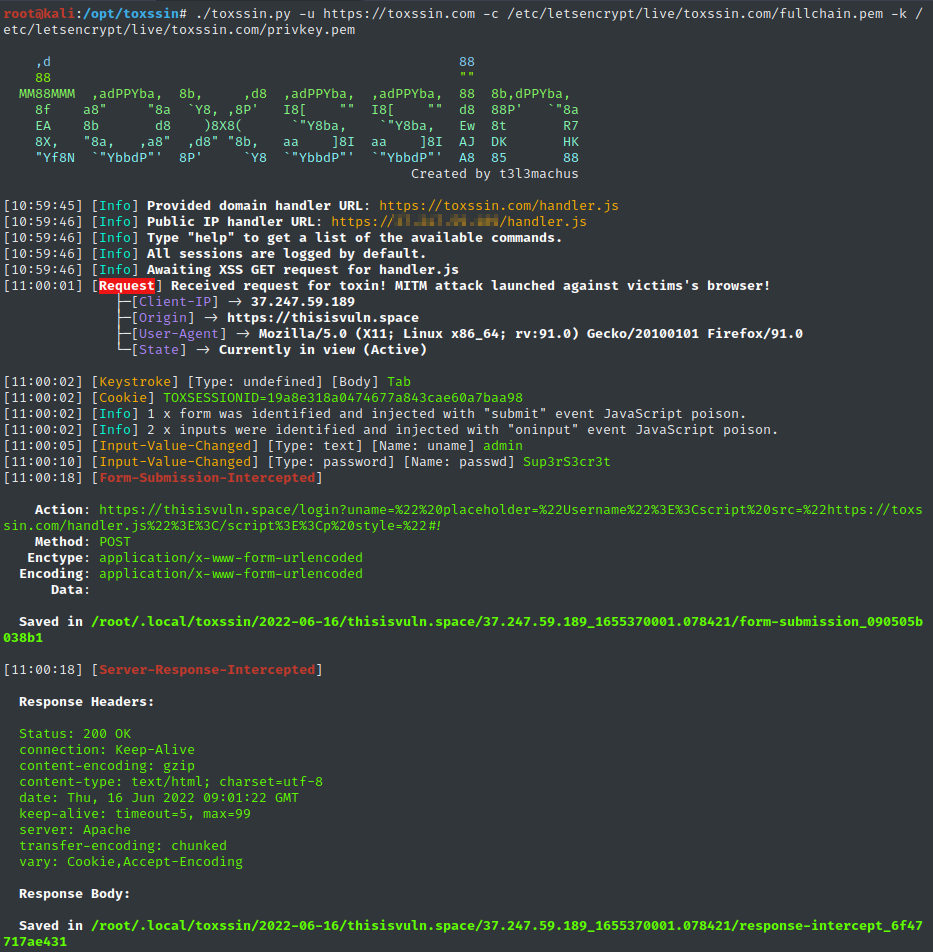 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
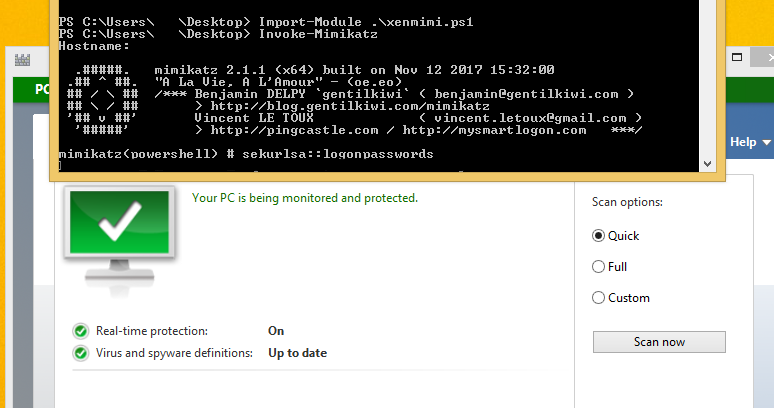 the-xentropy/xencrypt
A PowerShell script anti-virus evasion tool
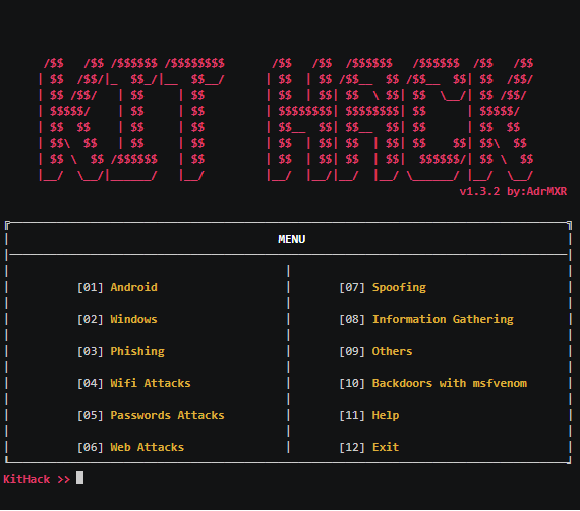 adrmxr/kithack
Hacking tools pack & backdoors generator.
 r00t-3xp10it/fakeimageexploiter
Use a Fake image.jpg to exploit targets (hide known file extensions)
 s3cur3th1ssh1t/offensivevba
This repo covers some code execution and AV Evasion methods for Macros in Office documents
 ne0nd0g/go-shellcode
A repository of Windows Shellcode runners and supporting utilities. The applications load and execute Shellcode using various API calls or techniques.
 ashwin990/adb-toolkit
ADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!








