#1
Tools for recovering passwords from hashes, encrypted sources, or through brute-force/dictionary attacks.
Kitploit recommended
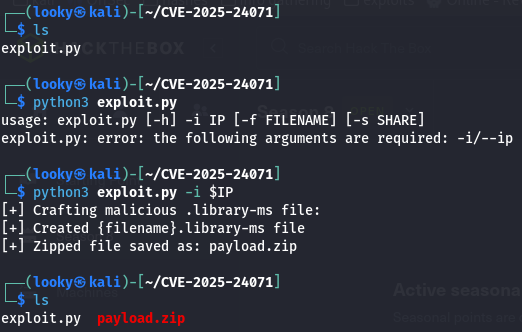
 looky243/cve-2025-24071-poc
CVE-2025-24071 Proof Of Concept
 gmikisilva/cve-2024-33901-proofofconcept
Short program that demonstrates the vulnerability CVE-2024-33901 in KeePassXC version 2.7.7
 okymi-x/cve-2021-43798
Python toolkit for authorized testing of CVE-2021-43798 Grafana path traversal, with arbitrary file read PoC, secret decryption, and user hash export…
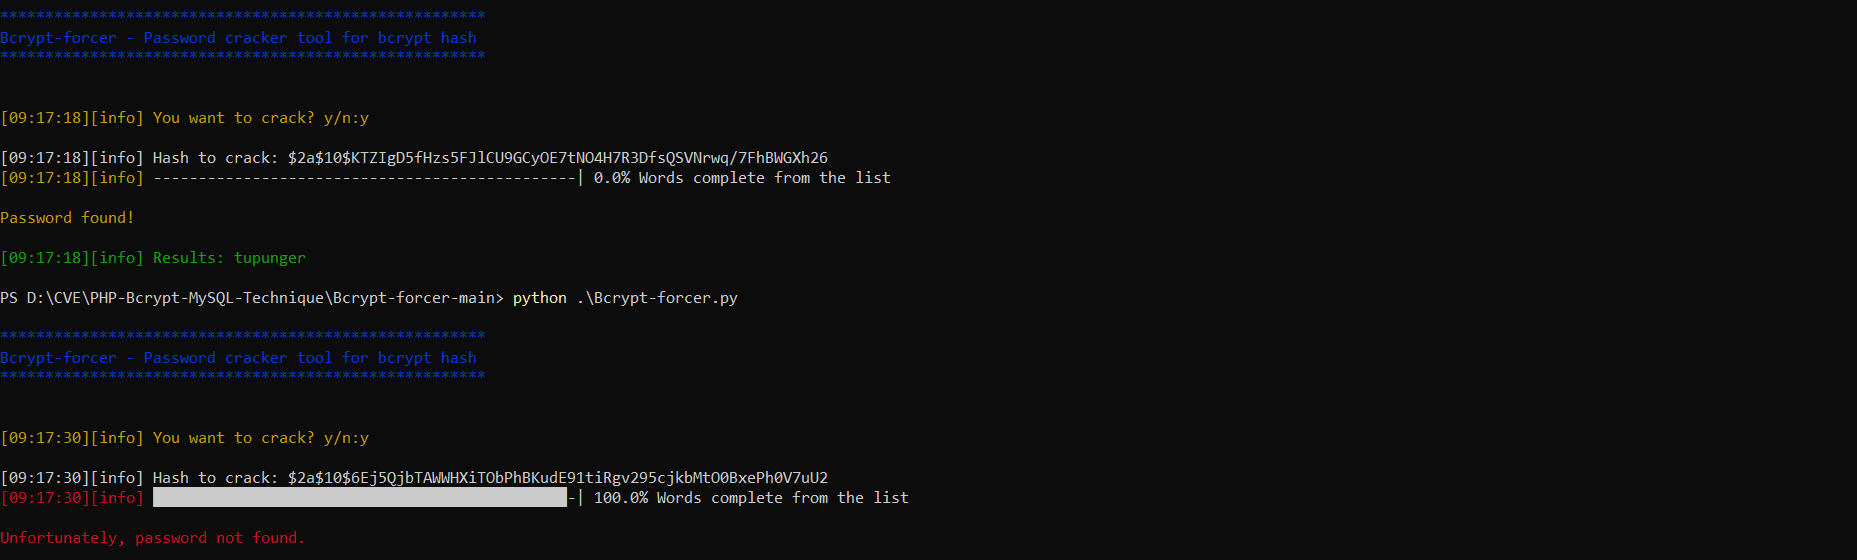 nu11secur1ty/bcrypt-forcer
Bcrypt hash cracker for penetration testing and password recovery. Decrypts Bcrypt hashes using dictionary or brute-force methods.
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 gurleen-147/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability-poc
This repository contains research notes and a high-level proof-of-concept (PoC) for CVE-2024-21413, a vulnerability observed in certain mail clients…
 petergabaldon/cve-2024-1346
Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…
 jagdeepsinghceh/cms-made-simple-python3
Python3-converted exploit and research notes for CMS Made Simple (CVE-2019-9053) — Unauthenticated SQL Injection vulnerability. Includes original…
 xk3nf4/cve-2022-25012
Argus Surveillance DVR v4.0 employs weak password encryption.
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 wrathfuldiety/zerologon
zerologon script to exploit CVE-2020-1472 CVSS 10/10
 vatsal200600/stegolab
All-in-one Image Steganography Toolkit for CTFs & Forensics
 p1ckzi/cve-2022-35513
CVE-2022-35513 | blink1-pass-decrypt
 bilalbaraz/passgen
Generate passwords from the terminal
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
 an00brektn/shirocrack
Simple hash cracker for Apache Shiro hashes written in Golang. Useful for exploiting CVE-2024-4956.
 gquere/cve-2018-16987
Technical disclosure of CVE-2018-16987: cleartext storage of external service passwords in Squash TM administration panel, with CVSS 4.1 scoring and…
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)