
 #1
Tools for recovering passwords from hashes, encrypted sources, or through brute-force/dictionary attacks.
Kitploit recommended

 00xglitch/bella
Bella is a pure python post-exploitation data mining tool & remote administration tool for macOS. 🍎💻
 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 mstxq17/cve-2020-1472
cve-2020-1472 复现利用及其exp
 moneertv/cve-2023-23397
CVE-2023-23397 C# PoC
 nitinronge91/extracting-user-credentials-for-web-portal-and-wifi-ap-for-hathway-router-cve-2024-44815-
CVE-2024-44815
 pointedsec/cve-2024-44541
This repository details a SQL Injection vulnerability in Inventio Lite v4's, including exploitation steps and a Python script to automate the attack.…
 s3l33/cve-2022-25012
Updated version of this weak password encryption script
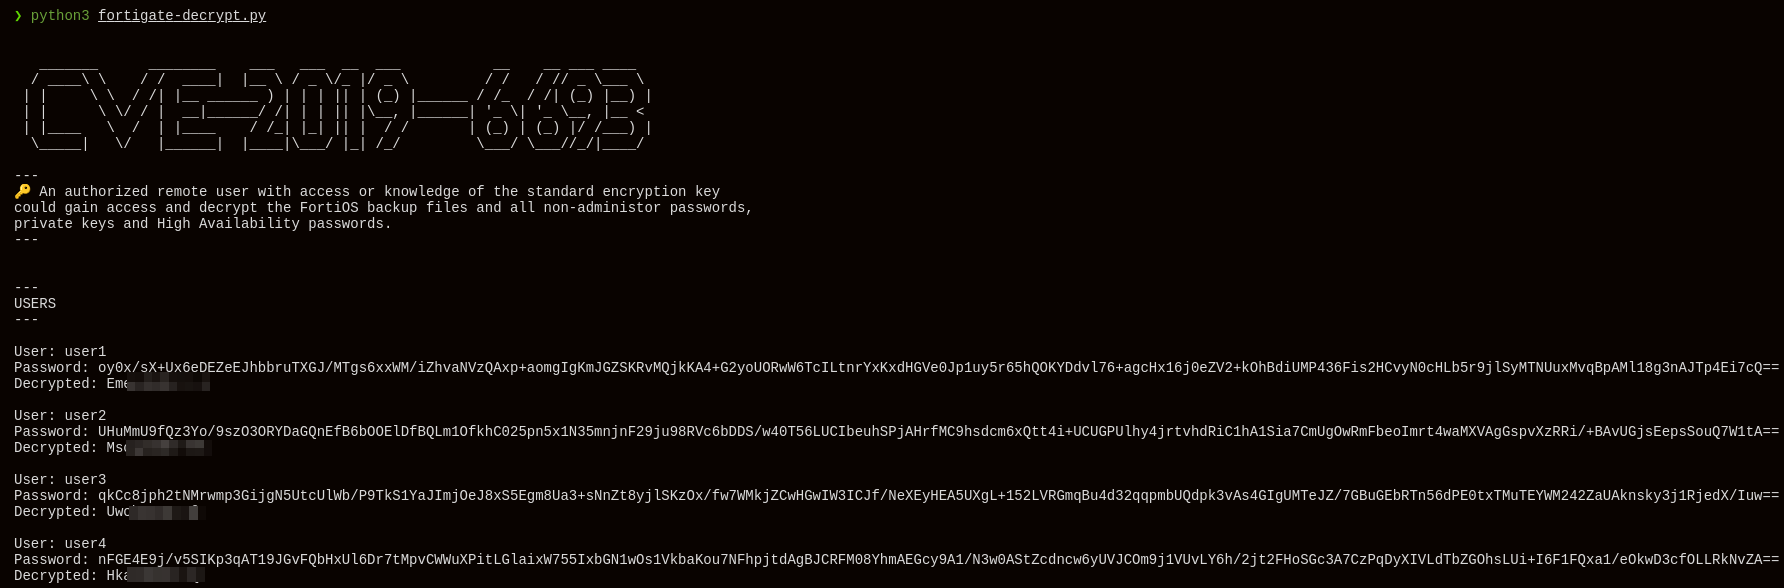 saladandonionrings/cve-2019-6693
An authorized remote user with access or knowledge of the standard encryption key can gain access and decrypt the FortiOS backup files and all…
 tamim1089/hikvisionexploiter
HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…
 und3sc0n0c1d0/bruteforce-to-keepass
This script complements the results obtained through the keepass-password-dumper tool when exploiting the CVE-2023-32784 vulnerability affecting…
 verylazytech/cve-2024-24919
POC - CVE-2024–24919 - Check Point Security Gateways
 verylazytech/cve-2024-4956
POC - CVE-2024–4956 - Nexus Repository Manager 3 Unauthenticated Path Traversal
 wiliam227user/cve-2018-12633-tplink-auth-bypass
A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
 yass2400012/email-exploit-moniker-link-cve-2024-21413-
Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…
 z-bool/venom-jwt
针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)
 z-jxy/keepass_dump
KeePass 2.X dumper (CVE-2023-32784)
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 deshanfer94/cve-2025-24071-poc-ntlmhashdisclosure-
CVE-2025-24071: NTLMv2 Hash Disclosure via .library-ms File








