
 #1
Tools for recovering passwords from hashes, encrypted sources, or through brute-force/dictionary attacks.
Kitploit recommended

 bilalbaraz/passgen
Generate passwords from the terminal
 ishaklaz/hash-eye
**HashEye** is a powerful Python CLI tool for instantly detecting and analyzing hash types. It provides detailed information about hash formats,…
 creusvictor/keepassxc-fzf
A lightweight CLI tool to interactively search and access your KeePassXC database entries using fzf. Fast, secure, and terminal-centric.
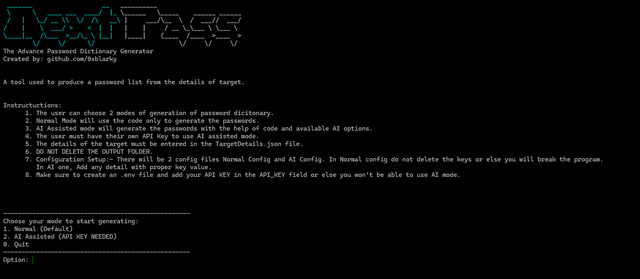 0xblarky/nextpass
A tool which can be used to generate password list or dictionary from the details of the target
 aaravmaloo/apm
A local password manager for everyone
 ottoyrocky/phantom-brain
Red portatil de reconocimiento inteligente con IA offline
 s1lkys/cve-2023-30367-mremoteng-password-dumper
Original PoC for CVE-2023-30367
 rinaliyeva/metasploitable2-vsftpd-exploitation
Project: vsFTPd 2.3.4 backdoor exploitation (CVE-2011-2523) on Metasploitable 2.
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 bytehackr/keepass_poc
POC for KeePass [CVE-2022-0725]
 boon-rekcah/cms-made-simple-2.2.9-cve-2019-9053
Python 3 exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks…
 0ldev/politician
Modern WiFi auditing library for ESP32 using advanced 802.11 techniques. Captures WPA/WPA2/WPA3 handshakes via PMKID extraction and CSA injection…
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 an00brektn/shirocrack
Simple hash cracker for Apache Shiro hashes written in Golang. Useful for exploiting CVE-2024-4956.
 abdelrahman0sayed/cve-2025-24071
This is a python PoC scripts for CVE-2025-24071 which is a vulnerability in Windows File Explorer that allows unauthorized access to sensitive…
 ac8999/cve-2025-24071
Python script to execute CVE-2025-24071
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
 0xcccc666/cve-2020-1472_tool-collection
cve-2020-1472_Tool collection








