
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 hibanitt/cve-2024-38063
In-depth technical analysis and proof-of-concept for CVE-2024-38063, a critical Windows IPv6 kernel RCE. Includes root-cause breakdown, Scapy-based…
 oscerd/cve-2026-59230
Proof-of-concept reproducers for Apache Camel camel-mail MimeMultipart header injection (CVE-2026-59230), demonstrating SSRF via CamelHttpUri…
 dingo97/cve-2026-20516
Write-up and ADB proof of concept for CVE-2026-20516, a confused deputy flaw in MediaTek Android TV MiracastService allowing local Wi-Fi Direct state…
 oscerd/cve-2026-60093
Proof-of-concept reproducers for Apache Camel path traversal vulnerability (CVE-2026-60093) in camel-azure-storage-datalake, demonstrating arbitrary…
 sweatyrocket/huawei-p10-cve-2017-8890-unlock
Huawei P10 VTR-L29C432B151 CVE-2017-8890 exploit research and bootloader-unlock journey
 ak777177/dirty-frag-analysis
Dirty Frag (CVE-2026-43284/43500) - Linux Kernel LPE Deep Technical Analysis by Bomb
 theopaid/cve-2026-66730-infinite-loop-dos-in-facil.io-mime-parser
Security Advisory: Infinite Loop DoS in facil.io MIME Parser (Partial Boundary)
 harshrajsinghania/cve-2026-86547-mrubyc-op-enter
Standalone proof of concept for CVE-2026-86547, a NULL pointer dereference in mrubyc op_enter() through 4.0.0.
 brunoteixeira1996/cve-2023-36250
Proof-of-concept for CSV injection in GNOME Time Tracker 3.0.2, demonstrating arbitrary code execution via crafted .tsv files and formula injection.
 lucabarile/zdi-can-16857
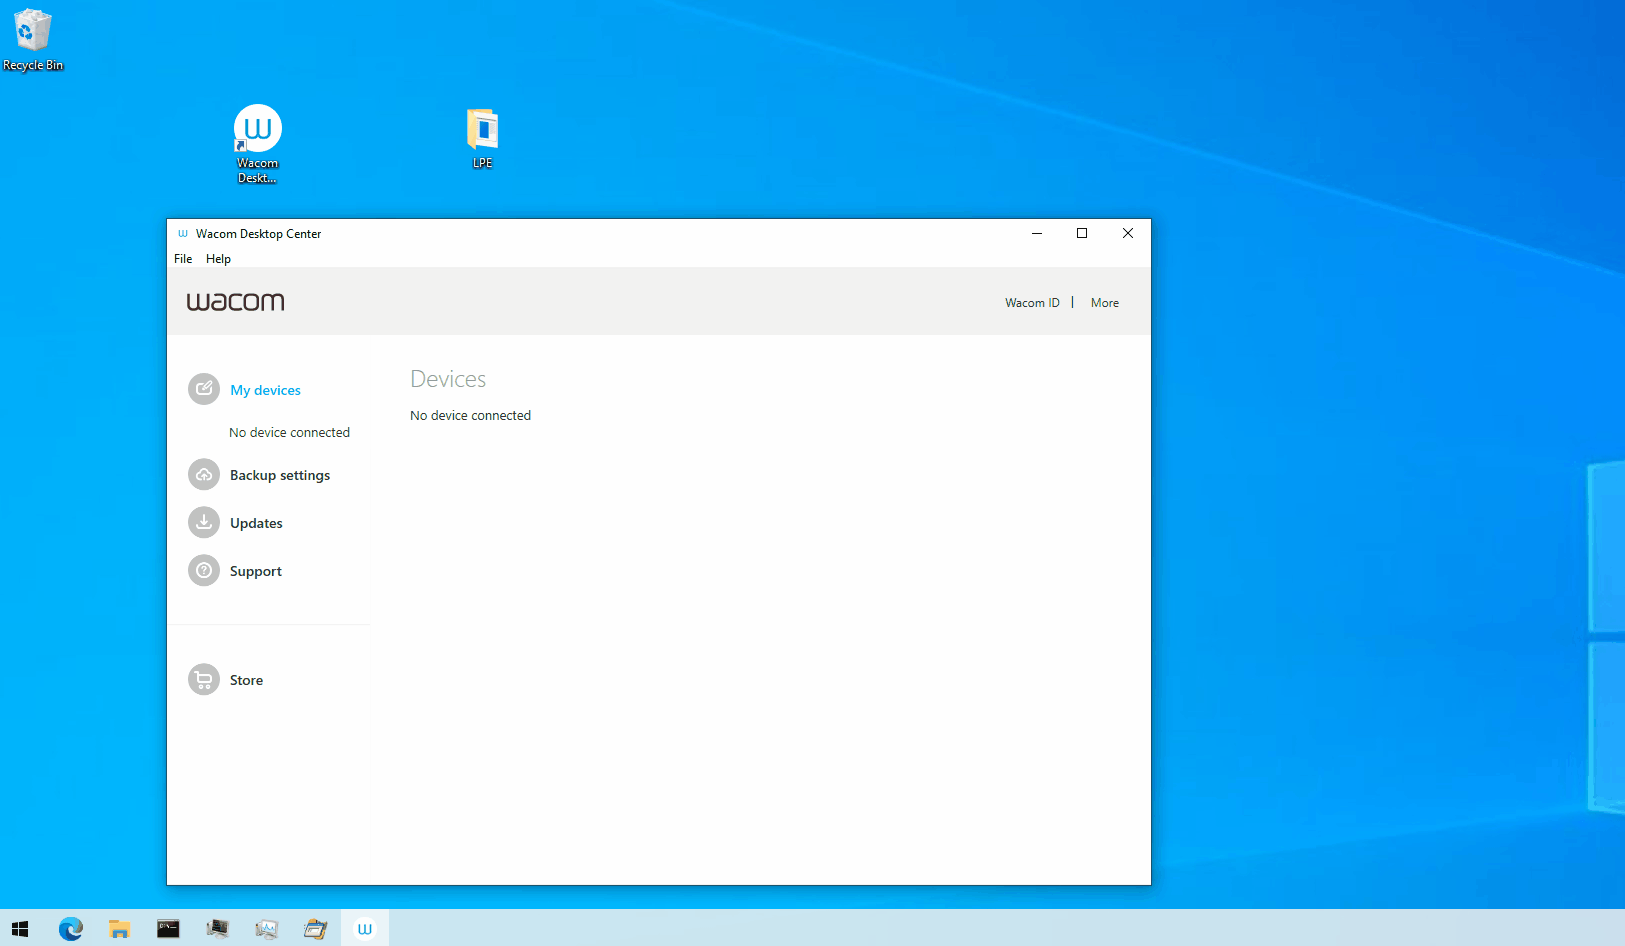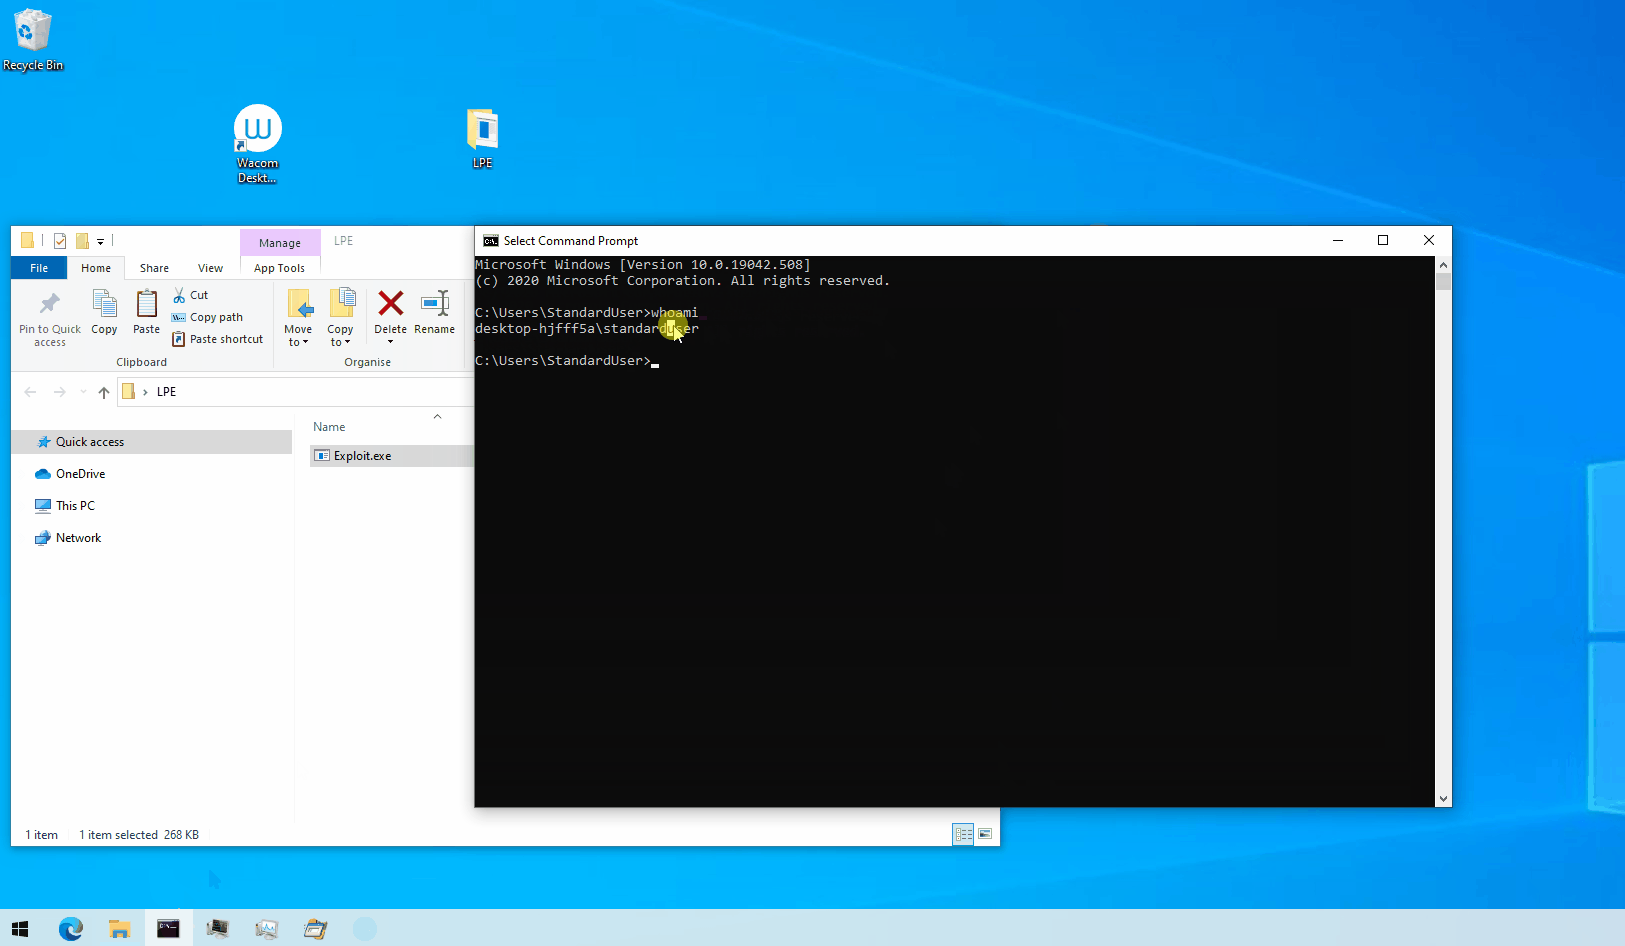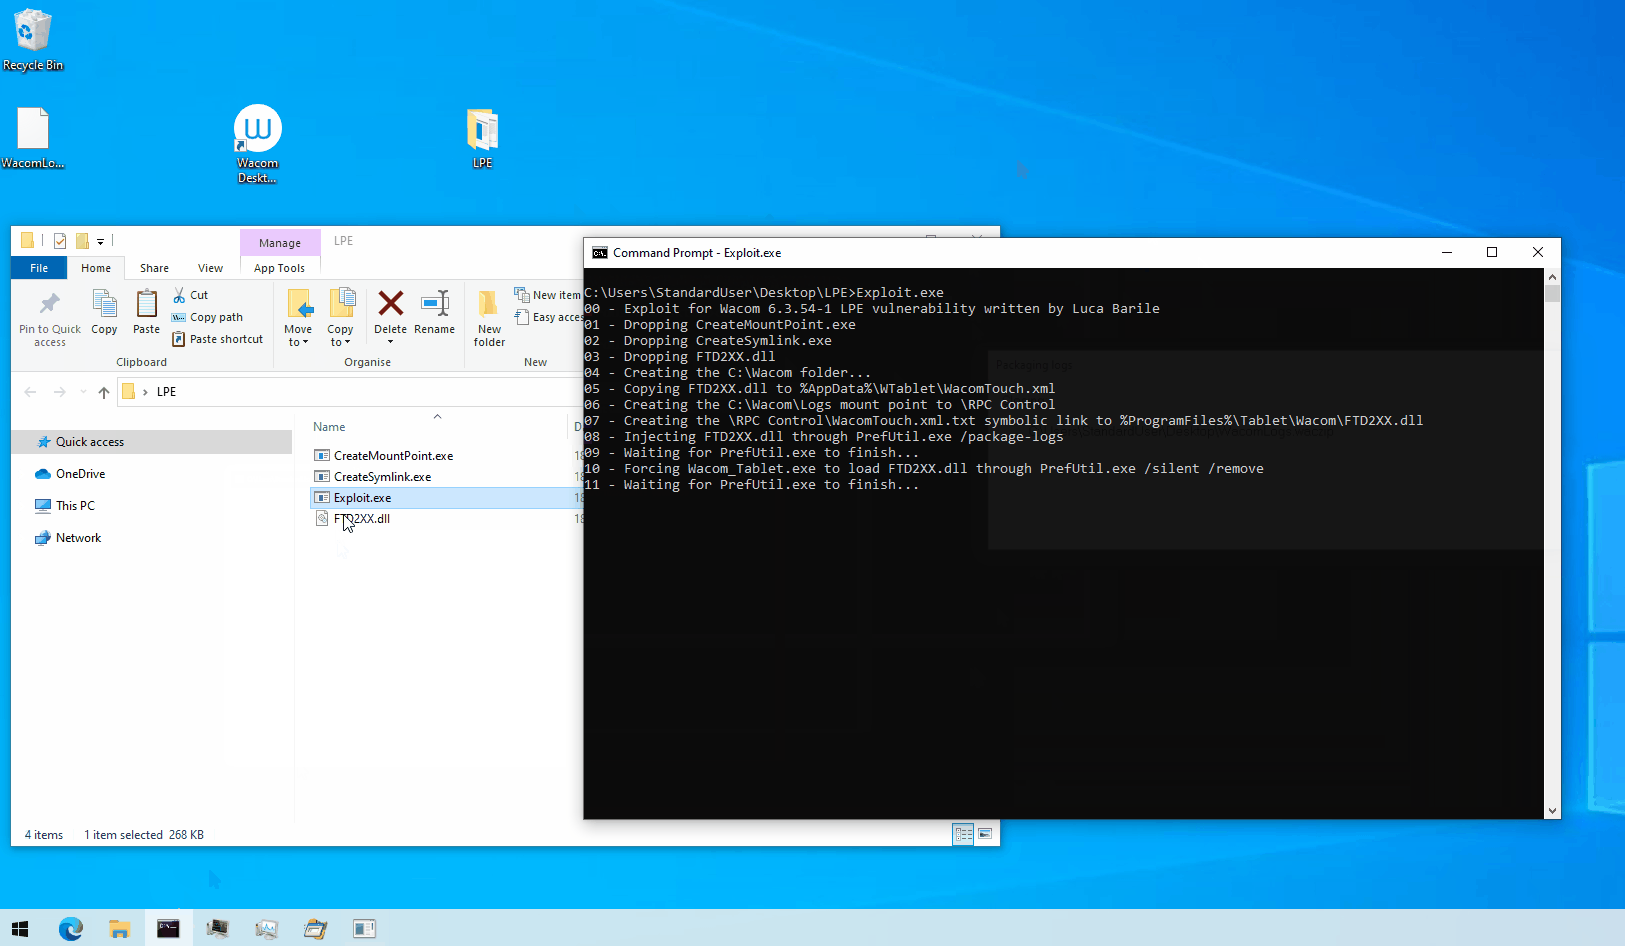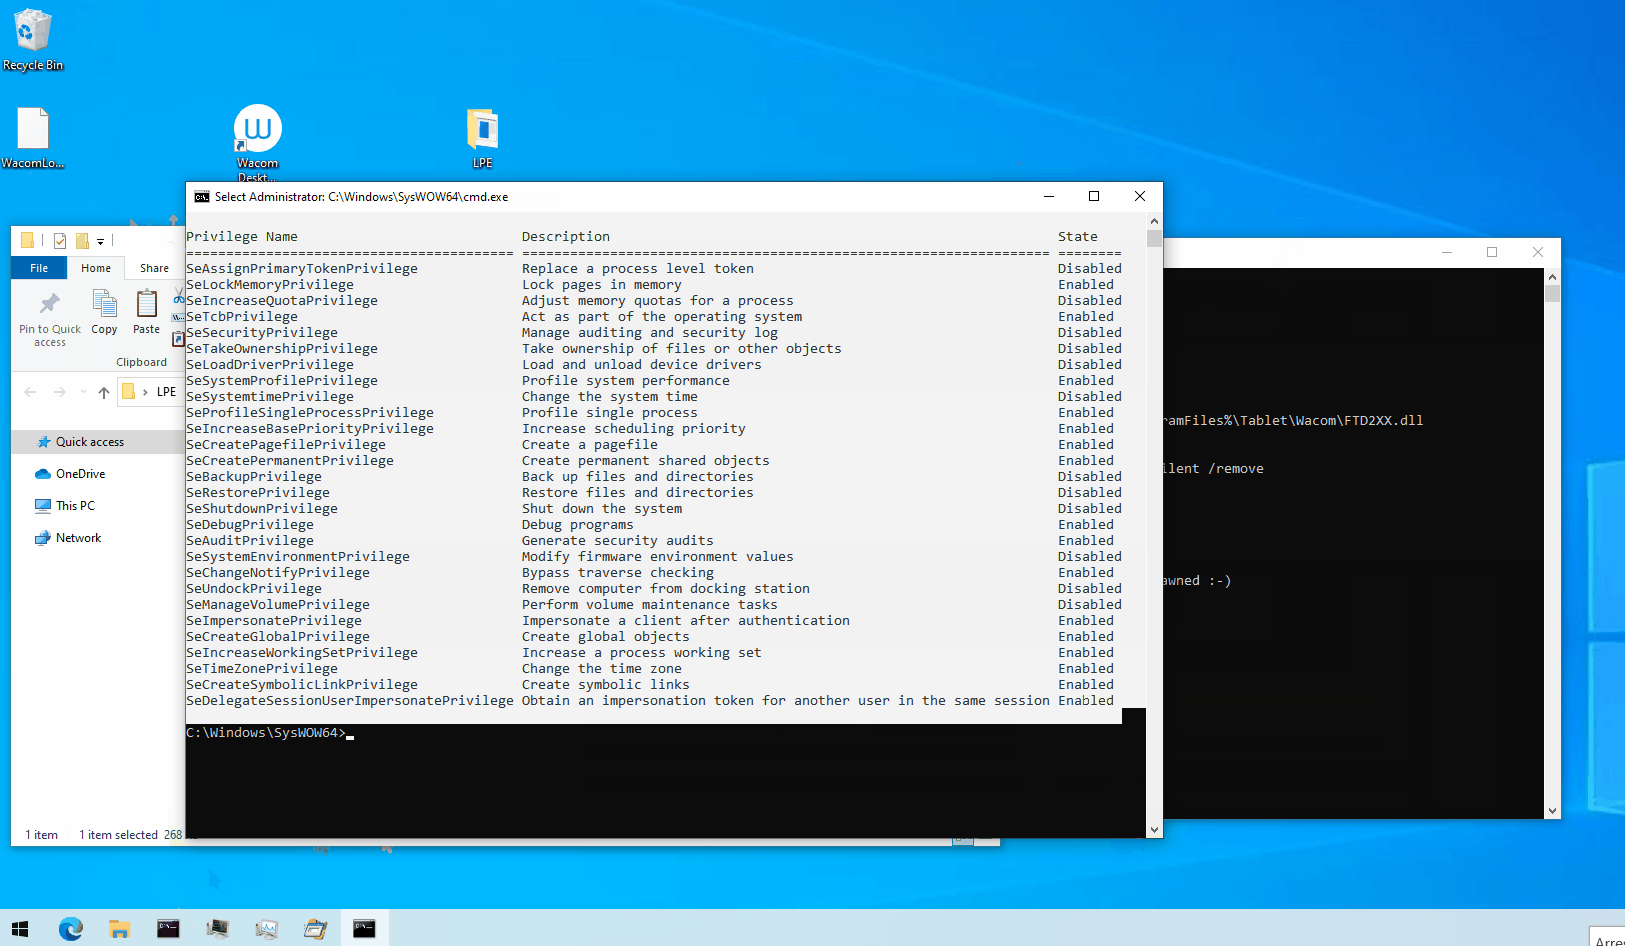
Exploit and report for CVE-2023-32163
 velessecurity/cve-2021-1675-printnightmare-analysis
Technical write-up and analysis of PrintNightmare (CVE-2021-1675 / CVE-2021-34527), covering RCE/LPE exploitation, detection via Windows event logs,…
 itres-labs/cve-2023-3350
Exploit for cryptographic Issue vulnerability on IBERMATICA RPS [CVE-2023-3350]
 l0lsec/cve-2021-3262
CVE-2021-3262 - Blind SQL Injection in the editOEN parameter of TripSpark VEO Transportation / NovusEDU. Unauthenticated, internet-facing. Payloads,…
 skoveit/cve-2026-34200
Proof-of-concept demonstrating unauthenticated cross-origin takeover of Nhost MCP Server, enabling database exfiltration, table drops, and permission…
 k0nnect/cve-2026-21440-writeup-poc
poc and writeup for cve-2026-21440: a critical path traversal vulnerability in @adonisjs/bodyparser allowing arbitrary file writing
 paparojonathan/cve-2026-9335-keras-hdf5-externallink
CVE-2026-9335: KerasFileEditor and load_weights follow h5py ExternalLinks, disclosing arbitrary local HDF5 file contents in keras ≤ 3.14.0. Advisory…
 gabrielftanaka/cve-2026-82221-poc
PoC for Unauthenticated Reflected Cross-Site Scripting (XSS) in RegistrationMagic WordPress Plugin
 oscerd/cve-2026-63039
Proof-of-concept for CVE-2026-63039, demonstrating ORDER BY SQL injection in Apache InLong's AuditAlertRule via orderField/orderType, with a…








