
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
 eynaexp/copy-fail-cve-2026-31431-modernized
Proof-of-concept exploit for CVE-2026-31431, modernized from the original Copy Fail PE exploit. Demonstrates the vulnerability for educational…
 squeeze440/linux-entra-sso-poc
PoC — origin validation error enabling Entra ID PRT SSO cookie exfiltration in linux-entra-sso (GHSA-g9vc-5j77-f2cm, CVE-2026-87005, CVSS 5.3).
 squeeze440/code-graph-rag-poc
PoC — symlink following to arbitrary file read/write outside project root in code-graph-rag (GHSA-85gg-2gfq-q95m, CVE-2026-87008, CVSS 7.1).
 oscerd/cve-2026-63621
Proof-of-concept reproducers for Apache Camel camel-knative structured CloudEvent header injection (CVE-2026-63621), demonstrating header injection…
 vinukalana/dirtypipe-cve-2022-0847
This repository is developed to analysis and understand DirtyPipe exploit CVE-2022-0847
 mrk336/breaking-the-update-chain-inside-cve-2025-59287-and-the-wsus-rce-threat
Technical analysis and proof-of-concept exploit for CVE-2025-59287, a critical RCE in Windows Server Update Services via unsafe deserialization,…
 01luyicheng/cve-2026-99999-exploit
CVE-2026-99999 Working PoC — real VM escape for Linux kernel csum_start bug (CVSS 9.3). Guest-to-Host heap leak. See also: CVE-2026-99999-analysis…
 bombobombone/cve-2026-73312
Proof-of-concept and technical write-up for CVE-2026-73312, an OAuth2 refresh token replay vulnerability in XenForo before 2.3.13. Includes a Python…
 oscerd/cve-2026-71300
Proof-of-concept reproducer for Apache Camel camel-atmosphere-websocket dispatch header injection (CVE-2026-71300), demonstrating how an injected…
 oscerd/cve-2026-46590
Reproducer for CVE-2026-46590: Apache Camel camel-pqc key-lifecycle unsafe deserialization (FileBasedKeyLifecycleManager legacy .key migration via…
 romain-deperne/cve-2026-34975
Proof-of-concept and technical analysis of CRLF email header injection in Plunk's raw MIME construction, demonstrating Bcc injection and other…
 amnsecurity/litellm-command-injection-security-assessment
Professional vulnerability assessment report for LiteLLM command injection risk, including executive summary, technical impact, remediation, and…
 itssixtyn3in/cve-2023-42222
Proof-of-concept exploit for CVE-2023-42222 in WebCatalog, demonstrating arbitrary URL execution via Electron's shell.openExternal to bypass security…
 vudangducminh/cve-2022-0847
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel race condition enabling unprivileged writes to read-only files and privilege…
 squeeze440/terrapod-poc
PoC — missing authorization on the platform-wide GPG trust-anchor store in Terrapod (GHSA-6qrc-597p-mrp9, CVE-2026-87006, CVSS 6.5).
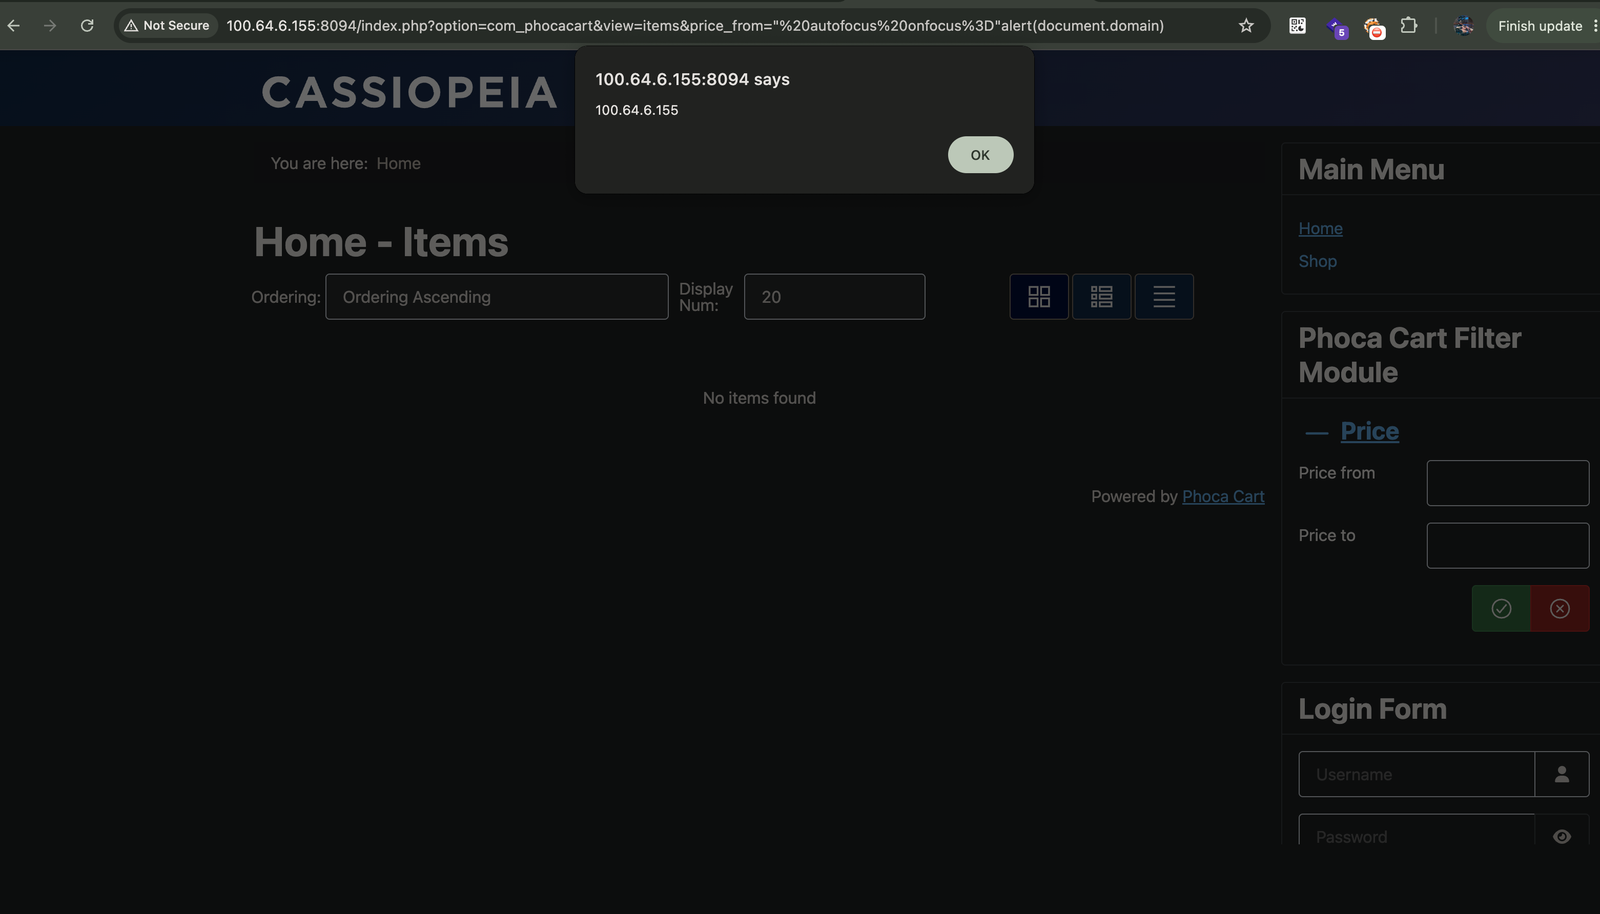 toanln-cov/cve-2026-76565
Reflected XSS via price_from & price_to Filter Parameters in PhocaCart
 oscerd/cve-2026-46584
Reproducer for CVE-2026-46584: Apache Camel camel-mail mail.smtp.* header injection enabling credential theft via on-path SOCKS interception (fixed…
 atsukisato/pgm-attack
Research code for poisoning attacks on the PGM-index, demonstrating how to craft adversarial data to degrade learned index performance.








