
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 rndhouse/vcamper
PoC: identify silent security patches before CVE
 sangsheng2026/honor-90gt-mag-an00-root-research
Android kernel root research toolkit for Honor 90 GT: SELinux device probing, slab spray primitive validation, and AArch64 kernel Image disassembly…
 sanjith1236/cve-2026-8206-kirki-exploit-analysis
Technical reconstruction and proof-of-concept for CVE-2026-8206, an unauthenticated account takeover in the WordPress Kirki plugin, with detection…
 0xblackash/cve-2026-98432
Technical advisory and defensive analysis of CVE-2026-98432, a Linux kernel IPv4 TCP use-after-free, with affected versions, detection commands, and…
 ryh1218/occ
Prohibited Items Segmentation via Occlusion-aware Bilayer Modeling (ICME 2025)
 dmitry-matvienko/malware-analysis-fake-hwmonitor
Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor
 686f6c61/poc-wp-core-cve-2026-93485
Laboratorio pedagógico de CVE-2026-93485 (Comment2Shell): stored XSS no autenticado en WordPress core vía wpautop -> RCE, con demo del root cause…
 uiuc-kang-lab/persistbd
Research code for training adapters that make LLM agent backdoors survive benign fine-tuning, with trigger-rate scoring, SWE-bench evaluation, and…
 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 sbamit/exponentiated-gradient-descent-llm-attack
A novel adversarial attack on LLM based on the Exponentiated Gradient Descent technique.
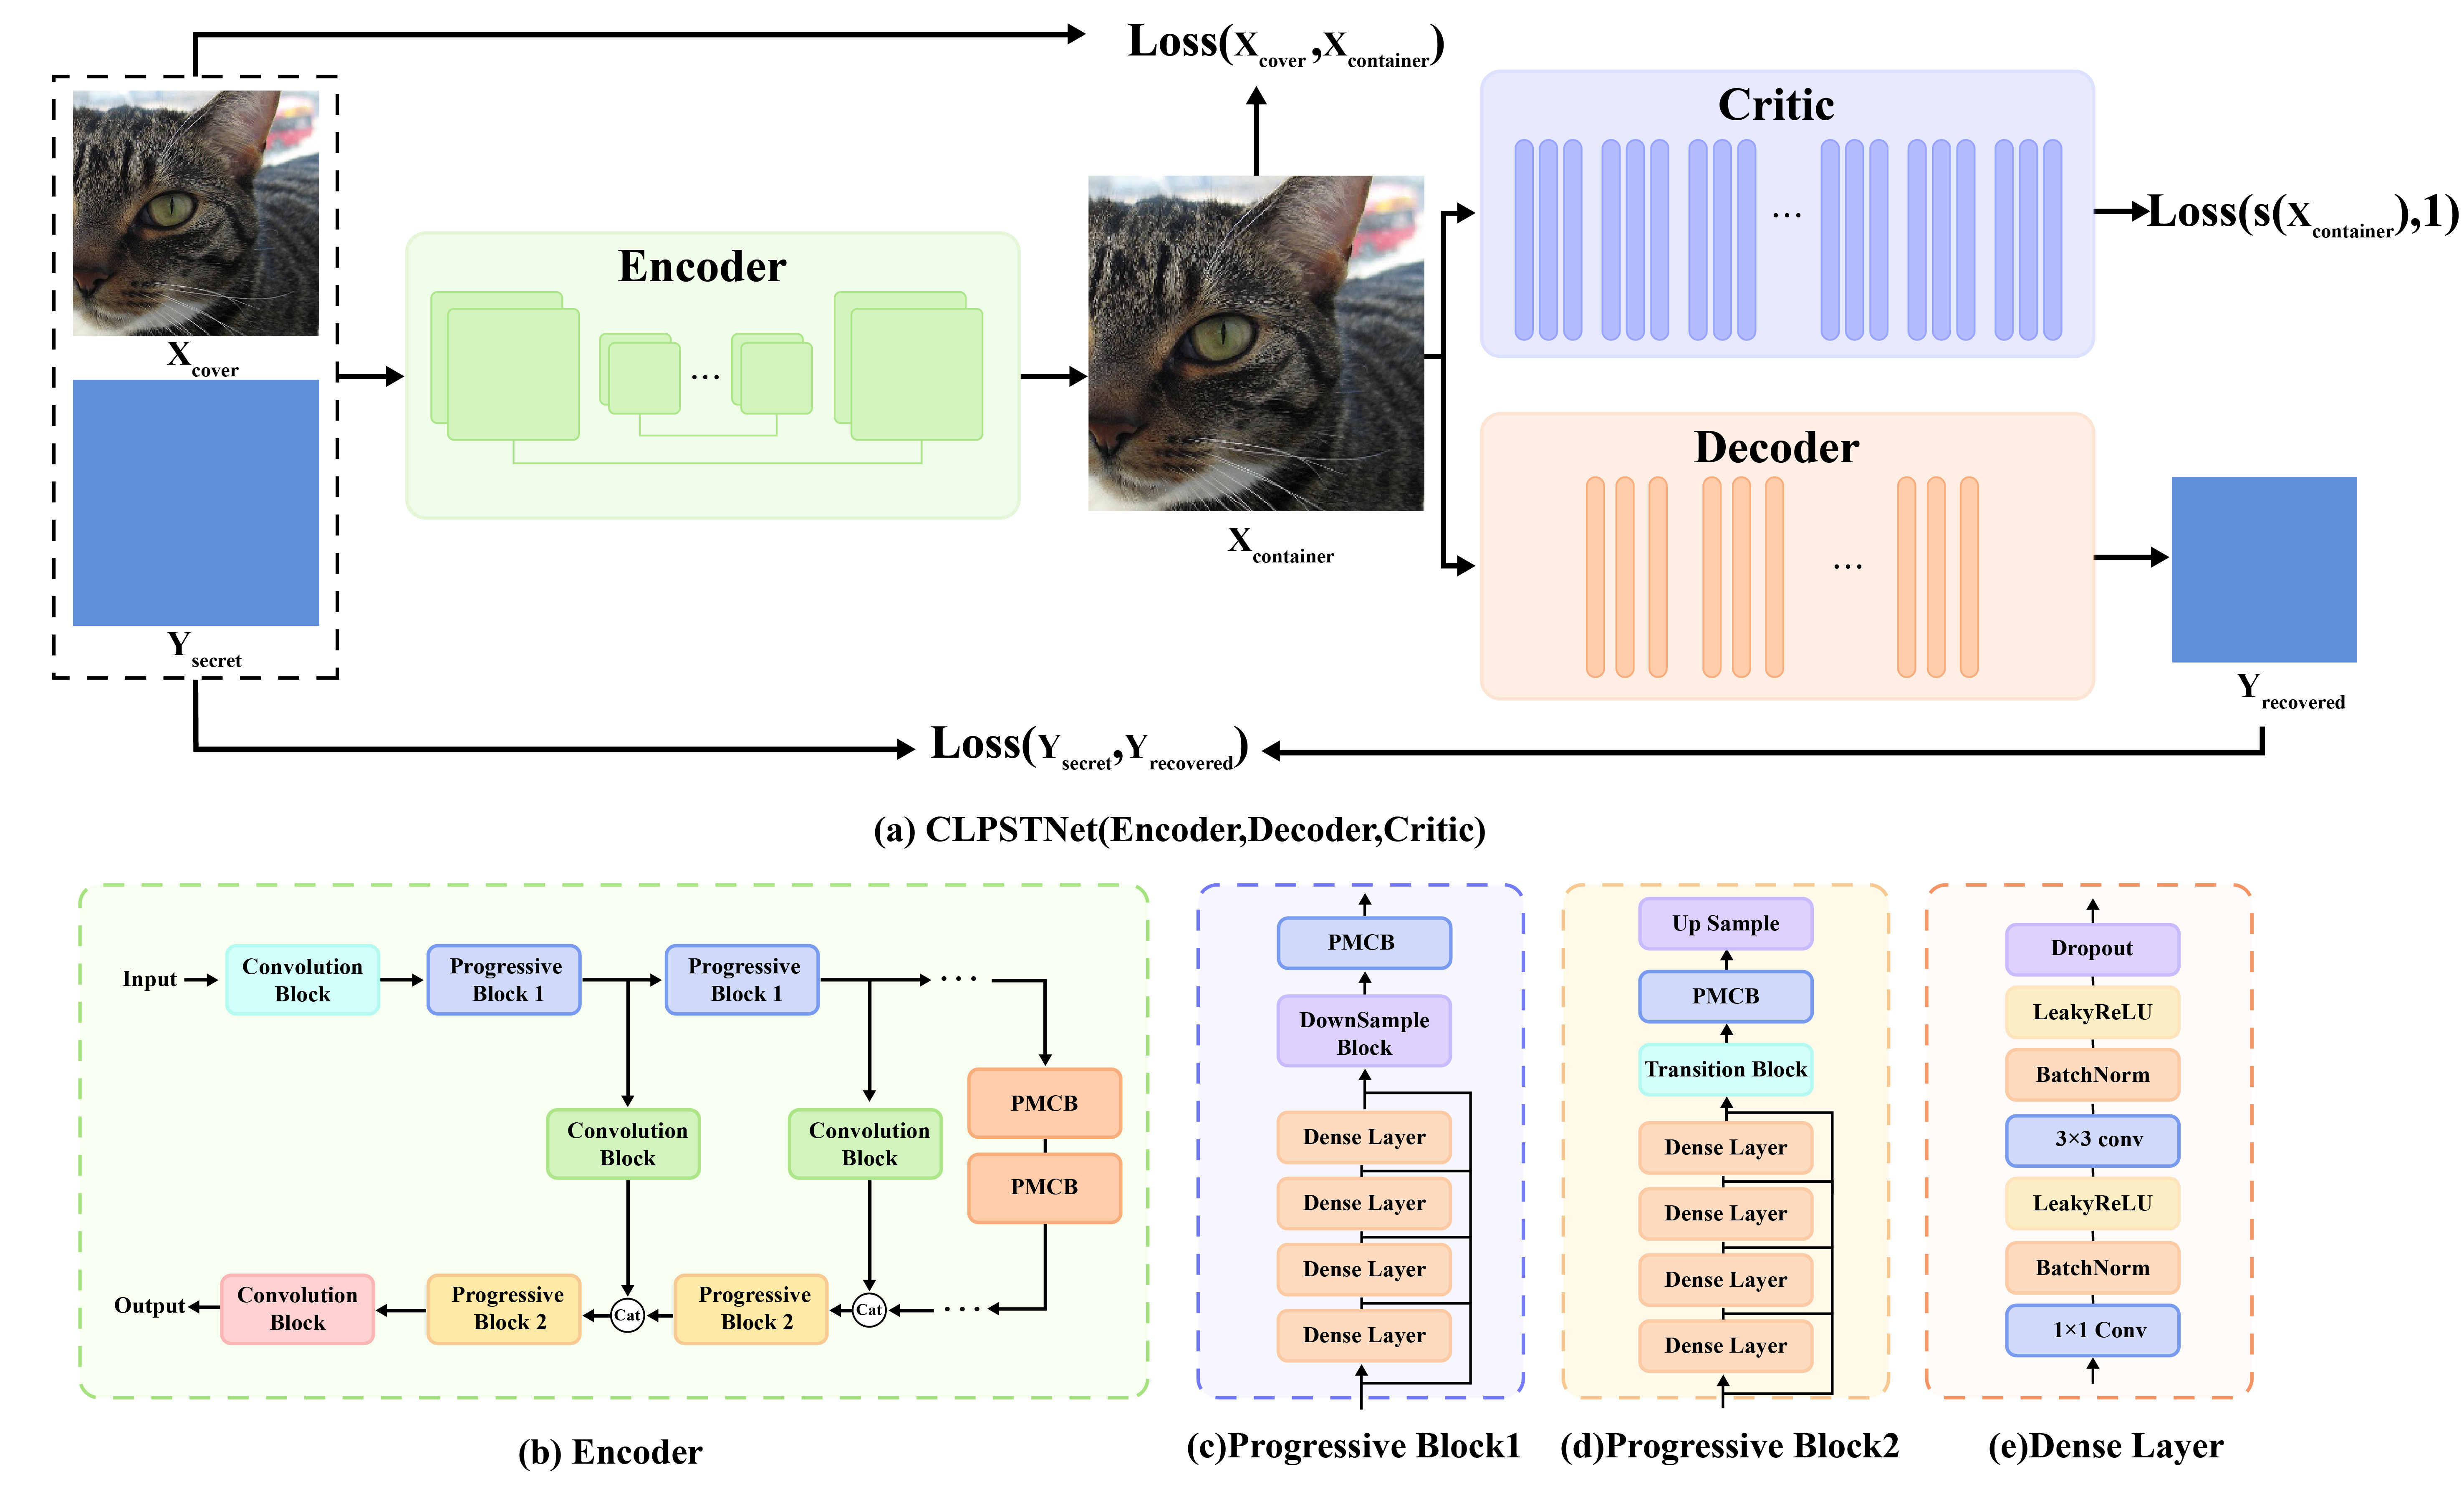 chaos-boops/clpstnet
CLPSTNet: A Progressive Multi-Scale Convolutional Steganography Model Integrating Curriculum Learning
 jawh3/striatum-ctf
Research artifacts for an MCP-based LLM agent that autonomously solves CTF challenges, including ablation data, analysis scripts, and a six-server…
 j-dahl7/mcp-attack-detection-sentinel
Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…
 xh4h/cve-2023-34840
XSS in angular-ui-notification
 ife-ella/cve-vulnerability
Repository referencing CVE-2026-0322; no README, documentation, or code details are available to describe its contents or purpose.
 vettrivel007/cve-disclosures
A repository documenting security vulnerabilities discovered in Free and Open Source Software (FOSS) by VETTRIVEL U
 dinosn/proftpd-cve-2026-42167-analysis
Independent reproduction, code-level root-cause analysis, and realistic-exposure write-up for CVE-2026-42167 (ProFTPD mod_sql is_escaped_text()…
 snailsploit/cve-2026-3288
Walkthrough: ingress-nginx Configuration Injection via rewrite-target Annotation








