
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 dtc7w3pq/visco-attack
Research pipeline implementing a visual-contextual jailbreak against multimodal LLMs: T2I prompt extraction, SD3.5 image rendering, multi-round spoof…
 infostealers-stats/credential-and-breach-monitoring
This repository provides a practical comparison of breach intelligence, dark web monitoring, and identity exposure services, with a focus on factors…
 x-stp/cves-2025-11187_15467_69418
OpenSSL pocs: PKCS#12 stack overflow, CMS IV overflow, OCB infoleak [partial chain]
 ashrafzaryouh/cve-2026-31402
Advisory write-up of CVE-2026-31402, a heap overflow in the Linux kernel NFSv4.0 LOCK replay cache, covering affected component, remote attack…
 0xblackash/cve-2026-31402
CVE-2026-31402
 d3kc4rt1/cve-2025-14893
Authenticated Stored Cross-Site Scripting (XSS) in IndieWeb WordPress Plugin
 d3kc4rt1/cve-2025-15260
Missing Authorization / Broken Access Control in Plugin - MyRewards – Loyalty Points and Rewards for WooCommerce
 vnchk1/sec_review_cve-2024-3094
Security review уязвимости CVE-2024-3094 с открытым исходным кодом
 cydtseng/vulnerability-research
Curated repository of vulnerability research write-ups with assigned CVEs, detailing discovered weaknesses, impact, and remediation across various…
 ashrafzaryouh/cve-2026-2699
Detection scripts, technical analysis, and proof-of-concept for CVE-2026-2699, a critical pre-auth authentication bypass in Progress ShareFile…
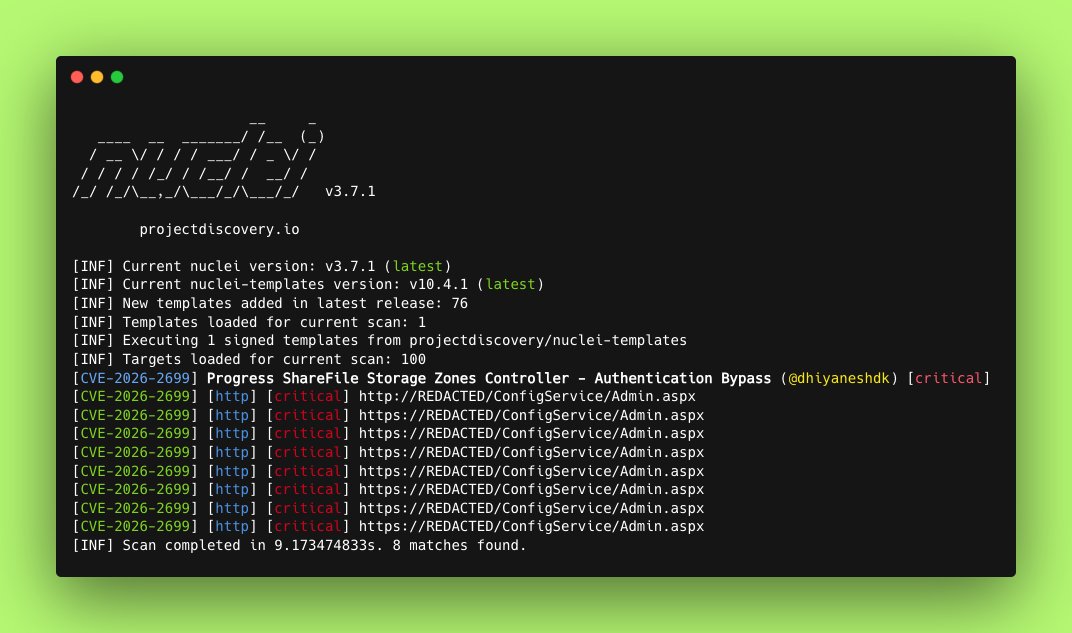 0xblackash/cve-2026-2699
CVE-2026-2699
 unknownhl/deepguard
Code for ACL 2026 (main) paper "DeepGuard: Secure Code Generation via Multi-Layer Semantic Aggregation"
 sangrok-jeon/cve-2020-1938-tomcat-ajp-ghostcat--analysis
CVE-2020-1938-Tomcat-AJP(Ghostcat)-Analysis
 semgrep/cve-2026-22732-demo
Minimal reproduction of CVE-2026-22732 — Spring Security HTTP headers silently dropped
 shaheeryasirofficial/cve-2025-8088
CVE-2025-8088 is a critical path traversal vulnerability in WinRAR 7.12
 tyranid/infosec-presentations
A repository of previous info-sec presentations I've presented.
 open-flaw/cve-2017-11499
Documentation of CVE-2017-11499: a hash flooding remote DoS vulnerability in Node.js caused by constant HashTable seeds, with analysis of the attack…
 darksp33d/hyperhives-macos-infostealer-analysis
Full static analysis of HyperHives macOS Rust infostealer — 571 decrypted config values, C2 infrastructure, DPRK/Contagious Interview attribution,…








