
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 sw0rd1ight/cve-2026-1207
Django 框架在使用 PostGIS 查询地理栅格(raster)数据时,若将未经验证的用户输入直接作为 band index(波段索引)参数,会引发 SQL 注入
 0xblackash/cve-2026-41651
CVE-2026-41651
 sivaadityacoder/cve-2025-68621
Educational PoC and analysis of CVE-2025-68621, a timing attack on Trilium Notes sync login. Demonstrates HMAC hash recovery via network timing…
 quantusync/alaniz-cipher
Encryption from Nonlinear Sheaf Morphisms over Graphs
 johnperifanis/cryptpad-cve-2025-51846-advisory
Sanitized advisory for CVE-2025-51846 affecting CryptPad WebSocket handling.
 devianntsec/cve-2025-55182
Master's thesis research on CVE-2025-55182 (React2Shell). Modular exploitation framework with 6 attack scenarios (RCE, exfiltration, defacement),…
 y3b3l4y3/cve-2025-55182-test
Proof-of-concept demonstrating React2shell vulnerability (CVE-2025-66478) in a Next.js application, providing a base for reproduction and…
 kaleth4/cve-2026-33825
Technical analysis of CVE-2026-33825 (BlueHammer), a local privilege escalation vulnerability in Microsoft Defender, including exploitation flow,…
 john-jung/cve-2026-26903-poc
A PoC for demonstrating CVE-2026-26903
 kaleth4/cve-2026-20180
In-depth technical analysis of Cisco ISE RCE vulnerabilities, including exploitation techniques, evasion methods, and remediation strategies for…
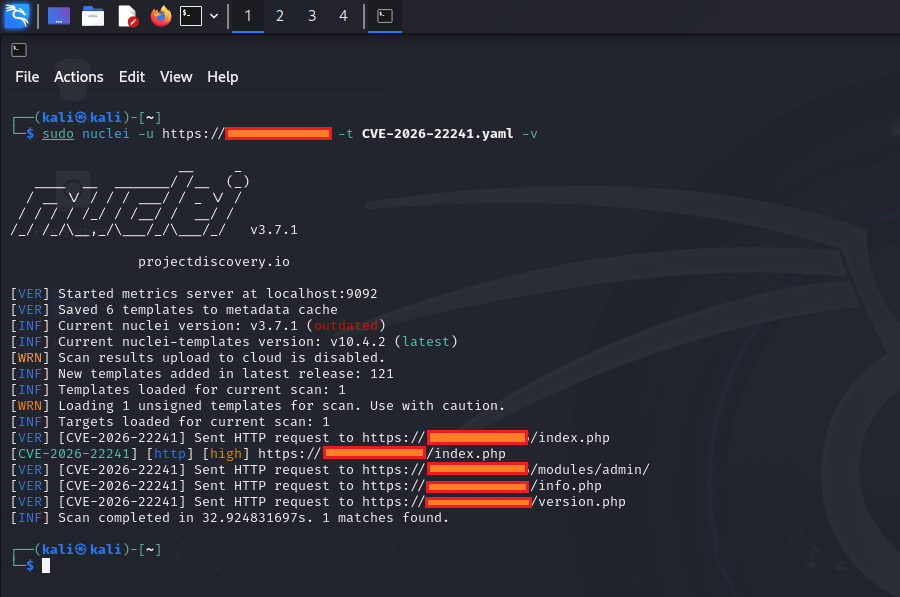 ashrafzaryouh/cve-2026-22241
Advisory and technical analysis of CVE-2026-22241, an unrestricted ZIP upload in Open eClass theme import (pre-4.2) enabling authenticated admin…
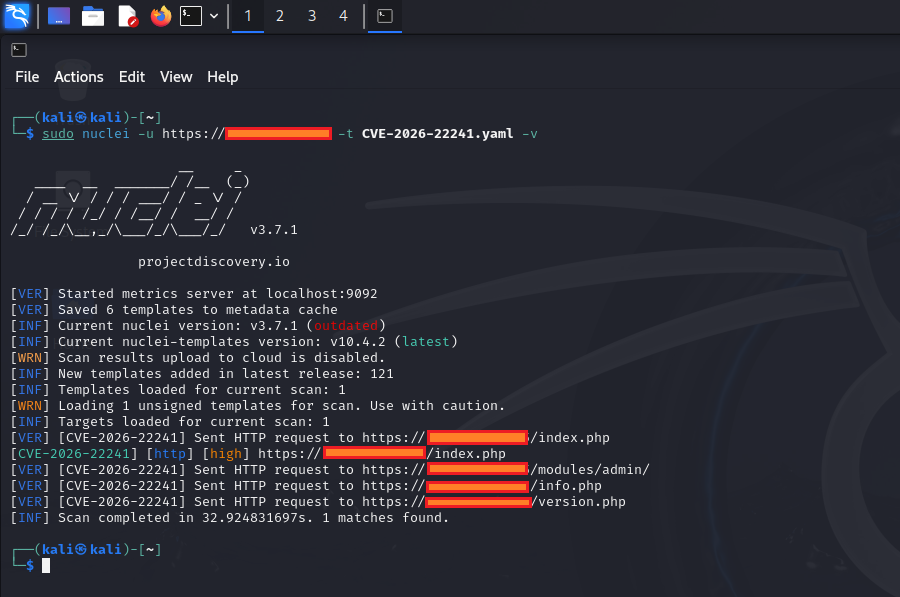 0xblackash/cve-2026-22241
CVE-2026-22241
 pathakabhi24/llm-mcp-security-field-guide
The most comprehensive LLM + MCP security guide i.e. OWASP aligned, real CVEs, actionable checklists
 manjustice/datadome-vm-internals
Analysis of DataDome's custom obfuscated VM and bytecode format, revealing string encryption, S-box ciphers, and browser fingerprinting signals for…
 husnainfareed/awesome-ethical-hacking-resources
😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.
 rat5ak/cve-2026-31413-bpf-container-escape
CVE-2026-31413: BPF verifier soundness bug - container escape
 d4rkks/cve-2025-7771-vulnerability-exploration
Escalating privilege in the system from unsigned driver using throttlestop vulnerability
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.








