
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 the-knell/not-the-key
Demonstrates that Home Assistant password changes do not revoke refresh or long-lived bearer tokens, with live proof on core 2026.11.0.
 securagenai/signed-but-steerable
Measuring and closing the text–vector integrity gap in offline RAG: margin law, vector-database audits and code-level verification.
 khenryaegis/vulnbot
LLM-driven multi-agent framework that autonomously replicates human penetration testing workflows, orchestrating Kali Linux tooling and RAG knowledge…
 reddelexc/hackerone-reports
Curated collection of top HackerOne bug bounty reports organized by vulnerability type and program, with scripts to fetch, deduplicate, and rank…
 uofw/uofw
The unofficial Official FirmWare, a complete latest PSP firmware reverse engineering project
 newbe3e/pwn2own-automotive-2026-alpine-ilx-f511-0-click-rce-exploit-writeup
Writeup of a 0-click remote code execution exploit chain developed for the Alpine iLX-F511 automotive head unit at Pwn2Own Automotive 2026.
 multimodal-ai-lab/tobac
Token by Token, Compromised: Backdoor Vulnerabilities in Unified Autoregressive Models (NeurIPS'26)
 hackpatato/poc-and-yara-rules-of-cve-2025-59528-flowise-has-remote-code-execution-vulnerability
Proof-of-concept exploit and YARA detection rules for CVE-2025-59528, a remote code execution vulnerability in Flowise, intended for authorized…

 aa22396584/ghostmap-research
Independent Android 15-17 reproduction of the GhostMap ZIP-metadata parser crash, with native crash analysis, redacted evidence, and offline APK…
 nanoturtle1145/cve-2026-98260-uaf
CVE-2026-98260 (posix-cpu-timers exec UAF) exploit research: S9280 Android 14 GKI 6.1 — UAF trigger + zero-write primitive + SELinux Permissive.…
 blkph0x/cve-2026-109619-zendpipelinelab
PHP CVE-2026-109619 stale session state: calibrated mod_php lab reproduction, evidence, and solver
 01luyicheng/cve-2026-99999-exploit
CVE-2026-99999 Working PoC — real VM escape for Linux kernel csum_start bug (CVSS 9.3). Guest-to-Host heap leak. See also: CVE-2026-99999-analysis…
 01luyicheng/cve-2026-99999-analysis
CVE-2026-99999 Educational Analysis — attack chain simulation of Linux kernel csum_start bug (CVSS 9.3). See also: CVE-2026-99999-exploit (Working…
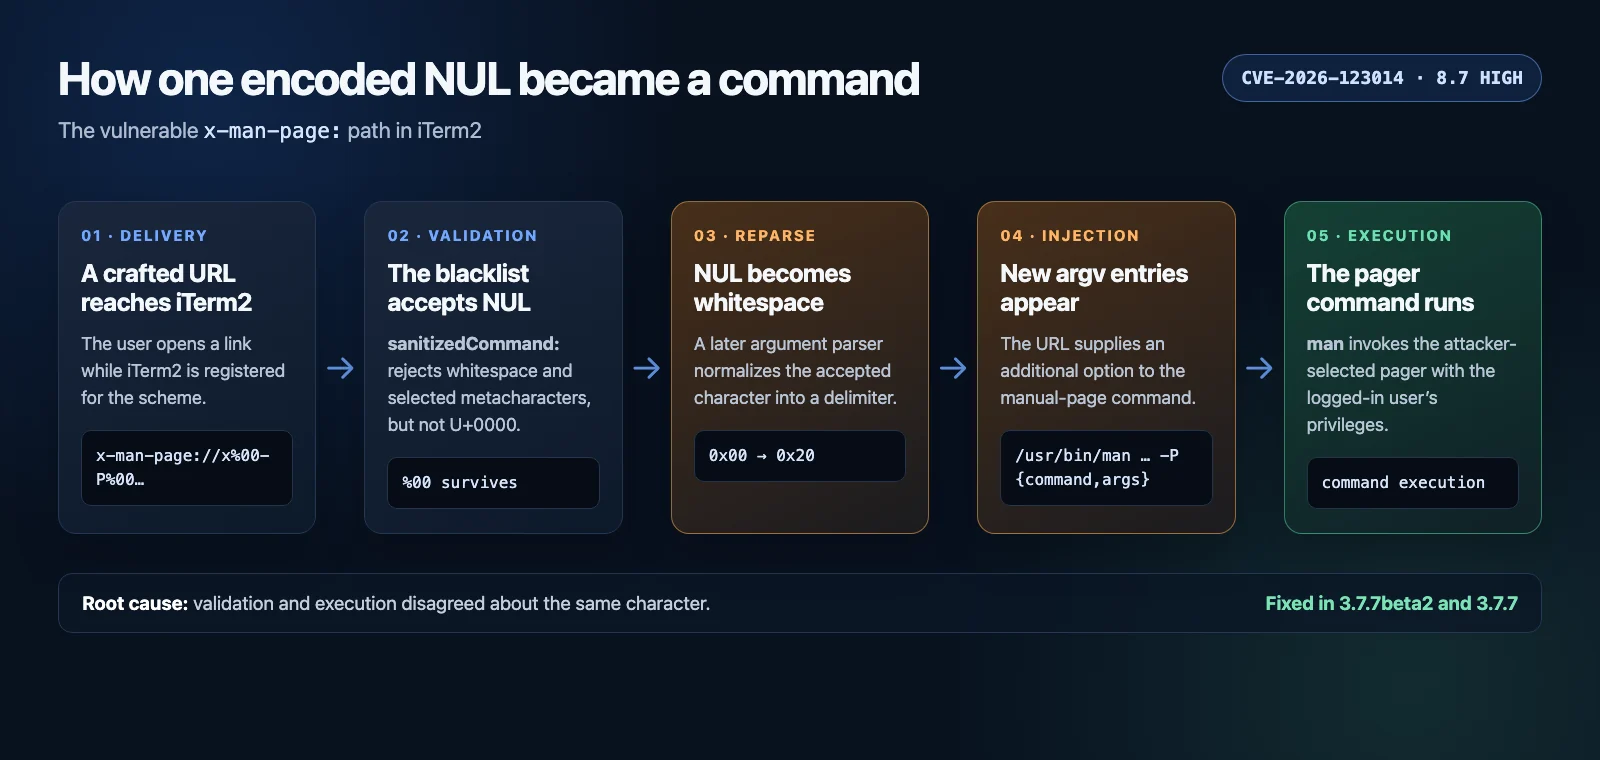 giki-shergill/cve-2026-123014---iterm2-terminal
PoC and research for CVE-2026-123014: iTerm2 x-man-page NUL-byte argument injection.
 ghost-bx1/authenticatorflaw-cve-2026-80097
CVE-2026-80097 - Microsoft Authenticator Android Token Theft PoC & Exploit
 the-knell/thirty-one-bits
Signed research paper and live key-recovery demonstration against InfiniteWP Client's NOSSL branch, which derives its signing key from 31 bits of…
 cyllex-framework/cyllex-argus
Local AI-assisted threat intelligence pipeline that ingests web, RSS and document sources, extracts quote-verified claims, and maps adversary…
 tianlansedexiaoniu/cve-2026-19971_guest
LB-LINK WR1210M (CVE-2026-19971) 未授权配置泄露漏洞与访客网络扩展攻击链分析








