
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended

 off-by-1-labs/flawed
Fix-Like Artifacts With Embedded Defects
 michalbednarski/resourcepoison
Writeup and exploit for CVE-2025-22441: Privilege escalation from installed app to SystemUI process on Android due to pass of untrusted…
 danielbohannon/revoke-obfuscation
PowerShell Obfuscation Detection Framework
 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 aenlr/strutt-cve-2014-0114
Technical analysis and proof-of-concept for Apache Struts 1 class parameter manipulation (CVE-2014-0114), demonstrating remote code execution on…
 uiuc-kang-lab/persistbd
Research code for training adapters that make LLM agent backdoors survive benign fine-tuning, with trigger-rate scoring, SWE-bench evaluation, and…
 selectstar-ai/finred-paper
finance domain specific red-teaming benchmark evaluation rubric
 0xcyberstan/cve-2026-59346-poc
PoC for CVE-2026-59346 - 32-bit integer overflow in VMware's VMXNET3 TSO segmentation path, guest-to-host crash.
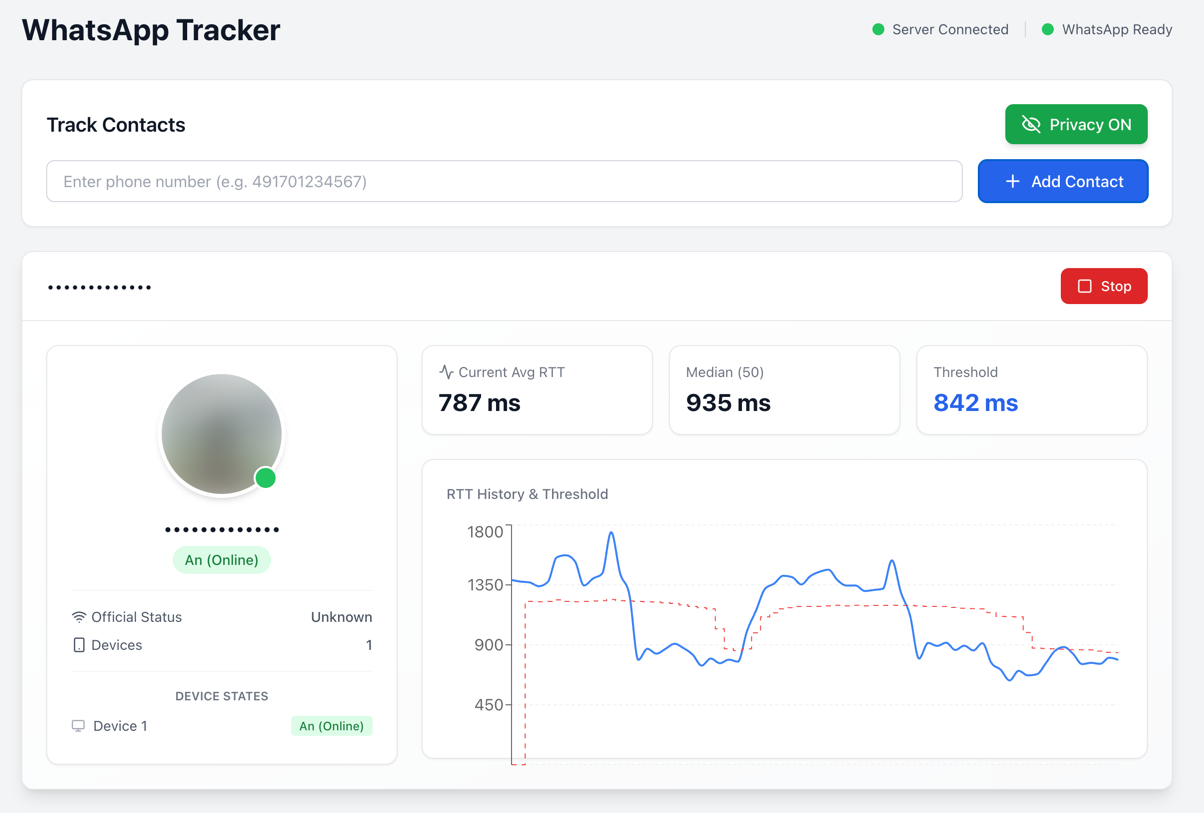 gommzystudio/device-activity-tracker
A phone number can reveal whether a device is active, in standby or offline (and more). This PoC demonstrates how delivery receipts + RTT timing leak…
 rub-nds/johnny-you-are-fired
Artifacts for the USENIX publication.
 themehackers/cve-2025-54100
CVE-2025-54100 (CVSS 7.8 High) is a command injection vulnerability in the Invoke-WebRequest cmdlet of Windows PowerShell 5.1. It arises from…
 thehackersbrain/certificate-of-compromise
SoK/Whitepaper on Offensive Operations against Active Directory Certificate Service
 theopaid/cve-2026-66752-http-request-smuggling-via-unparsed-transfer-encoding-values-tiny_http-
Security Advisory: HTTP Request Smuggling via Unparsed Transfer-Encoding Values (tiny_http)
 k9-modz/cve-2023-38873-g1
Proof-of-concept demonstrating a Clickjacking vulnerability on the G1 website, with a malicious iframe overlay and social engineering popup for…
 yxf203/defense-as-skill
Runtime guard skill that detects and blocks malicious skill-induced attacks in skill-augmented agents, with an MCTS loop that evolves the guard…
 zdcslab/rubrics-as-an-attack-surface
Research code for Rubric-Induced Preference Drift (RIPD): evolutionary rubric search, benchmark-preserving selection, and DPO policy misalignment…
 artur9010/amazon-mustang-hack
Kernel exploit research achieving temporary root on Amazon Fire 7 (Fire OS 7.3.3.1) via the Mali kbase JIT use-after-free CVE-2022-38181, with a…
 s-index/cve-2021-43811
awslabs/sockeye Code injection via unsafe YAML loading CVE-2021-43811








