
 #1
Tools for analyzing network traffic and communication logs to investigate security incidents.
Kitploit recommended
 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
 leonward/openfpc
OpenFPC, Open Source Full Packet Capture
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
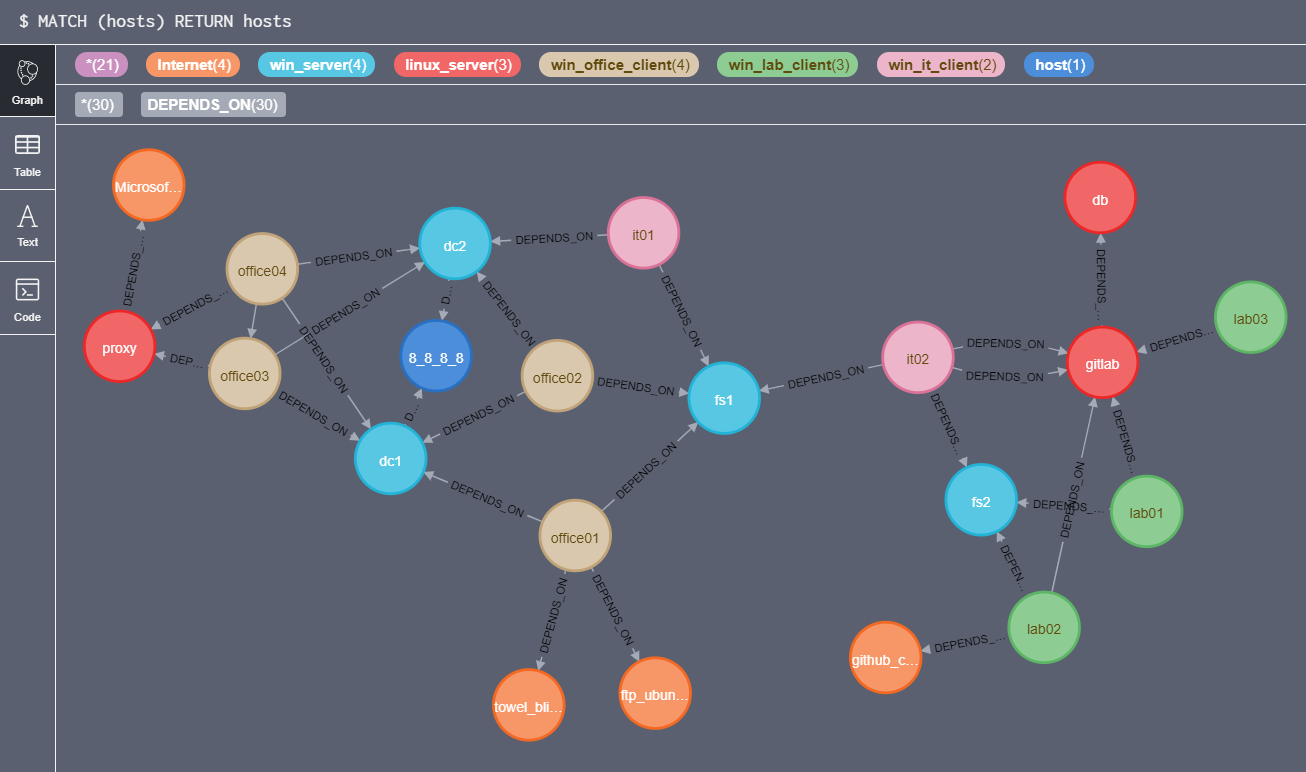 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
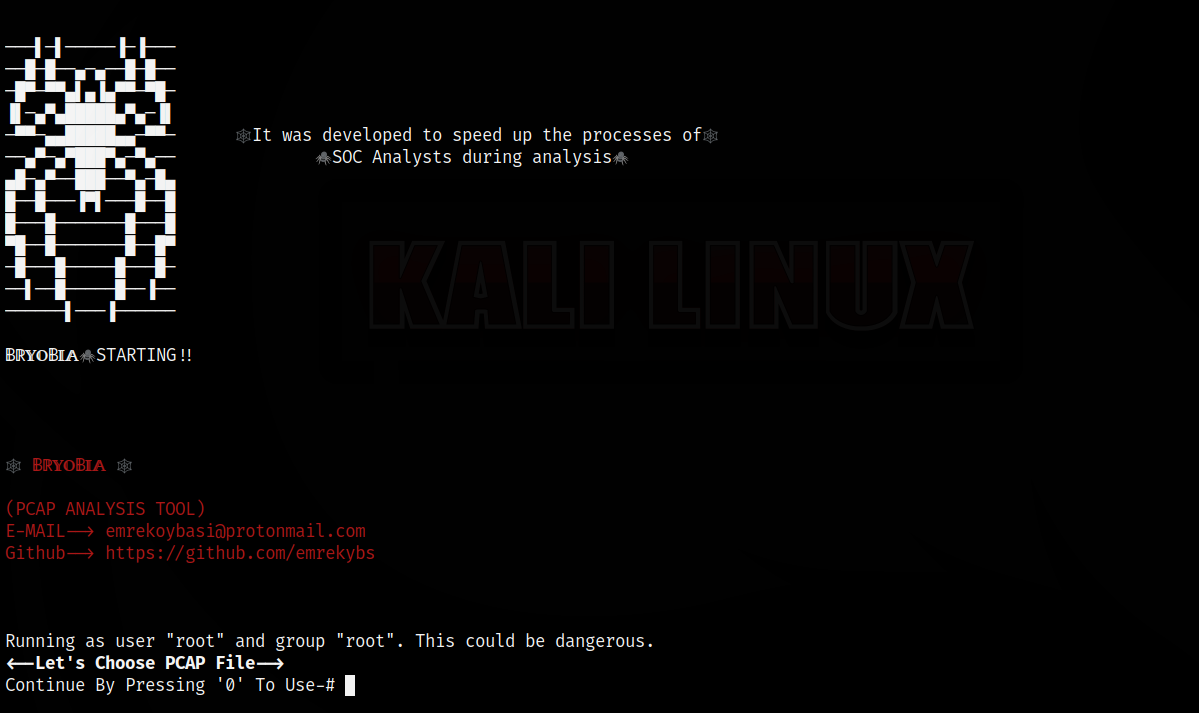 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
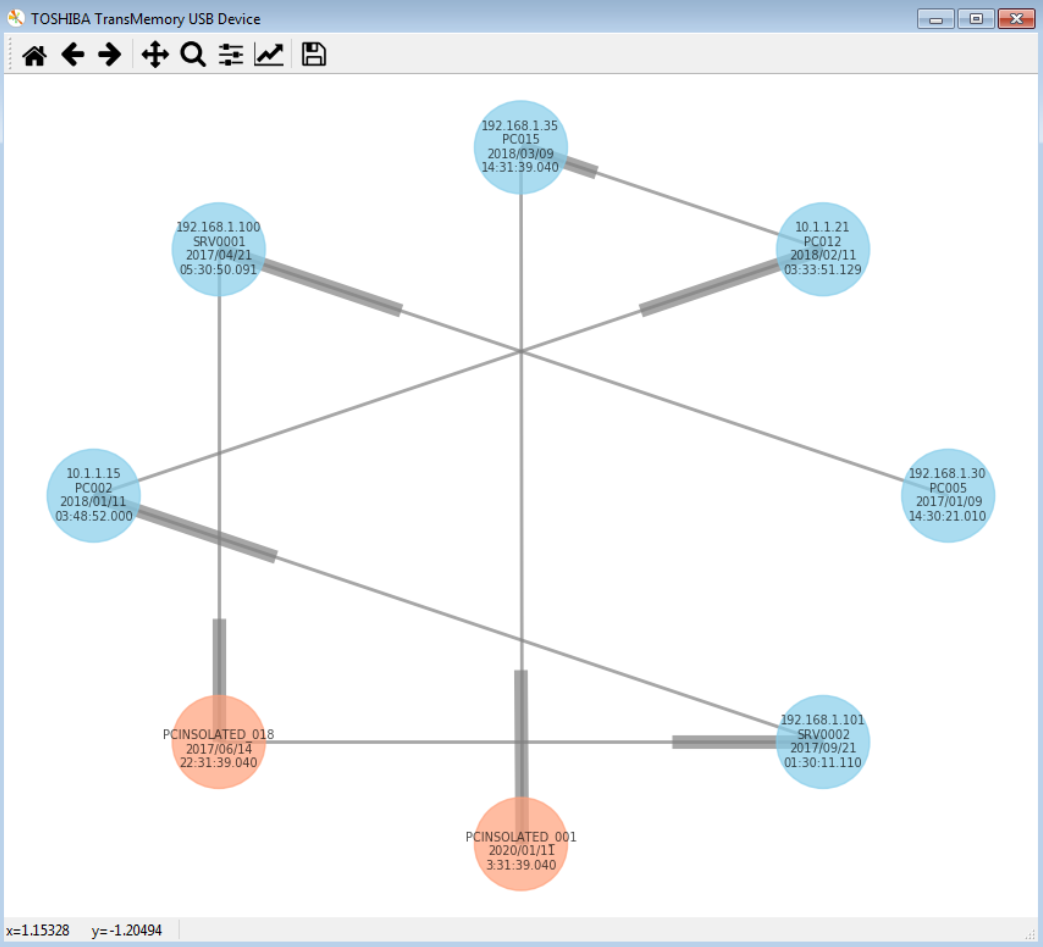 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
 kcreyts/plugxdecoder
Decodes PlugX traffic and encrypted/compressed artifacts
 kdbugk/game-of-kingshot-re
Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…
 kybr-git/dc30-badge-challenge-writeup
Writeup for the DEF CON 30 badge challenge
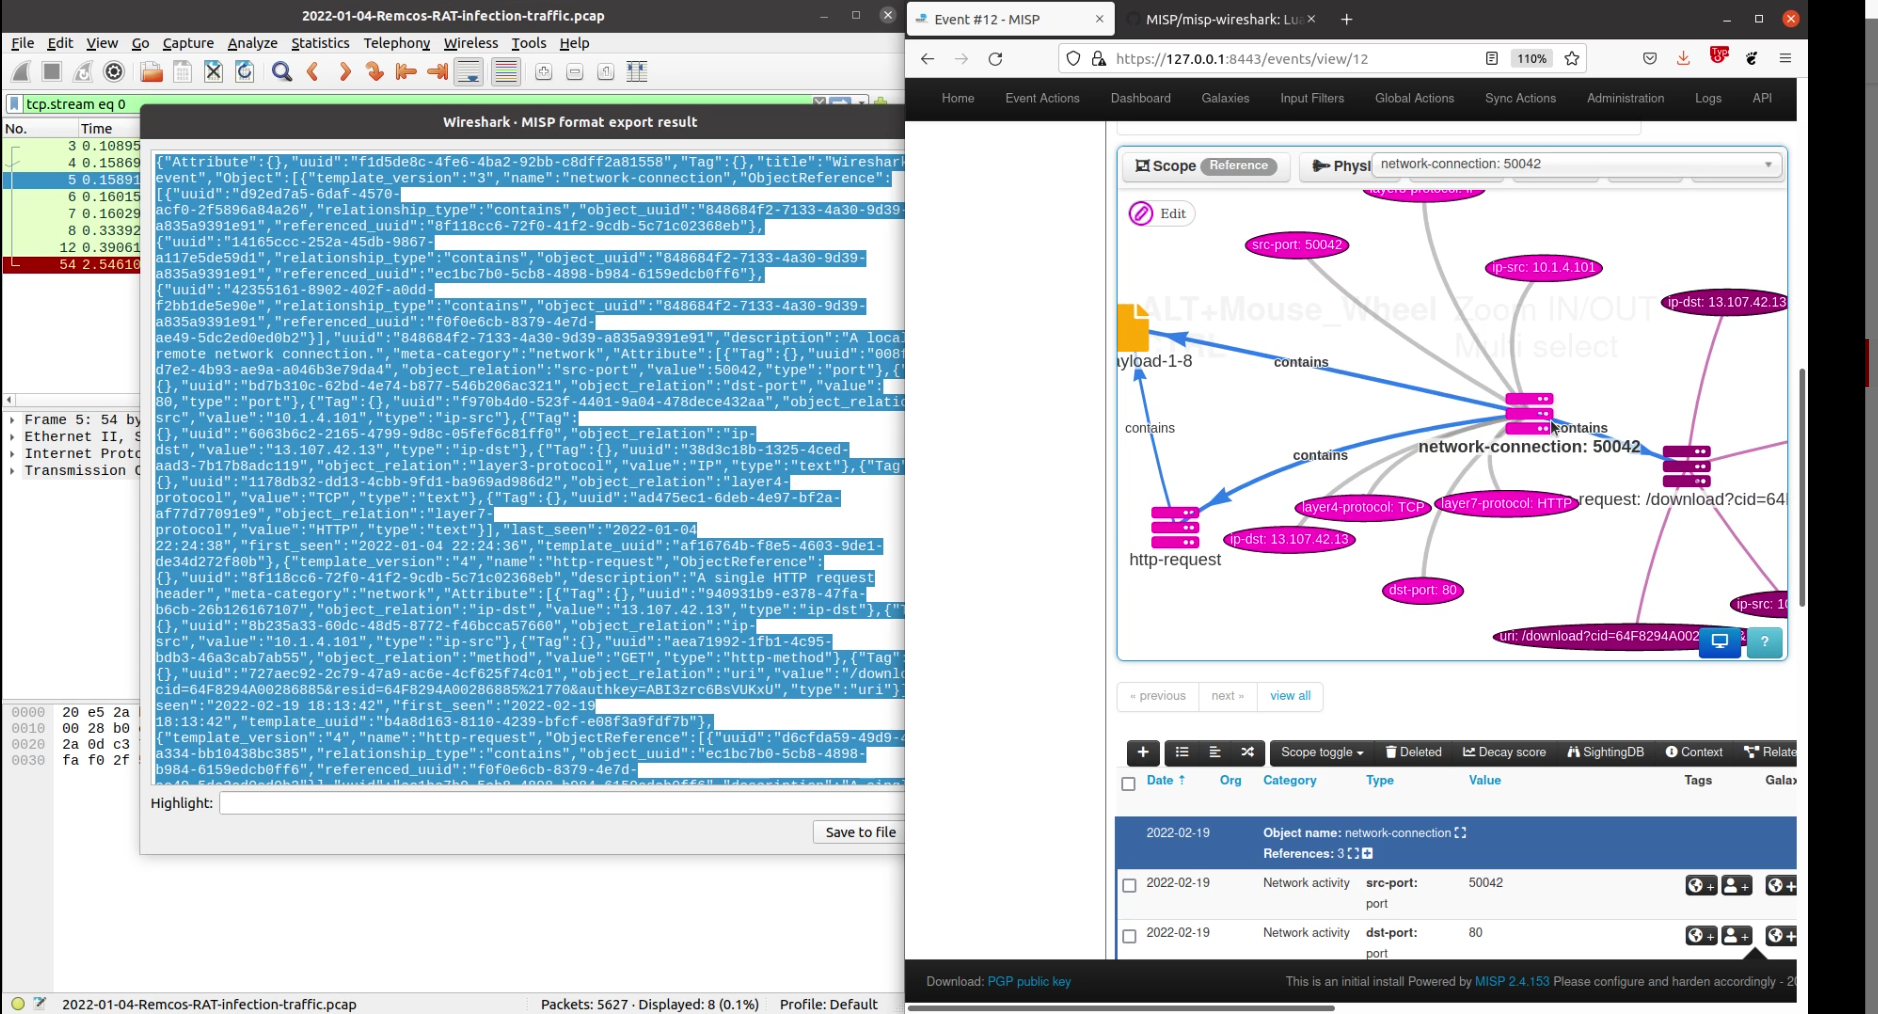 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
 corelight/zeek-community-id
Zeek support for Community ID flow hashing.
 appliedsec/forensicscanner
Forensic Scanner
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
 naacbin/covenantdecryptor
Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…








