

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Categories

Network Forensics

Tools for analyzing network traffic and communication logs to investigate security incidents.

Kitploit recommended

Top tools

10 selected
wireshark preview#1

wireshark

GitHubwireshark/wireshark
9.9k1 day ago
zeek preview#2

zeek

GitHubzeek/zeek
7.8k4 days ago
arkime preview#3

arkime

GitHubarkime/arkime
7.4k1 day ago
Malcolm preview#4

Malcolm

GitHubcisagov/malcolm
2.5k1 month ago
suricata preview#5

suricata

GitHuboisf/suricata
6.5k6 days ago
ntopng preview#7

ntopng

GitHubntop/ntopng
8.1k6h 51m ago
scapy preview#8

scapy

GitHubsecdev/scapy
12.5k2 days ago
etl2pcapng preview#10

etl2pcapng

GitHubmicrosoft/etl2pcapng
7351 year ago
netsniff-ng preview#11

netsniff-ng

GitHubnetsniff-ng/netsniff-ng
1.4k1 year ago
gopacket preview#13

gopacket

GitHubgoogle/gopacket
6.8k1 year ago
NewestRelevanceMost popularRecently updated
140 results
ACF preview

ACF

GitHubcyberhatcoil/acf

Android Connections Forensics

osintnetwork-forensicsmobile-forensics+2
3310 years ago
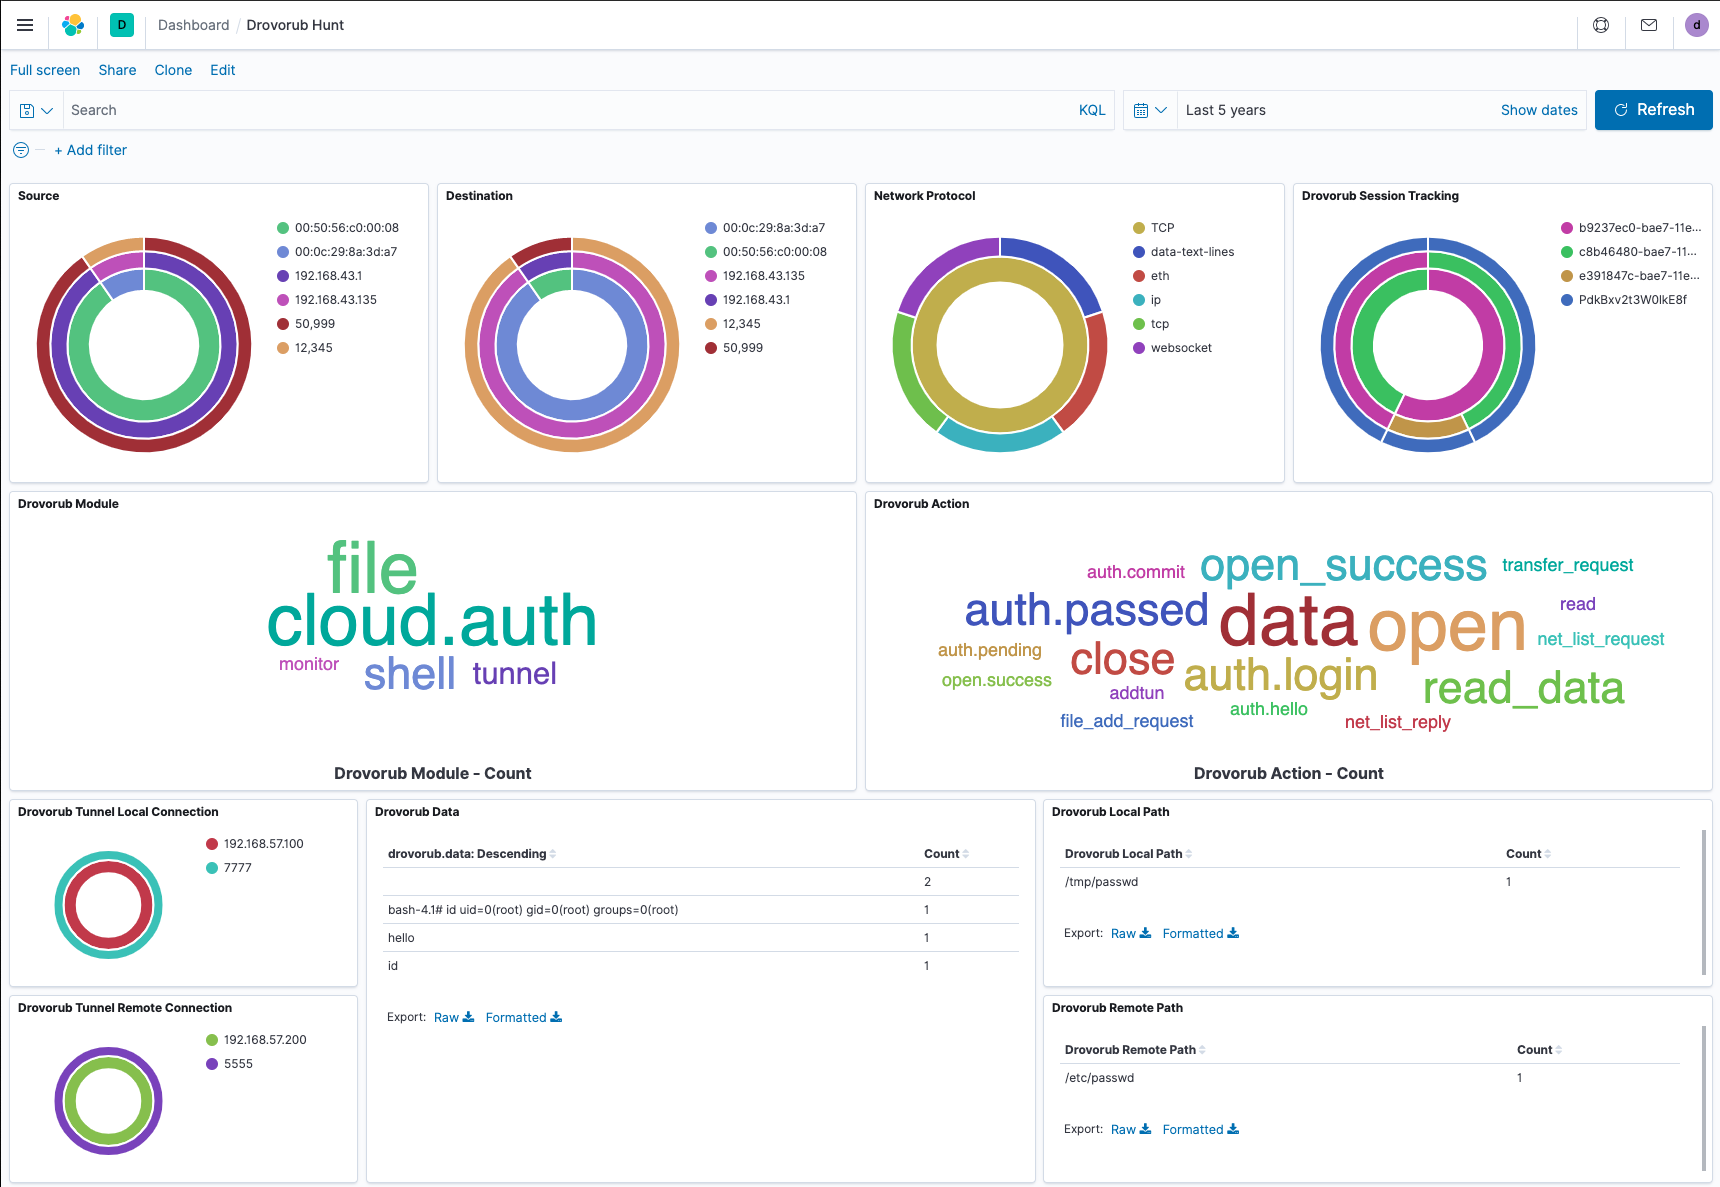
drovorub-hunt preview

drovorub-hunt

GitHubinsane-forensics/drovorub-hunt

A tool to assist with network-based hunting for GRU's Drovorub malware c2

threat-feeds-aggregatorsnetwork-forensicsmalware-analysis+3
256 years ago
Android-Projector-C2-Malware preview

Android-Projector-C2-Malware

GitHubkavan00/android-projector-c2-malware

Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
android-securityembedded-systems-securityioc-management+9
185 months ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
disk-forensicsosintdynamic-analysis-sandboxing+7
232 months ago
BlueFish preview

BlueFish

GitHubemrekybs/bluefish

Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
packet-sniffing-analysisnetwork-forensicsforensics+2
196 months ago
ndff preview

ndff

GitHubknqyf263/ndff

A flow-based network monitor with Deep Packet Inspection
packet-sniffing-analysisnetwork-forensicsnetwork-security+2
299 years ago
loki-parse preview

loki-parse

GitHubr3mrum/loki-parse

A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…

ioc-managementpacket-sniffing-analysisnetwork-forensics+5
139 years ago
pcapan preview

pcapan

GitHubsynacktiv/pcapan

A pcap capture analysis helper

packet-sniffing-analysisreconnaissancenetwork-forensics+3
253 years ago
Mortimer preview

Mortimer

GitHubnccgroup/mortimer

A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.

ioc-managementosintnetwork-forensics+3
1211 years ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

ioc-managementmemory-forensicsnetwork-forensics+7
121 month ago
zeek-spicy-ipsec preview

zeek-spicy-ipsec

GitHubcorelight/zeek-spicy-ipsec

A Zeek IPSec protocol analyzer based on Spicy.
packet-sniffing-analysisnetwork-forensicsnetwork-security+1
81 year ago
zeek-spicy-wireguard preview

zeek-spicy-wireguard

GitHubcorelight/zeek-spicy-wireguard

A Zeek Wireguard protocol analyzer based on Spicy.
packet-sniffing-analysisnetwork-forensicsnetwork-security
77 months ago
zeek-quic preview

zeek-quic

GitHubcorelight/zeek-quic

Bro analyzer that detects Google's QUIC protocol

packet-sniffing-analysisnetwork-forensicsnetwork-security+2
115 years ago
zeek-spicy-ospf preview

zeek-spicy-ospf

GitHubcorelight/zeek-spicy-ospf

A Zeek OSPF packet analyzer based on Spicy.
packet-sniffing-analysisnetwork-mappingnetwork-forensics+2
81 year ago
Sandb0x-Xtract0r preview

Sandb0x-Xtract0r

GitHubdarnellwashingtonjr94-art/sandb0x-xtract0r

Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…

dynamic-analysis-sandboxingmemory-forensicsnetwork-forensics+3
39 days ago
zeek-spicy-stun preview

zeek-spicy-stun

GitHubcorelight/zeek-spicy-stun

A Zeek STUN protocol analyzer based on Spicy.

packet-sniffing-analysisnetwork-forensicsforensics+2
51 year ago
linux-root-kit preview

linux-root-kit

GitHubic3-512/linux-root-kit

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…

privilege-escalationexploit-frameworksmemory-forensics+8
101 year ago
An-Integrated-Wireless-Network-Forensic-Analysis-Framework preview

An-Integrated-Wireless-Network-Forensic-Analysis-Framework

GitHubbenadia/an-integrated-wireless-network-forensic-analysis-framework

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…


packet-sniffing-analysisnetwork-forensicsforensics+2
68 years ago
Previous1…5678Next



