
 #1
Tools for analyzing RAM dumps to find running processes, network connections, and hidden malware.
Kitploit recommended

 rin449/bhpai
Multi-format malware analysis platform combining a stealth Ring-3 Windows sandbox, static PE/PDF analyzers, ransomware key recovery, and an AI…
 mein-0/gvcidrv64
Proof-of-concept exploit for Gigabyte's GVCIDrv64.sys kernel driver, achieving local privilege escalation via arbitrary physical memory and I/O port…
 withsecurelabs/volatility-plugins
Volatility plugins for memory forensics, including detection of Gargoyle memory scanning evasion techniques.
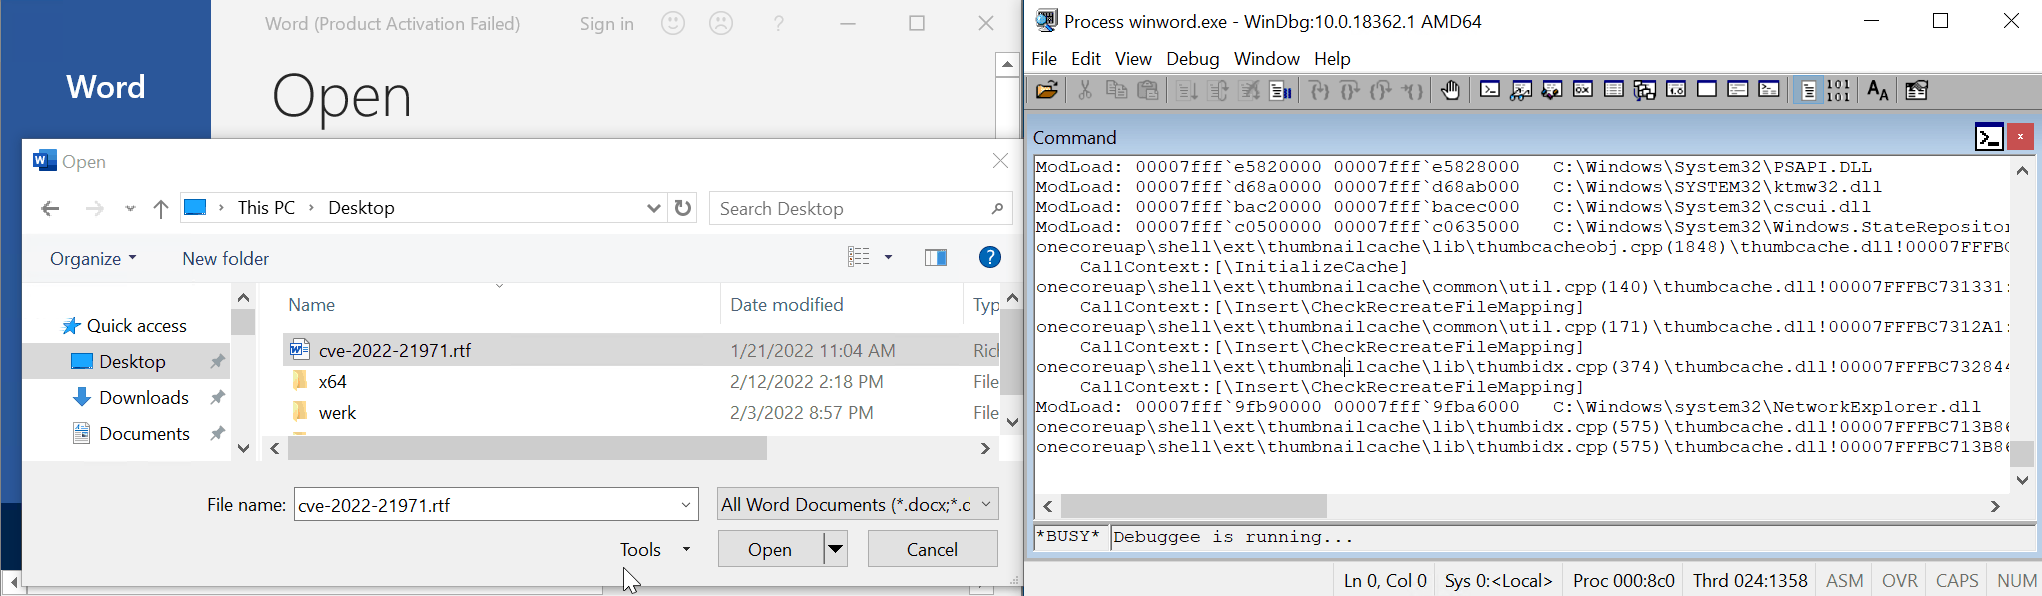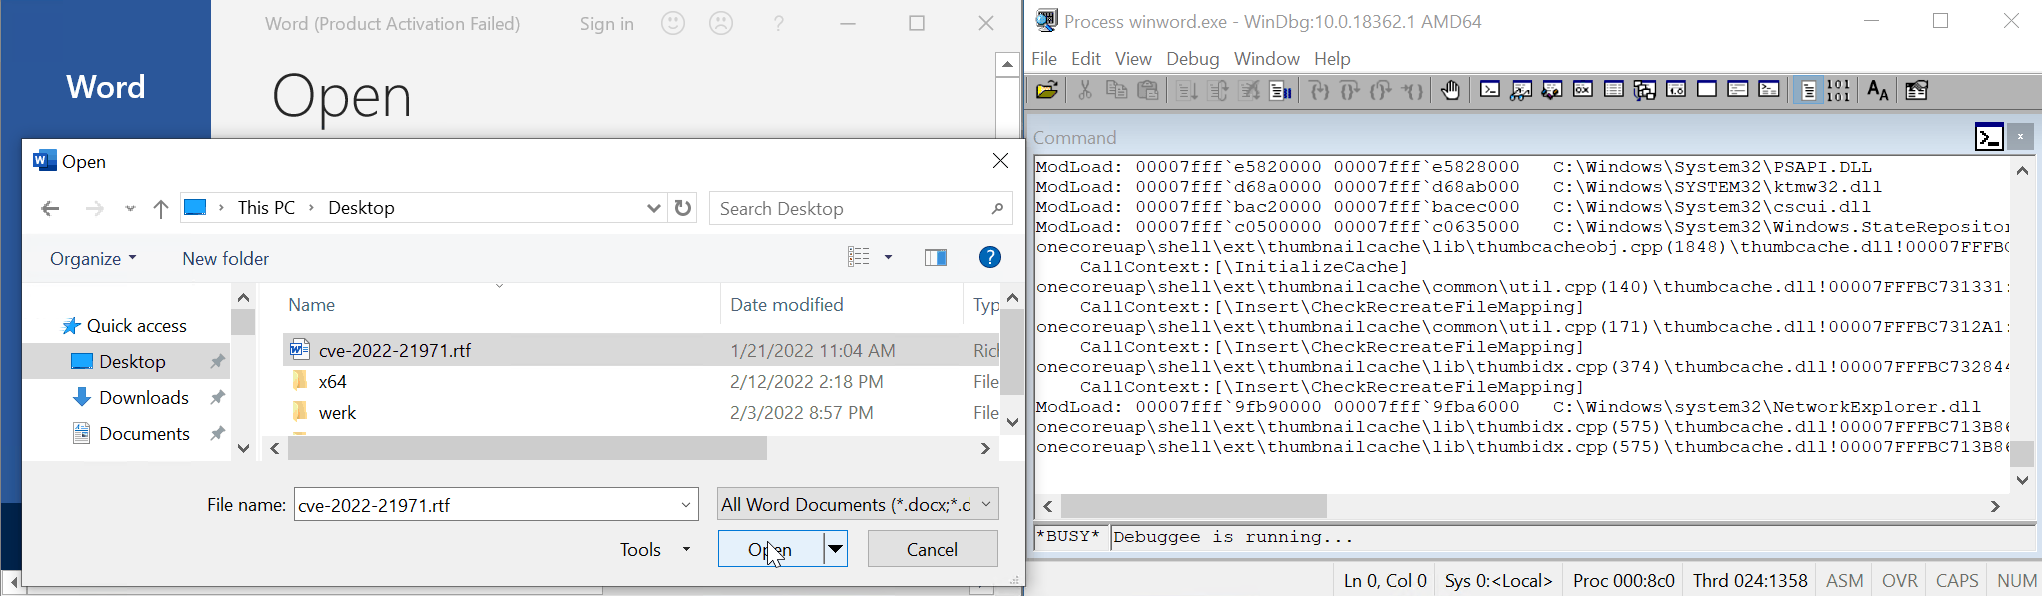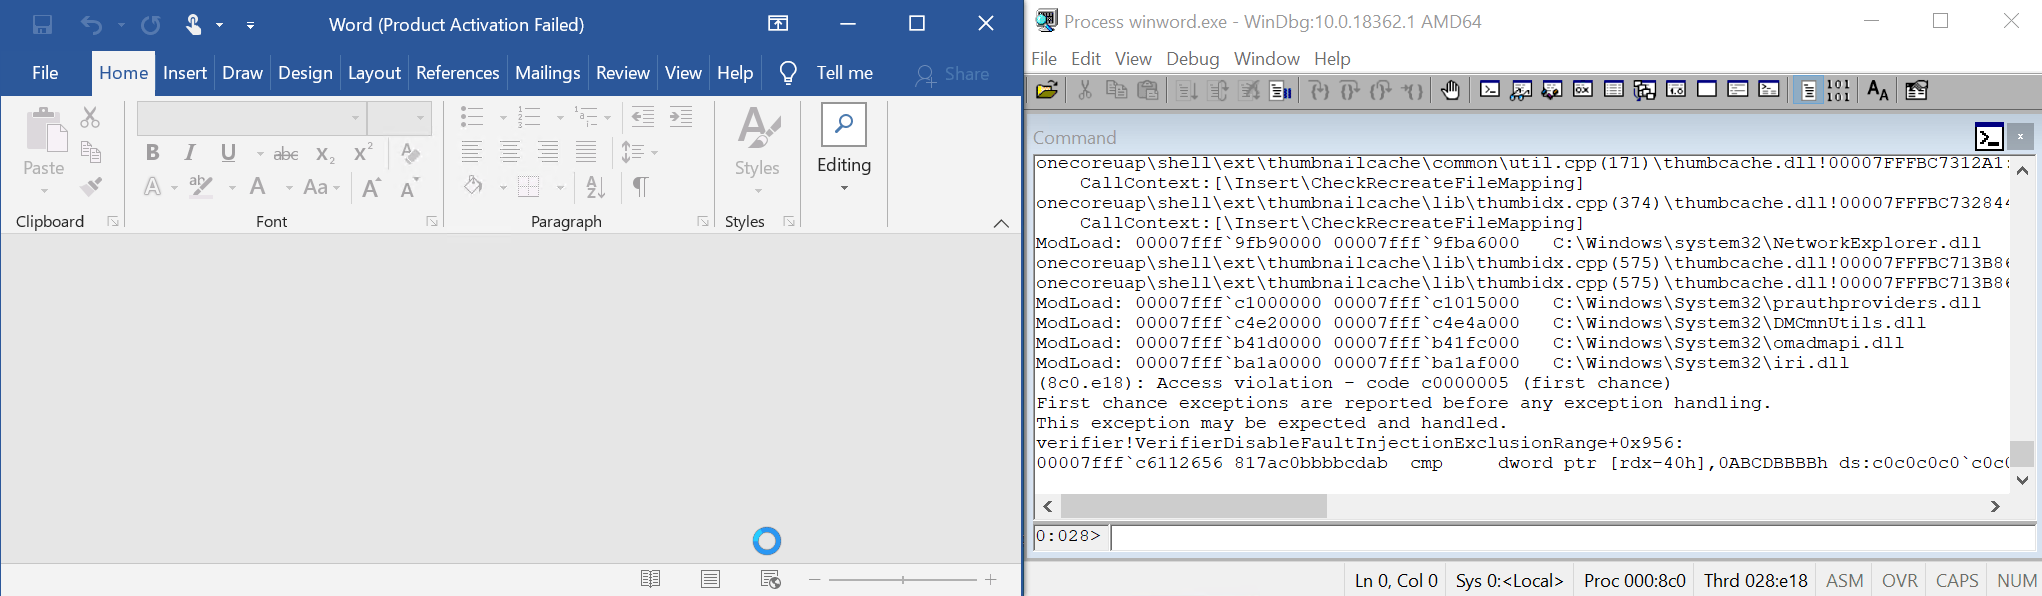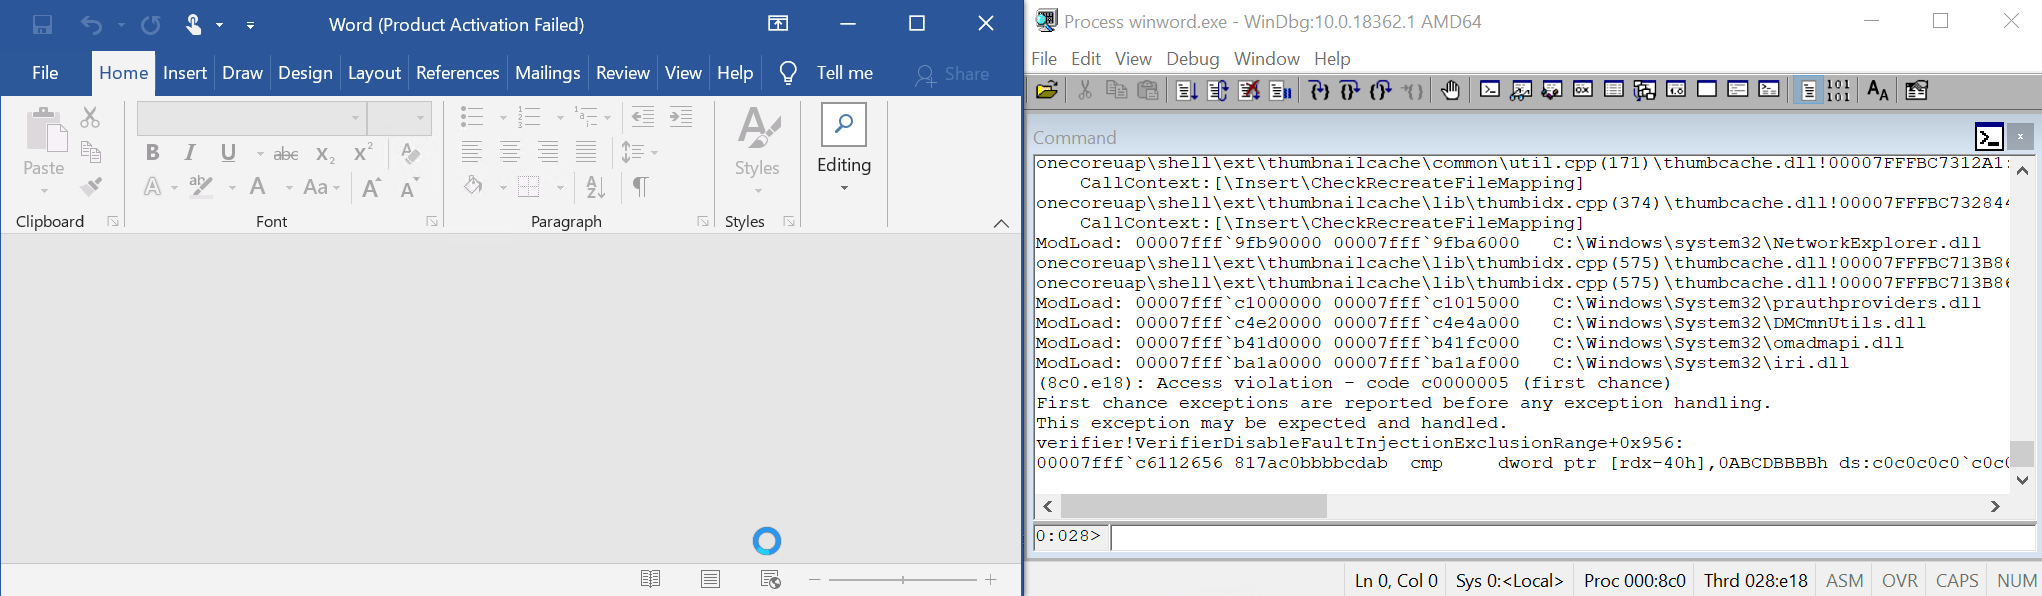 malwareman007/cve-2022-21971
POC Of CVE-2022-21971
 maherazzouzi/cve-2024-26817-amdkfd
Potential Integer Overflow Leading To Heap Overflow in AMD KFD.
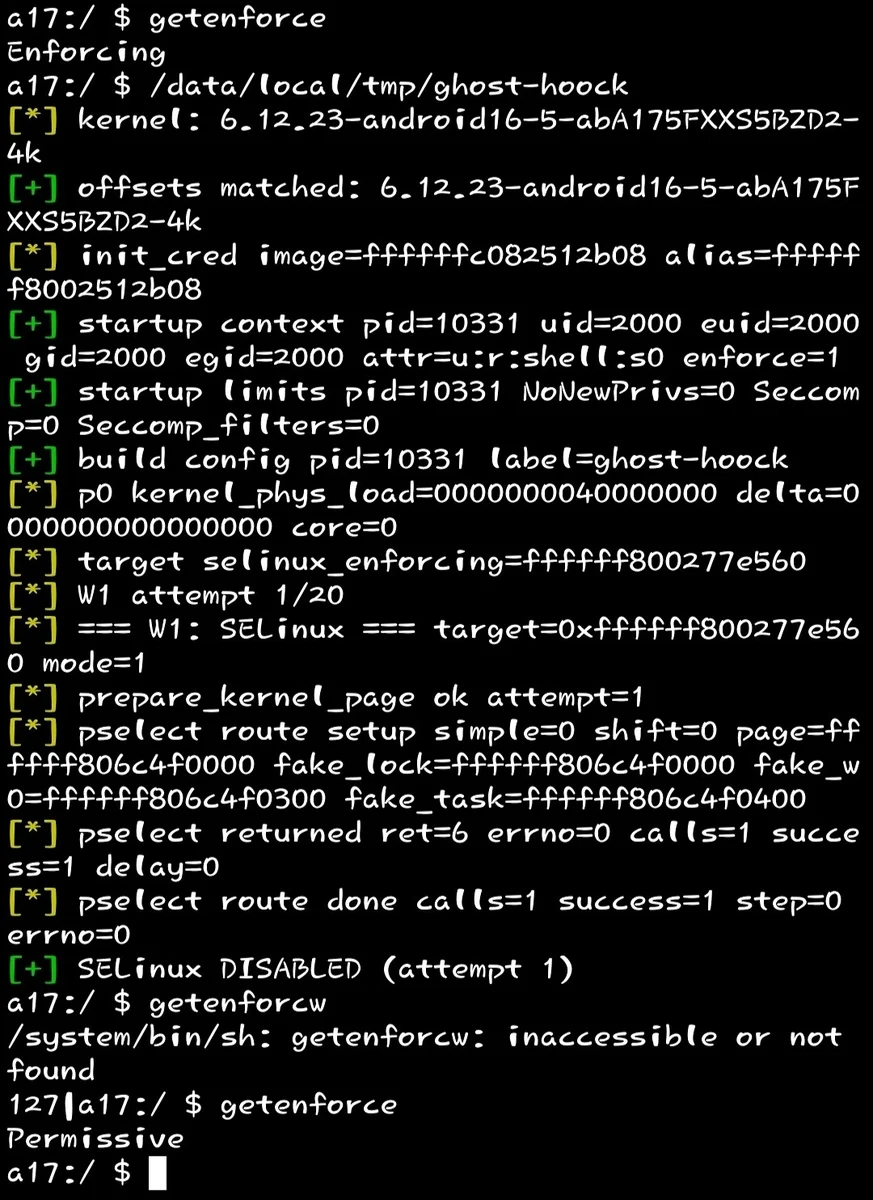 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 bbaranoff/cve-2023-4863
Proof-of-concept exploit for CVE-2023-4863, a heap buffer overflow in libwebp, demonstrating crash trigger and reproduction steps with…
 se1ims/pixelsmash
Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 alonhr/secdrvpoolleak
A PoC for CVE-2018-7250
 jvidhan/cve-2026-43687
Reverse engineering notes and a self-contained PoC for the macOS NFS client access-cache race (CVE-2026-43687), with kext disassembly diff and dtrace…
 abraxas/cve-2026-19445-sni-uaf
Proof-of-concept lab for CVE-2026-19445, a CPython ssl SNI SSLContext use-after-free where a remote TLS client frees the server's dispatch context…
 learningdisordercapital35/cve_2025_24257----not-mine
Demonstrate CVE-2025-24257 with a public PoC for IOGPUFamily kernel heap OOB read/write and panic analysis
 abraxas/vbox-lsilogic-sas-config
VirtualBox 7.2.20 - Critical - Local - Type confusion / arb R/W - SAS1068 CONFIG SCSI-SPI overlay
 abraxas/qemu-xhci-complete-uaf
QEMU 11.1.2 - High - Local - UAF - xhci_complete leftover of CVE-2026-17588 doorbell DMA
 abraxas/qemu-nvme-sgl-bar
QEMU 11.1.2 - High - Local - UAF - NVMe SGL span into BAR0 incomplete CVE-2021-3929
 abraxas/sqlite-fts5-securedel
SQLite 3.53.4 - High - Local - Crash - FTS5 secure-delete PutVarint footer overrun
 pwnhacker0x18/ios-kernel-crash
Exploit for CVE-2018-4407-Memory Corruption








