
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended

 gmh5225/awesome-web3-security
A curated list of Web3 Security materials and resources for Pentesters and Bug Hunters.
 lkarlslund/deploy-goad
Script to install prerequisites for deploying GOAD on Ubuntu Linux 22.04
 pmaynard/ics-testbed-framework
Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…
 matheusht/redthread
An autonomous red-teaming engine for LLMs. RedThread manages the full security lifecycle: generating adversarial attacks, executing precision…
 xcellerator/freebsd_kernel_hacking
Learning FreeBSD Kernel Hacking - Exercises
 dinosn/mariadb-13-rce-lab
MariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…
 abraxas/cve-2026-87902
Proof-of-concept and disclosure pack for CVE-2026-87902, an unauthenticated local file inclusion in WordPress Core via locate_template(), with a…
 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
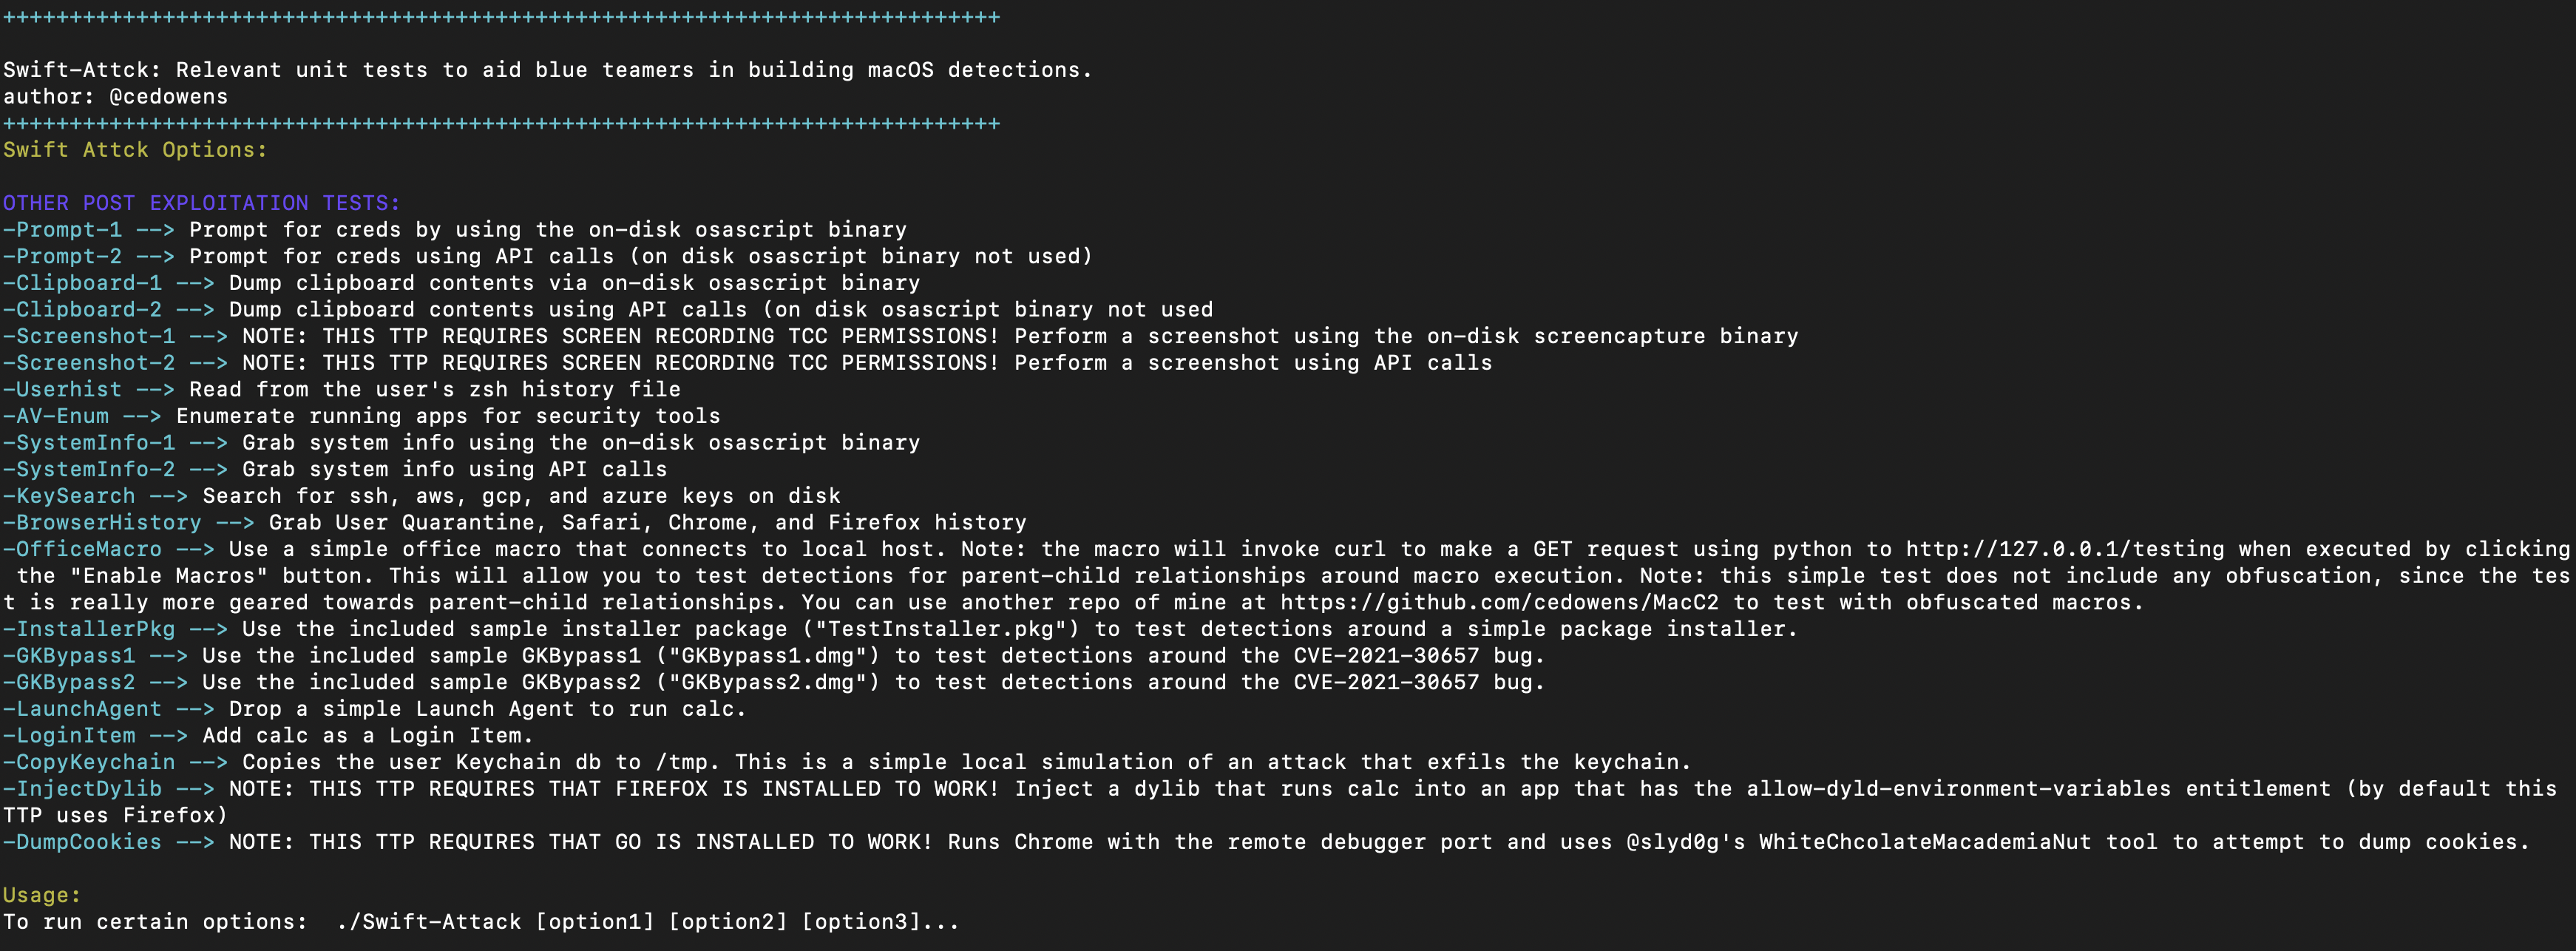 cedowens/swift-attack
Unit tests for blue teams to aid with building detections for some common macOS post exploitation methods.
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 zwjjustdoit/xstream-1.4.17
XSTREAM<=1.4.17漏洞复现(CVE-2021-39141、CVE-2021-39144、CVE-2021-39150)
 mainframed/dc30_workshop
DEFCON 30 Mainframe buffer overlow workshop container
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
 ressl/cve-2026-87902-poc
PoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…
 jonwiggins/xmloxide
A pure Rust reimplementation of libxml2
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…








