
 #1
Tools for managing, sharing, and integrating Indicators of Compromise (IOCs) into security defenses.
Kitploit recommended
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 alex-cart/leaf
Linux Evidence Acquisition Framework
 infostealers-stats/data-breach
A continuously updated resource that catalogs confirmed data breaches from across the globe. Each entry includes the breach name, usually aligned…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
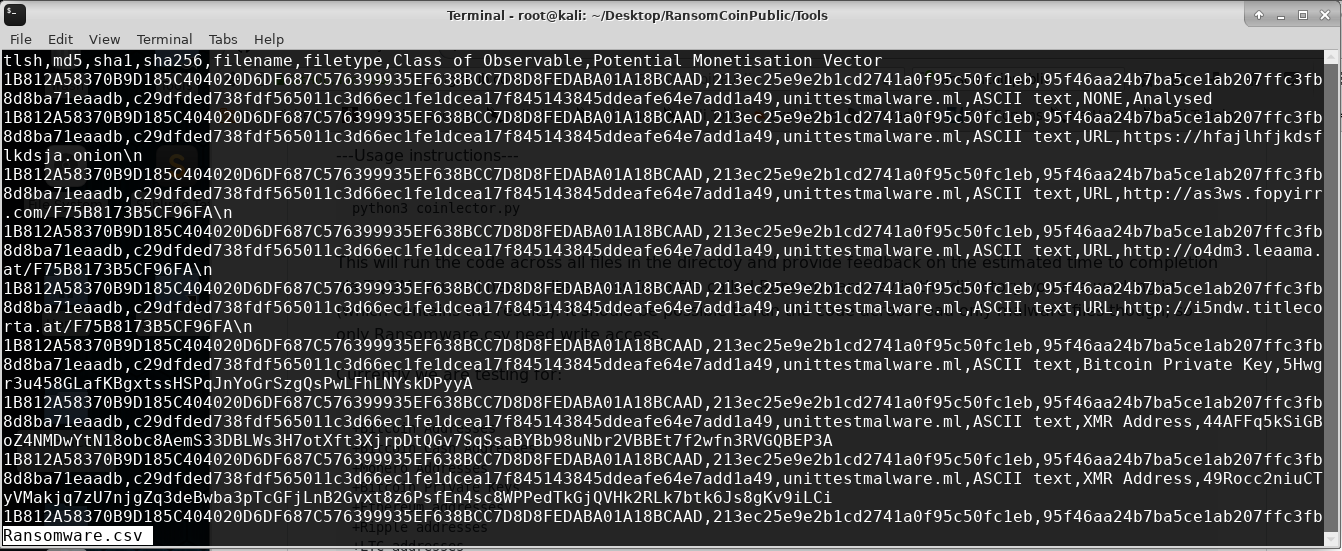 concinnity-risks/ransomcoinpublic
A DFIR tool to extract cryptocoin addresses and other indicators of compromise from binaries.
 malienist/lupo
WinDbg plugin for automated malware dynamic analysis and IOC extraction. Executes within the debugger to collect predefined indicators and writes…
 taxiiproject/libtaxii
A Python library for handling TAXII Messages invoking TAXII Services.
 carbonblack/active_c2_ioc_public
Active C2 IoCs
 deepfield/public-research
DDoS botnet research and indicators of compromise from Nokia Deepfield ERT
 essexrich/threatactors-ttps
Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
 ethan-andrews/exploitarium-detections
KQL detection rules for Microsoft Sentinel and Defender XDR covering the bikini/exploitarium anonymous disclosure — a personal research archive of…
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
 ctrlaltint3l/intelligence
Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
 emcghee/payloadautomation
Automates Cobalt Strike payload development, testing, and deployment via a Python-to-Sleep bridge; includes artifact inspection, IoC tracking, and…
 nicolasriverocorvalan/cloud-sniper
Virtual Security Operations Center
 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.








