
 #1
Tools for managing, sharing, and integrating Indicators of Compromise (IOCs) into security defenses.
Kitploit recommended

 st0rn/siglens
Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
 hackinghippo/log4shell_ioc_ips
log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 archanchoudhury/msdt_cve-2022-30190
This Repository Talks about the Follina MSDT from Defender Perspective
 arpsyndicate/vedas-signatures
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 14,000 CVEs
 citrix/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
 threatray/threat-research
IoCs and YARA rules from Threatray's Threat Research
 chaitanyakrishna/iocscraper
IOCPARSER.COM is a Fast and Reliable service that enables you to extract IOCs and intelligence from different data sources.
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 0xtoxin/malware-iocs
Just my findings of malwares
 reddrip7/log4shell_cve-2021-44228_related_attacks_iocs
Curated repository of Indicators of Compromise (IOCs), attack source IPs, and Snort/Suricata detection rules for Log4Shell (CVE-2021-44228) attacks.
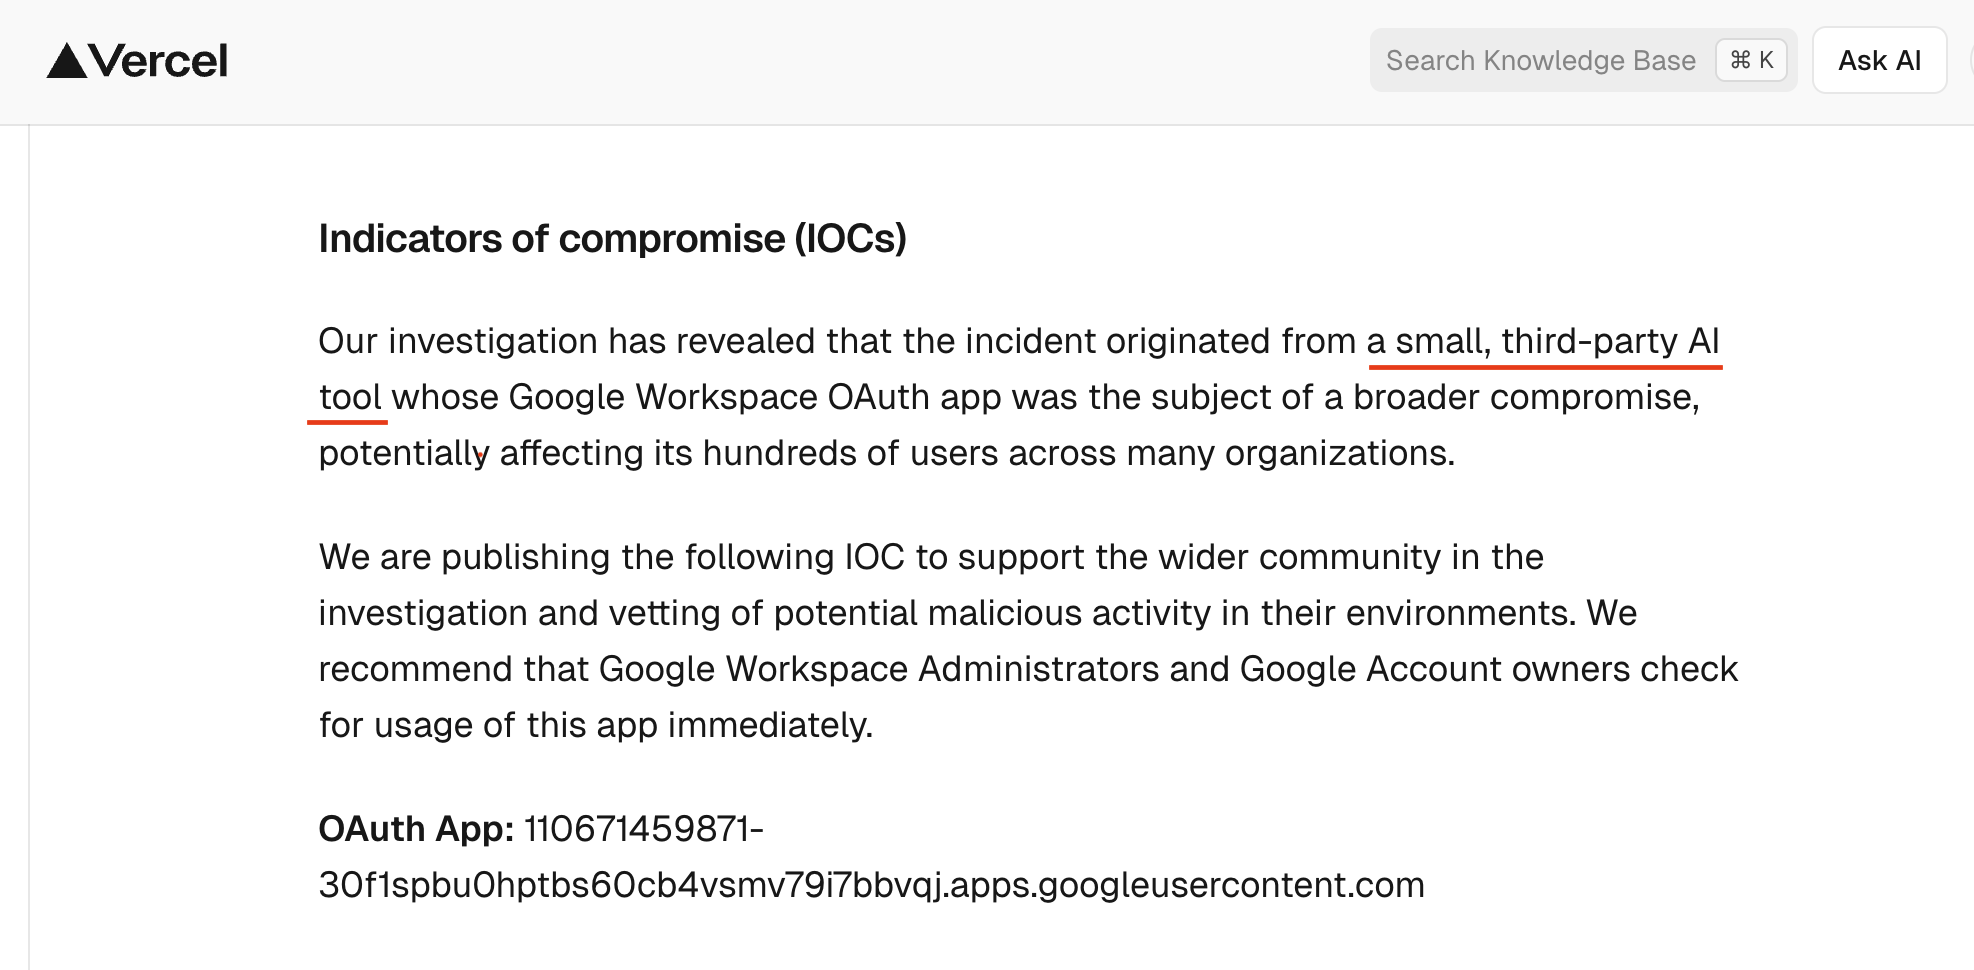 opensourcemalware/vercel-april2026-incident-response
This is an incident response playbook we created for the Vercel April 2026 compromise
 backbay-labs/thrunt-god
Threat hunting command system for agentic IDEs
 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…








