
 #1
Tools for managing, sharing, and integrating Indicators of Compromise (IOCs) into security defenses.
Kitploit recommended
 abhinavbom/threat-intelligence-hunter
TIH is an intelligence tool that helps you in searching for IOCs across multiple openly available security feeds and some well known APIs. The idea…

 wiz-sec-public/wiz-research-iocs
Curated public database of indicators of compromise aggregated by Wiz Research for threat detection, hunting, and incident response workflows.
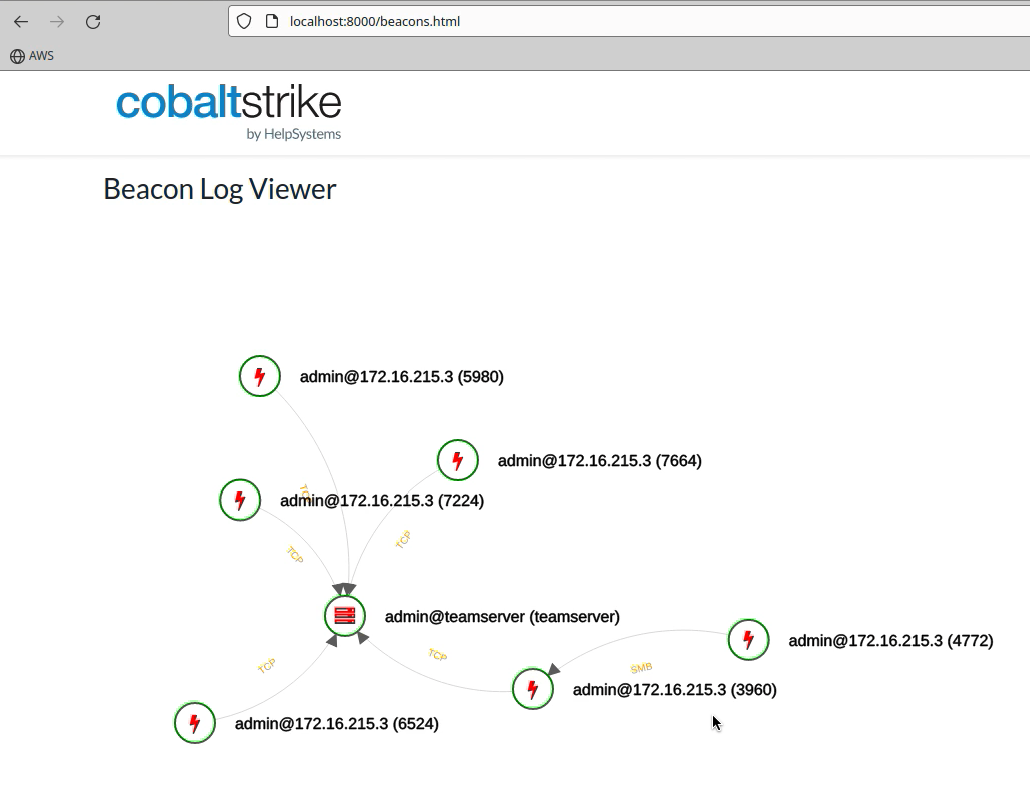 cobalt-strike/sleep_python_bridge
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…
 mubix/cve-2021-44228-log4shell-hashes
Hashes for vulnerable LOG4J versions
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 silascutler/malpipe
Malware/IOC ingestion and processing engine
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 huntresslabs/threat-intel
This repository contains supplemental items including IOCs, and signatures discussed in Huntress blogposts, and other media.
 assafmo/xioc
Extract indicators of compromise from text, including "escaped" ones.
 cado-security/dfir_resources_revil_kaseya
Resources for DFIR Professionals Responding to the REvil Ransomware Kaseya Supply Chain Attack
 elastic/labs-releases
Elastic Security Labs releases
 cronup/malware-iocs
Collects and organizes malware indicators of compromise (IOCs) for rapid threat detection, incident response, and actionable intelligence sharing.
 adulau/the-art-of-pivoting
The Art of Pivoting - Techniques for Intelligence Analysts to Discover New Relationships in a Complex World
 google/threat-team
No longer maintained. Please refer to Google Threat Intelligence / Virus Total collections.
 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
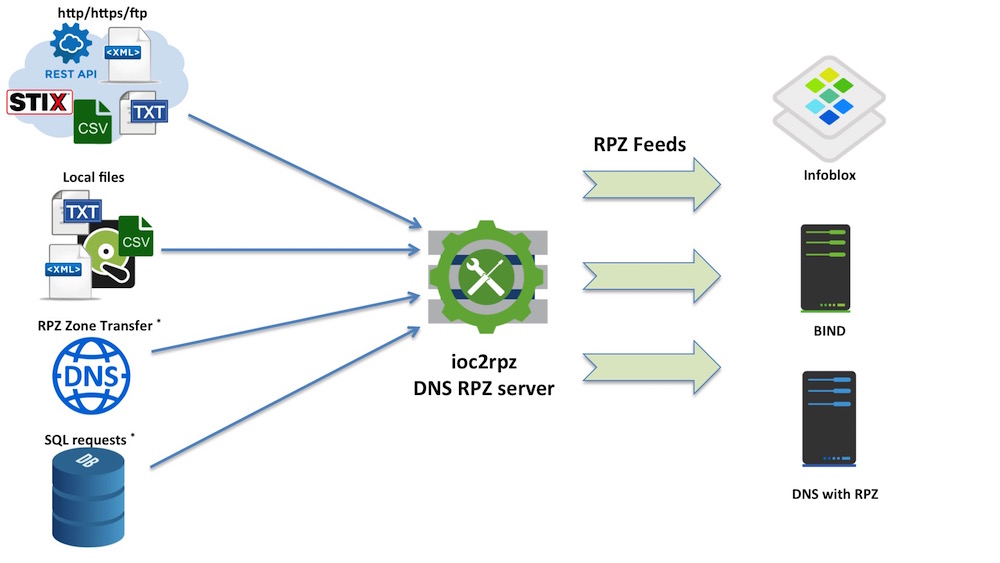 homas/ioc2rpz
ioc2rpz is a place where threat intelligence meets DNS.








