#1
IR playbooks, triage, case management, evidence collection, and incident management tools.
Kitploit recommended

 deepfence/packetstreamer
⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐
 yelparchive/osxcollector
A forensic evidence collection & analysis toolkit for OS X
 maliceio/malice
VirusTotal Wanna Be - Now with 100% more Hipster
 google/stenographer
Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those…
 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud
 snovvcrash/usbrip
Tracking history of USB events on GNU/Linux
 dropbox/securitybot
Distributed alerting for the masses!
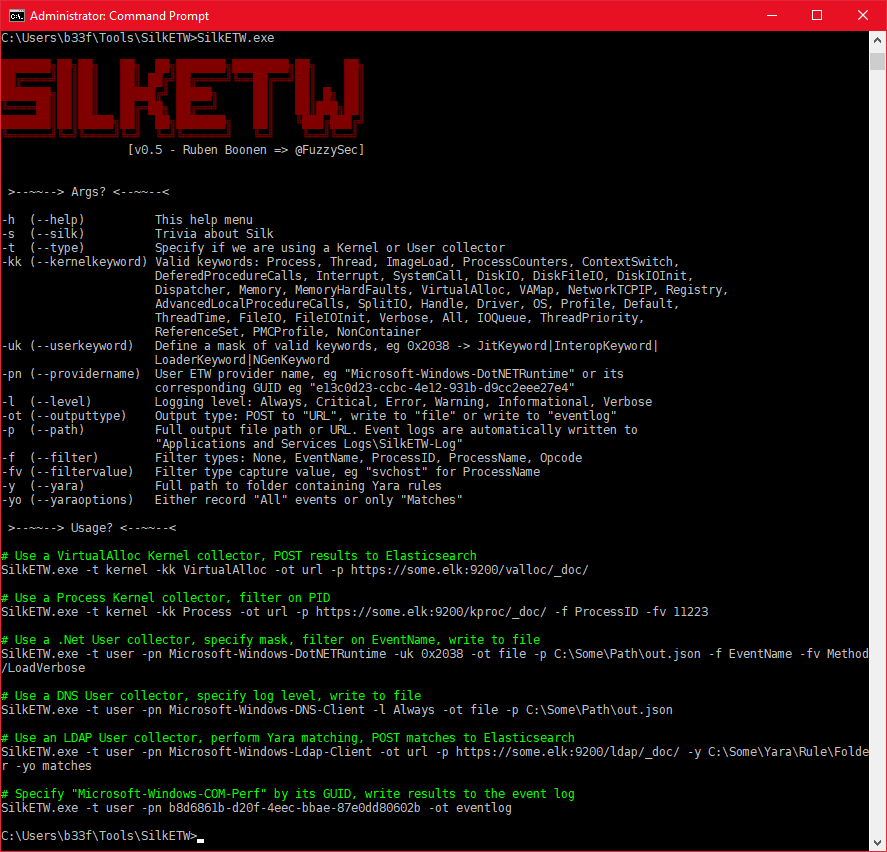 mandiant/silketw
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…

 cloudflare/mitmengine
A MITM (monster-in-the-middle) detection tool. Used to build MALCOLM:
 grapl-security/grapl
Graph platform for Detection and Response
 t4d/stalkphish
StalkPhish - The Phishing kits stalker, harvesting phishing kits for investigations.
 mandiant/mandiant-azure-ad-investigator
Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
 ebwi11/agentsmith-hids
By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.
 maldev-academy/dumpchromesecrets
Extract data from modern Chrome versions, including refresh tokens, cookies, saved credentials, autofill data, browsing history, and bookmarks
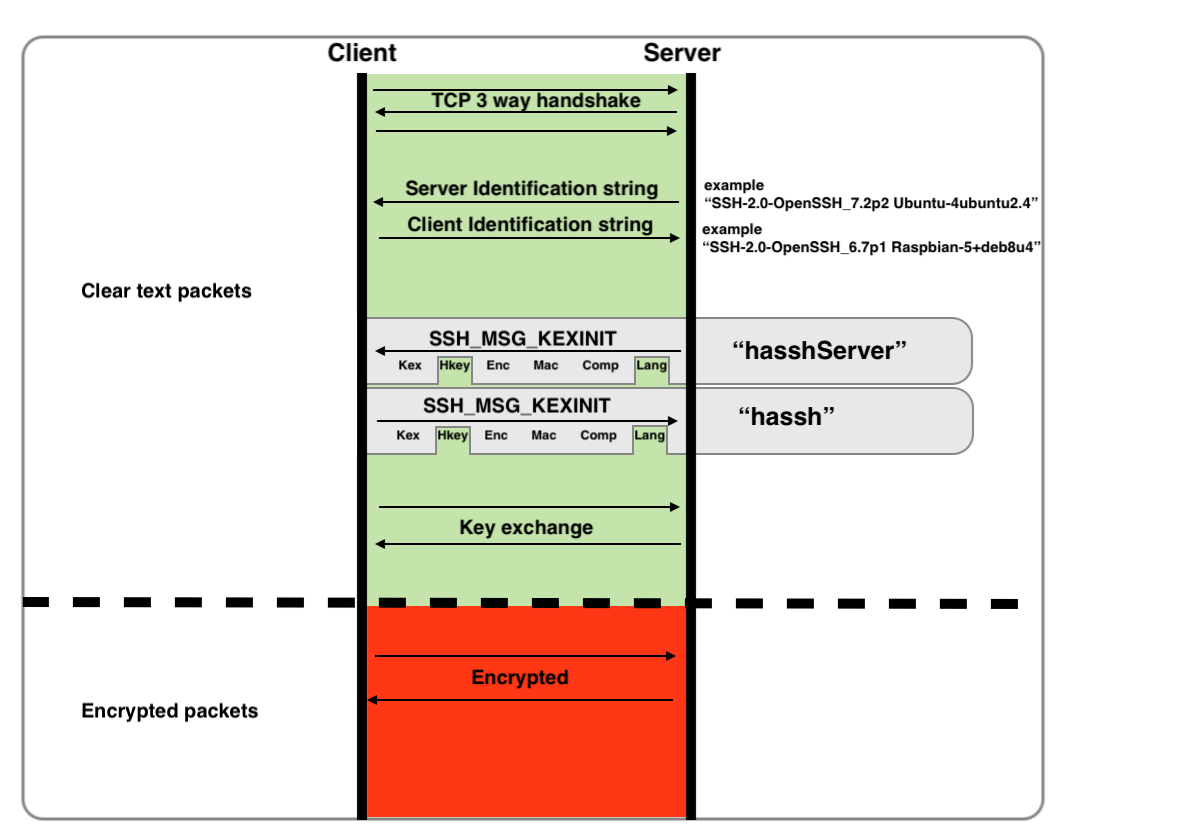 salesforce/hassh
HASSH is a network fingerprinting standard which can be used to identify specific Client and Server SSH implementations. The fingerprints can be…
 blackhillsinfosec/eventlogging
Automation scripts to deploy Windows Event Forwarding, Sysmon, and custom audit policies in an Active Directory environment.