#1
IR playbooks, triage, case management, evidence collection, and incident management tools.
Kitploit recommended

 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
 nbulischeck/tyton
Kernel-Mode Rootkit Hunter
 dfir-dd/dfir-toolkit
CLI tools for forensic investigation of Windows artifacts
 certcc/cve-2021-44228_scanner
Scanners for Jar files that may be vulnerable to CVE-2021-44228
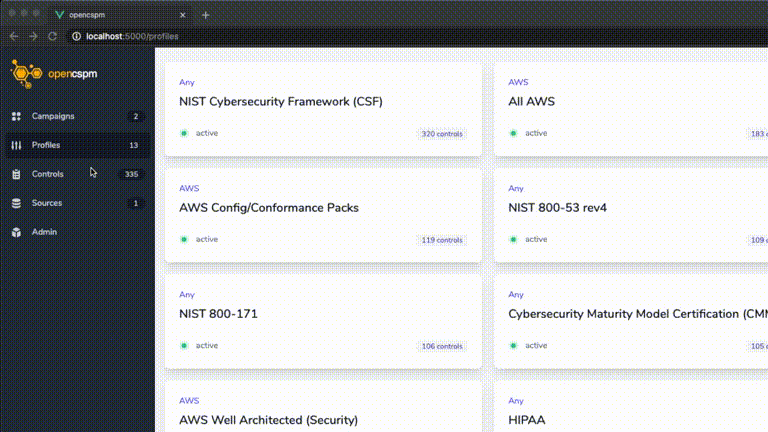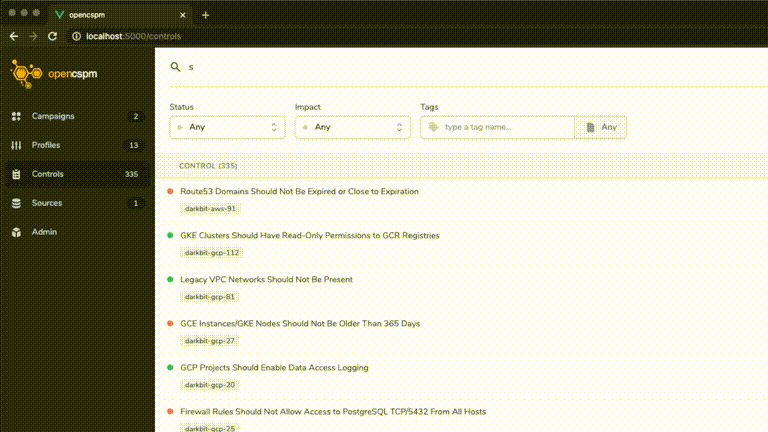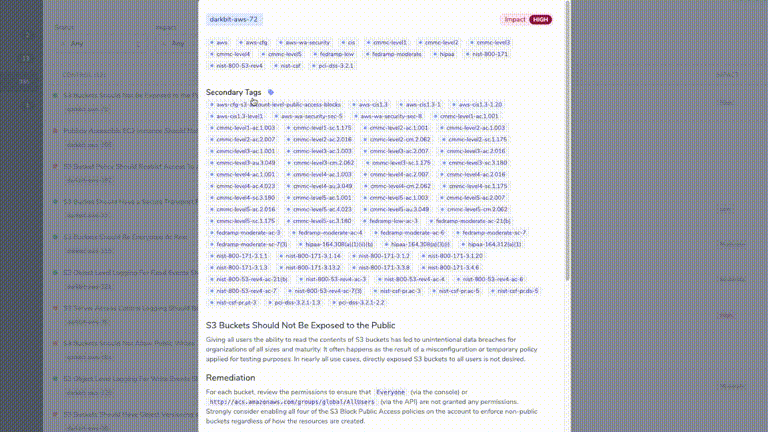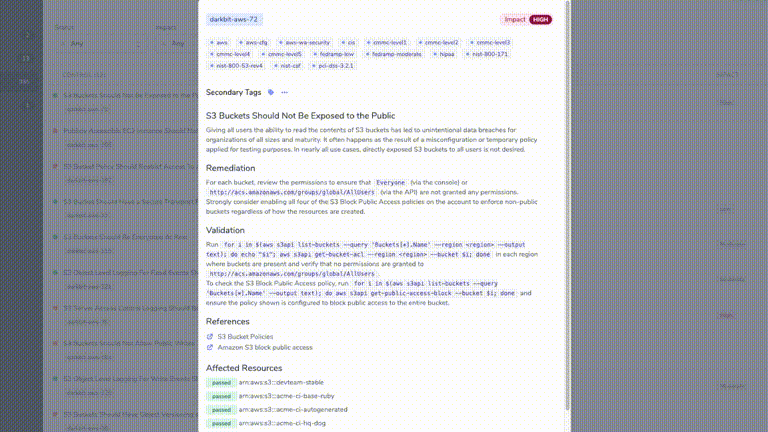 opencspm/opencspm
Open Cloud Security Posture Management Engine
 captaingeech42/ransomwatch
Ransomware leak site monitoring
 cisagov/esxiargs-recover
A tool to recover from ESXiArgs ransomware
 trailofbits/sinter
A user-mode application authorization system for MacOS written in Swift
 cado-security/varc
Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…
 504ensicslabs/damm
Differential Analysis of Malware in Memory
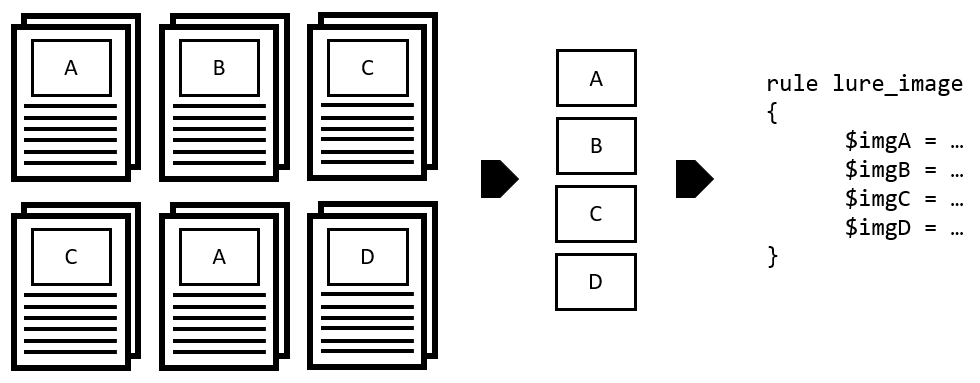 target/halogen
Automatically create YARA rules from malicious documents.
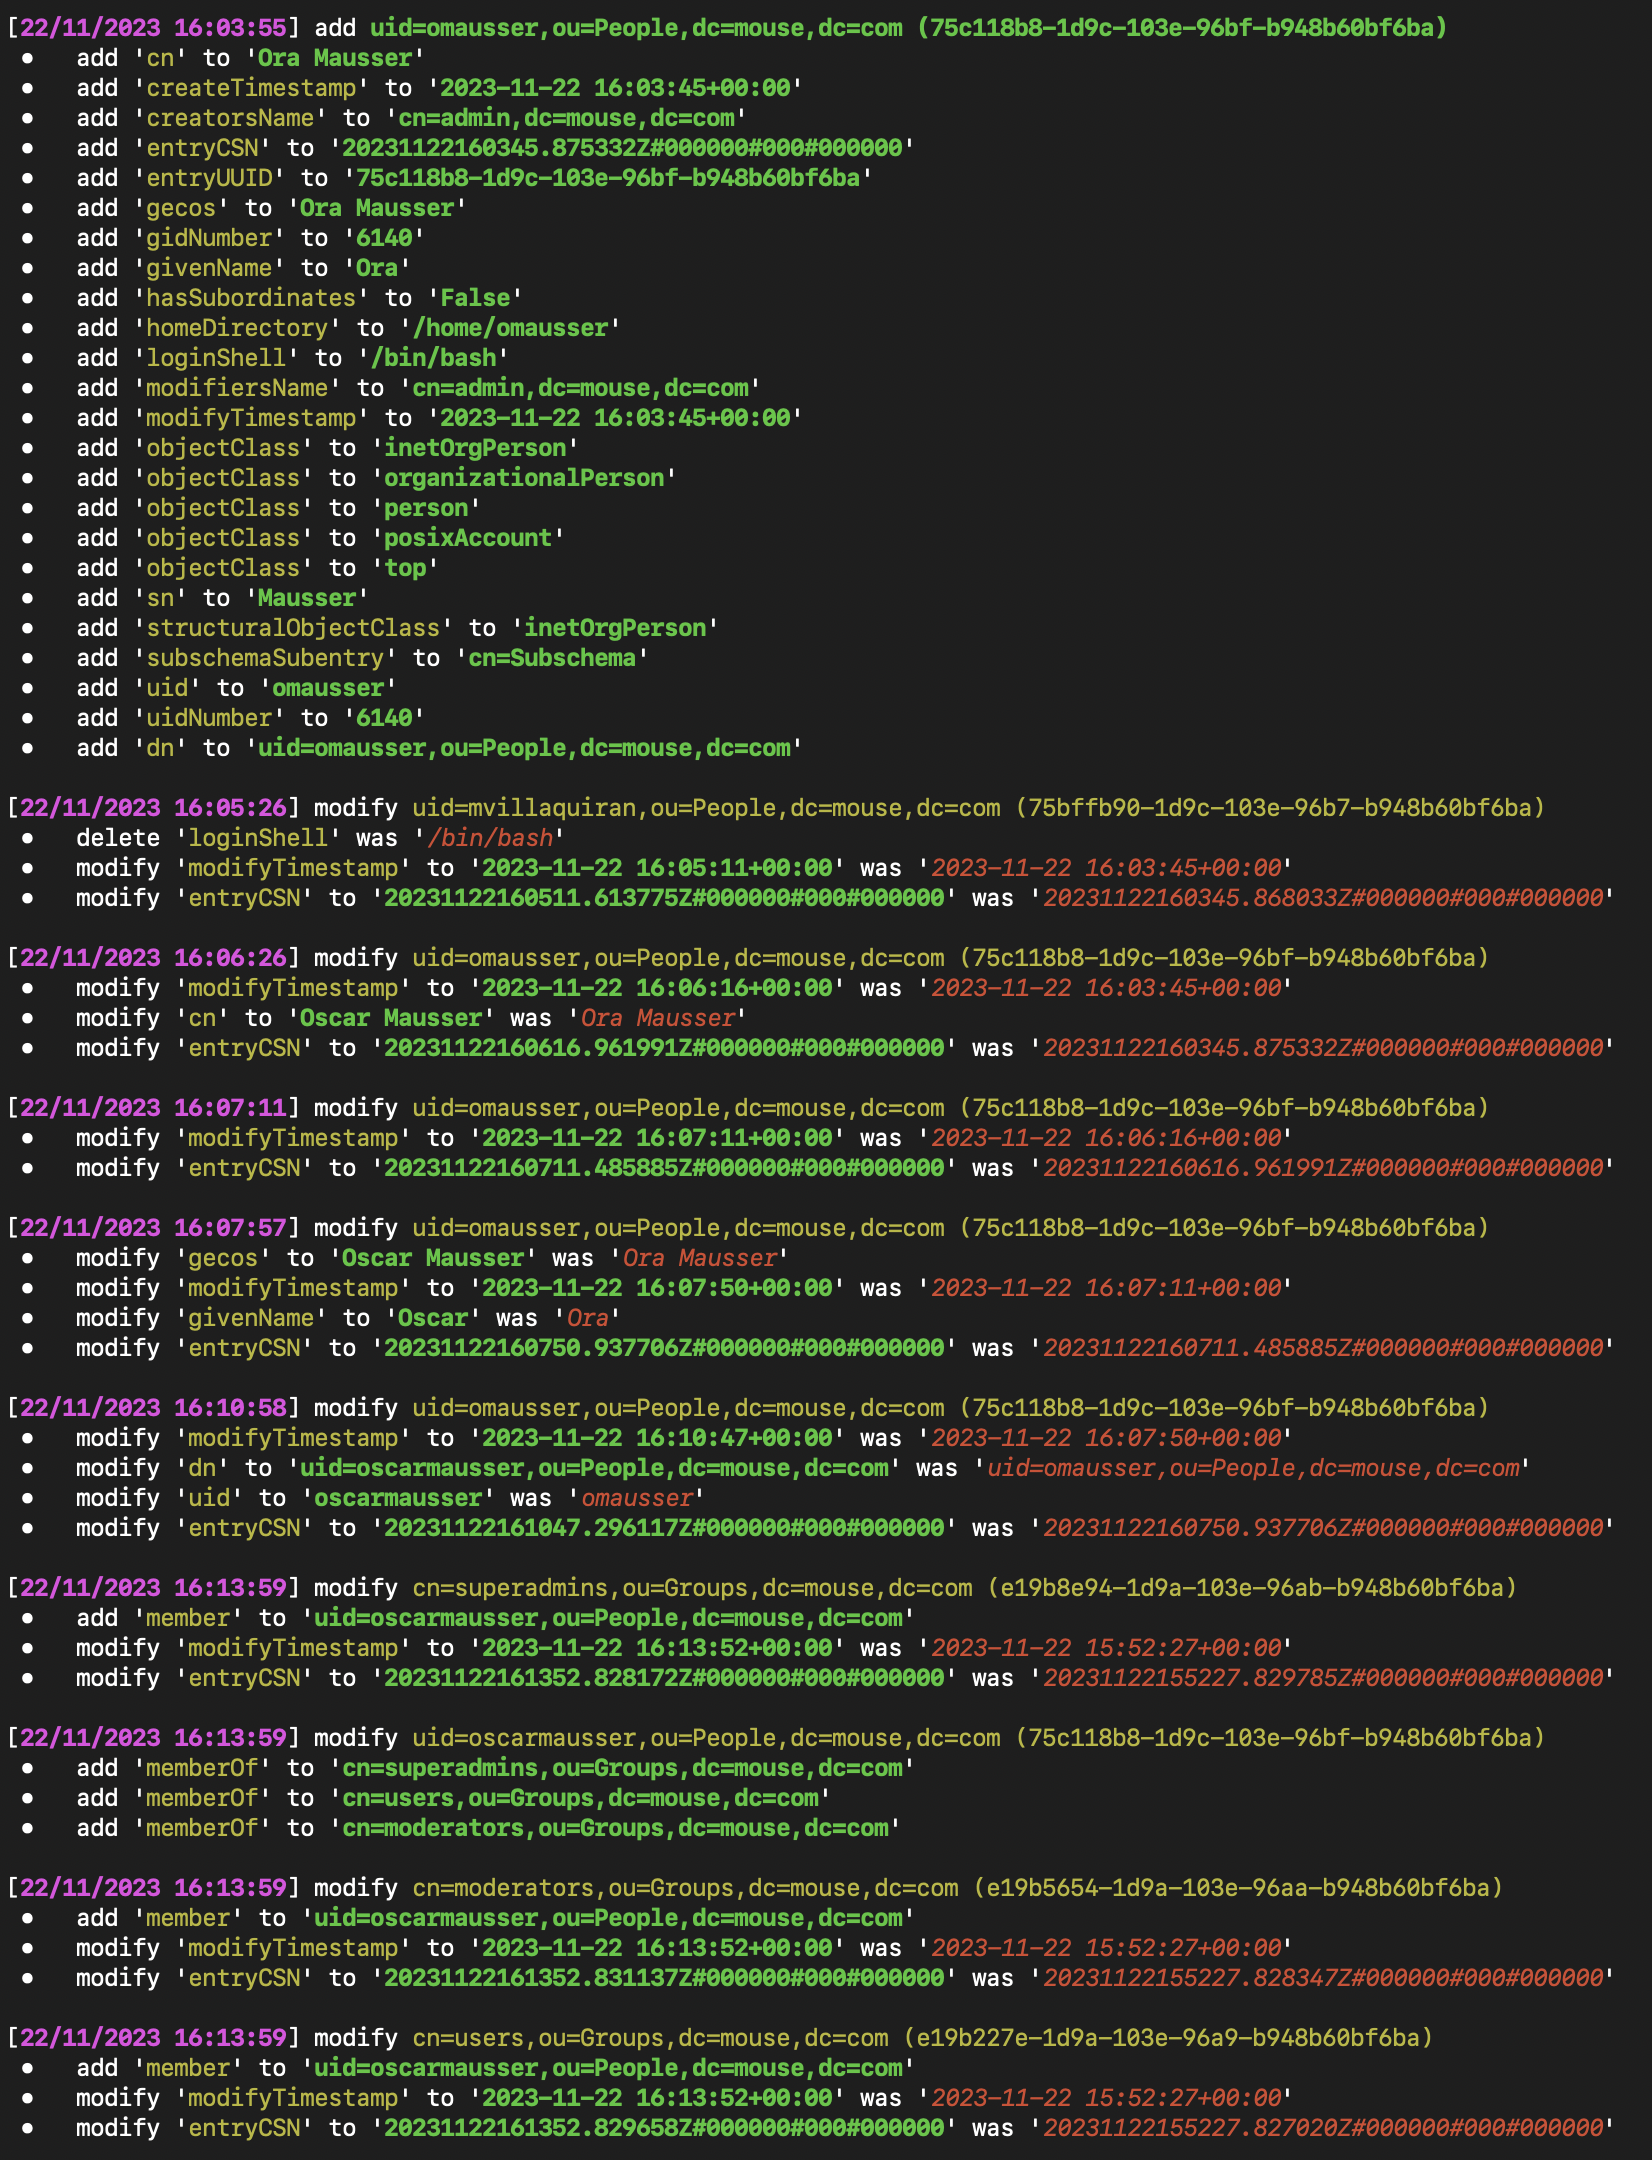 megamansec/ldap-monitoring-watchdog
LDAP Watchdog: A real-time linux-compatible LDAP monitoring tool for detecting directory changes, providing visibility into additions, modifications,…
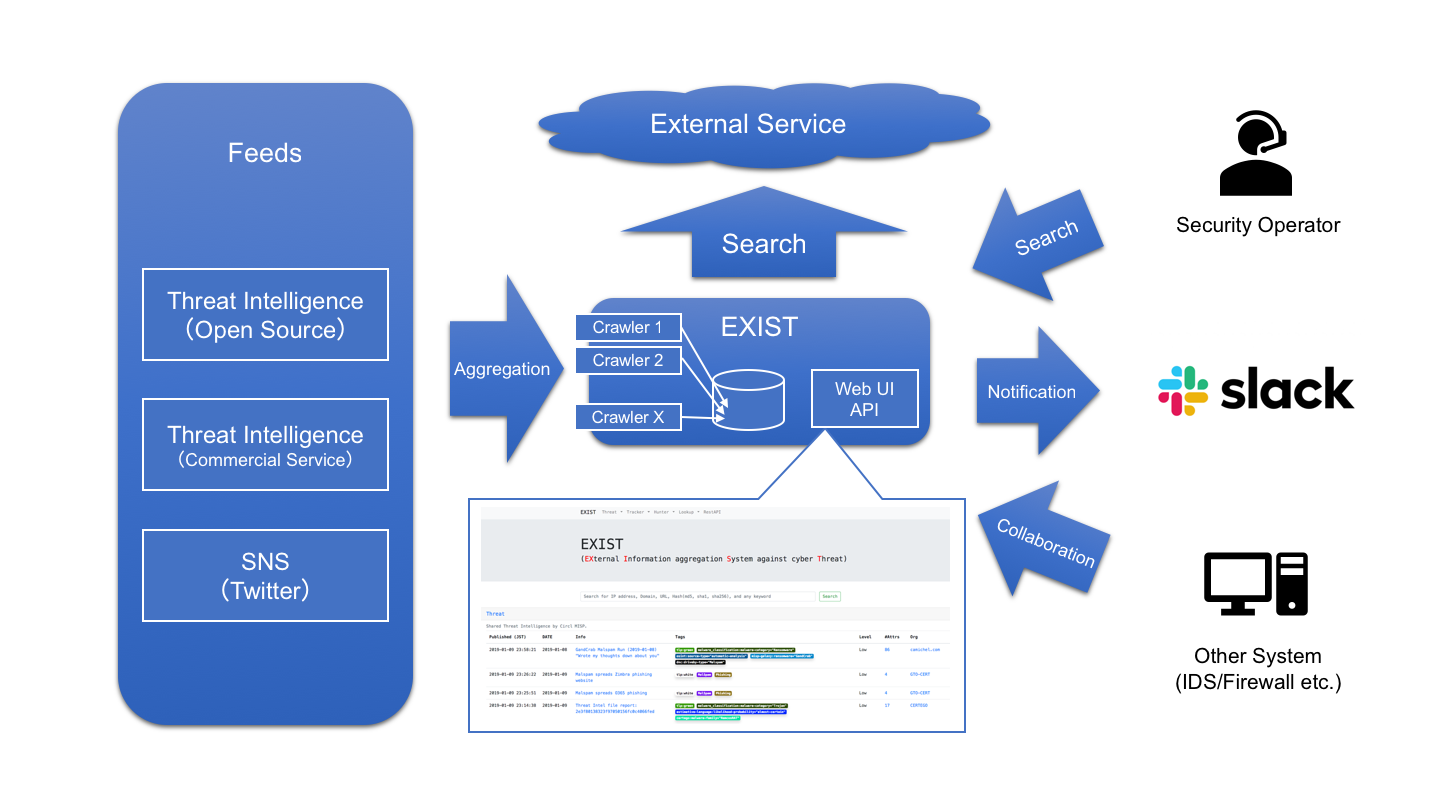 nict-csl/exist
EXIST is a web application for aggregating and analyzing cyber threat intelligence.
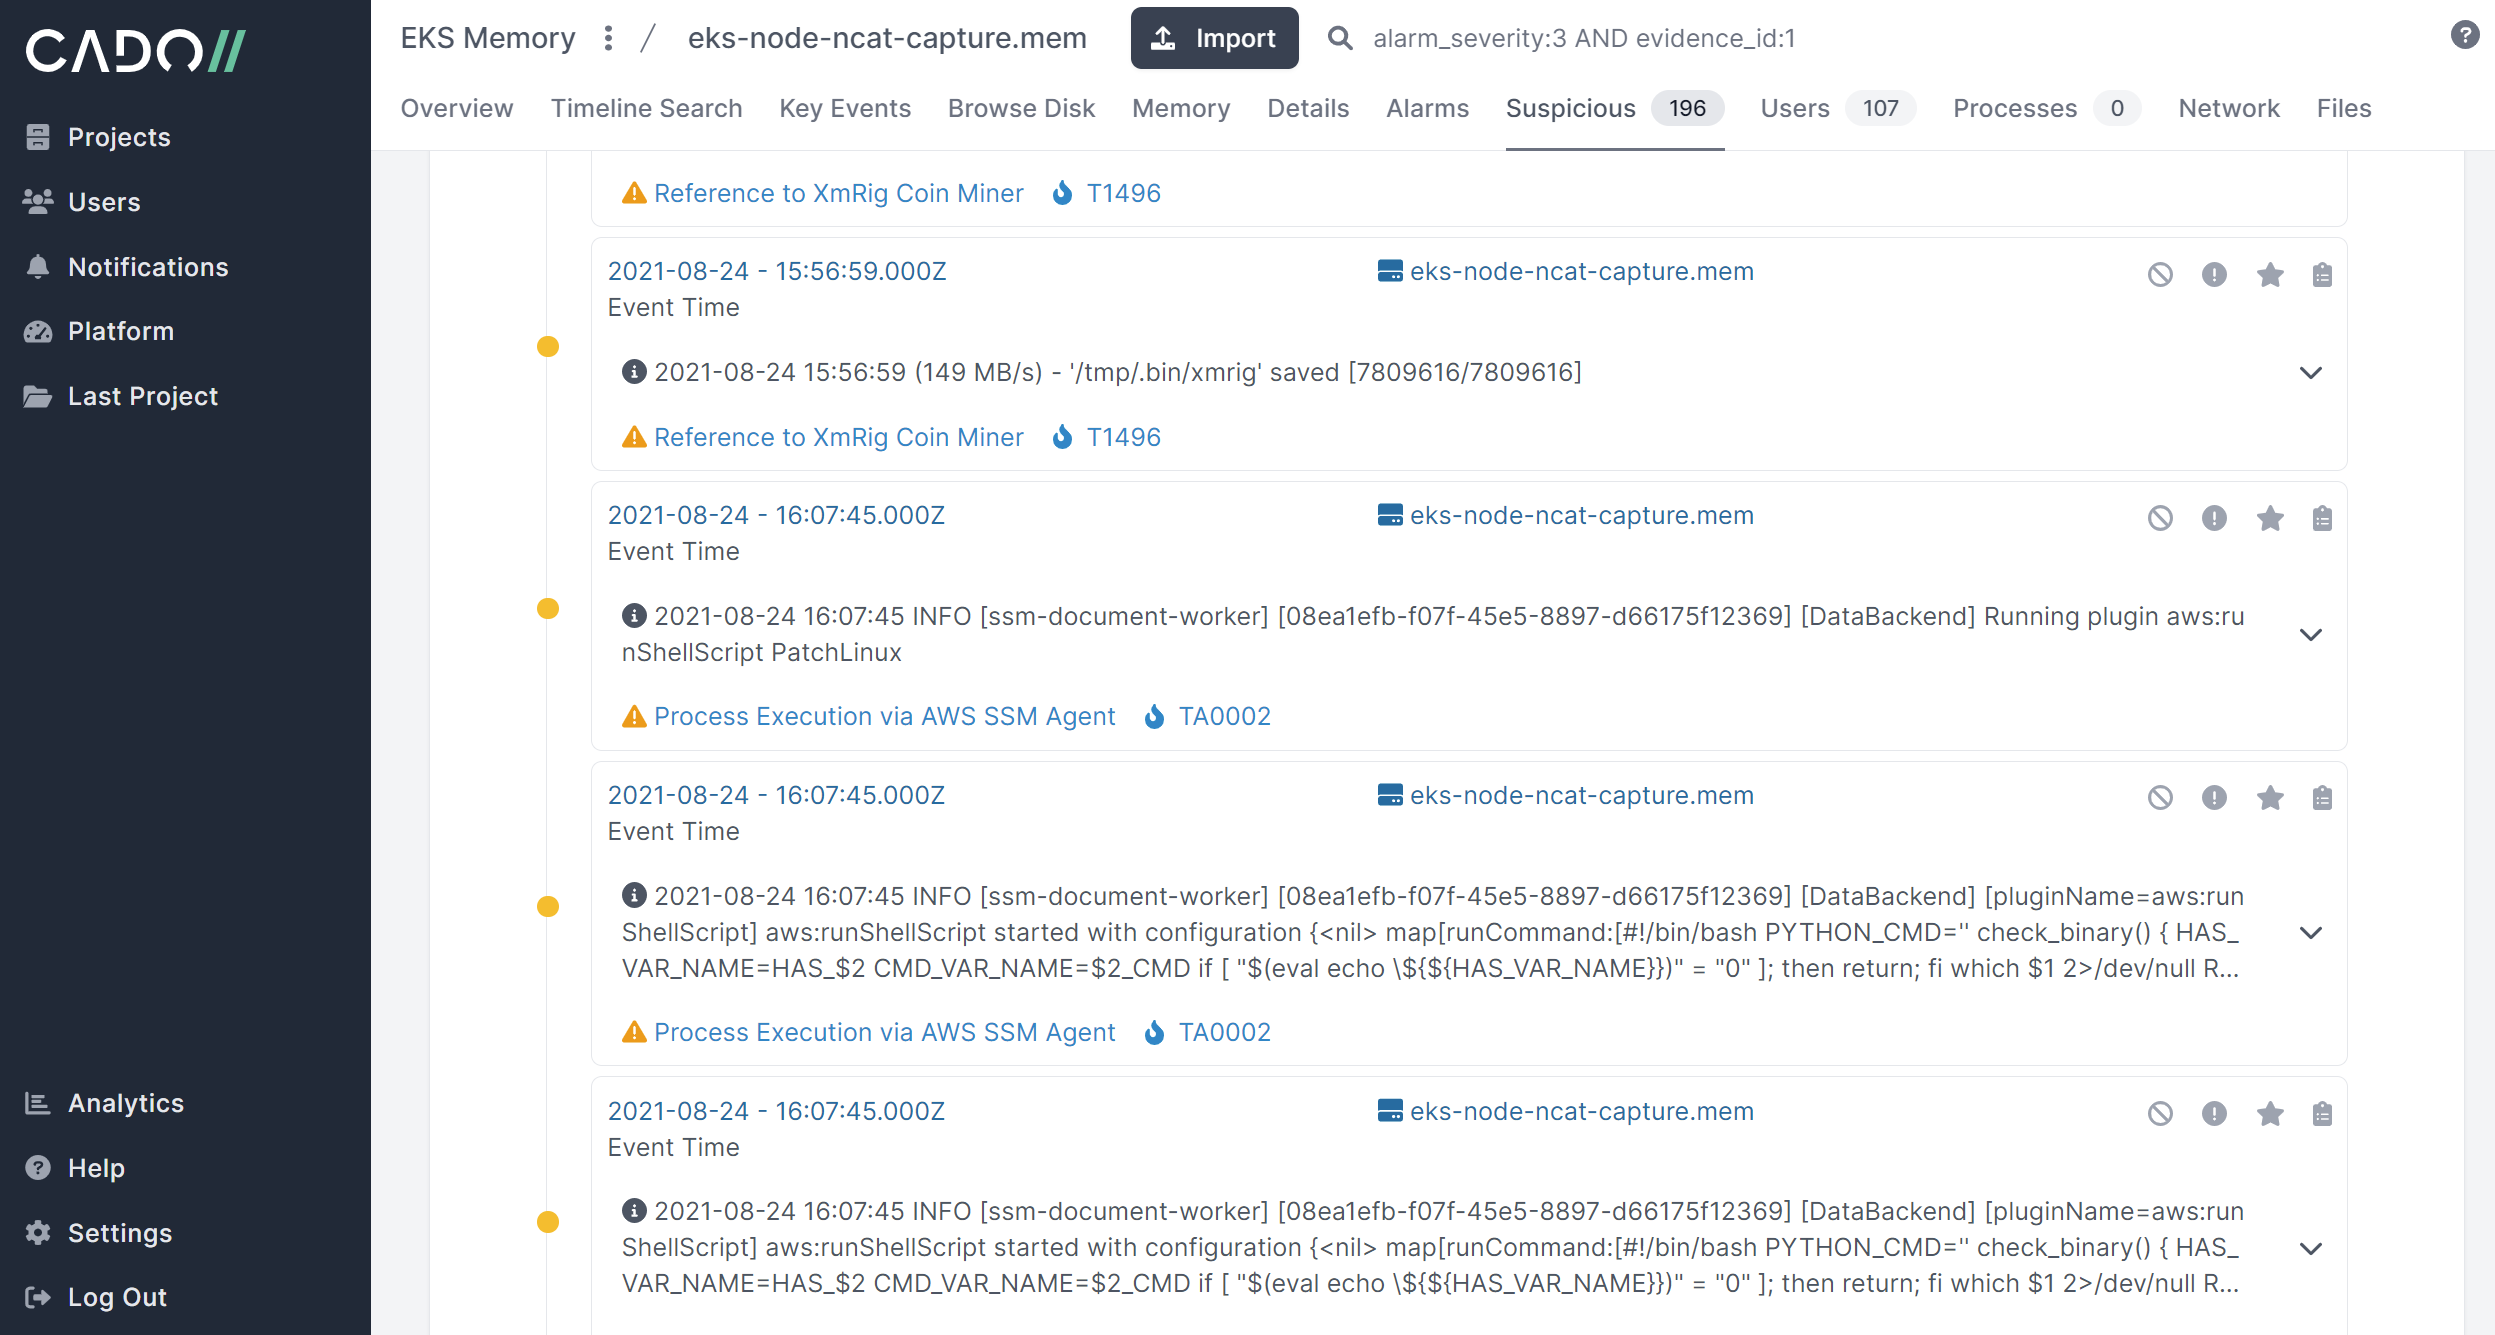 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
 0x0v1/audix
Audix is a PowerShell tool to quickly configure the Windows Event Audit Policies for security monitoring