Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Incident Response | Kitploit
Categories

Incident Response

IR playbooks, triage, case management, evidence collection, and incident management tools.

Kitploit recommended

Top tools

10 selected
velociraptor preview#1

velociraptor

GitHubvelocidex/velociraptor
4.2k15h 59m ago
osquery preview#2

osquery

GitHubosquery/osquery
23.4k2 days ago
wazuh preview#3

wazuh

GitHubwazuh/wazuh
16.5k3 days ago
volatility3 preview#4

volatility3

GitHubvolatilityfoundation/volatility3
4.3k7 days ago
iris-web preview#5

iris-web

GitHubdfir-iris/iris-web
1.5k1 day ago
fleet preview#6

fleet

GitHubfleetdm/fleet
6.9k3h 33m ago
timesketch preview#7

timesketch

GitHubgoogle/timesketch
3.4k6h 35m ago
plaso preview#8

plaso

GitHublog2timeline/plaso
2.2k11 days ago
autopsy preview#9

autopsy

GitHubsleuthkit/autopsy
3.3k4 months ago
mvt preview#10

mvt

GitHubmvt-project/mvt
14.6k2 days ago
NewestRelevanceMost popularRecently updated
1348 results
PersistenceSniper preview

PersistenceSniper

GitHublast-byte/persistencesniper

Powershell module that can be used by Blue Teams, Incident Responders and System Administrators to hunt persistences implanted in Windows machines.…

defensive-toolspersistence-mechanismsforensics+1
2.1k1 year ago
Tourmaline preview

Tourmaline

GitHubv-pun215/tourmaline

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
ioc-managementreverse-engineeringmalware-analysis+7
1013 days ago
Microsoft-Sentinel-SecOps preview

Microsoft-Sentinel-SecOps

GitHubeshlomo1/microsoft-sentinel-secops

SOC operations content for Microsoft Sentinel, including hunting queries, incident response playbooks, and security event analysis for Azure cloud…
cloud-securitythreat-intelligenceincident-response+1
2682 months ago
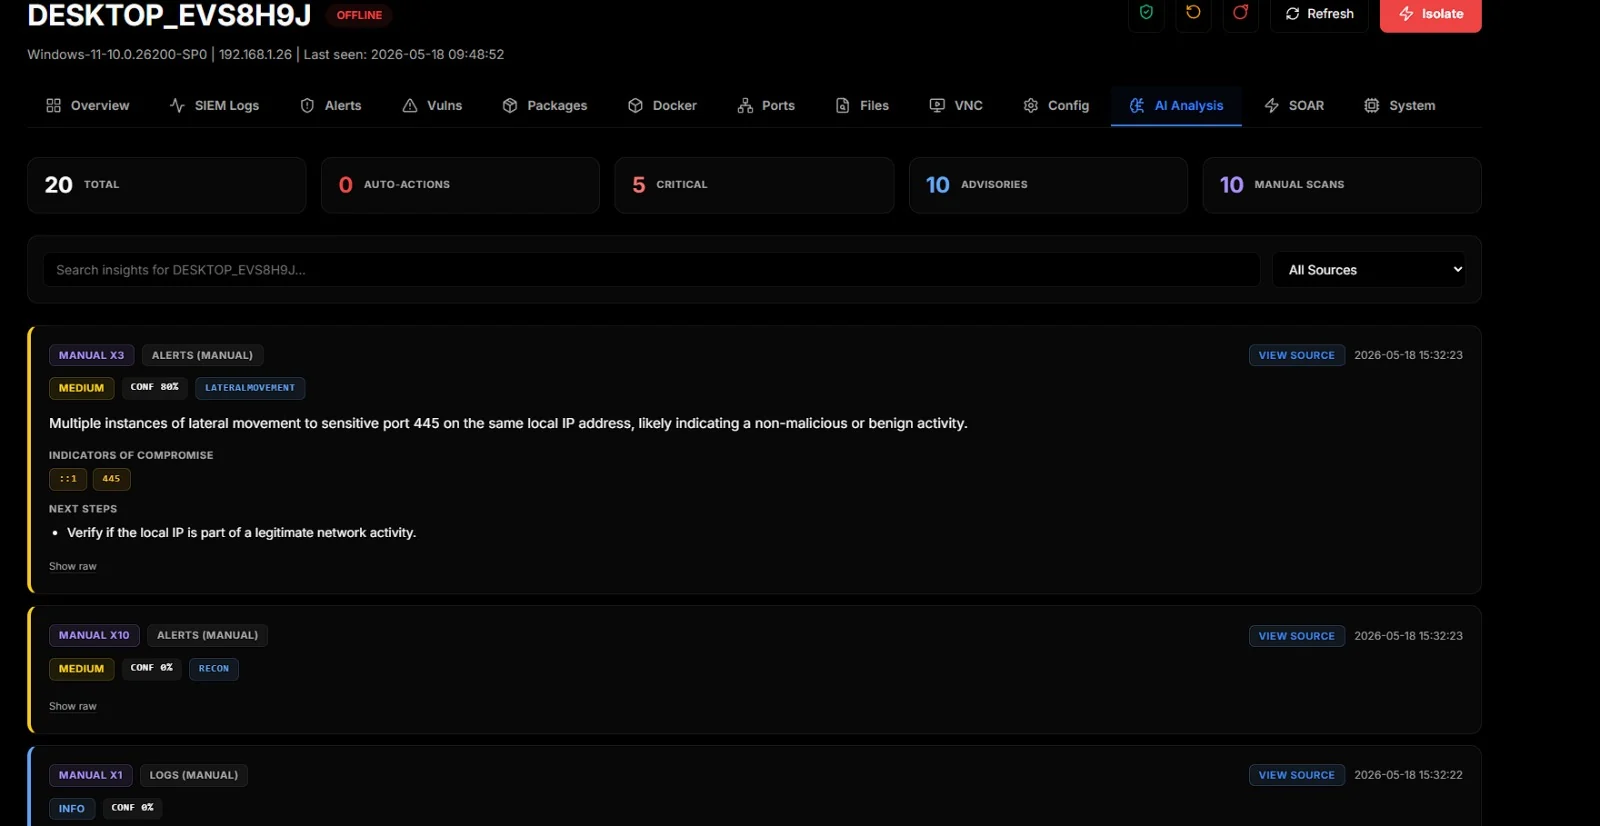
Sentora preview

Sentora

GitHubd3vhex/sentora

An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.
vulnerability-scannersthreat-intelligenceintrusion-detection+3
104 days ago
passivedns preview

passivedns

GitHubgamelinux/passivedns

A network sniffer that logs all DNS server replies for use in a passive DNS setup
network-forensicsforensicsinformation-gathering+3
1.7k2 years ago
chainsaw preview

chainsaw

GitHubwithsecureopensource/chainsaw

Rapidly Search and Hunt through Windows Forensic Artefacts

defensive-toolsvulnerability-analysisforensics+4
3.7k1 month ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ioc-managementstatic-analysisdynamic-analysis-sandboxing+10
6.1k15 days ago
Quick-Analysis preview

Quick-Analysis

GitHubvc0rexor/quick-analysis

Provides rapid triage and summarization of malware samples and threat indicators, highlighting key behavioral and contextual details for analysts.
malware-analysisthreat-intelligenceincident-response
393 years ago
MemProcFS preview

MemProcFS

GitHubufrisk/memprocfs

MemProcFS

memory-forensicsreverse-engineeringforensics+5
4.2k9 days ago
fastnetmon preview

fastnetmon

GitHubpavel-odintsov/fastnetmon

Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
packet-sniffing-analysisnetwork-mappingnetwork-security+5
3.7k21 days ago
halo-record preview

halo-record

GitHubbkuan001/halo-record

Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.

forensicssupply-chain-securityincident-response+1
639 days ago
prismor preview

prismor

GitHubprismorsec/prismor

Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…

defensive-toolscontainer-securitydevsecops+5
28316h 19m ago
EntraTrace preview

EntraTrace

GitHubbert-janp/entratrace

Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
defensive-toolsidentity-managementinformation-gathering+5
543 days ago
aiiroverlay preview

aiiroverlay

GitHubjacobideji/aiiroverlay

AI IR Overlay™ — practical incident response framework for AI agents in production. Built on NIST SP 800-61 r3, mapped to NIST AI RMF, NIST CSF 2.0,…
vulnerability-analysiscloud-securitythreat-intelligence+4
32 months ago
ciso-assistant-community preview

ciso-assistant-community

GitHubintuitem/ciso-assistant-community

GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…
defensive-toolsvulnerability-analysisconfiguration-auditing+4
4.4k6 days ago
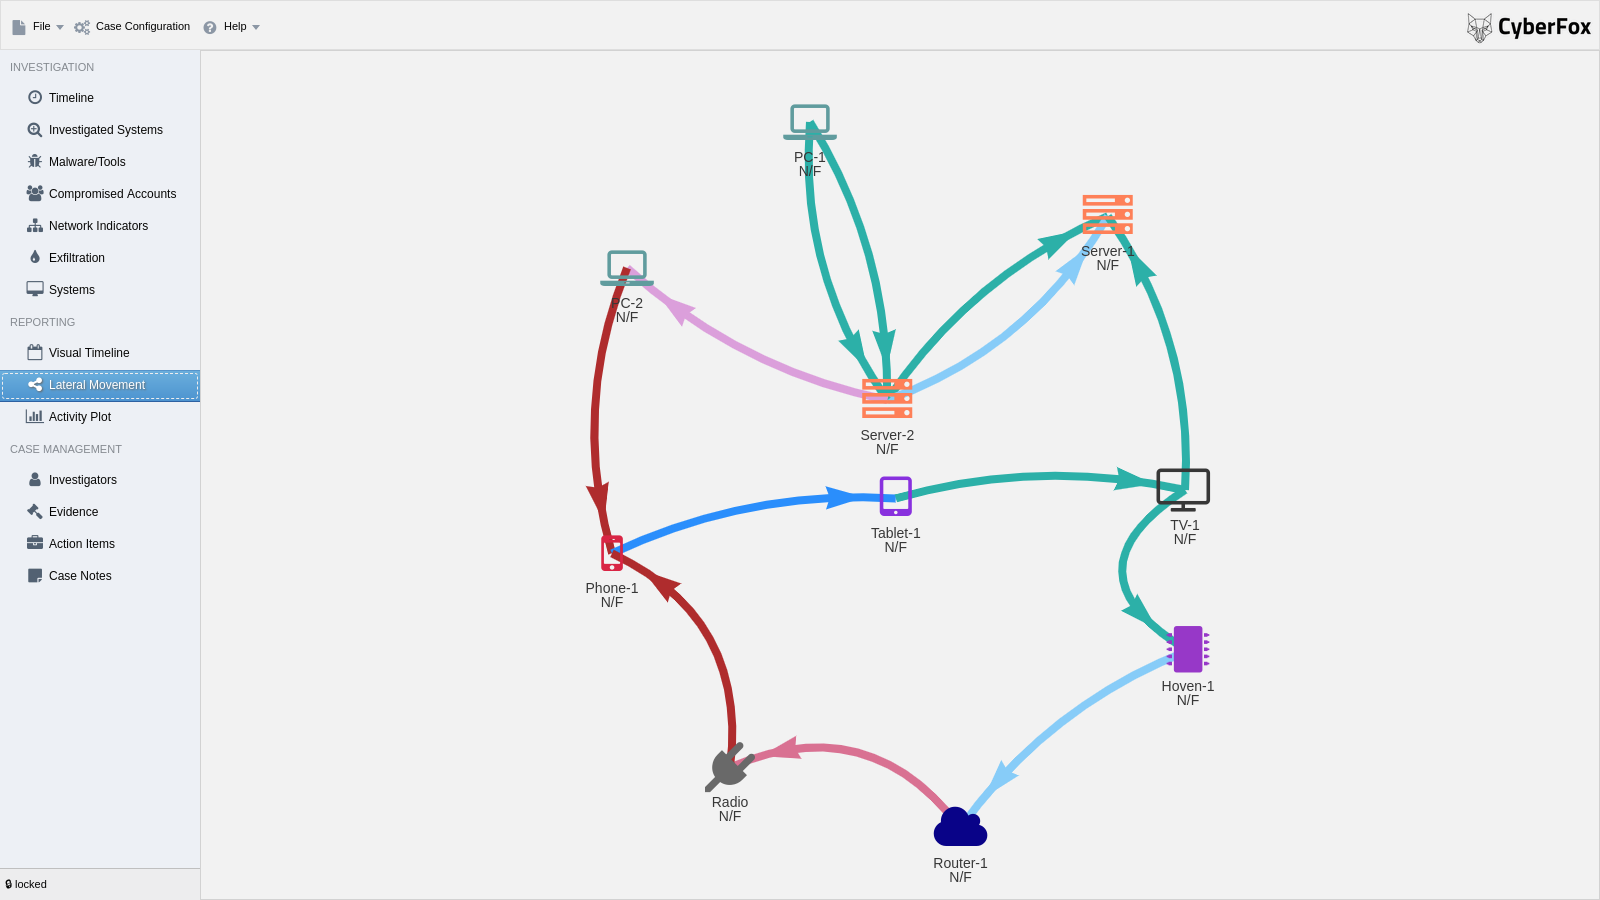
Aurora-Incident-Response preview

Aurora-Incident-Response

GitHubcyb3rfox/aurora-incident-response

Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
forensicsinformation-gatheringdigital-forensics+3
1.1k3 years ago
Kage-DFIR-toolkit preview

Kage-DFIR-toolkit

GitHubkarim852/kage-dfir-toolkit

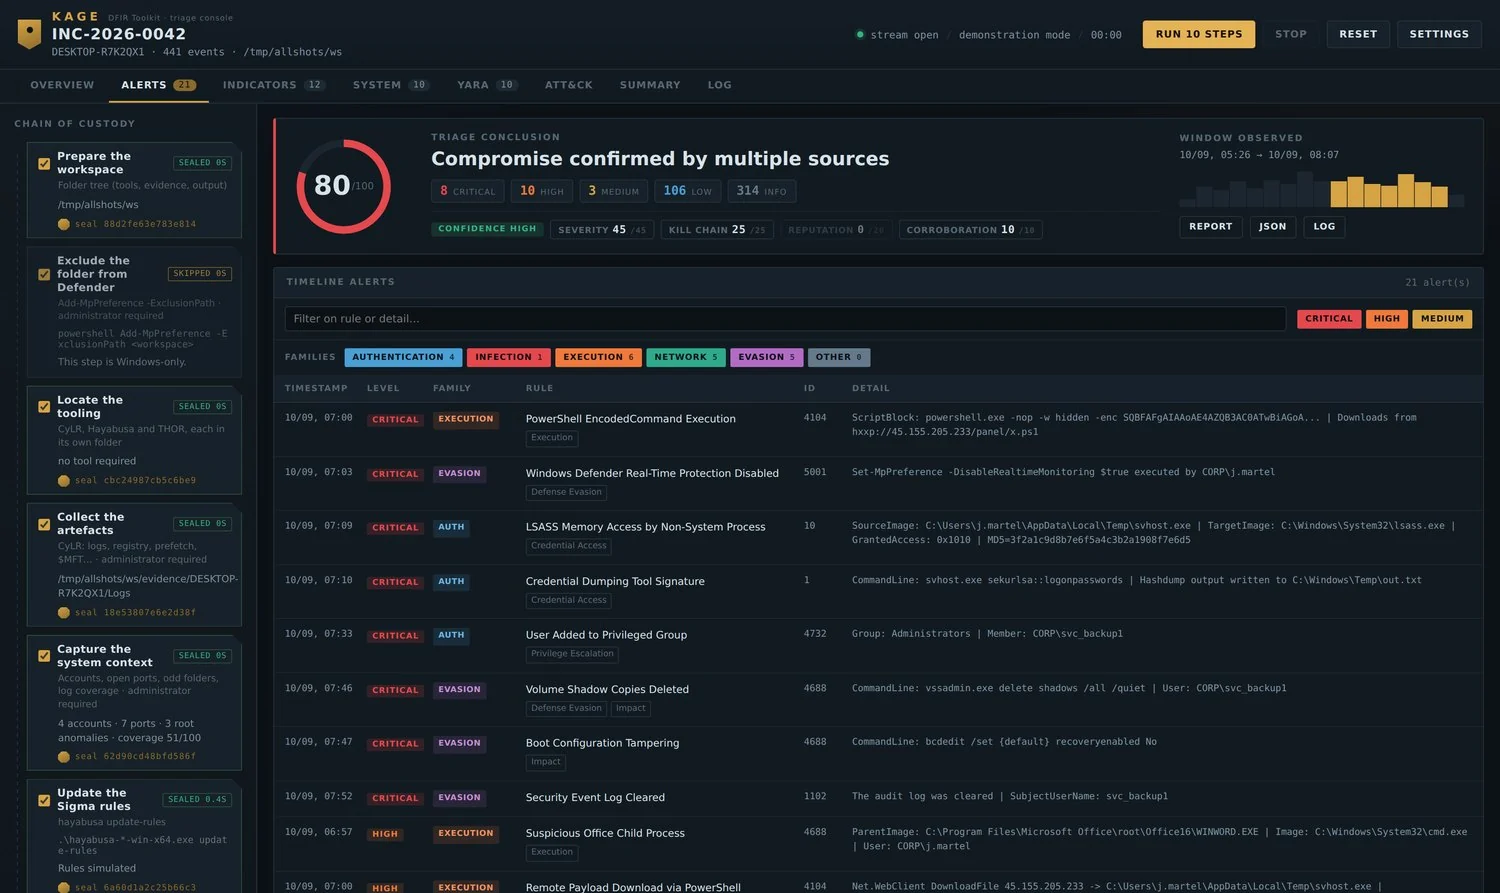
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
defensive-toolsioc-managementvulnerability-analysis+8
186 days ago
attackgen preview

attackgen

GitHubmrwadams/attackgen

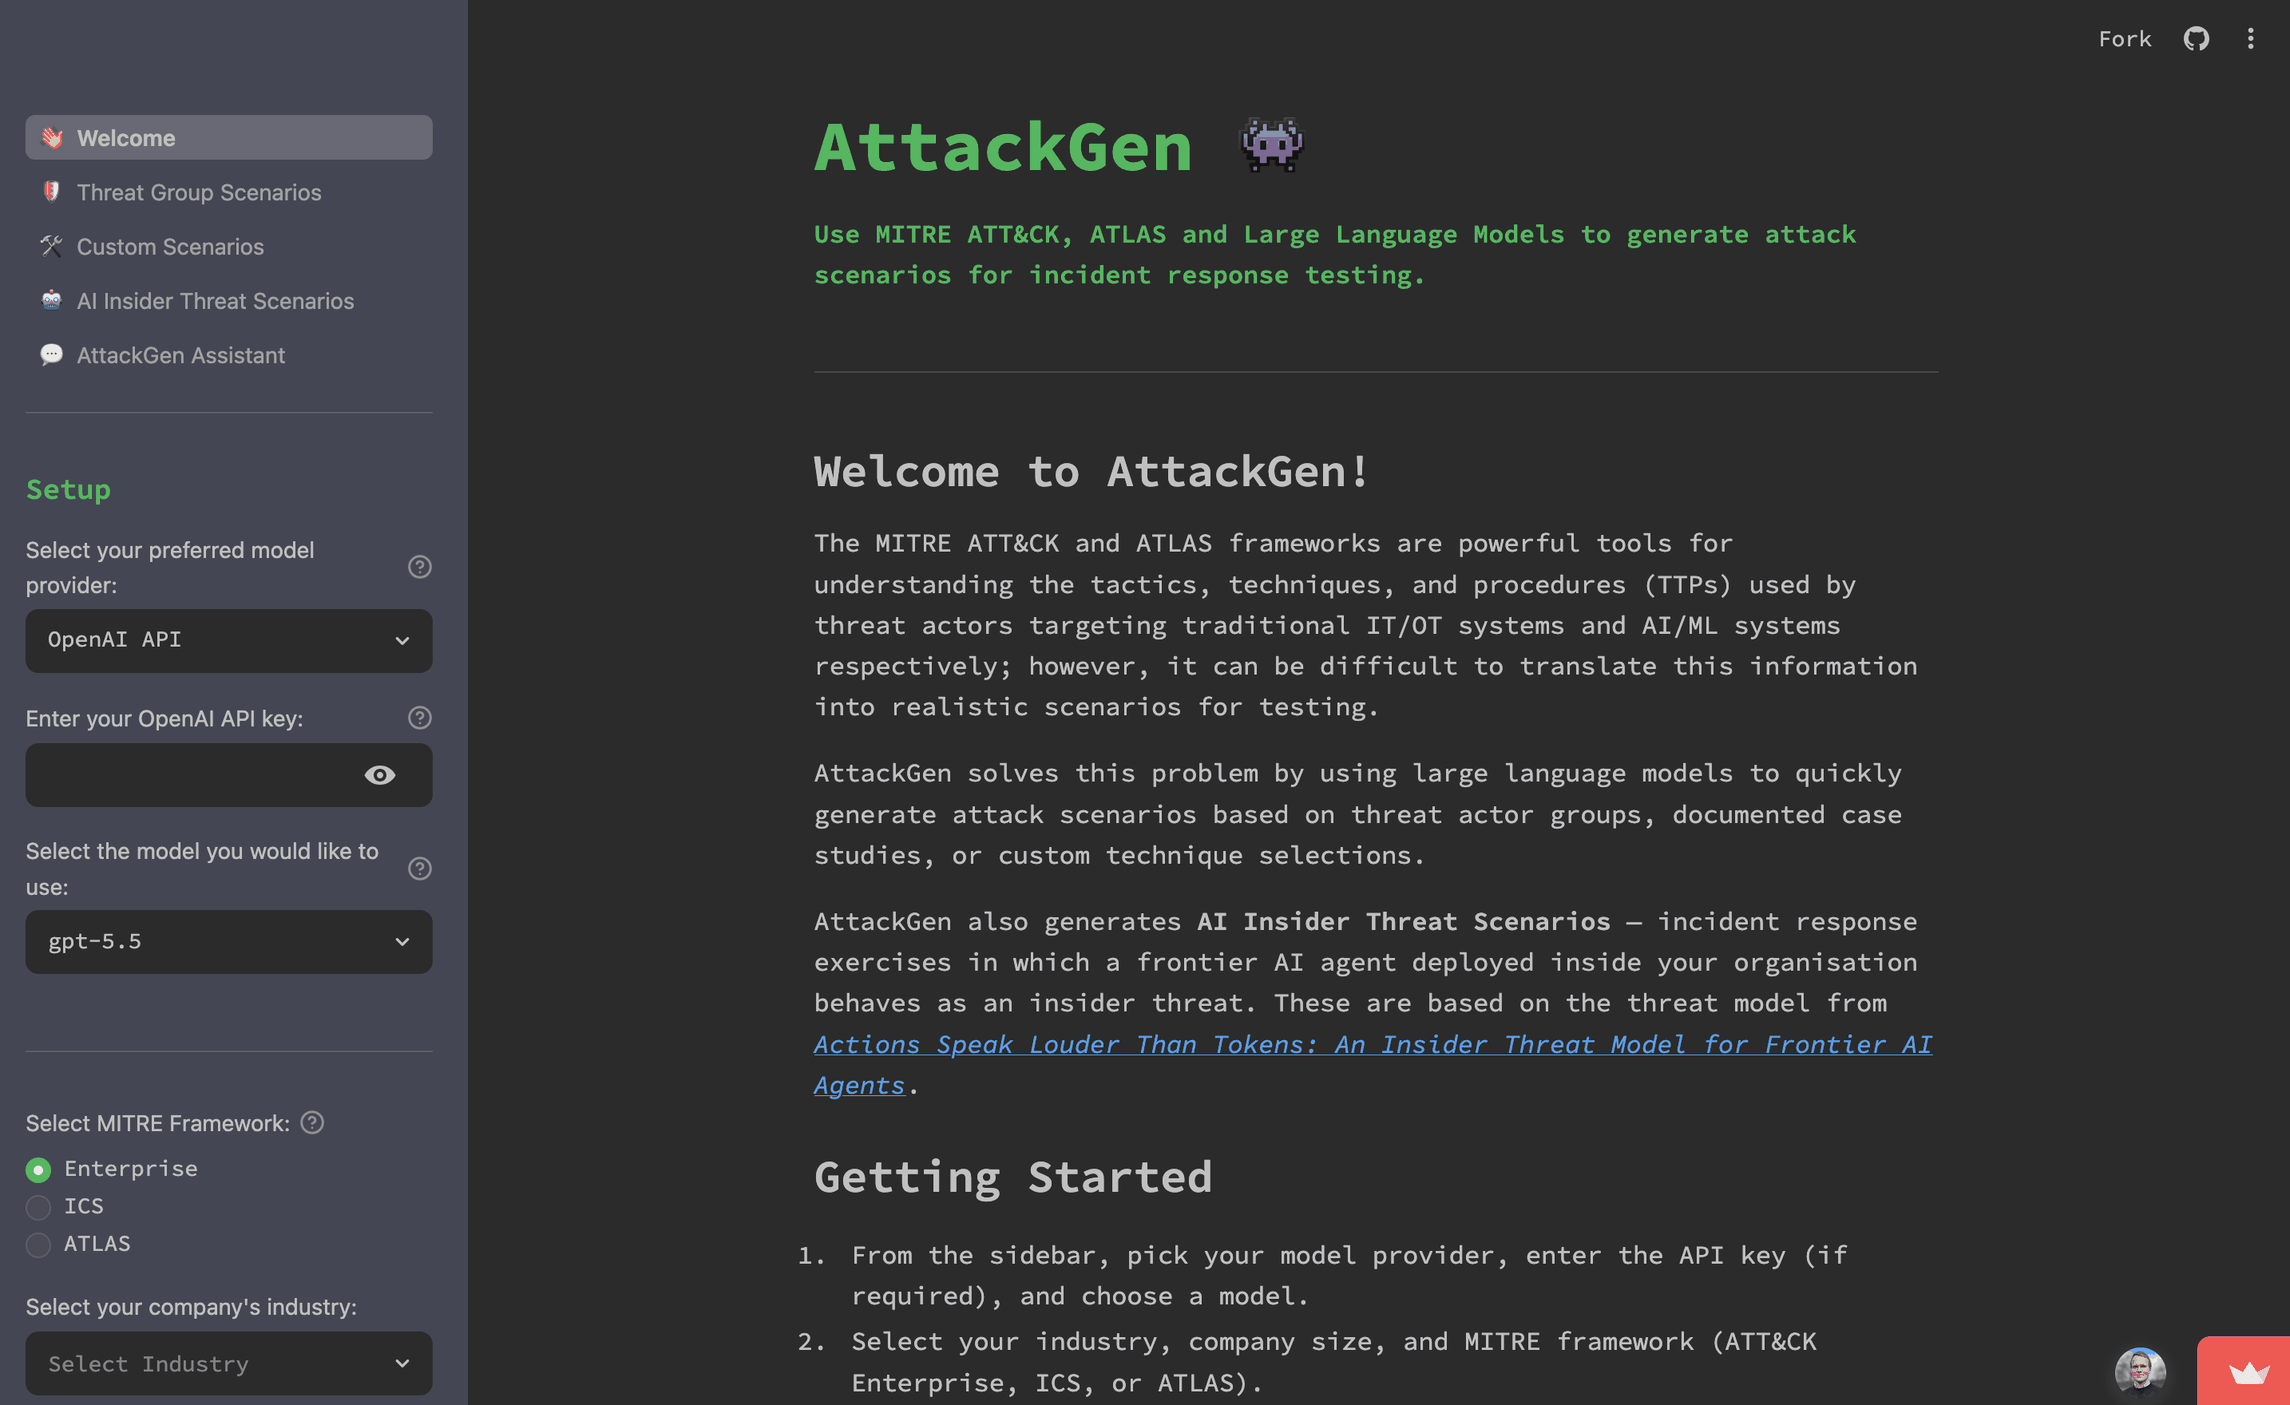
AttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…


ctfpenetration-testingthreat-intelligence+5
1.2k3 days ago
Previous1234…75Next