
 #1
 bats3c/ghost-in-the-logs
Kernel-level tool to disable Sysmon and Windows Event Logging via driver-based hook injection, enabling stealthy post-exploitation operations on…
 xm0kht4r/ven0m-ransomware
Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.
 reverseclabs/wepwnise
WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
 nccgroup/phantap
Phantom Tap (PhanTap) - an ‘invisible’ network tap aimed at red teams
 cryptolok/ghostinthenet
Ultimate Network Stealther that makes Linux a Ghost In The Net and protects from MITM/DOS/scan
 saadahla/shellcode-hide
This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)
 realgam3/pymultitor
PyMultitor - Python Multi Threaded Tor Proxy
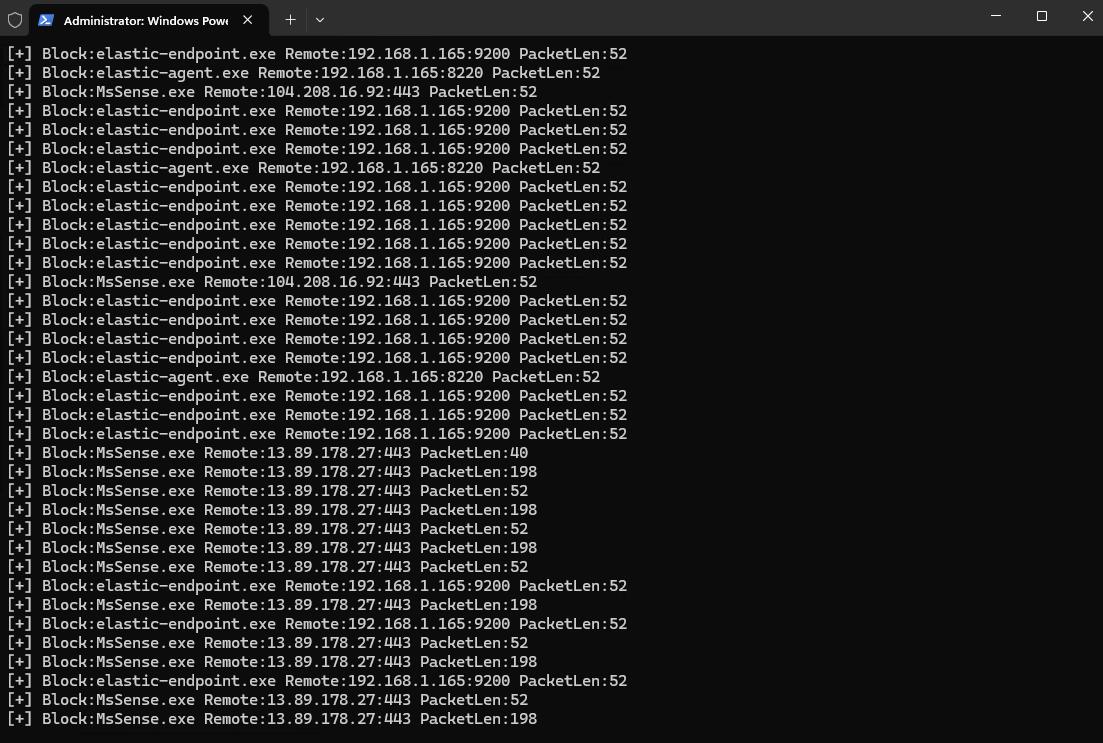 senzee1984/edrprison
Leverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
 mthbernardes/gtrs
GTRS - Google Translator Reverse Shell
 mharjac/bad_ducky
Rubber Ducky compatible clone based on CJMCU BadUSB HW.
 pushpenderindia/crypter
Python-based crypter that encrypts source code with AES-256 and Base64, evades VM detection via registry, process, and MAC checks, and executes…
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
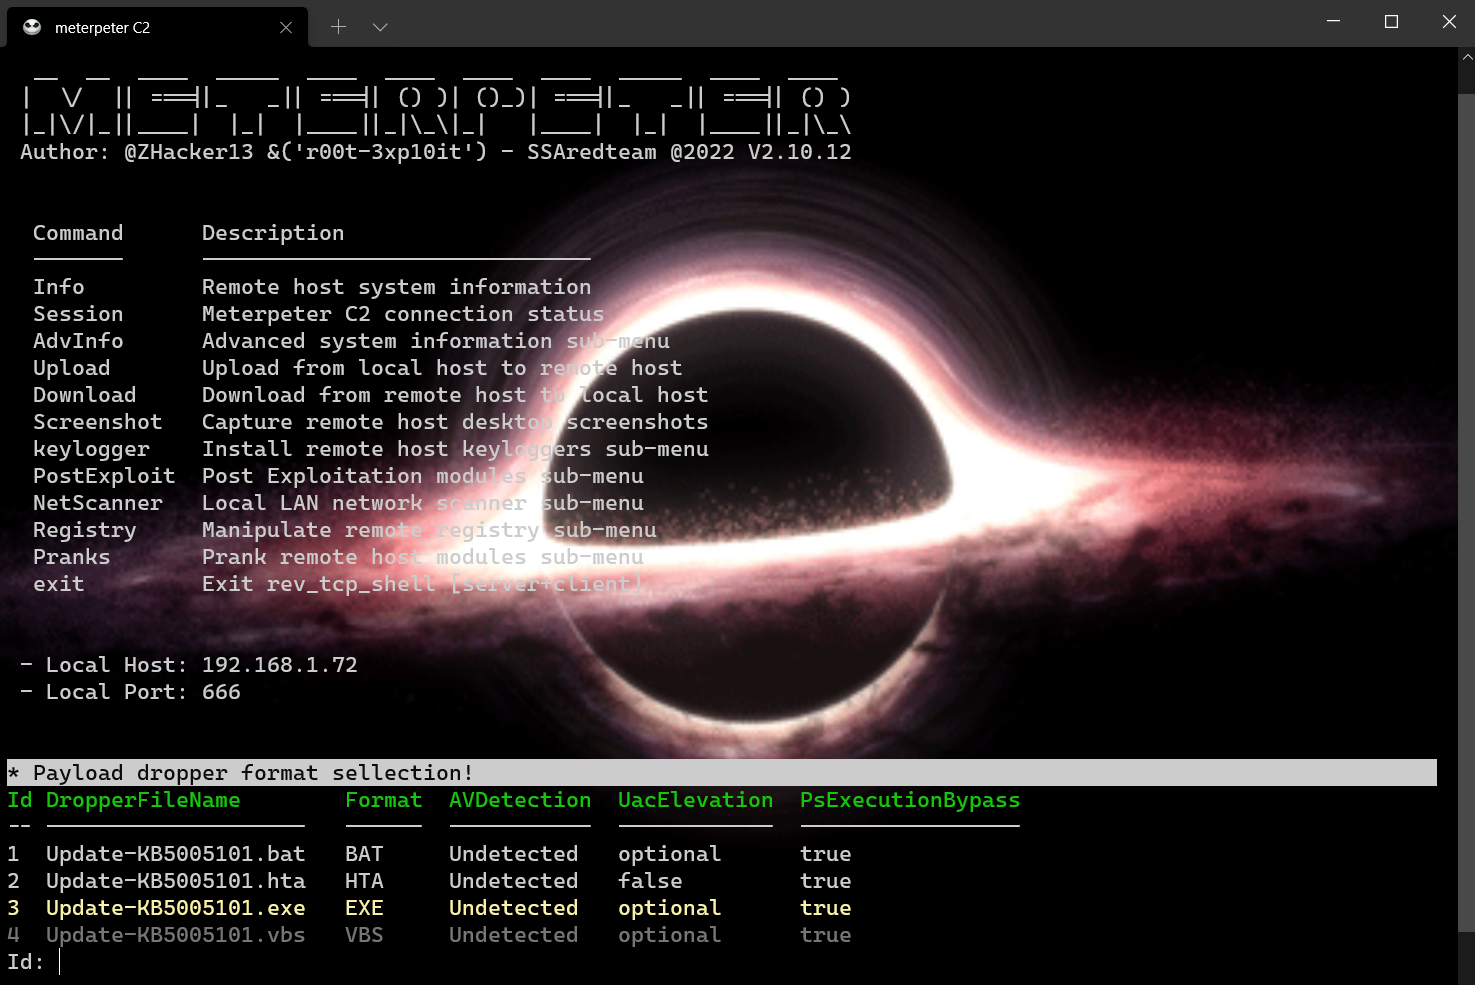 r00t-3xp10it/meterpeter
C2 Powershell Command & Control Framework with BuiltIn Commands
 3v4si0n/http-revshell
Powershell reverse shell using HTTP/S protocol with AMSI bypass and Proxy Aware
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code









