
 #1
Tools for bypassing Intrusion Detection and Prevention Systems (IDS/IPS) and network security controls.
Kitploit recommended
 zeronetworks/rpcfirewall
Windows RPC firewall that audits, detects, and blocks malicious remote procedure calls to prevent lateral movement, reconnaissance, and exploitation…
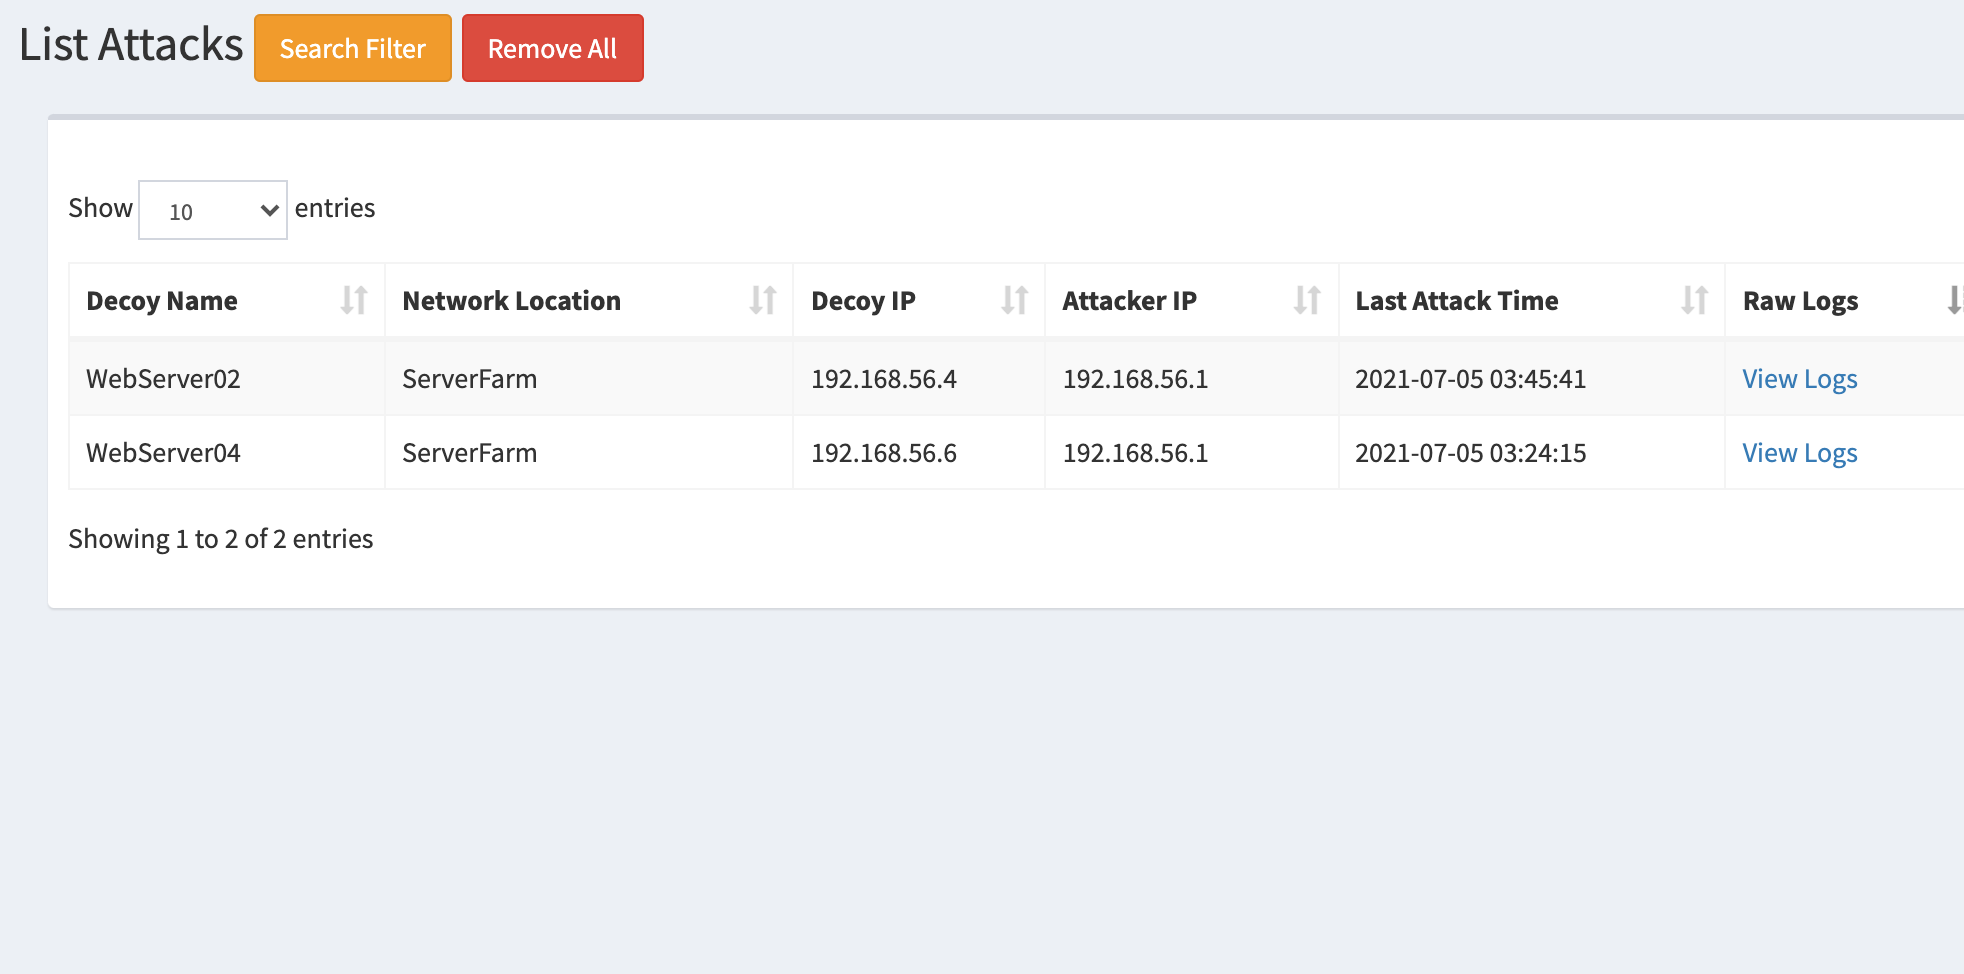 bhdresh/dejavu
DejaVU - Open Source Deception Framework
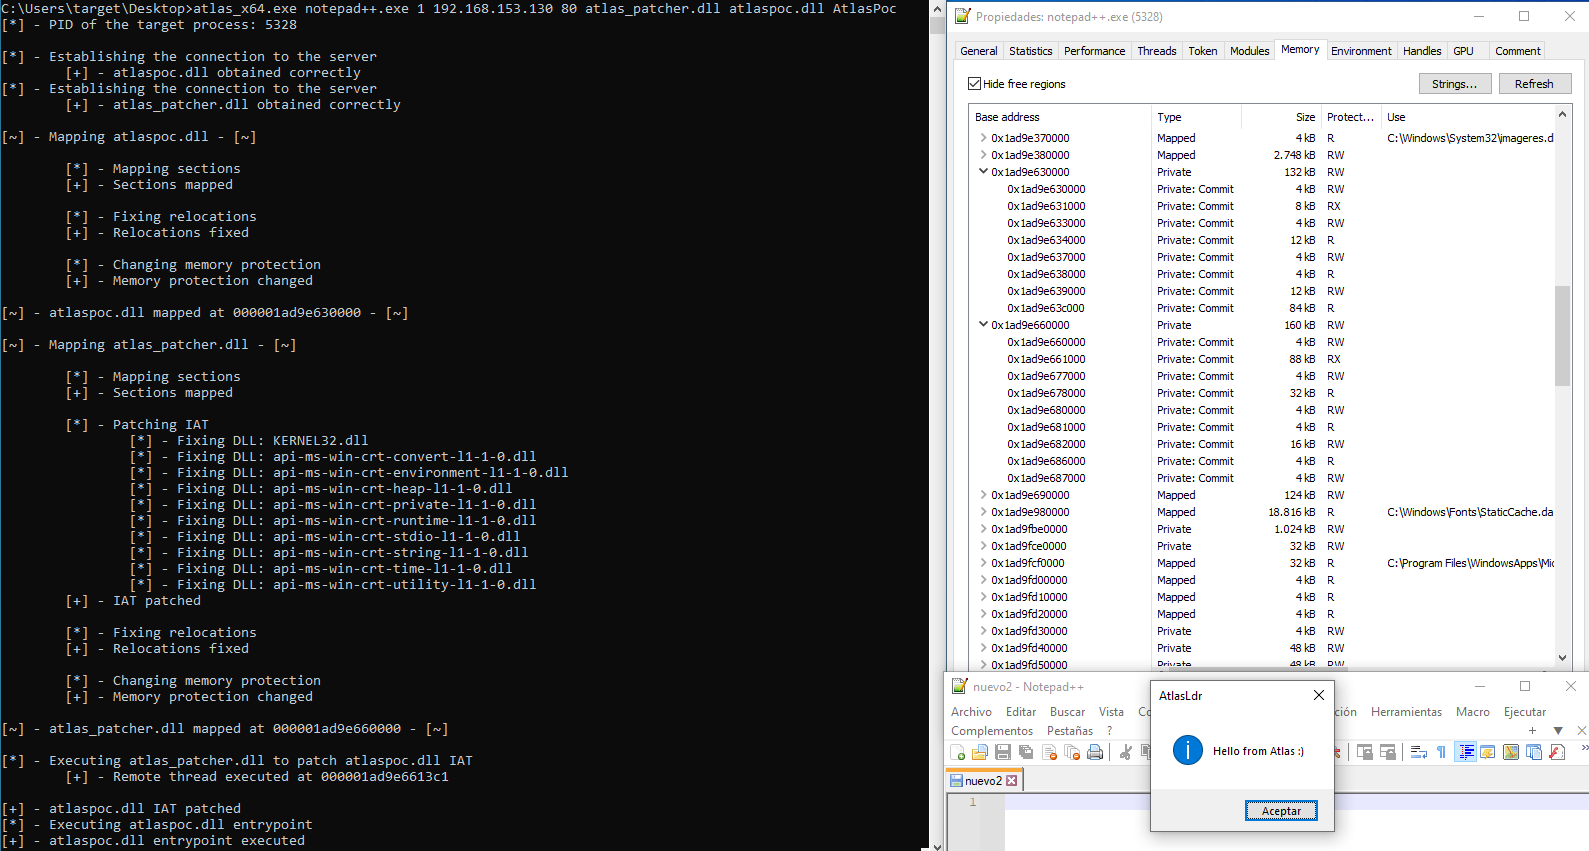 krypteria/atlasldr
Reflective x64 PE/DLL Loader implemented using Dynamic Indirect Syscalls
 syworks/wireless-ids
Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.
 an0nud4y/av-edr-lab-environment-setup
AV/EDR Lab environment setup references to help in Malware development
 telefonica/ibombshell
Tool to deploy a post-exploitation prompt at any time
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
 vxfemboy/ghostport
A high-performance port spoofing tool built in Rust. Confuse port scanners with dynamic service emulation across all ports. Features customizable…
 mrash/psad
psad: Intrusion Detection and Log Analysis with iptables
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 idov31/venom
Venom is a library that meant to perform evasive communication using stolen browser socket
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 d4rksystem/vboxcloak
A PowerShell script that attempts to help malware analysts hide their Windows VirtualBox Windows VM's from malware that may be trying to evade…
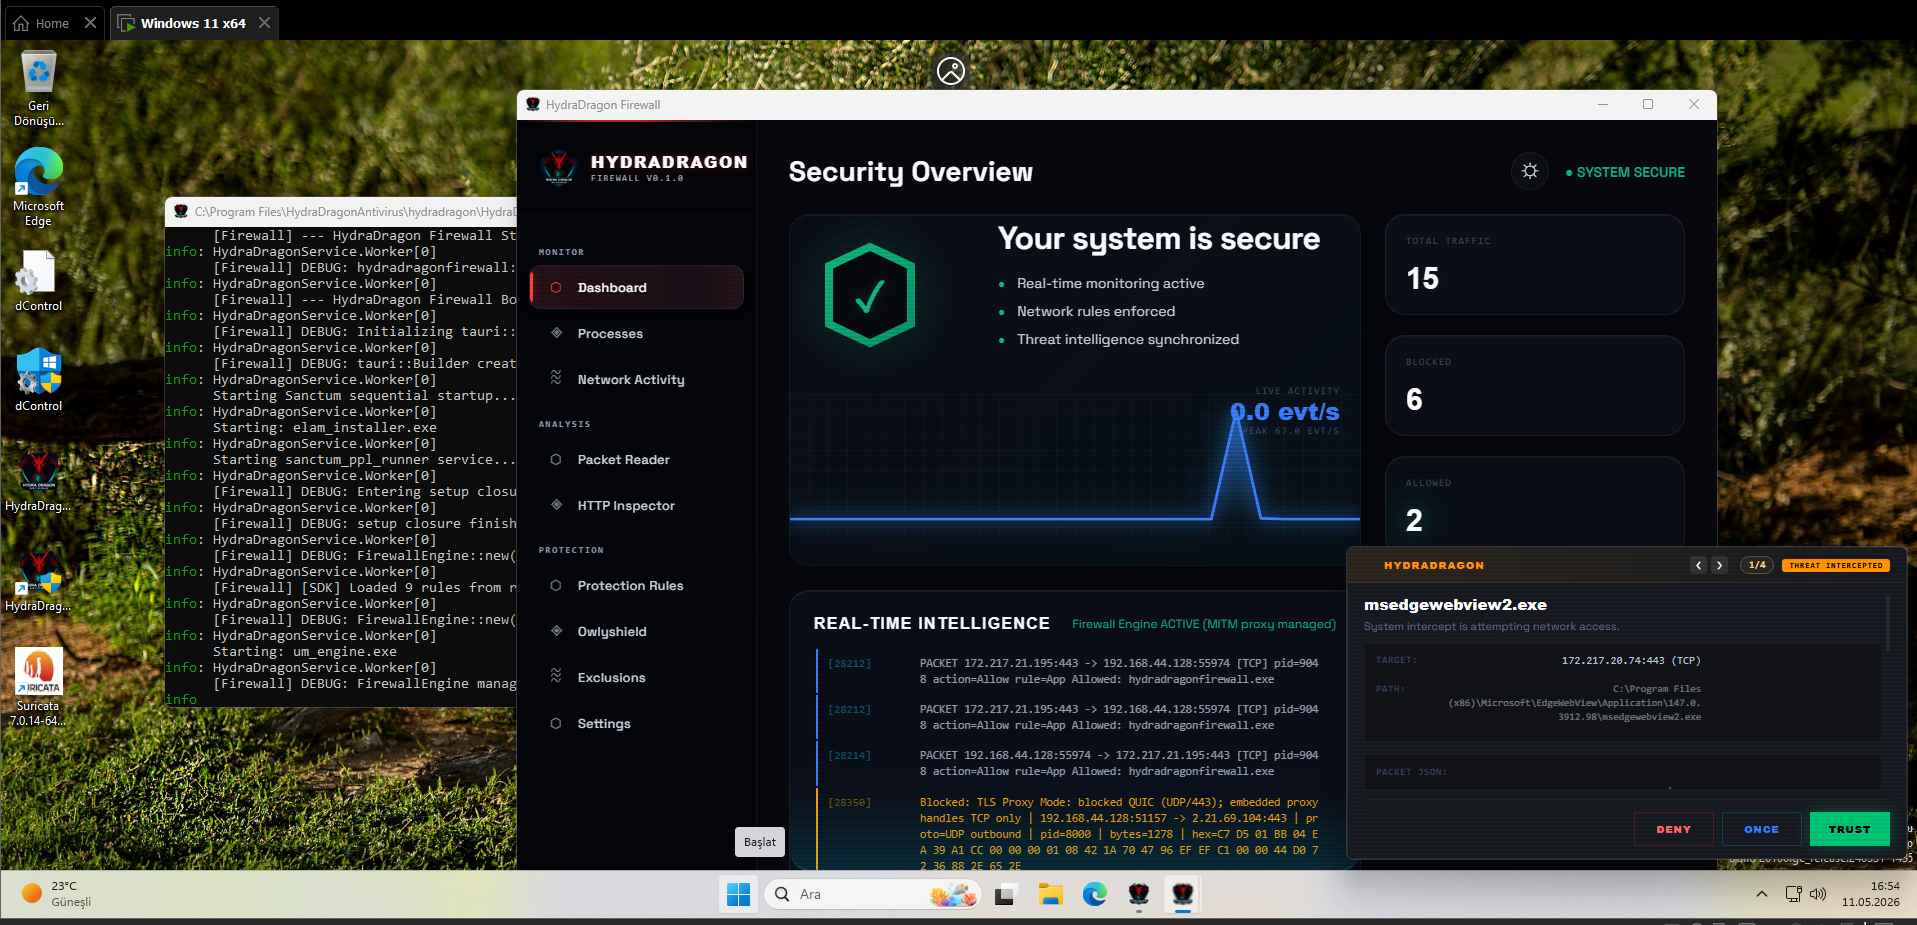 hydradragonantivirus/hydradragonantivirus
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…
 robertdavidgraham/isowall
This is a mini-firewall that completely isolates a target device from the local network.








