
 #1

 darknesschieftain/injection-vulnerability-in-paradox-security-systems-ipr512-cve-2023-24709-poc
In Paradox Security System IPR512 Web console login form page, attacker can input JavaScript string, such as "</script>" that will overwrite…

 smillier/hydralincan
Hydrabus Shield for LIN and CAN Buses
 seifallahhomrani1/cve-2023-0861-poc
Analyzing and Reproducing the Command Injection Vulnerability (CVE-2023-0861) in NetModule Routers
 wack0/batondrop_armv7
An implementation of baton drop (CVE-2022-21894) for armv7 (MSM8960)
 joelgmsec/thunderstorm
Modular framework to exploit UPS devices
 yilin1203/cve-2022-40881
Proof-of-concept exploit for CVE-2022-40881 targeting SolarView Compact devices. Uses fofa query for reconnaissance and payload delivery for…
 ethancunt/cve-2022-45600
Proof-of-concept exploit for command injection vulnerability in Aztech WMB250AC routers, enabling authenticated privilege escalation to root shell…
 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
 swzhouu/cve-2022-48311
HP Deskjet 2540 series printer Firmware Version CEP1FN1418BR and Product Model Number A9U23B HTTP configuration page Cross Site Scripting (XSS)…
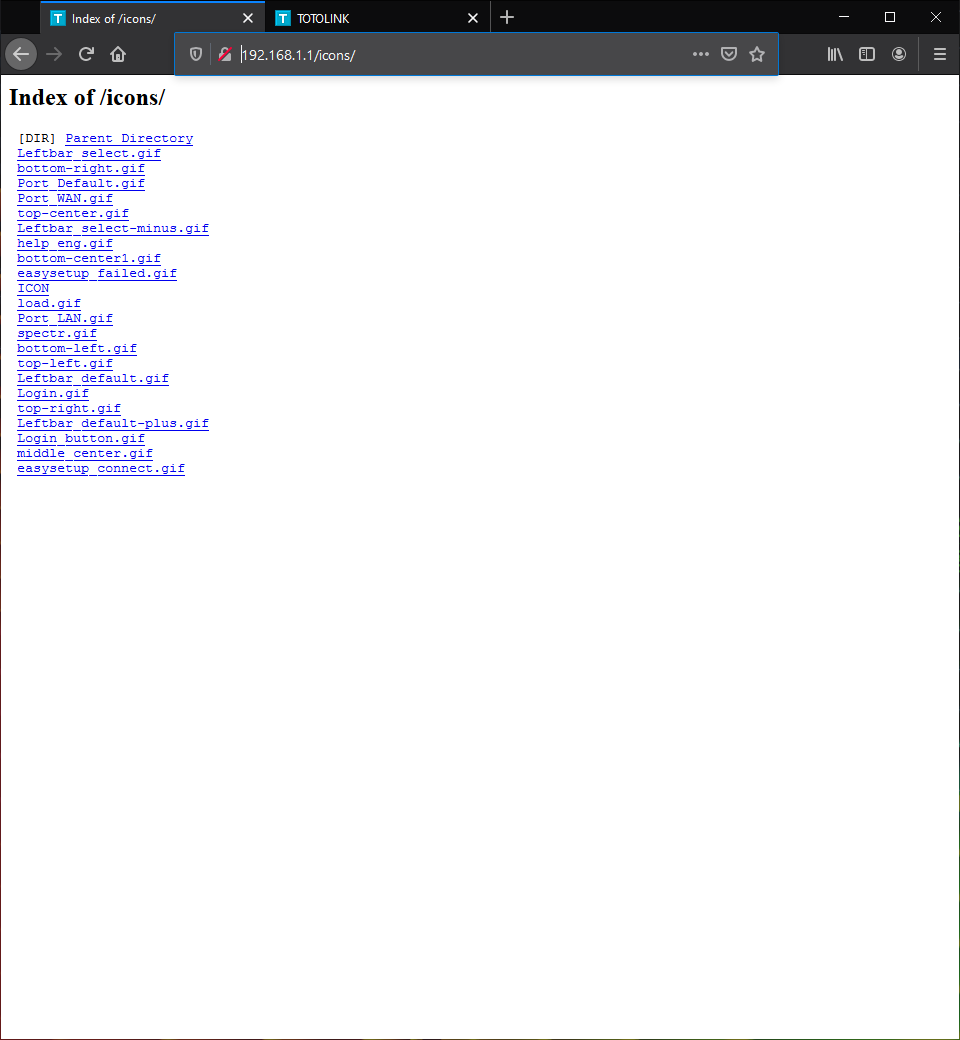 swzhouu/cve-2020-27368
TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability
 risinek/esp32-wifi-penetration-tool
Exploring possibilities of ESP32 platform to attack on nearby Wi-Fi networks.
 dumitory-dev/cve-2020-35391-poc
Tenda N300 Authentication Bypass via Malformed HTTP Request Header
 rdomanski/exploits_and_advisories
Repository that tracks public exploits, vulnerabilities and advisories that I [co-]discovered or [co-]authored.
 leoservalli/privilege-escalation-askey
Privilege escalation vulnerability on ASKEY routers
 otsmr/internet-of-vulnerable-things
The results of my small term paper on the topic of the Internet of Vulnerable Things and the exploit for CVE-2022-48194.
 trinadh465/linux-4.19.72_cve-2022-45934
Linux kernel source tree modified to demonstrate or patch CVE-2022-45934, providing a basis for vulnerability analysis and exploitation research.









