
 #1
Tools for assessing the security of physical hardware, embedded systems, and IoT devices.
Kitploit recommended

 trou/cpu_rec_rs
Determine which CPU architecture is used in a binary file.
 usbarmory/gotee-example
GoTEE - example application
 inradii/iottack
Framework for testing common IoT protocols and IoT implementations
 usbarmory/gotee
Go Trusted Execution Environment (TEE)
 we5ter/scanners-box
The Ultimate Open-Source Security Arsenal for Hackers, Enterprises, and AI Agents——面向极客、企业与 AI 智能体的全域开源网络安全工具矩阵
 unsignedchad/cve-2026-21155-sve-2026-3546
Technical writeup and PoC for CVE-2026-21155 (SVE-2026-3546): fail-open signature checks and an unbounded boot-logo JPEG decode in Samsung Exynos…
 elttam/publications
Offensive security research hub aggregating original vulnerability advisories, CVE proof-of-concept exploits, conference talks, and internal tooling…
 ironfox-oss/ironfox
Hardened Android web browser forked from Mull/Firefox with privacy-focused patches, anti-fingerprinting, telemetry removal, and secure defaults for…
 affolter-engineering/mqattack
Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
 mattifinder/rpmc_attacks
Research code and hardware for RPMC attacks: voltage glitching, SPI interposer firmware, and NV-state rollback to brute-force Windows Hello and…
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 zephyrproject-rtos/zephyr
Primary Git Repository for the Zephyr Project. Zephyr is a new generation, scalable, optimized, secure RTOS for multiple hardware architectures.
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 dpt/chasehq
Chase H.Q. for ZX Spectrum — reverse-engineered and reconstructed in portable C
 vulncheck-oss/initial-access-community
Go-based exploits for unauthenticated network vulnerabilities in routers, VPNs, appliances, and IoT, bundled with PCAPs, Suricata/Snort/YARA/Sigma…
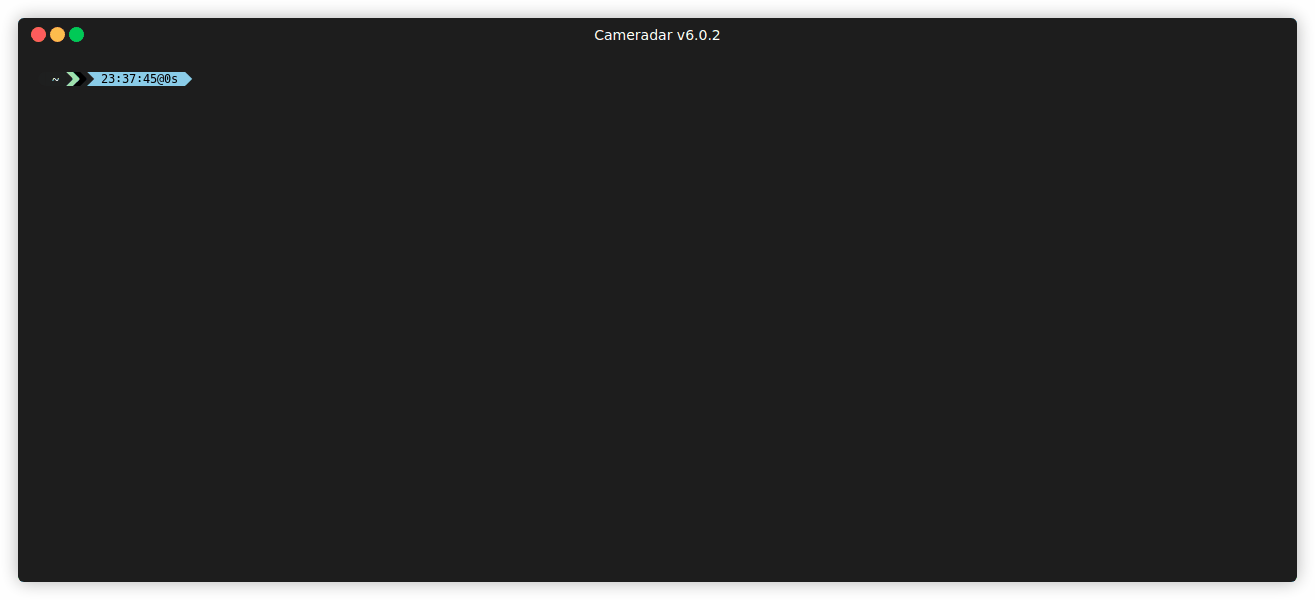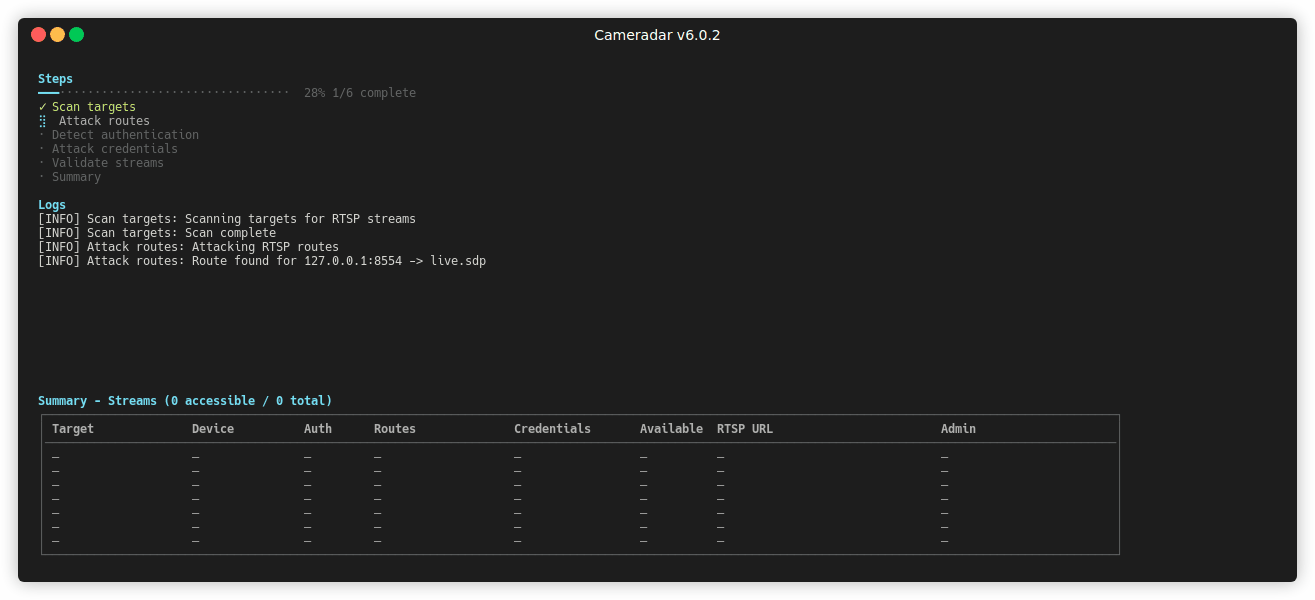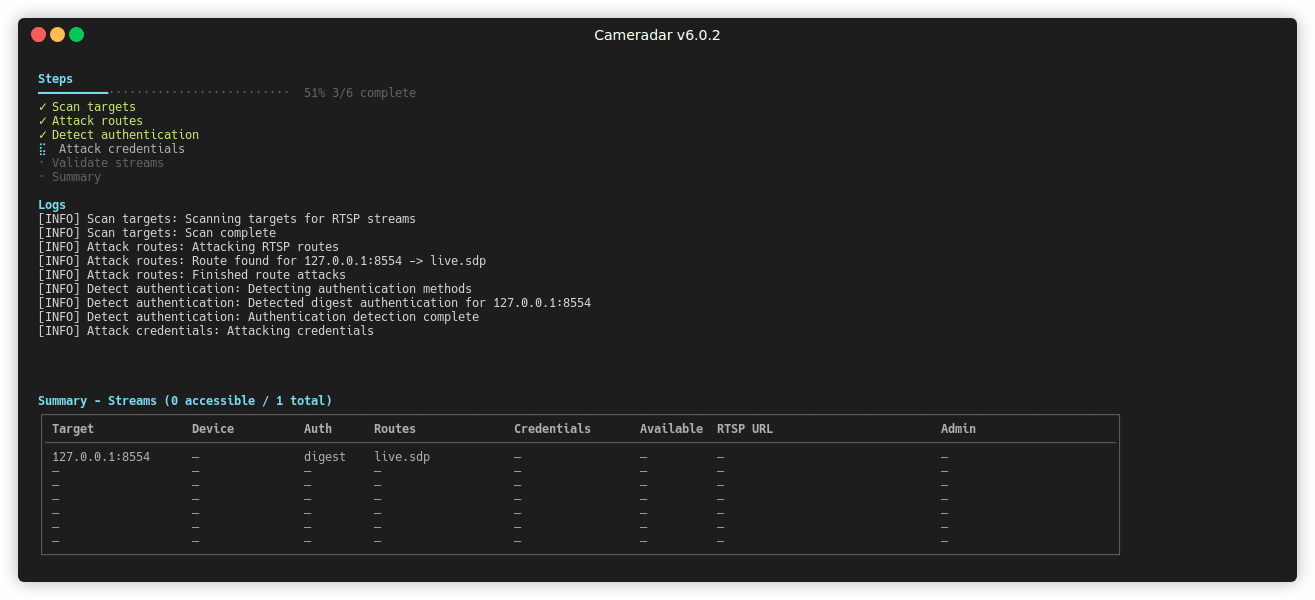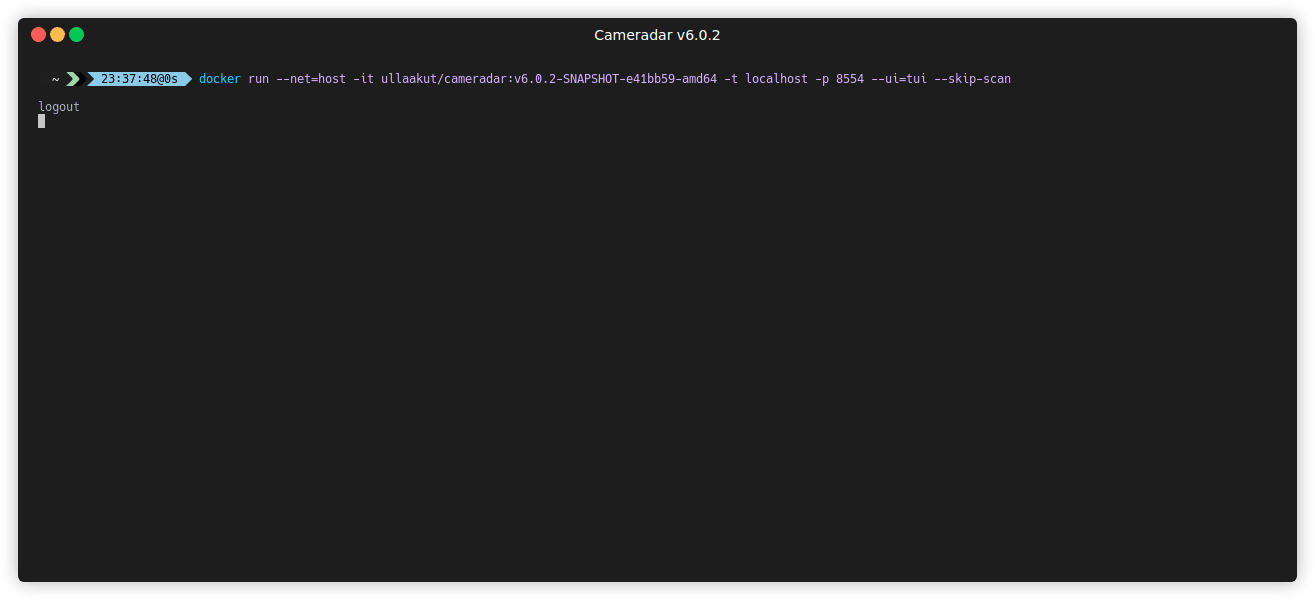 ullaakut/cameradar
Cameradar hacks its way into RTSP videosurveillance cameras
 aomsin2526/xperia_5_bl_unlocker_poc
My take on unlocking Xperia 5 SO-01M for p42(SO-01M_55.0.D.7.203_1319-8175_R9A) bootloader using CVE-2021-1931
 dorskfr/tapodate
Sets up a local Tapo C200 using CVE-2021-4045








