
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Fuzzing — Page 46 | Kitploit
Categories

Fuzzing

Fuzz testing, mutation-based, generation-based, and coverage-guided fuzzing tools.

Kitploit recommended
Top tools

10 selected
AFLplusplus preview#1

AFLplusplus

GitHubaflplusplus/aflplusplus
6.7k4 days ago
oss-fuzz preview#2

oss-fuzz

GitHubgoogle/oss-fuzz
12.5k14h 51m ago
honggfuzz preview#3

honggfuzz

GitHubgoogle/honggfuzz
3.4k27 days ago
clusterfuzz preview#5

clusterfuzz

GitHubgoogle/clusterfuzz
5.6k16h 31m ago
domato preview#7

domato

GitHubgoogleprojectzero/domato
1.8k1 year ago
cargo-fuzz preview#9

cargo-fuzz

GitHubrust-fuzz/cargo-fuzz
1.9k3 months ago
LibAFL preview#10

LibAFL

GitHubaflplusplus/libafl
2.6k3 days ago
boofuzz preview#11

boofuzz

GitHubjtpereyda/boofuzz
2.4k1 month ago
Angora preview#16

Angora

GitHubangorafuzzer/angora
9574 years ago
Awesome-Fuzzing preview#17

Awesome-Fuzzing

GitHubsecfigo/awesome-fuzzing
5.9k3 years ago
NewestRelevanceMost popularRecently updated
1009 results
CVE-2026-20404-MediaTek-modem-remote-DoS-rogue-base-station-scenario- preview

CVE-2026-20404-MediaTek-modem-remote-DoS-rogue-base-station-scenario-

GitHubgeorge0papasotiriou/cve-2026-20404-mediatek-modem-remote-dos-rogue-base-station-scenario-

A MediaTek modem input validation issue can cause a system crash (remote DoS) when a UE connects to a rogue base station controlled by an attacker…
vulnerability-analysisexploitationfuzzing+2
1
8 months ago
CVE-2016-3627 preview

CVE-2016-3627

GitHuboneton429/cve-2016-3627

PoC of CVE-2016-3627
static-analysisvulnerability-analysisexploitation+2
11 year ago
cve-2023-21987-poc preview

cve-2023-21987-poc

GitHubchunzhennn/cve-2023-21987-poc

Proof-of-concept exploit for Oracle VirtualBox VGA out-of-bounds read vulnerability, demonstrating address leaking from VirtualBox components on…
memory-forensicsvulnerability-analysisexploitation+3
12 years ago
CVE-2024-22641 preview

CVE-2024-22641

GitHubzunak/cve-2024-22641

Proof-of-concept for CVE-2024-22641: ReDoS vulnerability in TCPDF <=6.7.4 triggered by crafted SVG files, demonstrating regex backtrack limit…
vulnerability-analysisexploitationweb-security+3
12 years ago
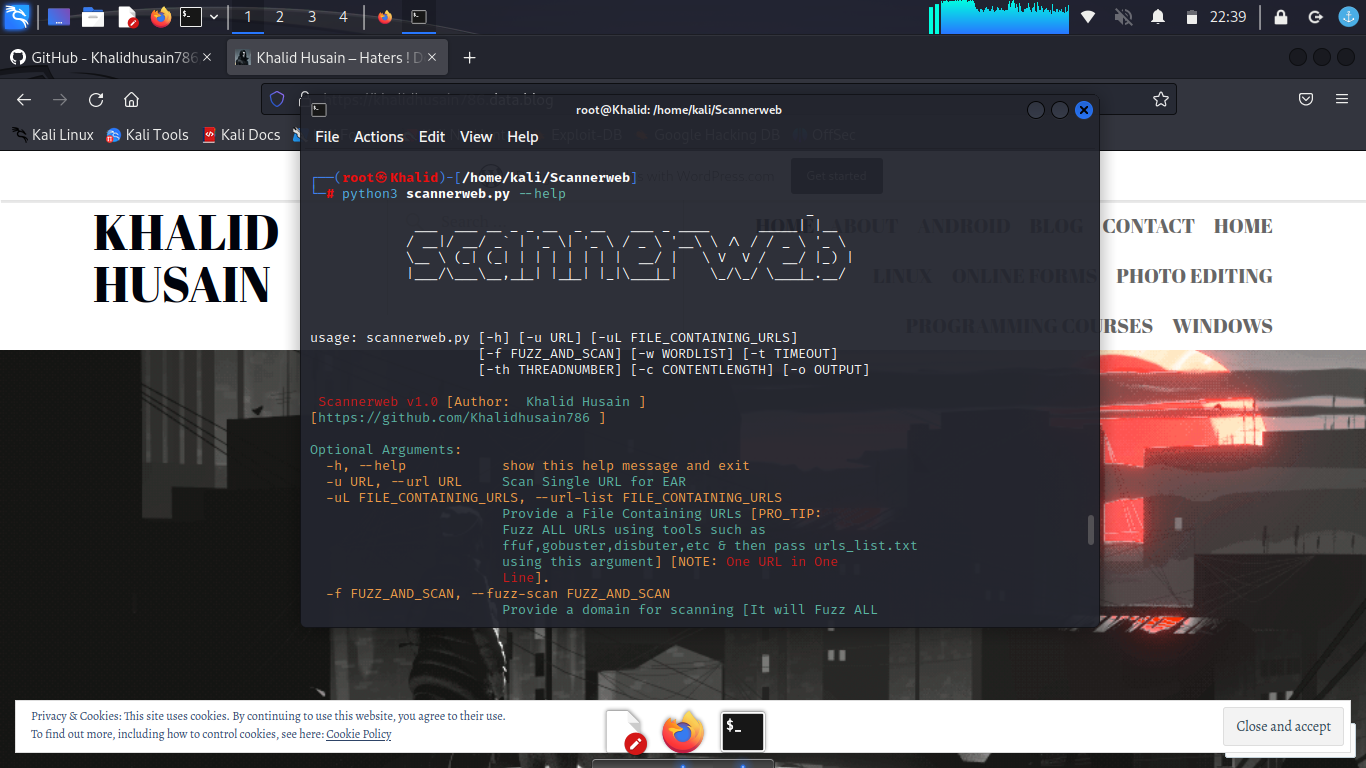
Scannerweb preview

Scannerweb

GitHubkhalidhusain786/scannerweb

Python3 vulnerability scanner that fuzzes all URLs of a target website and scans them for web vulnerabilities, with optional GoBuster integration for…
vulnerability-scannersweb-vulnerability-scannersweb-security+1
19 months ago
LibPNG_OSS-Fuzz preview

LibPNG_OSS-Fuzz

GitHubenessar/libpng_oss-fuzz

Security research project on fuzzing libpng with OSS-Fuzz. Includes seed corpus analysis, custom read/write fuzzers, and a proof-of-concept exploit…
vulnerability-analysiscode-analysisexploitation+3
10 years ago
ClaimJumper preview

ClaimJumper

GitHubfevra-dev/claimjumper

Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
password-crackingvulnerability-scannersexploitation+6
19 months ago
CTF-Web-Exploitation preview

CTF-Web-Exploitation

GitHubarnavps/ctf-web-exploitation

A comprehensive collection of 12 containerized web exploitation challenges covering CVE-2023-25690, WebAuthn bypasses, HTTP/3 smuggling, and advanced…
reconnaissancecontainer-securityvulnerability-analysis+8
16 months ago
tmux-fuzzing preview

tmux-fuzzing

GitHublucadibello/tmux-fuzzing

Enhanced fuzzing for tmux using OSS-Fuzz. Includes custom `cmd-fuzzer` and `argument-fuzzer` harnesses for improved code coverage and a PoC for…
vulnerability-analysiscode-analysisfuzzing+3
11 year ago
log4j-scanner preview

log4j-scanner

GitHubmanishkanyal/log4j-scanner

A Log4j vulnerability scanner is used to identify the CVE-2021-44228 and CVE_2021_45046
vulnerability-scannersexploitationwaf-bypass+3
14 years ago
CVE-2026-26399-Disclosure preview

CVE-2026-26399-Disclosure

GitHubacen28/cve-2026-26399-disclosure

Disclosure of a stack-based use-after-return vulnerability in Arduino_Core_STM32, detailing technical root cause, affected versions, and fix, with…
embedded-systems-securityvulnerability-analysisfuzzing+1
16 months ago
CVE-2025-5688-FreeRTOS-Plus-TCP-Out-of-Bounds-Write preview

CVE-2025-5688-FreeRTOS-Plus-TCP-Out-of-Bounds-Write

GitHubmbanyamer/cve-2025-5688-freertos-plus-tcp-out-of-bounds-write

PoC exploit for CVE-2025-5688: remote out-of-bounds write in FreeRTOS-Plus-TCP via crafted LLMNR/mDNS queries, causing crash or potential RCE on…
embedded-systems-securityiot-securityvulnerability-analysis+6
7 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubpopclom/cve-2025-5548

Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
exploit-frameworksvulnerability-analysisreverse-engineering+8
7 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubdiego57709/cve-2025-5548

Structured lab for controlled exploitation of CVE-2025-5548 (FreeFloat FTP Server). Includes environment setup, fuzzing, EIP control, badchars…
vulnerability-analysisexploitationreverse-engineering+8
7 months ago
reproducer-poc-CVE-2022-0847 preview

reproducer-poc-CVE-2022-0847

GitHubstfnw/reproducer-poc-cve-2022-0847

Very rough PoC for detecting/reproducing CVE-2022-0847 (dirty pipe) through random generation of syscalls and differential fuzzing against a model.
dynamic-analysis-sandboxingvulnerability-analysisexploitation+3
8 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubjgs-developer/cve-2025-5548

Stack-based buffer overflow exploit for FreeFloat FTP Server, demonstrating reverse engineering, EIP control, and shellcode execution for educational…
vulnerability-analysisexploitationreverse-engineering+5
7 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubalberto-galindo/cve-2025-5548

Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
static-analysisvulnerability-analysisexploitation+8
7 months ago
CVE-2026-29628 preview

CVE-2026-29628

GitHubkiyochii/cve-2026-29628

Proof-of-concept for CVE-2026-29628, a stack-based buffer overflow in tinyobjloader's experimental parser, with ASan/UBSan reproduction and fix…


vulnerability-analysiscode-analysisexploitation+2
6 months ago
Previous1…454647…57Next







