
 #1

 thomaspoppelgaard/netscaler-ctx697096-checker
Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…
 lsecqt/sessionview
A portable C# utility for enumerating local and remote windows sessions
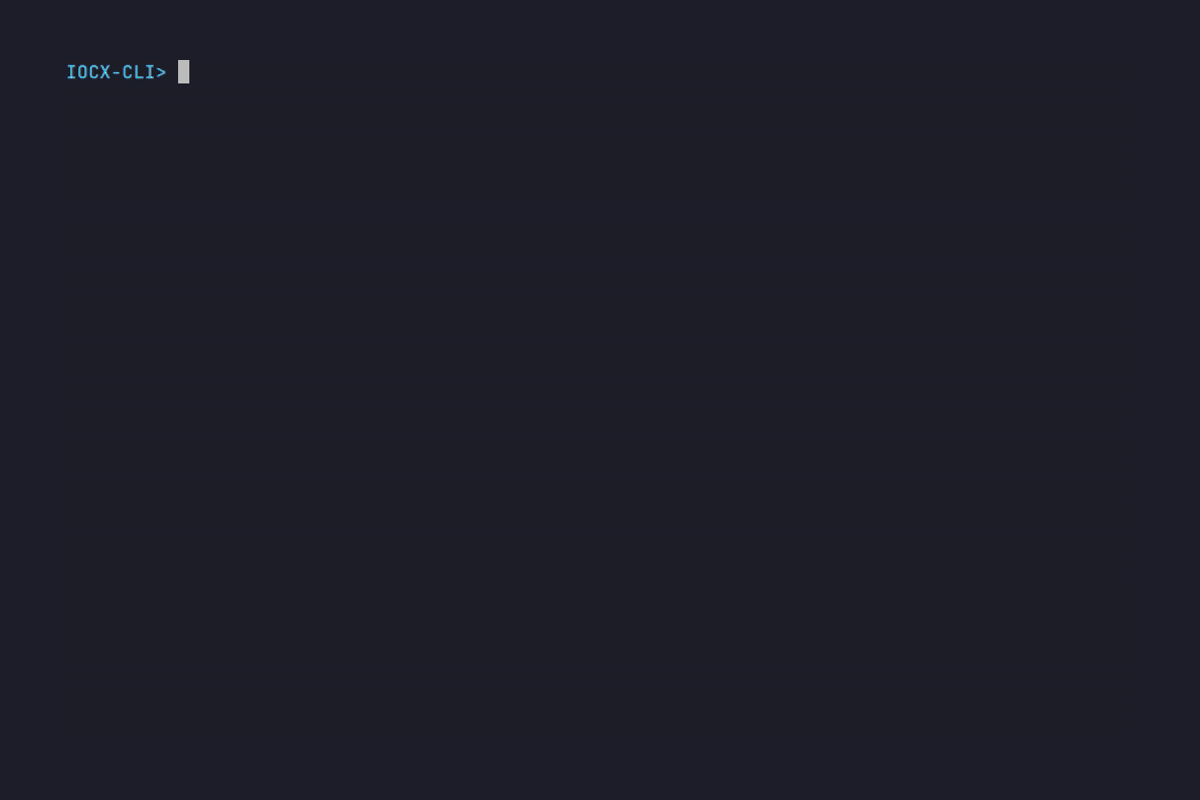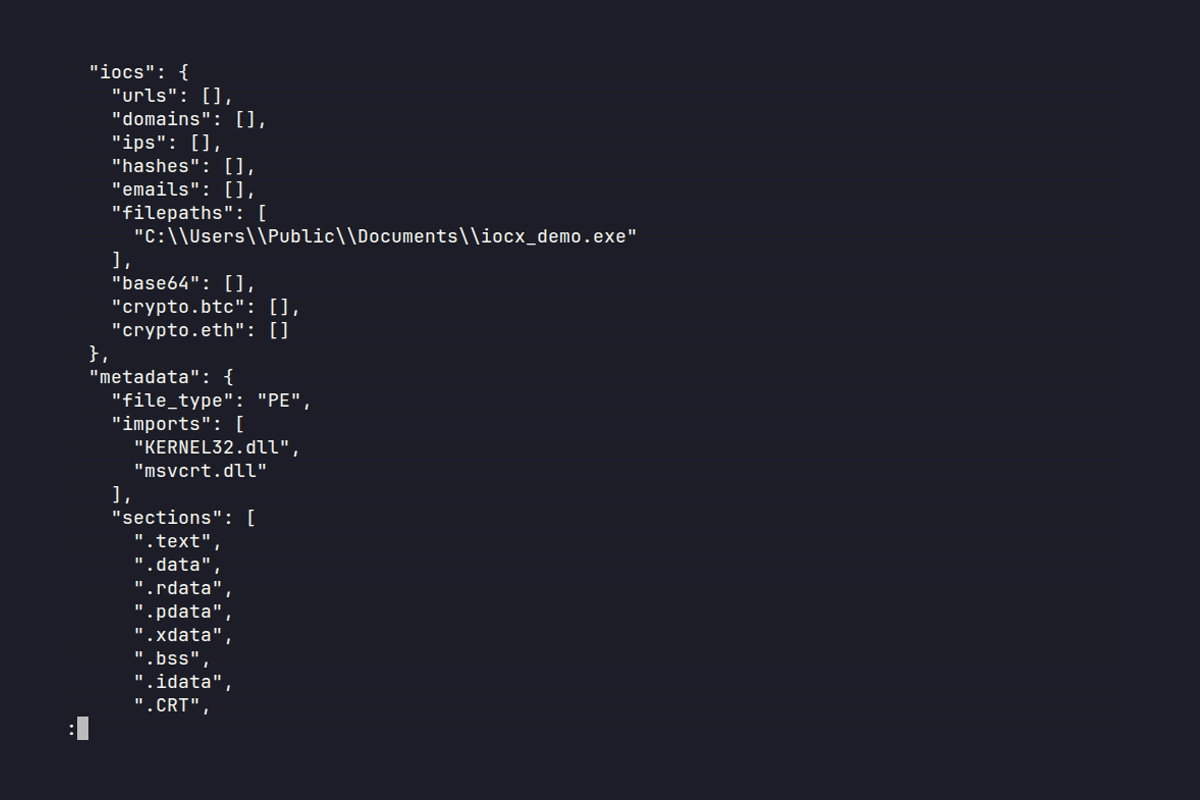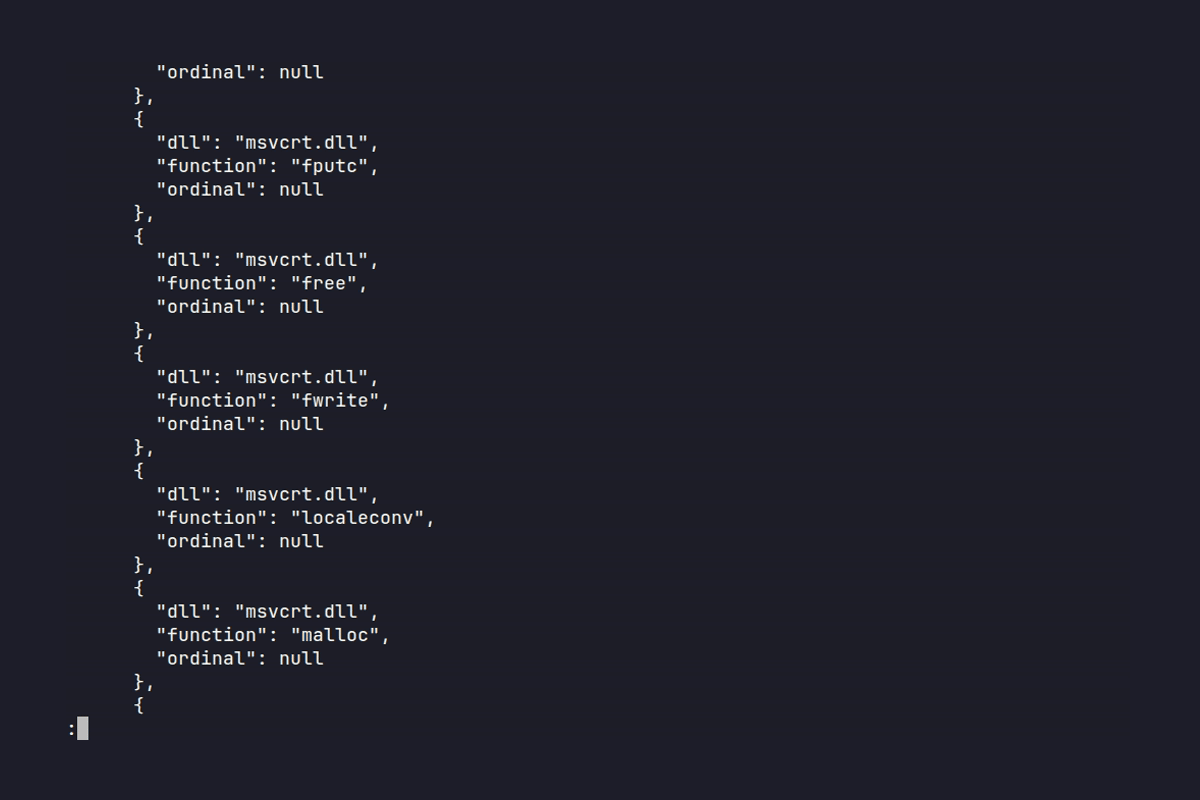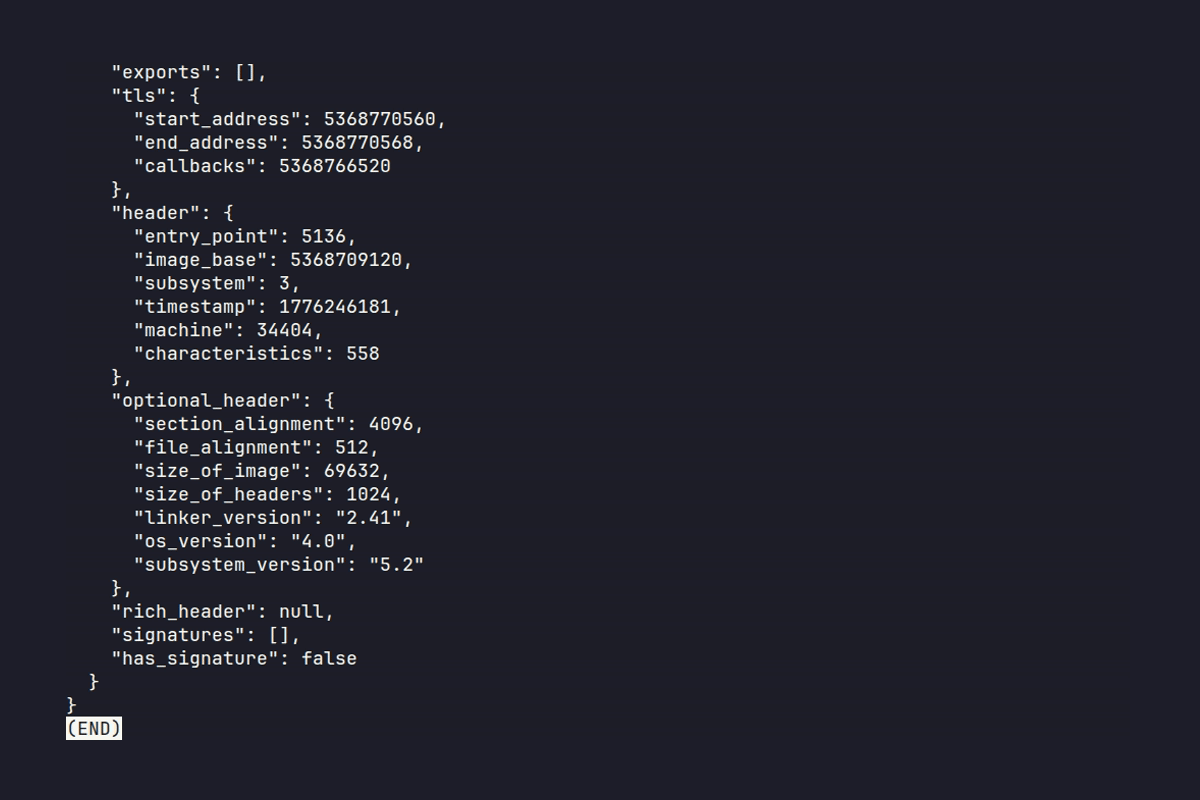 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 gilnett/wstrace
Standalone zero-driver Windows system and API monitor in Rust
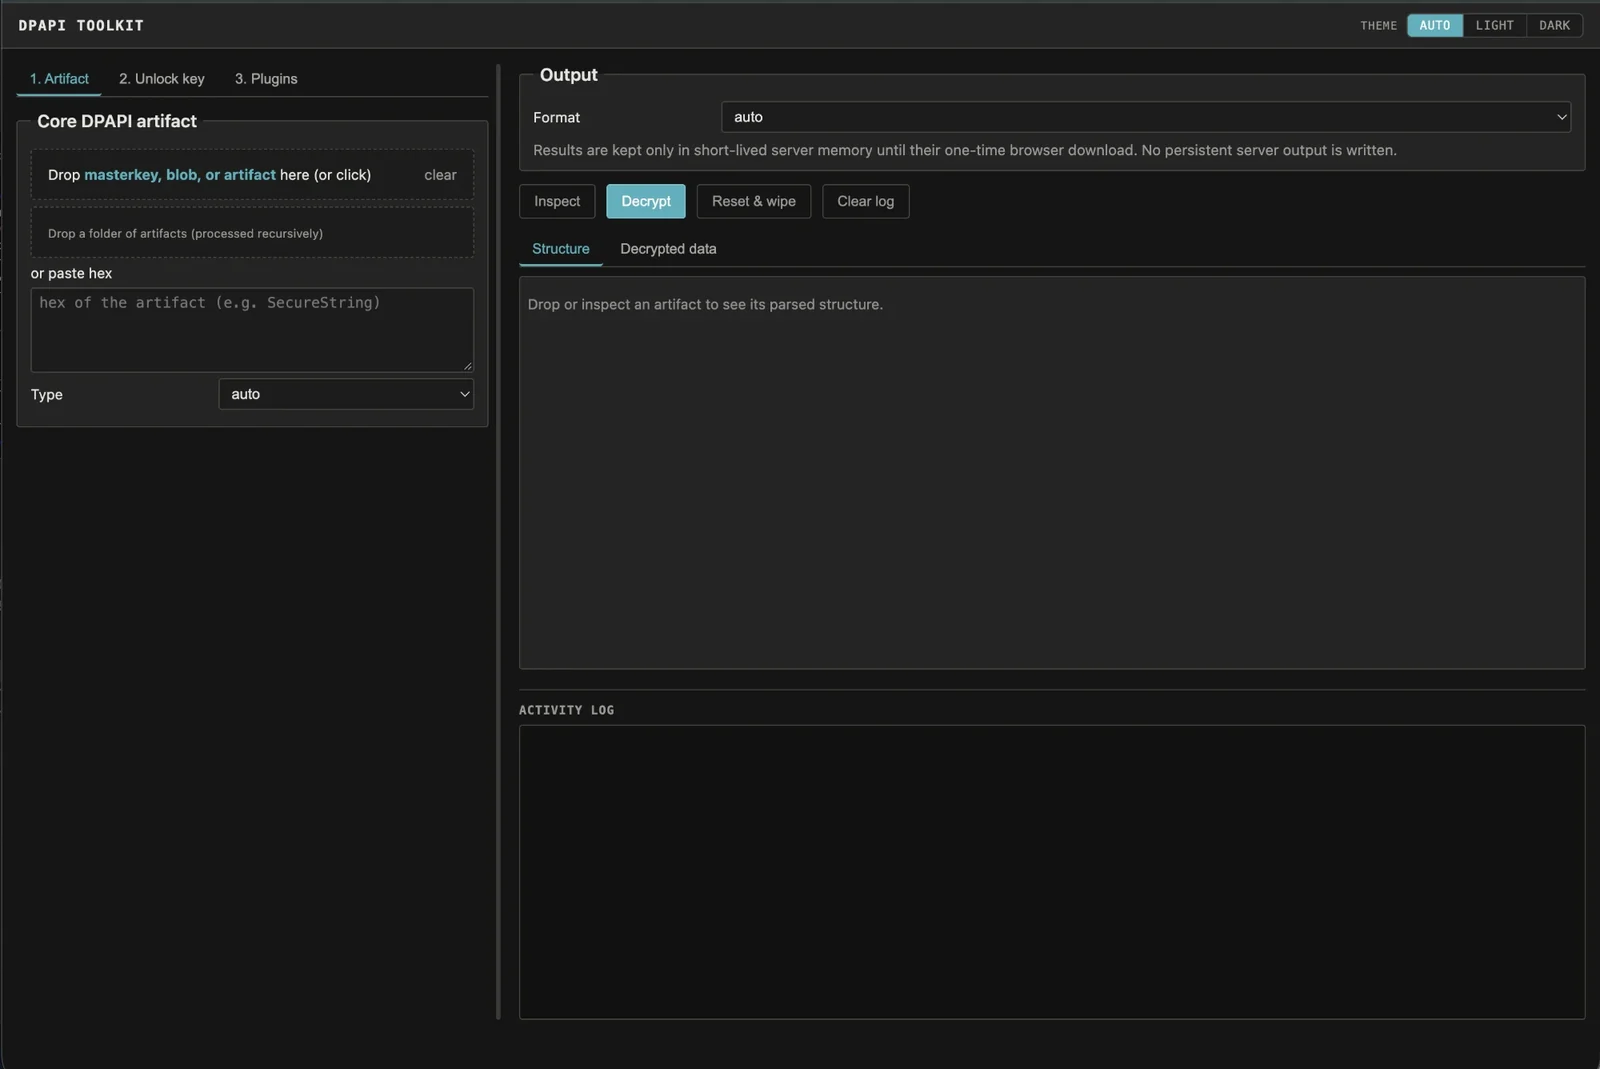 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
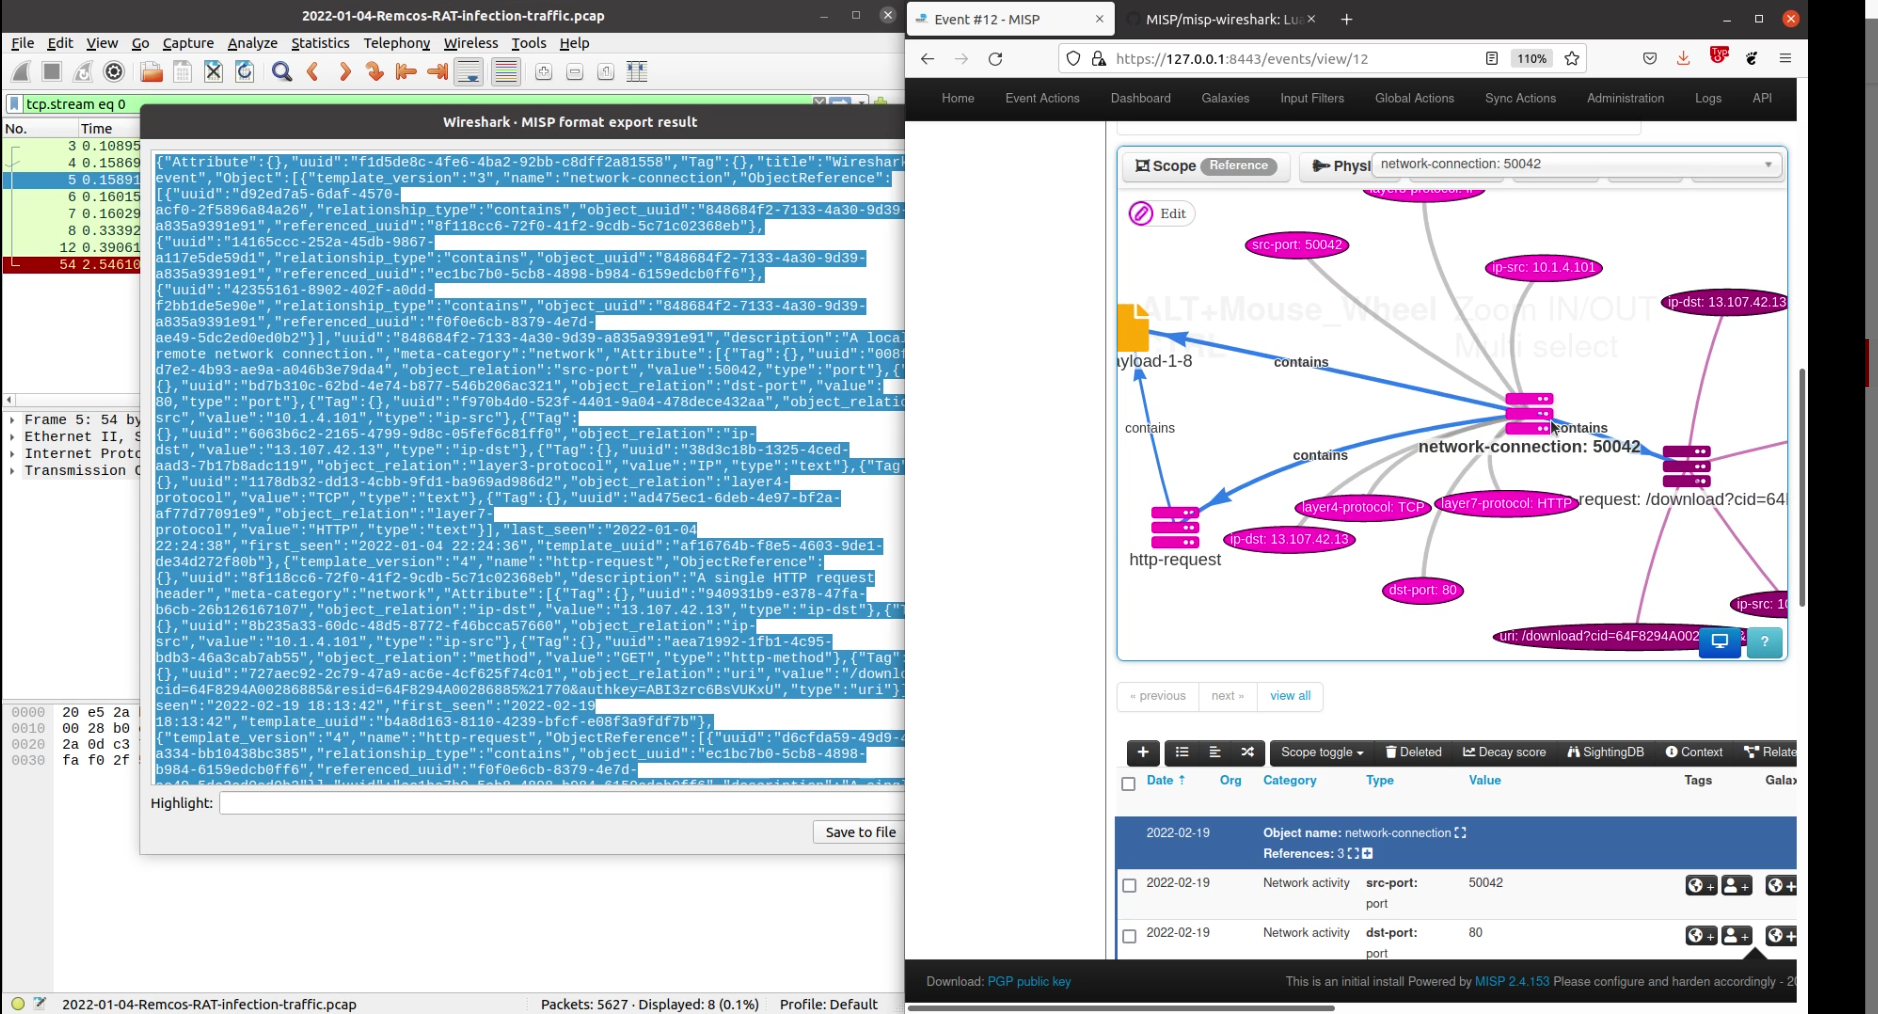 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
 piotr-kniaz/eslockdecryptor
Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)
 zephrfish/stompy
Timestomp Tool to flatten MAC times with a specific timestamp
 bi8d0/driversentinel
DriverSentinel is a security tool developed in Go that detects malicious and vulnerable drivers on Windows systems by comparing them against the…
 fireeye/cve-2021-44228
OpenIOC rules to facilitate hunting for indicators of compromise
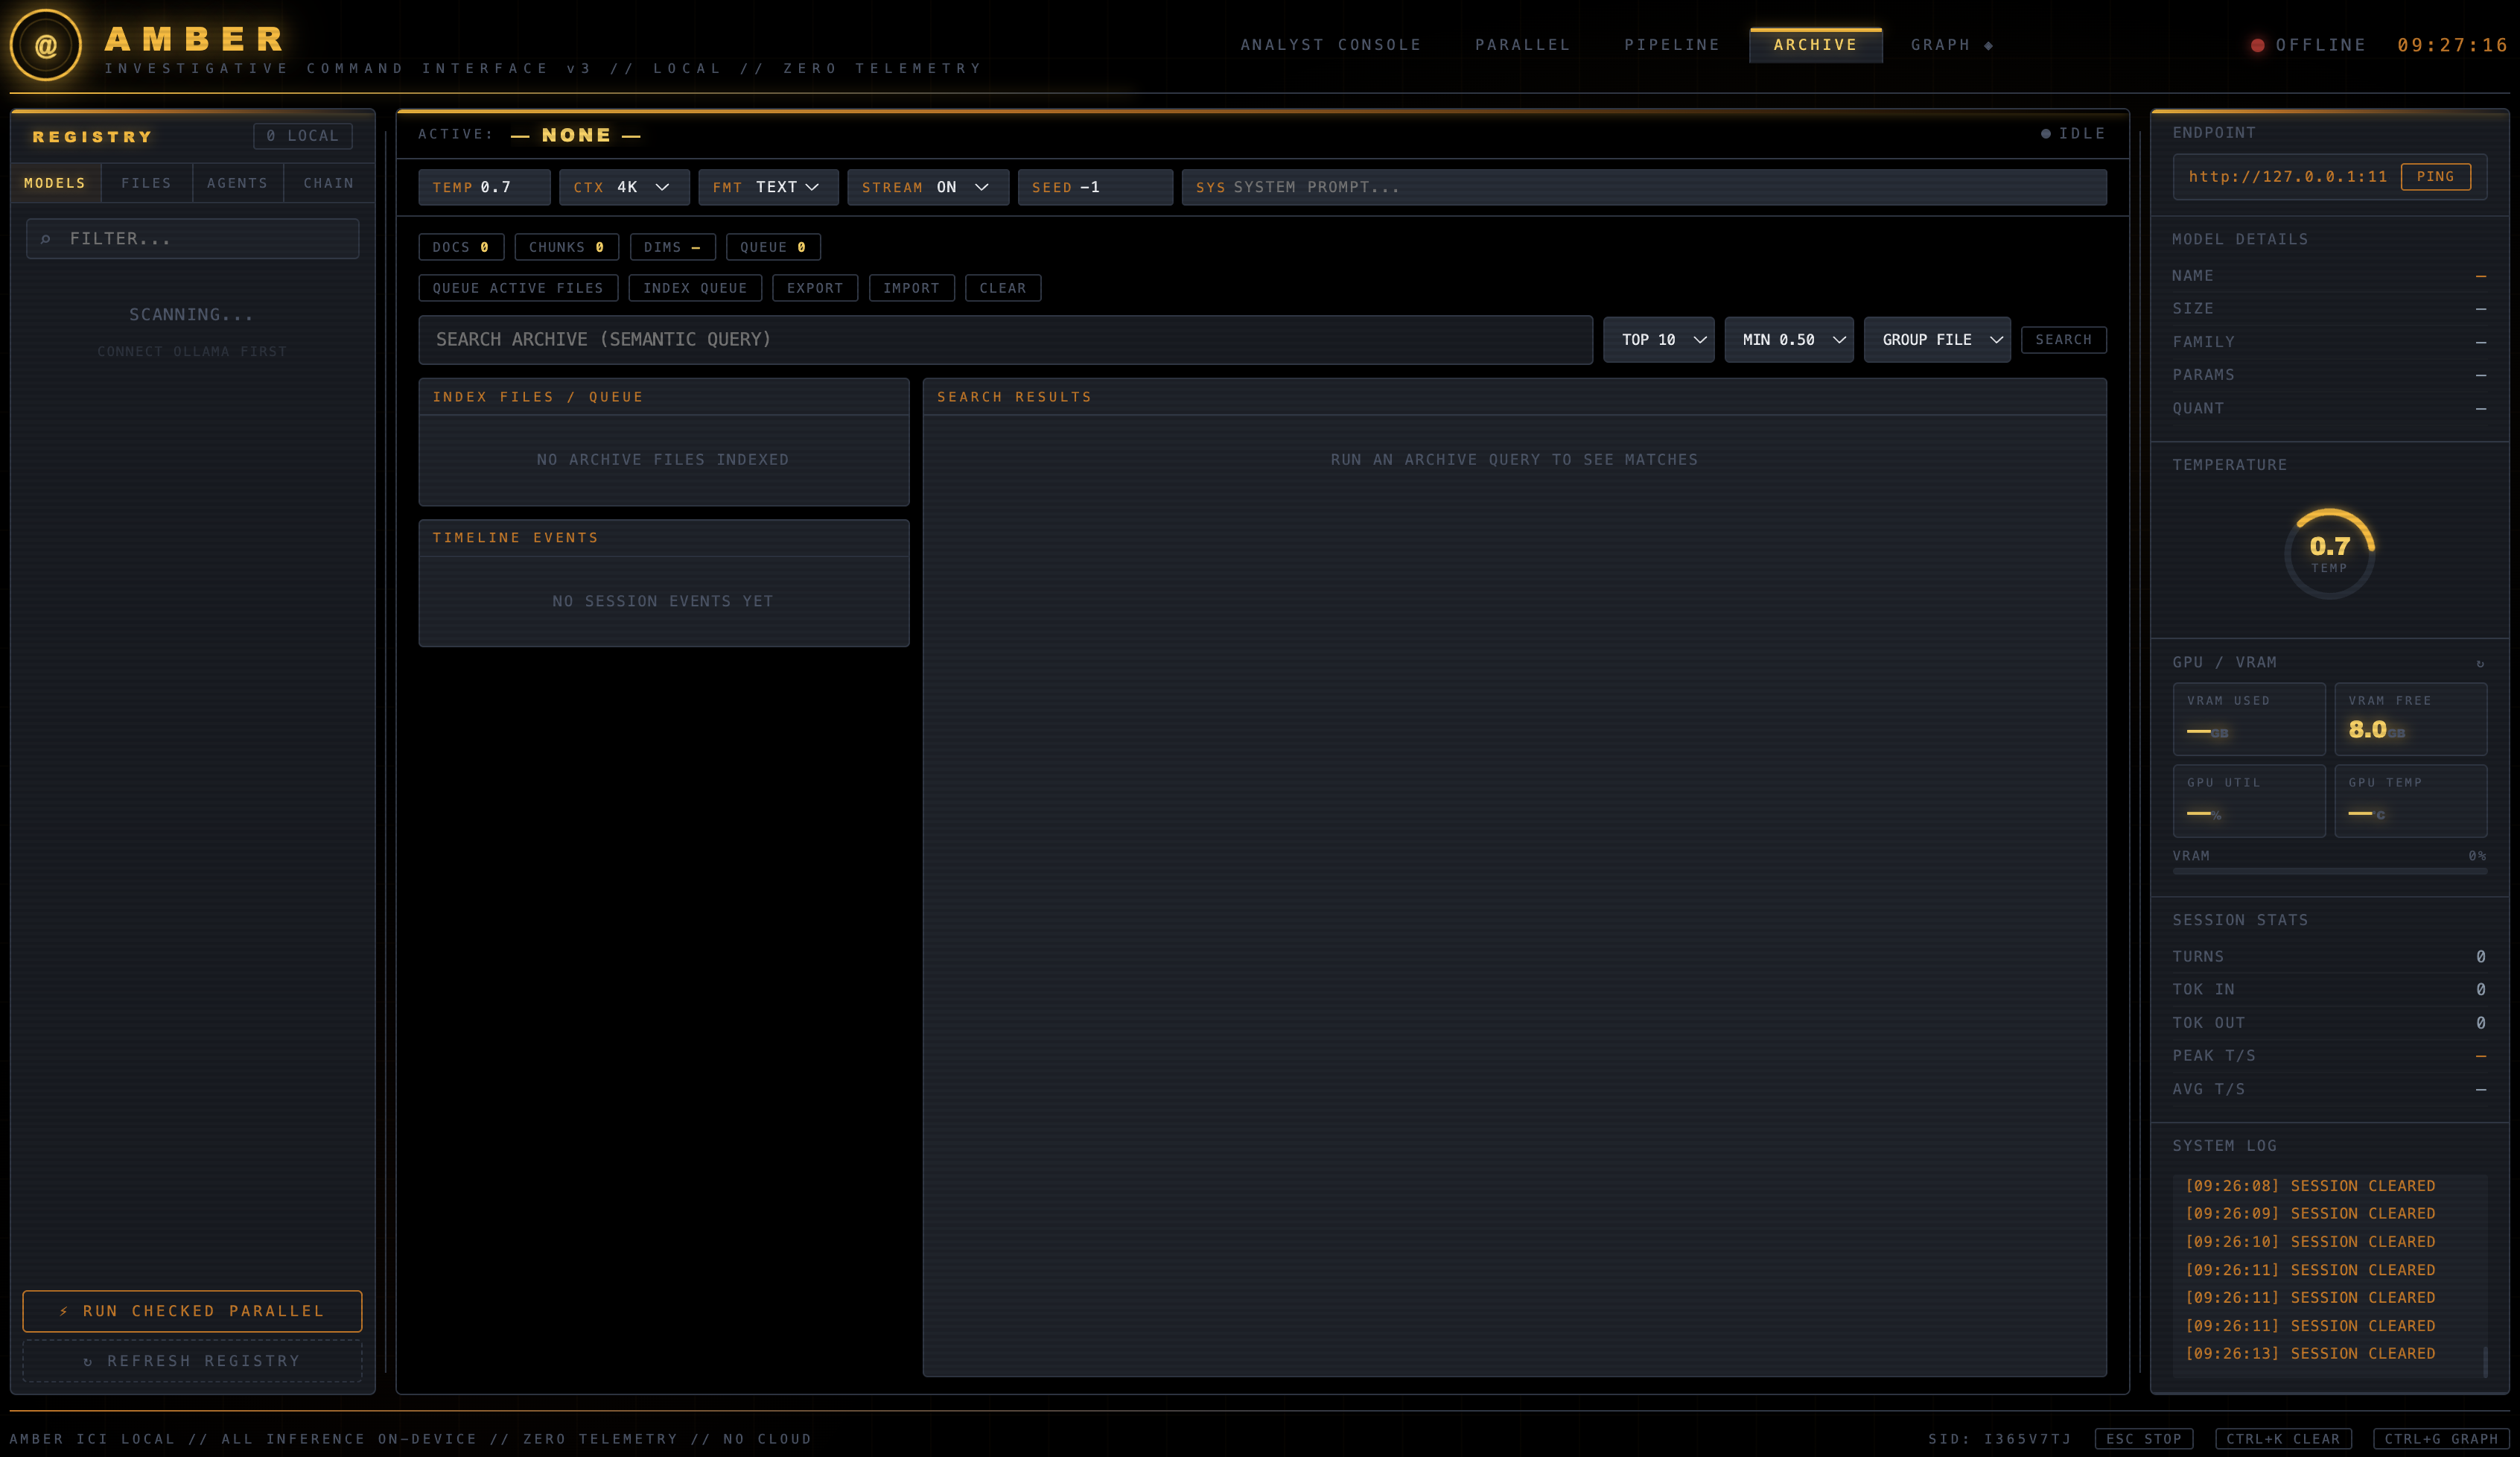 gs-ai/amber-ici
AMBER ICI v5: local-first Ollama investigative command center with case-scoped evidence, agent chains, hybrid retrieval, streaming analysis, graph…
 hakavlad/tird
Steganographic storage & File encryption tool
 nccgroup/metadataplus
A tool to use novel locations to extract metadata from Office documents.
 appliedsec/forensicscanner
Forensic Scanner
 letsdefendio/simple-live-data-collection
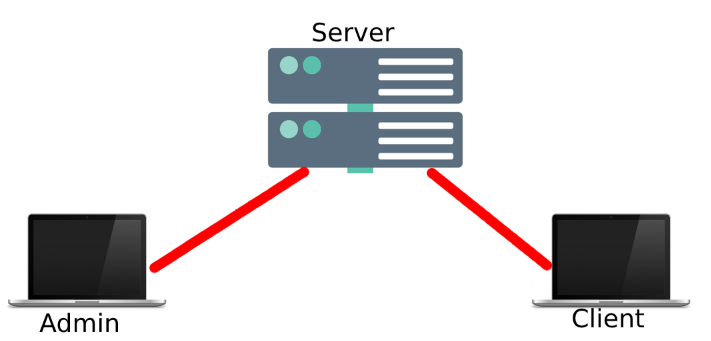
Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…









