
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Forensics — Page 32 | Kitploit
Categories

Forensics

Digital forensics, evidence collection, timeline analysis, and incident investigation tools.

Kitploit recommended
Top tools

10 selected
autopsy preview#1

autopsy

GitHubsleuthkit/autopsy
3.3k6 months ago
sleuthkit preview#2

sleuthkit

GitHubsleuthkit/sleuthkit
3.2k8 days ago
volatility3 preview#3

volatility3

GitHubvolatilityfoundation/volatility3
4.3k23 days ago
plaso preview#4

plaso

GitHublog2timeline/plaso
2.2k2 days ago
bulk_extractor preview#5

bulk_extractor

GitHubsimsong/bulk_extractor
1.4k24 days ago
velociraptor preview#6

velociraptor

GitHubvelocidex/velociraptor
4.2k1 day ago
timesketch preview#7

timesketch

GitHubgoogle/timesketch
3.4k1 day ago
mvt preview#8

mvt

GitHubmvt-project/mvt
15.7k6 days ago
androidqf preview#9

androidqf

GitHubmvt-project/androidqf
23015 days ago
avml preview#10

avml

GitHubmicrosoft/avml
1.1k12 days ago
NewestRelevanceMost popularRecently updated
947 results
wcw-cyberring-pav-decryptor preview

wcw-cyberring-pav-decryptor

GitHubblakebratcher/wcw-cyberring-pav-decryptor

Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…
static-analysisencryption-decryption-toolsreverse-engineering+5
259 months ago
Veto preview

Veto

GitHubprofessorquantumuniverse/veto

Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
android-securityioc-managementstatic-analysis+8
227 days ago
FileWatchTower preview

FileWatchTower

GitHubiomoath/filewatchtower

FWT is a security analysis and file monitoring tool that utilizes Sysmon events.

hash-analysisforensicsmalware-analysis+4
292 years ago
iCloudKitExtractor preview

iCloudKitExtractor

GitHubgiordanosconti/icloudkitextractor

Experimental .NET/WPF forensic toolkit for iCloud auth, CloudKit/MMCS backup download, and Octagon/PCS recovery (ADP, Recovery Key, Lockdown Mode).…

encryption-decryption-toolsios-securityforensics+6
1822h 33m ago
ESFang preview

ESFang

GitHubwithsecurelabs/esfang

ESF modular ingestion tool for development and research.
forensicsdigital-forensicsincident-response+1
384 years ago
ipdecap preview

ipdecap

GitHublpefferkorn/ipdecap

Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
packet-sniffing-analysisencryption-decryption-toolsvulnerability-analysis+3
348 years ago
aiengine preview

aiengine

GitHubcamp0/aiengine

Programmable packet inspection engine with NIDS, DNS classification, frequency analysis, and auto-regex generation. Supports Python/Ruby/Java/Lua…
packet-sniffing-analysisvulnerability-analysisforensics+5
319 years ago
Get-AppLockerEventlog preview

Get-AppLockerEventlog

GitHubromaissaadjailia/get-applockereventlog

This is a repo for fetching Applocker event log by parsing the win-event log
forensicsthreat-intelligenceincident-response+1
294 years ago
usn_analytics preview

usn_analytics

GitHub4n6ist/usn_analytics

It's not just UsnJrnl (USN Journal Records/Change Journal Records) parser.
disk-forensicsforensicsdata-recovery+1
248 years ago
excelpeek preview

excelpeek

GitHubslaughterjames/excelpeek

Static analysis tool for investigating potentially malicious Microsoft Excel files, extracting metadata, macros, and embedded objects to aid digital…
static-analysisforensicsmalware-analysis+1
384 years ago
shadow-fleet-tracker-light preview

shadow-fleet-tracker-light

GitHubformerlab/shadow-fleet-tracker-light

Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally

osintreconnaissancenetwork-mapping+9
426 months ago
VAXD preview

VAXD

GitHubbicurico/vaxd

Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
embedded-systems-securityreverse-engineeringdebuggers+7
174 months ago
ShadowNet preview

ShadowNet

GitHubantisurveillanceagency/shadownet

ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…
wi-fi-auditingmemory-forensicsosint-social-engineering+9
371 month ago
EventHorizon preview

EventHorizon

GitHubhullabrian/eventhorizon

Tool that gathers a customizable set of ETW telemetry and generates user-defined detections

defensive-toolsmemory-forensicsforensics+5
569 months ago
WhacAMole preview

WhacAMole

GitHubignacioj/whacamole

Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…

ioc-managementdynamic-analysis-sandboxingmemory-forensics+9
452 years ago
BurpMetaFinder preview

BurpMetaFinder

GitHubjosue87/burpmetafinder

Burp Suite extension for extracting metadata from files
osintforensicsinformation-gathering+1
205 years ago
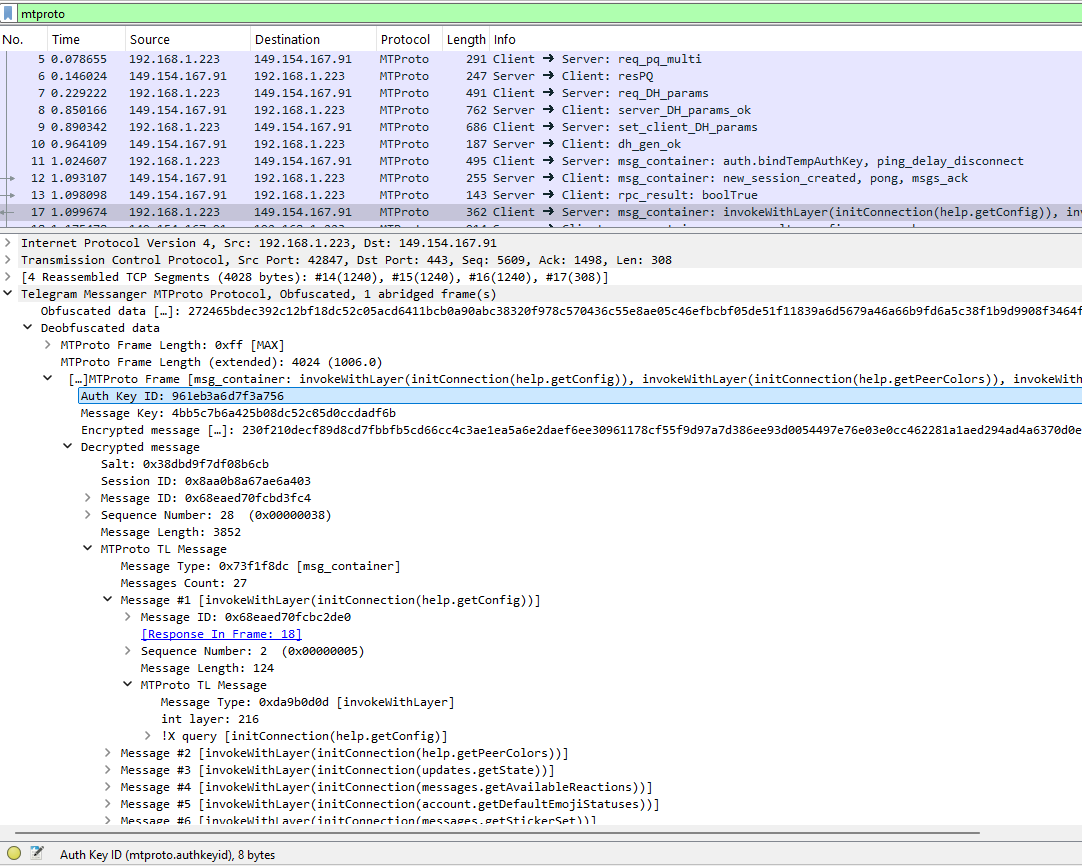
mtproto-dissector preview

mtproto-dissector

GitHubtomer8007/mtproto-dissector

Wireshark plugin for dissecting the Telegram protocol

packet-sniffing-analysisencryption-decryption-toolsreverse-engineering+2
407 months ago
witchcraft preview

witchcraft

GitHubcosmic-zip/witchcraft

WITCHCRAFT is a cyberdeck toolkit built for runners who dive deep into the mesh. It’s your all-in-one rig for data-ghosting, ICE-breaking, and…


osintphishing-toolsreconnaissance+8
521 year ago
Previous1…313233…53Next







