#1
Tools for weaponizing vulnerabilities to gain unauthorized access to systems or data.
Kitploit recommended

 r41n3rzuf477/quickassist_uac_bypass
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 padovah4ck/cve-2019-1253
Poc for CVE-2019-1253
 dinosn/php-cve-2026-10961x-lab-poc
PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…
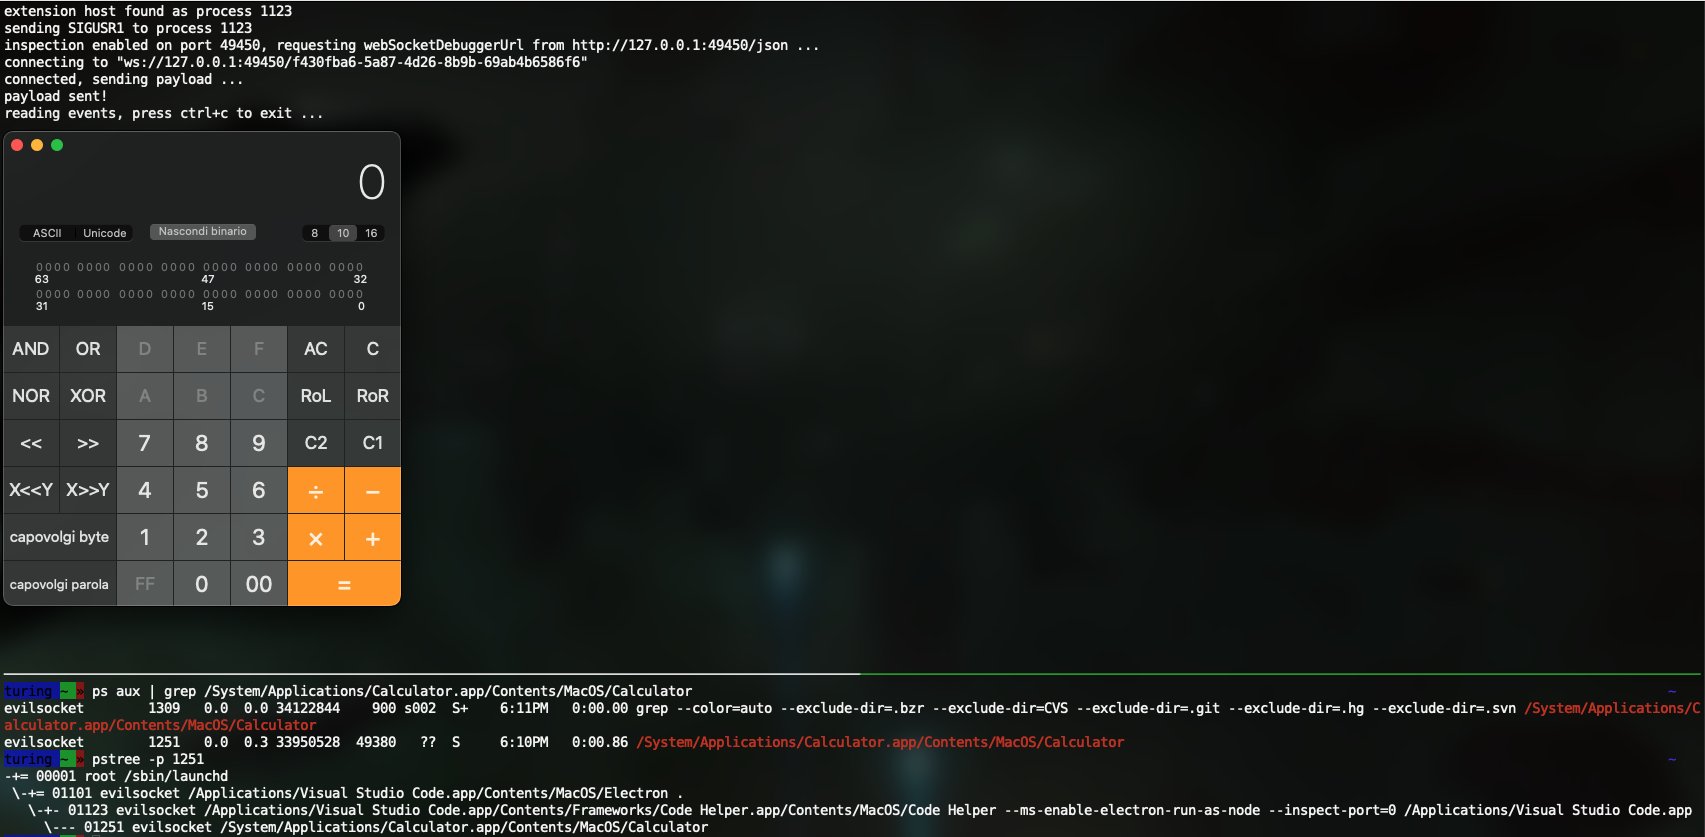 evilsocket/jscythe
Abuse the node.js inspector mechanism in order to force any node.js/electron/v8 based process to execute arbitrary javascript code.
 b1n4r1b01/desc_race
iOS 15.1 kernel exploit POC for CVE-2021-30955
 nccgroup/pybeacon
A collection of scripts for dealing with Cobalt Strike beacons in Python
 opsxcq/exploit-cve-2014-6271
Shellshock exploit + vulnerable environment
 thewhiteh4t/killcast
Manipulate Chromecast Devices in your Network
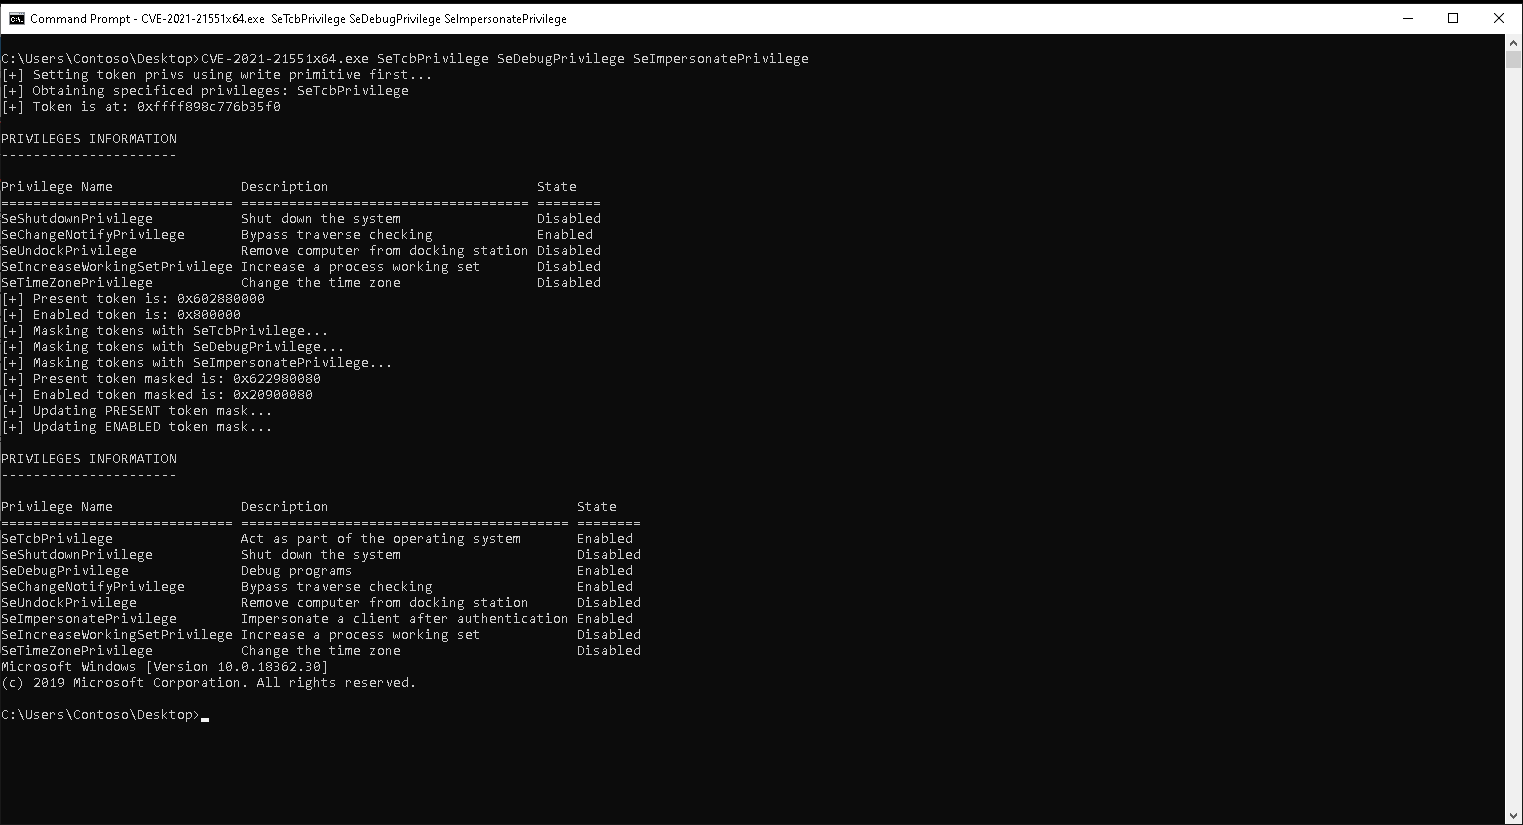 waldo-irc/cve-2021-21551
Exploit to SYSTEM for CVE-2021-21551
 breenmachine/javaunserializeexploits
Exploit Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS using Python PoC scripts and crafted HTTP requests.
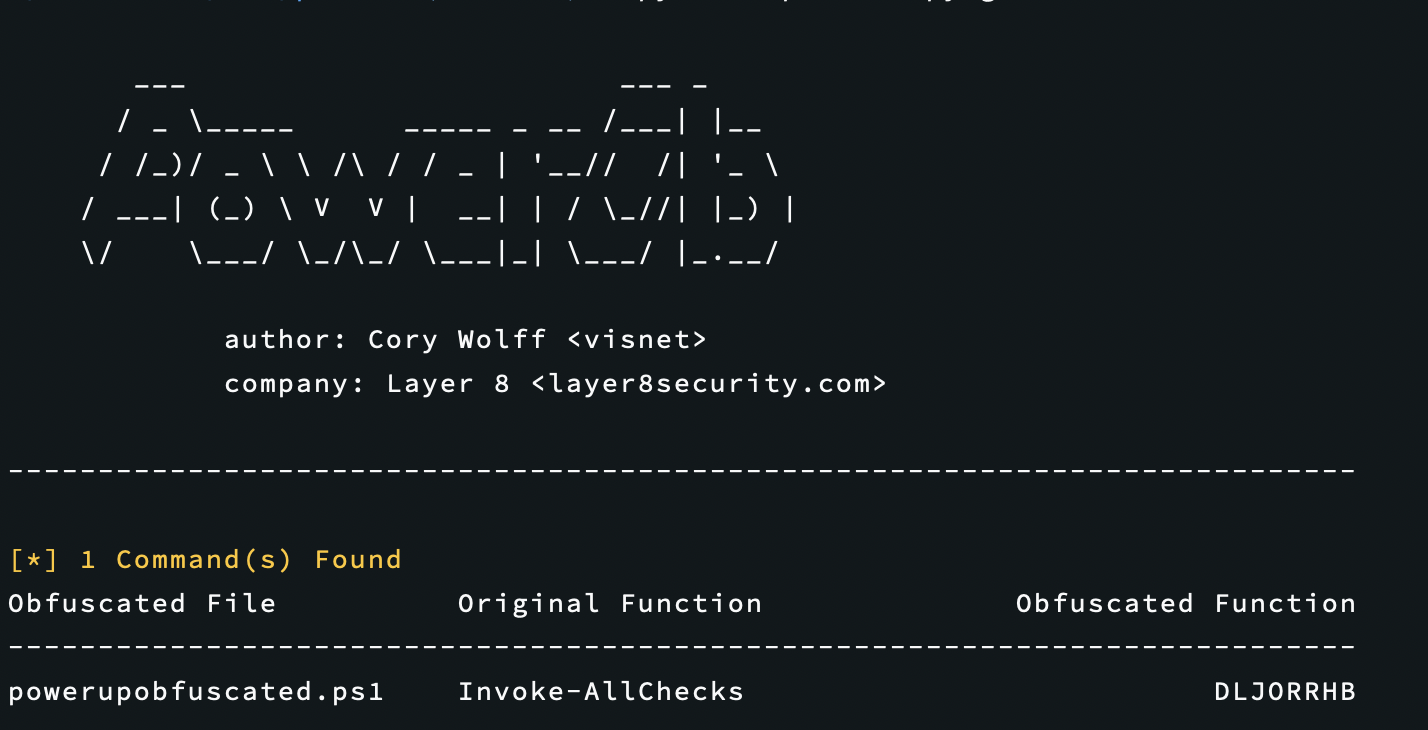 cwolff411/powerob
An on-the-fly Powershell script obfuscator meant for red team engagements. Built out of necessity.
 rickdejager/cve-2023-4911
CVE-2023-4911 proof of concept
 rxwx/cve-2017-8570
Proof of Concept exploit for CVE-2017-8570
 zcgonvh/cve-2020-17144
weaponized tool for CVE-2020-17144
 octoberfest7/dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking