
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
powerob — An on-the-fly Powershell script obfuscator meant for red team engagements. Built out of necessity. | Kitploit
Tools/GitHubGitHub/cwolff411/powerob
Payload GenerationScripting & AutomationPenetration TestingRed Teaming
GitHubcwolff411/powerob

powerob

An on-the-fly Powershell script obfuscator meant for red team engagements. Built out of necessity.

View Repository
14540835 years agoReviewed by Kitploit
Share

fenrir-desktop-bg

Powerob

An on-the-fly Powershell script obfuscator meant for red team engagements. Built out of necessity.

This only obfuscates functions and removes found in PowerShell scripts. Roadmap includes bfuscating variables. Pull requests and collaborative welcomed.

About

This was built out of the need to bypass endpoint security on a recent engagement. During priv esc attempts I could not download PowerUp.ps1 until it was obfuscated.

This is technically v2 and has been updated to remove comments.

Installation

git clone https://github.com/cwolff411/powerob

Usage

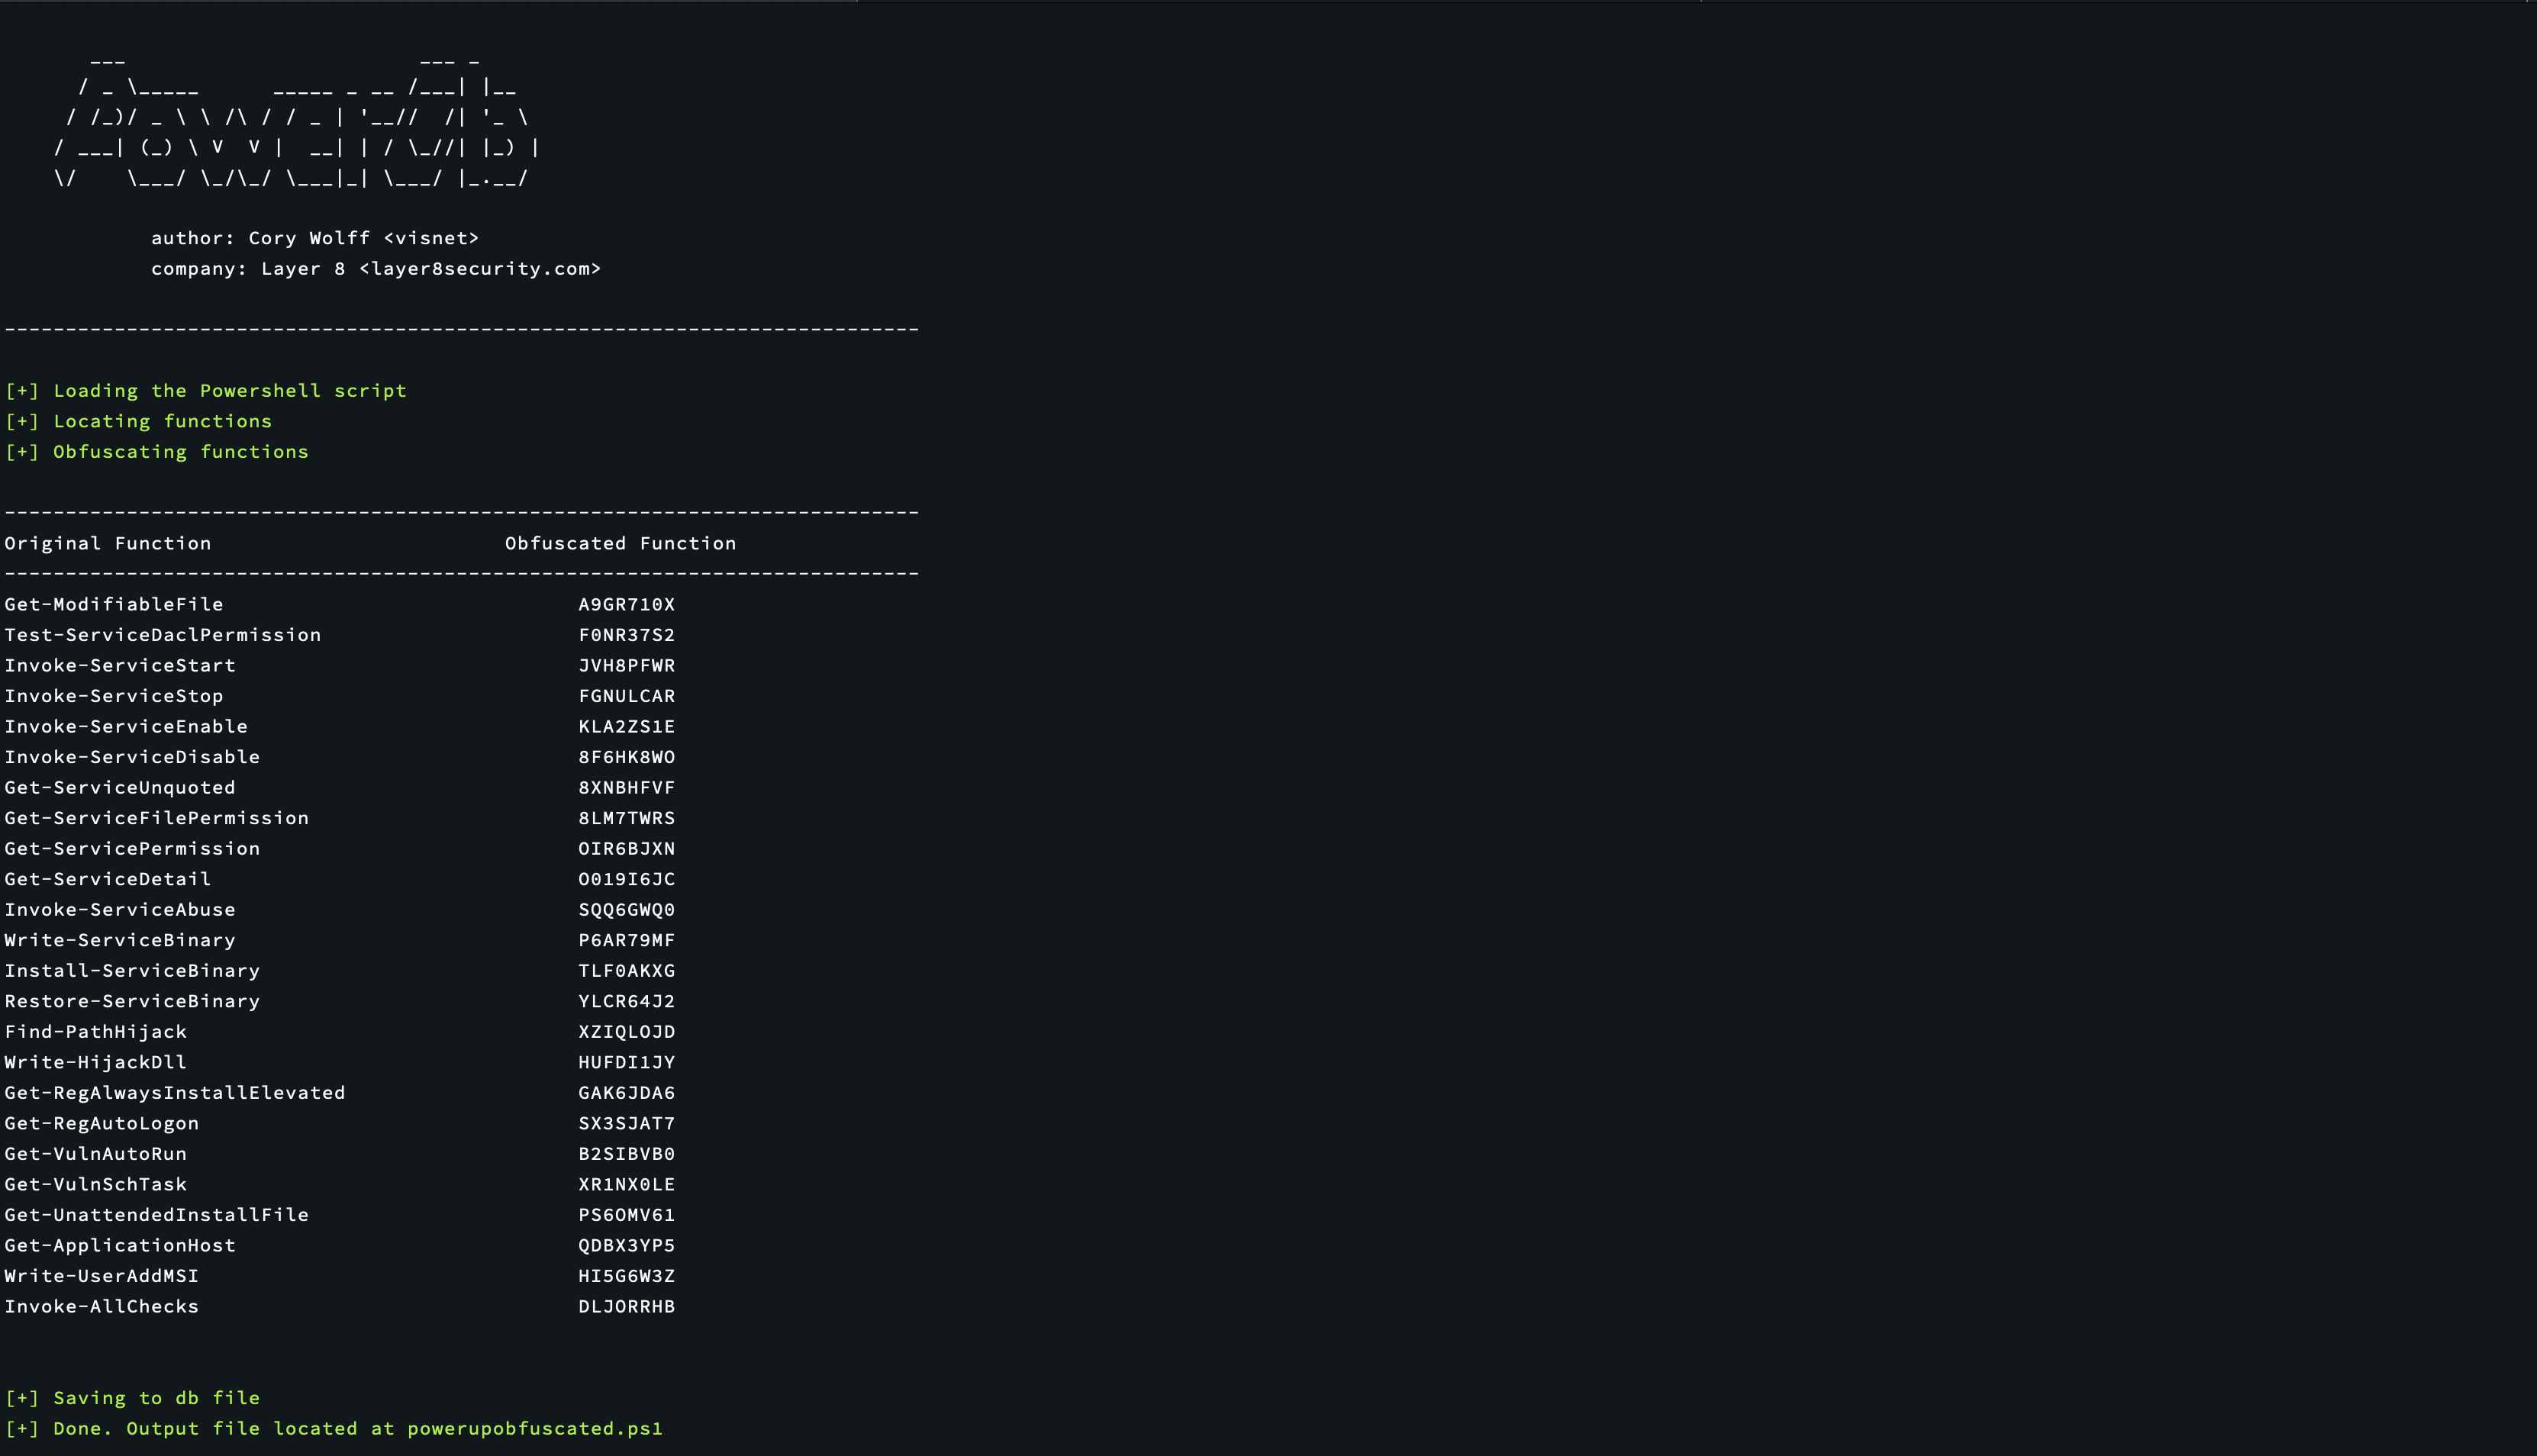
python3 powerob.py obfuscate originalfile.ps1 obfuscatedfile.ps1

Takes an INPUTFILE obfuscates it and dumps the obfuscated version into OUTPUTFILE.
PowerOb


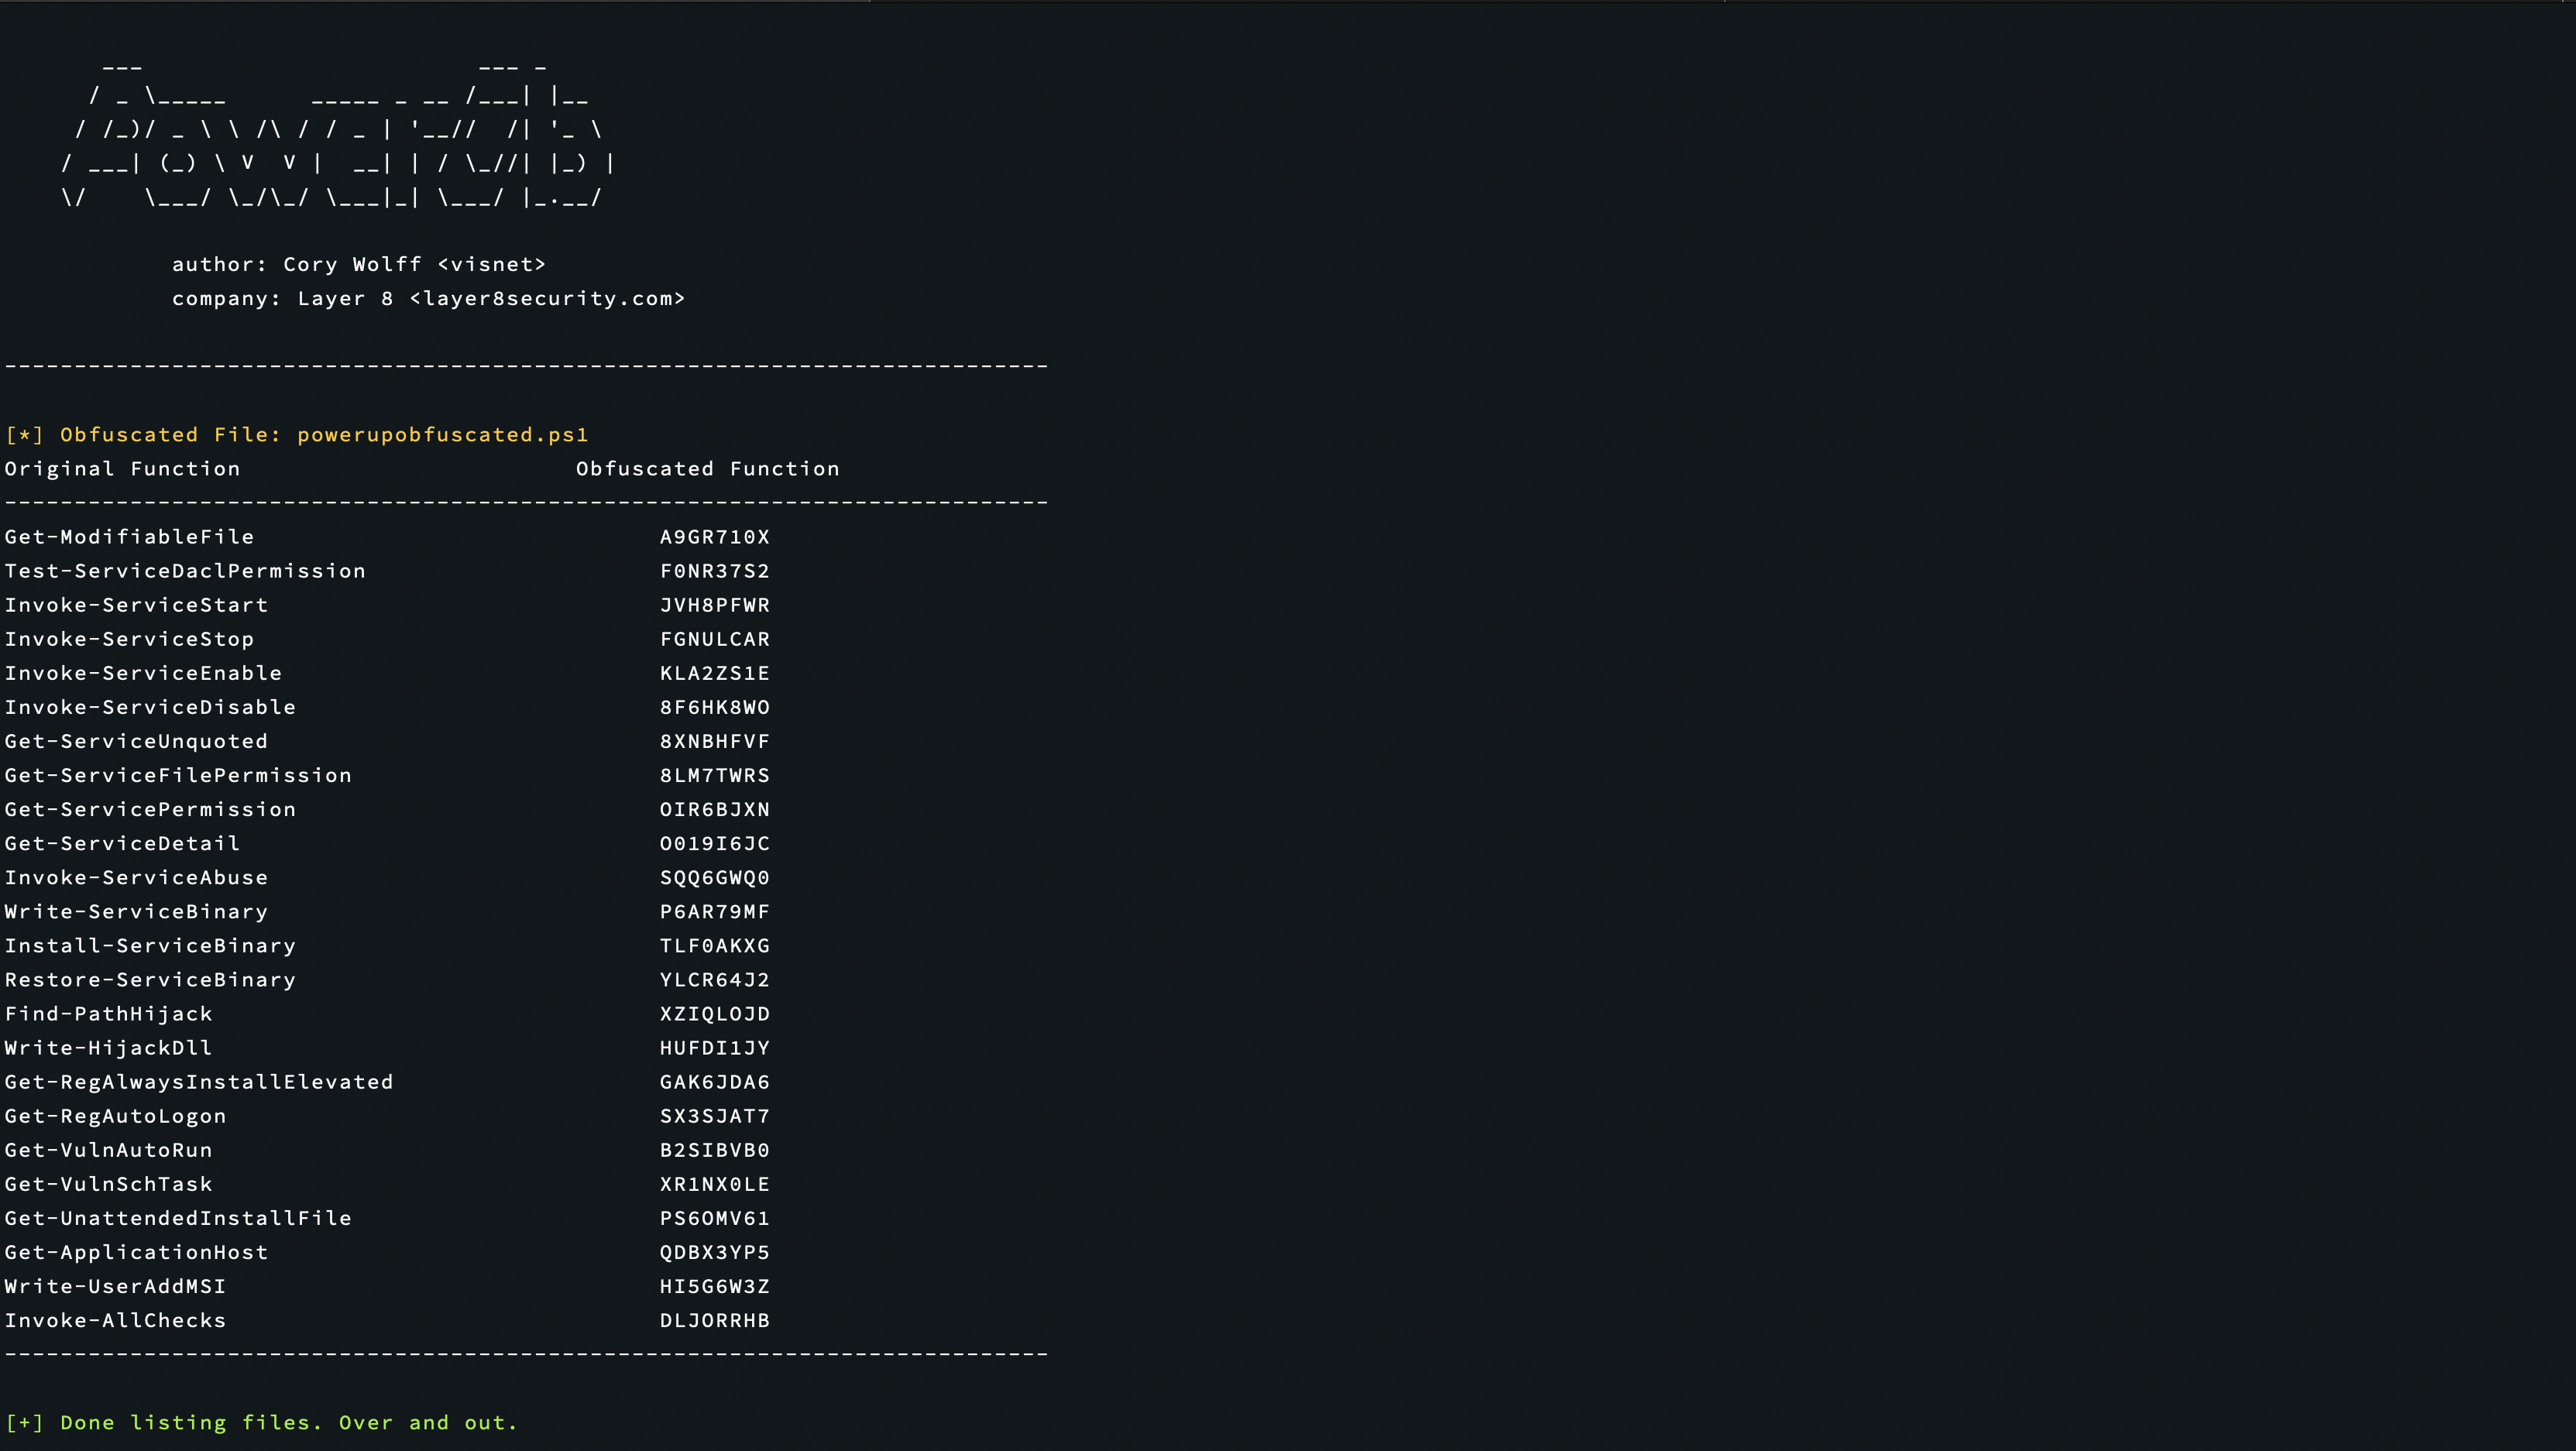
python3 powerob.py list

Lists all of the currently obfuscated files along with their commands and associated obfuscated commands.
PowerOb


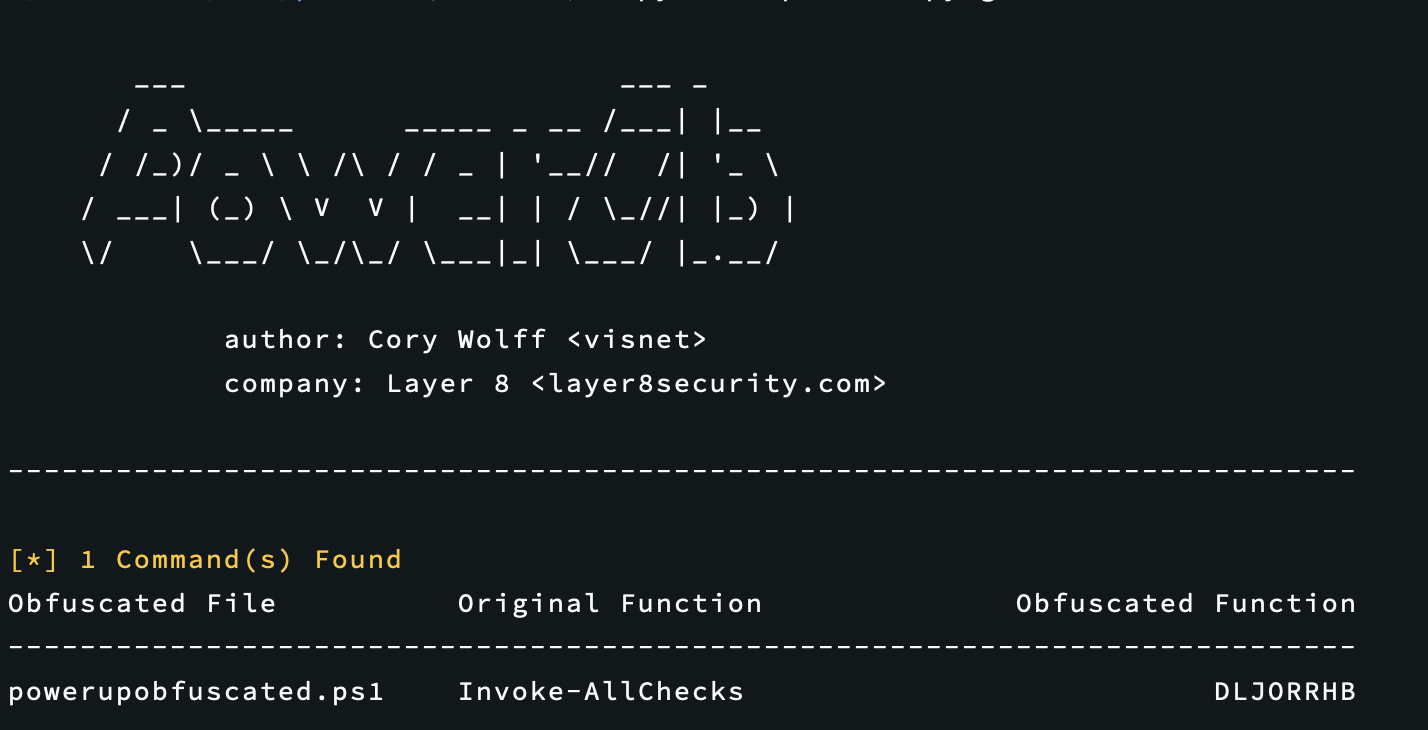
python3 powerob.py getcommand COMMAND_NAME

For reference on the fly for when you forget. Takes the original command name and displays the obfuscated command name to be used in Powershell.
PowerOb


python3 powerob.py cleardb

Maintenance function to clear the db of past obfuscated files and functions.

License

MIT License

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →





