
 #1
 nikaiw/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation vulnerability in polkit's pkexec, demonstrating exploitation for security…
 shadowabi/cve-2026-31431-copyfail-universal-lpe
CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback
 payatu/cve-2018-14442
PoC for Foxit Reader CVE-2018-14442
 cedowens/mythic-macro-generator
Python3 script to generate a macro to launch a Mythic payload. Author: Cedric Owens
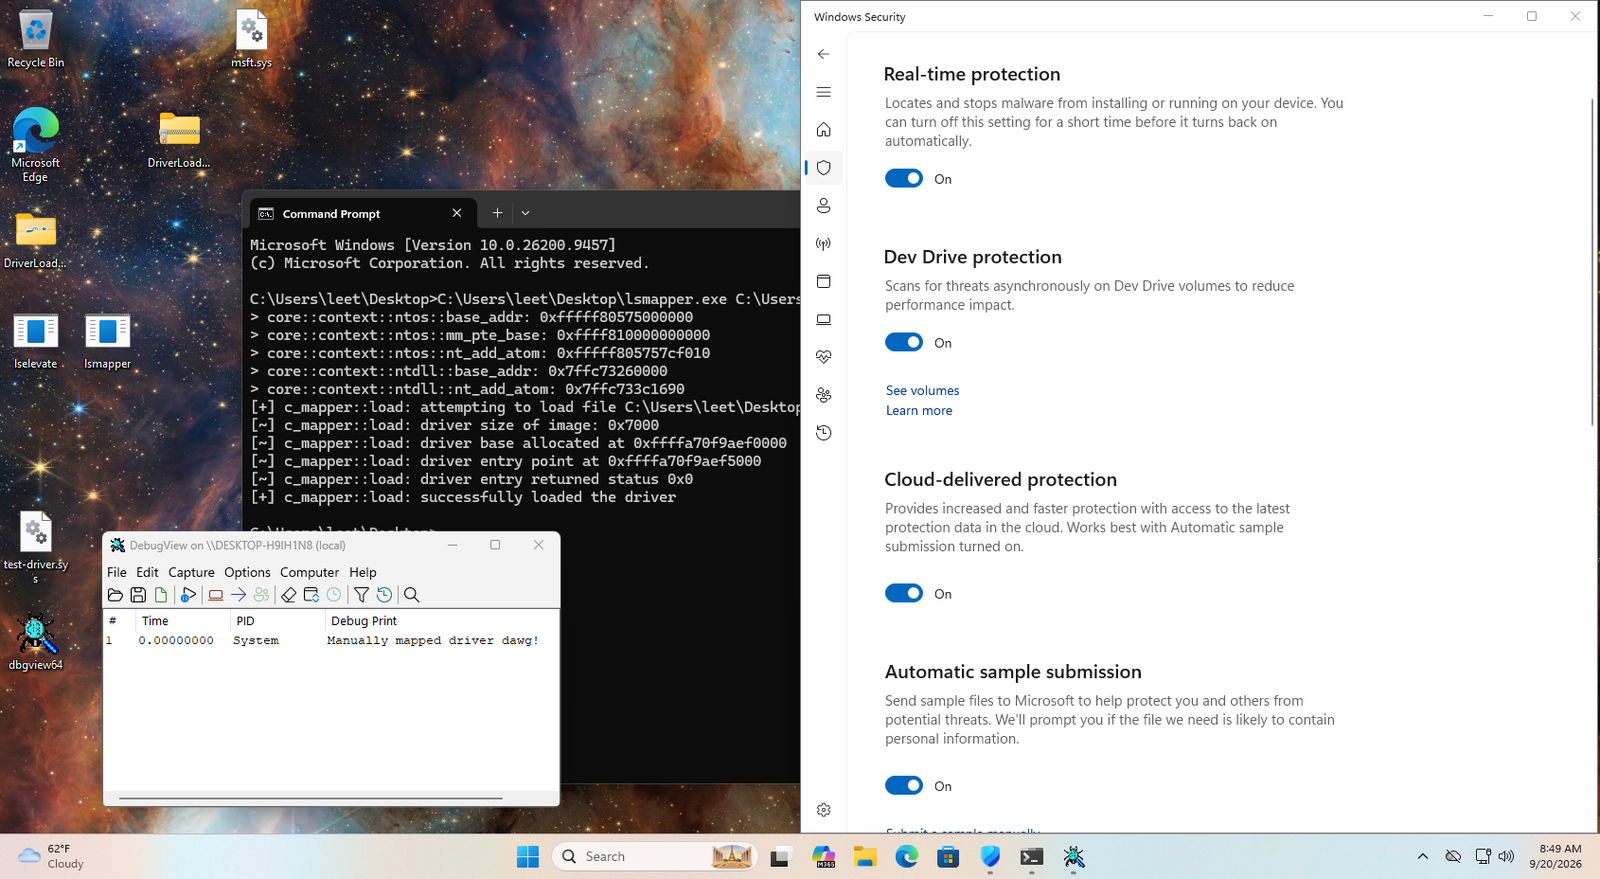 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
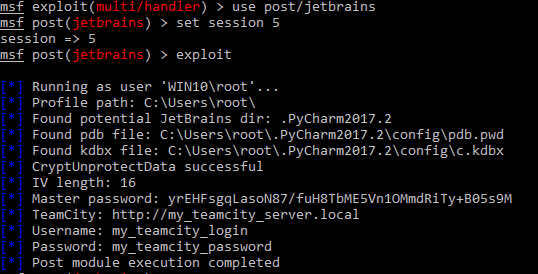 kacperszurek/pentest_teamcity
Pentest TeamCity using Metasploit
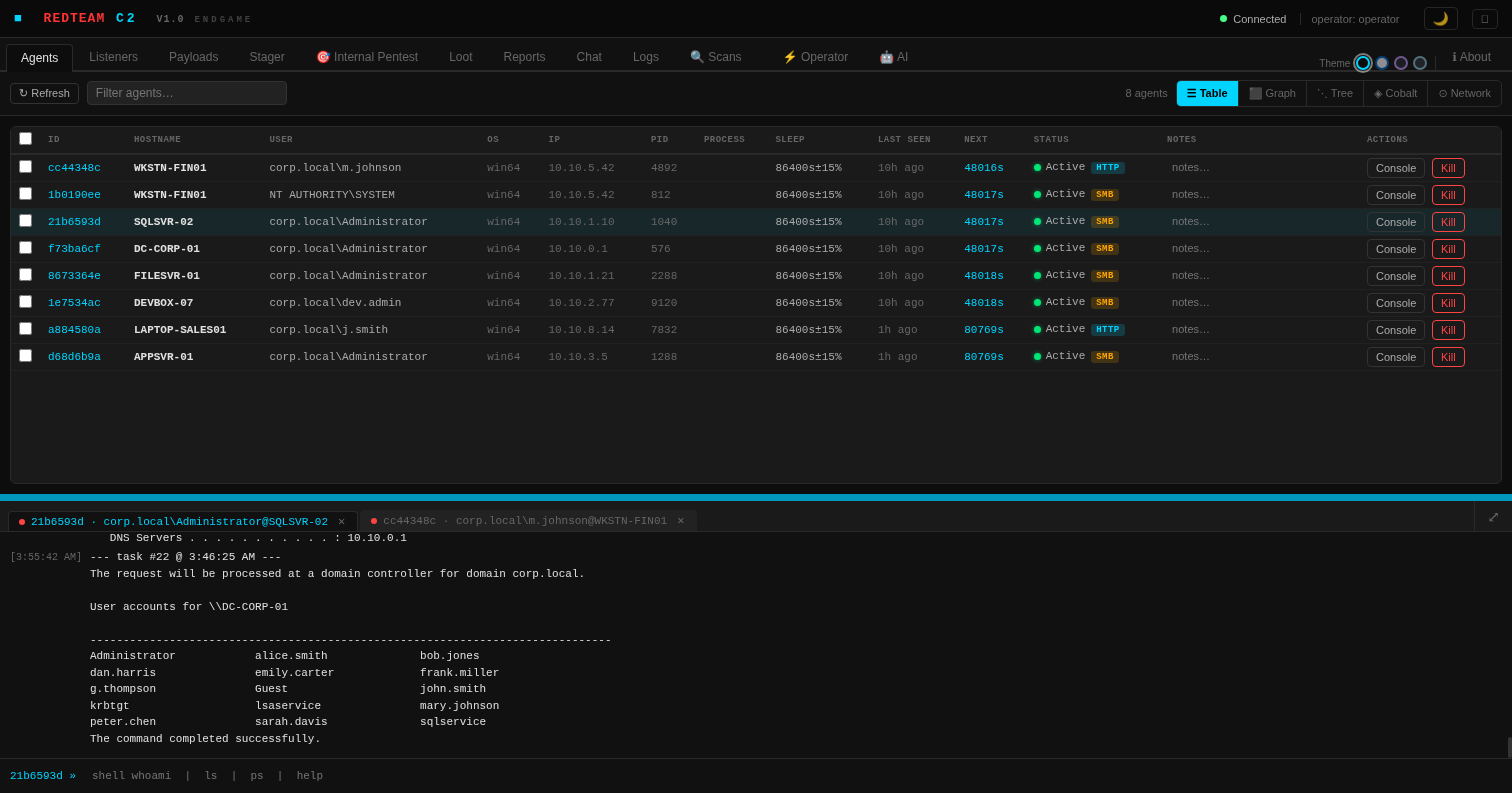 endgamec2framework/endgame
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations
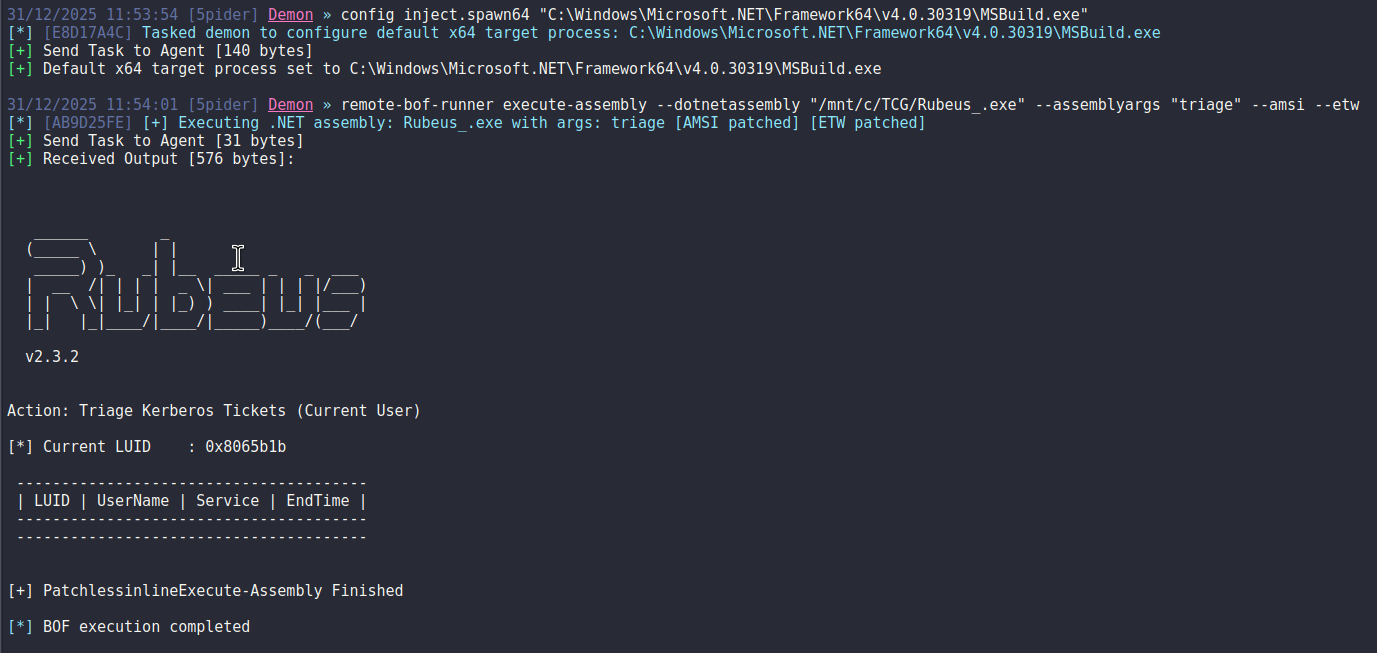 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 averagesecurityguy/c2
A simple, extensible C&C beaconing system.
 n0qword/mythic_ornn
LLM-driven generator for Mythic Agents, Payload-Type and C2 Profiles.
 bishopfox/joro
A collaborative web exploitation framework.
 0xshe/cve-2026-31431
Kernel privilege escalation exploit for CVE-2026-31431, abusing AF_ALG interface to overwrite /bin/su and spawn a root shell. Includes C…
 charmve/pystegosploit
PoC - Exploit Delivery via Steganography and Polyglots, CVE-2014-0282
 jackofmosttrades/bluebox
Automated Exploit Toolkit for CVE-2015-6095 and CVE-2016-0049
 stillbigjosh/neo
The NeoC2 Framework
 exbotanical/brutus
extensible exploitation framework shipped on a modular multi-tasking architecture
 moiz-2x/cve-2025-24990_poc
Proof of Concept CVE-2025-24990 (Agere Systems's driver)









