
 #1
Comprehensive frameworks for exploit development, testing, and execution.
Kitploit recommended
 moiz-2x/cve-2025-24990_poc
Proof of Concept CVE-2025-24990 (Agere Systems's driver)
 zer0yu/zeroscan
Multi-Thread Vulnerability Verify Framework
 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
 kryptsec/oasis
Open-source AI security benchmarking CLI. Measure how AI models perform offensive security tasks with MITRE ATT&CK analysis and KSM scoring.
 huynambka/cve-2026-26114-poc
Proof-of-concept exploit for CVE-2026-26114, a remote code execution vulnerability in Microsoft SharePoint, with a Python PoC and Metasploit module…
 ynwarcs/cve-2023-24871
pocs & exploit for CVE-2023-24871 (rce + lpe)
 estamelgg/cve-2021-4034-nogcc
Standalone exploit for CVE-2021-4034 (polkit pkexec) that runs without gcc or cmake, providing interactive shell or one-liner command execution on…
 joelgmsec/thunderstorm
Modular framework to exploit UPS devices
 kungfulon/nf-tables-lpe
Linux kernel privilege escalation exploits targeting Netfilter's nf_table module, developed by Team Orca for multiple CVEs.
 taroballzchen/cve-2022-41040-metasploit-proxynotshell
the metasploit script(POC) about CVE-2022-41040. Microsoft Exchange are vulnerable to a server-side request forgery (SSRF) attack. An authenticated…
 degenerat3/meteor
A cross-platform C2/teamserver supporting multiple transport protocols, written in Go.
 duck-sec/cve-2023-28252-compiled-exe
A modification to fortra's CVE-2023-28252 exploit, compiled to exe
 apkc/cve-2024-26229-bof
BOF implementations of CVE-2024-26229 for Cobalt Strike and BruteRatel
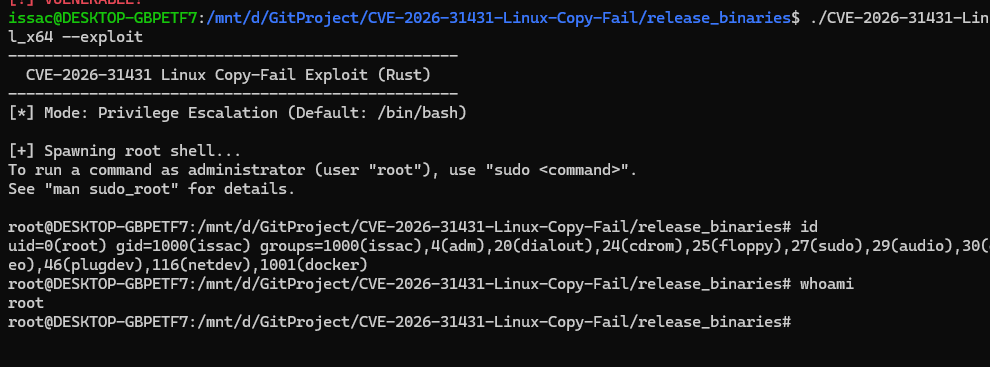 iss4cf0ng/cve-2026-31431-linux-copy-fail
Rust-based local privilege escalation exploit for CVE-2026-31431, enabling execution of custom shellcode such as Meterpreter on Linux systems.
 tayontech/scope
AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
 alexlinov/miniplasma-runner
CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback
 aazhuliang/cve-2021-31956-exp
Exploit for CVE-2021-31956, a Windows kernel privilege escalation vulnerability, targeting Windows 10 1903. Provides a proof-of-concept…
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…








