
 #1
Cybersecurity research, materials, labs, and learning paths, including CTFs and curated educational resources.
Kitploit recommended

 binderlabs/dircreate2system
Weaponizing to get NT SYSTEM for Privileged Directory Creation Bugs with Windows Error Reporting
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.
 zer0condition/gdrvloader
Unsigned driver loader using CVE-2018-19320
 zhuyansen/awesome-ai-reverse-engineering
Open-source AI reverse engineering tools for coding agents: Ghidra MCP, IDA Pro MCP, jadx, Frida, skills and REA. 122 repos, each read and…
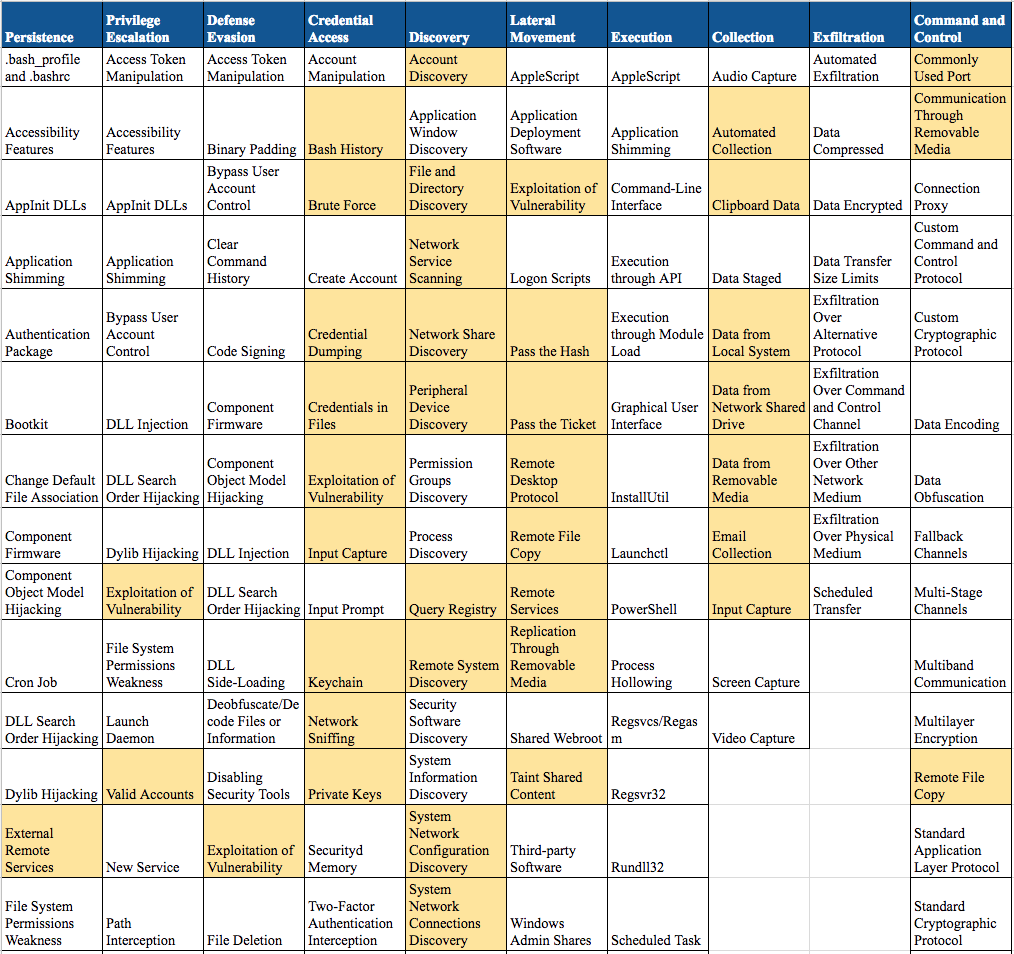 0x4d31/deception-as-detection
Deception based detection techniques mapped to the MITRE’s ATT&CK framework
 jymcheong/autottp
Automated Tactics Techniques & Procedures
 nextronsystems/ransomware-simulator
Safe ransomware simulation tool for testing antivirus detection. Simulates macro staging, volume shadow copy deletion, document encryption, and note…
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 fknmega/aether
AI-driven OSINT and security research agent that builds a live knowledge graph from public data, with bundled recon tools and offensive-security…
 fportantier/vulpy
Vulnerable Python Application To Learn Secure Development
 samyk/quickjack
Quickjack is a point-and-click tool for intuitively producing advanced clickjacking and frame slicing attacks.
 cy4nguy/python-ransomware
Complete Python RansomeWare Source Code With Full Decoumetions.
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
 helixo32/crimsonedr
Simulate the behavior of AV/EDR for malware development training.
 chompie1337/linux_lpe_ebpf_cve-2021-3490
eBPF-based Linux kernel local privilege escalation exploit targeting CVE-2021-3490. Provides root shell access on vulnerable Ubuntu kernels 5.8.0-25…
 iss4cf0ng/openpetya
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
 binarly-io/supplychainattacks
Curated repository of documented firmware supply chain attacks, featuring IoCs, detection tools, and references to help defenders understand and…
 antropos17/aegis
Open-source EDR for AI agents. Monitors processes, file access, network activity, and behavioral anomalies in real time with 110 agent signatures and…








